 安全软件
点击放大
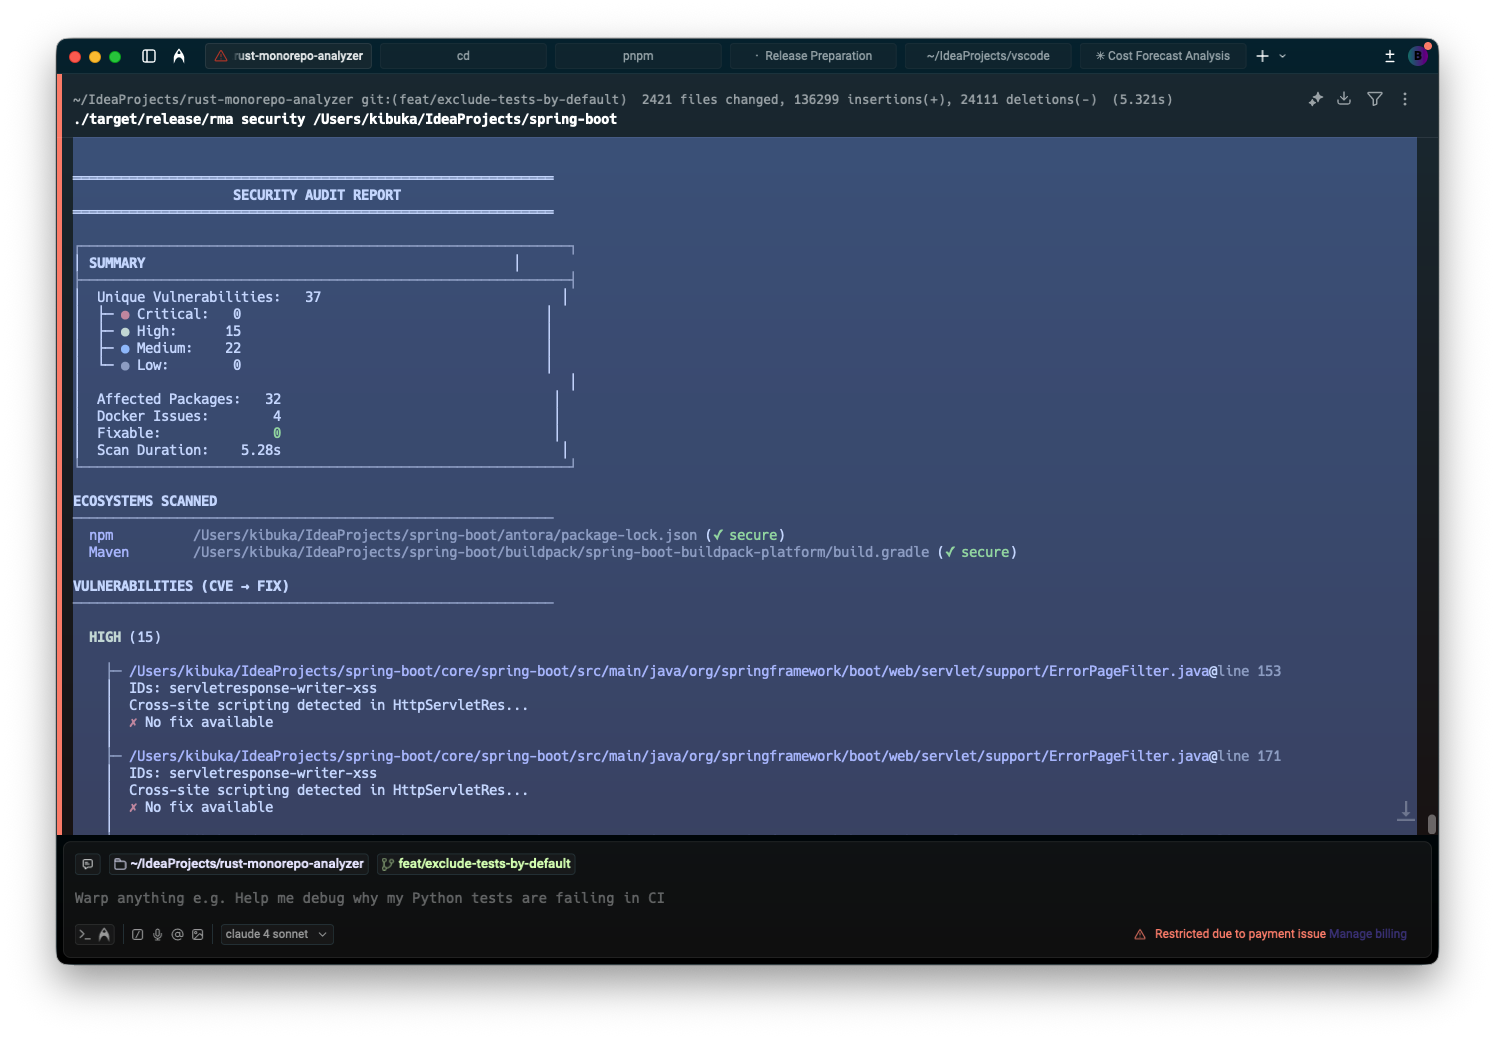
qryon - Qryon — Find security vulnerabilities in seconds.
项目说明
Qryon
<di="center">
Find security in seconds, not minutes.
![CI]()
![npm]()
![crates.io]()

</div>
<p align="center">
<img src="pics/demo.gif" alt="Qryon scanning a codebase and finding " width="700">
</p>
---
Why Qryon?
| Feature | Qryon | Semgrep OSS | CodeQL |
|---------|:---:|:-----------:|:------:|
| Scan 1M lines | 45s | 8+ min | 15+ min |
| Languages | 28 | 30+ | 12 |
| Setup | npm i -g qryon | Docker/pip | Complex |
| Rules | 647+ | 2500+ | |
| Cross-file taint | Yes | Pro only | Yes |
| Single binary | Yes | No | No |
| Price | Free | Free/Paid | Free |
Qryon is 10x faster because it compiles Semgrep rules to native Rust matchers at build time - no interpreter o.
---
Quick Start
<details>
<summary><strong>More installation methods</strong></summary>
Homebrew (macOS/Linux):
Cargo (Rust):
Docker:
Shell Script:
GitHub Actions:
</details>
---
What It Finds
Security Detection
Supported Languages
| Language | Security Rules | Frameworks |
|----------|----------------|------------|
| Rust | unsafe, injection, crypto | Actix, Axum, Rocket |
| Ja/TypeScript | XSS, injection, secrets | Express, React, Next.js |
| Python | exec, injection, secrets | Django, Flask, FastAPI |
| Go | unsafe, SQL injection | Gin, Echo, GORM |
| Java | injection, crypto, deser | Spring, Jakarta |
Plus 23 more languages with parsing and metrics support.
---
Interactive TUI
Browse findings, call graphs, and taint flows with keyboard na:
<p align="center">
<img src="pics/tui-findings.png" alt="Interactive TUI showing findings" width="600">
</p>
Keyboard shortcuts: j/k na, Tab switch tabs, s filter se, / search, q quit
---
GitHub Actions
Findings appear in the GitHub Security tab automatically.
---
Qryon Dashboard - Team Features
Love the CLI? Qryon Dashboard adds powerful team features:
| Feature | CLI | Dashboard |
|---------|:---:|:---------:|
| Scan & detect | Yes | Yes |
| Historical trends | - | Yes |
| AI-powered explanations | - | Yes |
| Auto-fix suggestions | - | Yes |
| Team collaboration | - | Yes |
| Baseline diffs | - | Yes |
| PR integration | - | Yes |
| RBAC & audit logs | - | Yes |
Try Qryon Dashboard free →
---
Ad Features
<details>
<summary><strong>Cross-File Taint Tracking</strong></summary>
Track data flows across file and function boundaries:
</details>
<details>
<summary><strong>Dependency Scanning</strong></summary>
Integrated with OSV.dev for real-time C:
Supports: Cargo, npm, PyPI, Go modules, Maven
</details>
<details>
<summary><strong>HTTP API (Daemon Mode)</strong></summary>
REST API + WebSocket for IDE integration.
</details>
<details>
<summary><strong>IDE Integrations</strong></summary>
</details>
<details>
<summary><strong>WASM Plugins</strong></summary>
Extend with custom analysis rules:
</details>
---
How It Works
Qryon compiles Semgrep community rules at build time into optimized nati:
Result: No interpreter o. No Semgrep dependency. Single binary.
---
Configuration
Inline suppression:
---
Benchmarks
On a 500K LOC monorepo:
---
Contributing
Contributions welcome! See CONTRIBUTING.md.
License
MIT or Apache-2.0, at your option.
---
<di="center">
Documentation · Dashboard · Issues
Made with Rust
</div>
项目信息
开发语言:Rust
Star 数:10
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Qryon — Find security vulnerabilities in seconds. 647+ rules, 28 languages, 10x faster than Semgrep. Free & open source CLI.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | qryon - Qryon — Find security vulnerabilities in seconds. |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:02:49 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 526 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |