 安全软件
点击放大
xss-grenade - Modern XSS vulnerability scanner for real-world we
项目说明
<p align="center">
<img src="assets/xss_grenade.png" alt="XSS Grenade — automated XSS scanner" width="860">
</p>
<h1 align="center">XSS Grenade</h1>
<p align="center">
<b>Next-generation XSS detection engine for modern web applications.</b><br>
Built for real-world security testing — not just payload fuzzing.
</p>
<p align="center">
<img src=" alt="License: GPLv3">
<img src=" alt="Python 3.8+">
<img src=" alt="GUI: PyQt5">
<img src=" alt="Platform">
<img src=" alt="Status: active">
</p>
---
> [!WARNING]
> Authorized use only. Test only systems you own or ha written permission to test — an in-scope bug-bounty program or a signed engagement. Unauthorized scanning is illegal in most jurisdictions, and you are responsible for how you use this tool.
---
Why XSS Grenade?
Most scanners stop at reflections — "your input came back in the page." XSS Grenade goes further and confirms real, exploitable in a real browser.
> [!NOTE]
> New to XSS? Cross-Site Scripting is when an app renders attacker-controlled input as active code in a 's browser. A "reflection" only means your input *appeared* in the response — it isn't a bug until it actually executes. XSS Grenade does that last, hard step for you: it loads the page in a real headless Chromium and checks whether the payload *fires*.
---
What makes it different
| | |
|---|---|
| Context-aware injection | Detects *where* a parameter lands and fires only the payloads that fit that context — including multiple contexts for the same parameter. |
| Real-browser | Candidates are re-loaded in headless Chromium (Playwright). Only findings that actually execute survive. |
| Static JS taint analysis | Parses Ja to an AST and traces untrusted sources (location.*, document.referrer, window.name, postMessage) into dangerous sinks (innerHTML, eval, document.write, framework sinks). |
| Modern classes | DOM XSS · mutation XSS (mXSS) · prototype pollution → XSS · DOM clobbering · Trusted Types misconfig · SSR hydration issues. |
| Bug-bounty | postMessage abuse · JSONP callback injection · dangling markup (scriptless, CSP-resistant) · SVG/XML content-type reflection. |
| Known-C detection | Fingerprints React, Vue, Angular, Next.js, jQuery, lodash, DOMPurify… and flags with known XSS/RCE CVEs. |
---
GUI Preview
<p align="center">
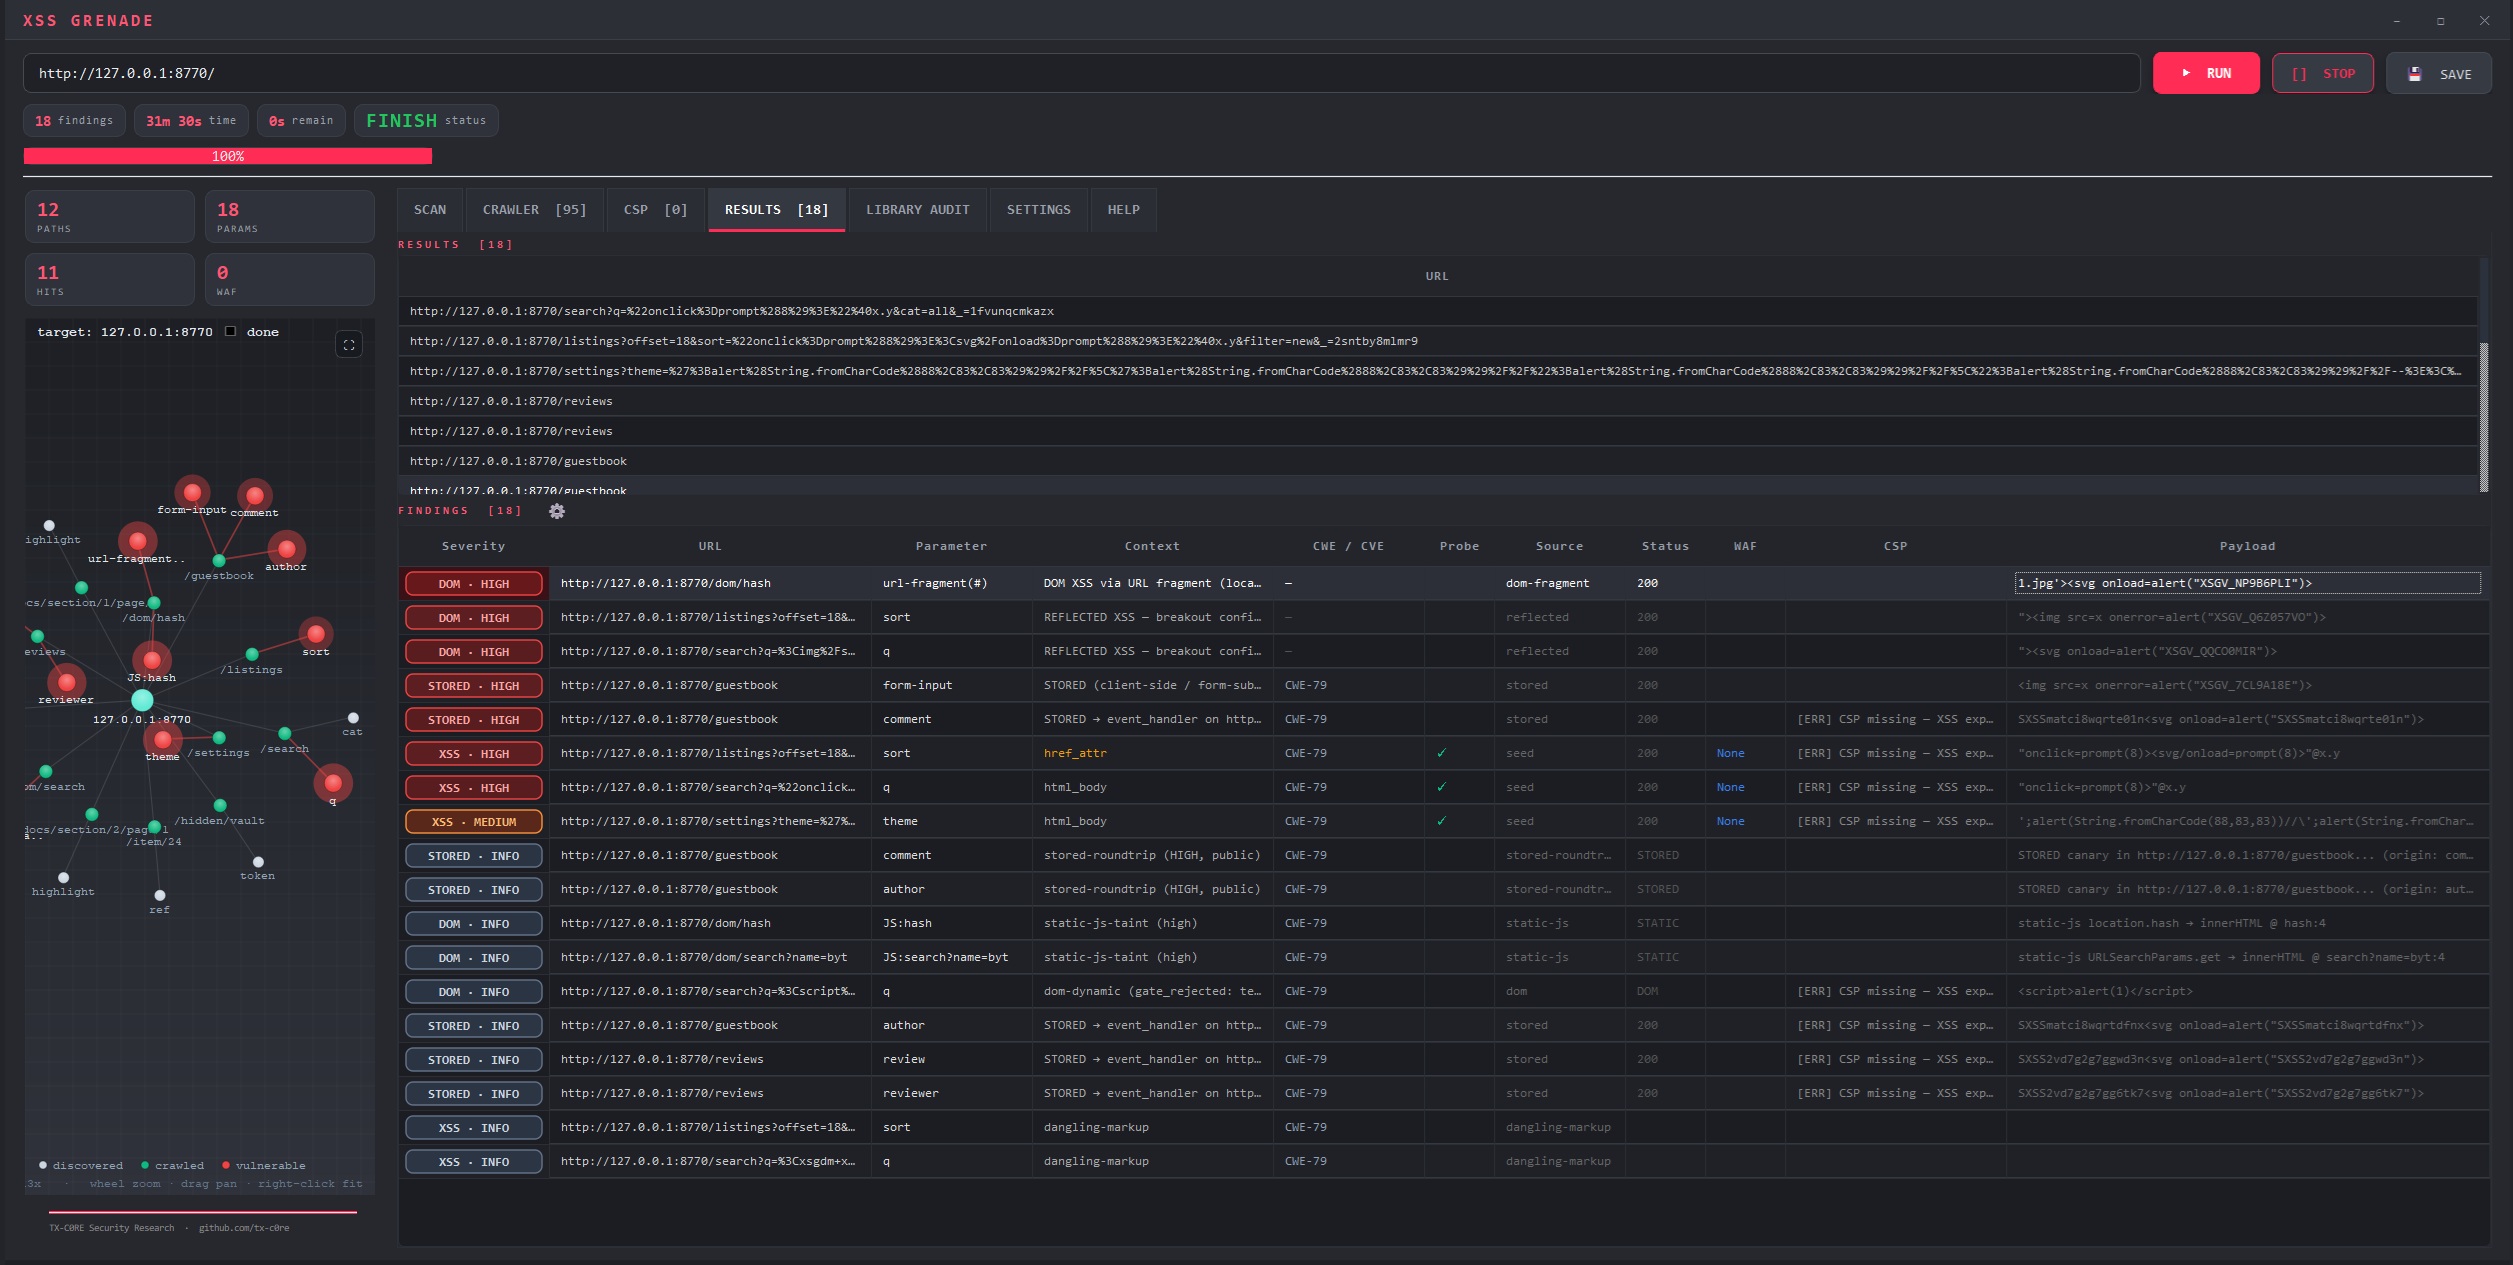
<img src="assets/screenshot.jpg" alt="XSS Grenade GUI — li graph, real-time findings, browser- results" width="960">
</p>
A li graph, real-time se findings, and browser- results — all from a single PyQt5 desktop app.
---
Quick start
> [!TIP]
> No login? No problem — but ~80% of interesting XSS hides behind authentication. Paste your session cookies in SETTINGS → Authentication to scan admin panels, profiles and dashboards. Cookies stay in memory only — ne to reports or logs.
---
Usage
1. Enter the target URL in the top bar.
2. Pick your modules in the SETTINGS tab (or keep the sensible defaults).
3. Click RUN.
4. Watch findings appear in real time — the attack-surface graph and the FINDINGS table update live.
5. Export the report: SAVE → JSON + HTML + PoC bundle.
✔ Findings are in a real browser • ✔ Output is *exploitable* , not noise.
⚡ Fast Scan mode
Enable “Smart Payloads” for a quick, high-signal first pass:
---
🧪 Detection modules
Fully modular — enable only what you need.
| Category | Capability |
|---|---|
| Crawl | SPA-aware endpoint & parameter discovery (sitemap, forms, XHR, hash routes) |
| Reflected XSS | Context-aware payload injection + breakout synthesis |
| DOM XSS | Runtime (headless) and static JS taint analysis |
| Stored XSS | Multi-canary round-trip detection |
| Prototype Pollution | Client-side sources → known gadget chains → XSS |
| CSP Bypass | Misconfig detection + JSONP / unsafe-inline / nonce-reuse bypasses |
| postMessage | Weak or absent origin → sink |
| JSONP | Callback-parameter injection |
| SVG / XML | Content-type–dri |
| WebSocket | onmessage handlers with DOM sinks |
| Headers / CORS | Header reflection + CORS misconfiguration |
| Library CVEs | front-end library / framework |
---
Reports
One-click export, three formats:
✔ Deduplicated • ✔ Se • ✔ Safe to open (payloads escaped in the report)
---
🛡️ Safety
---
Project structure
---
Roadmap
---
🤝 Contributing
Pull requests welcome. To keep the project sharp and safe:
---
⚖️ License
GNU GPLv3 — free and open source. If you modify and distribute it, you must keep it open. See LICENSE.
---
⚠️ Disclaimer
For authorized security testing only. You are solely responsible for how you use this tool; unauthorized use may be illegal.
<p align="center">
<sub>TX-C0RE Security Research · <a href="
</p>
项目信息
开发语言:Python
Star 数:9
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Modern XSS vulnerability scanner for real-world web applications. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | xss-grenade - Modern XSS vulnerability scanner for real-world we |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:03:04 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 481 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |