 安全软件
点击放大
EARScanner - Execution After Redirect (EAR) / Long Response Red
项目说明
<h1 align="center">EARScanner</h1>
<p align="center">
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
<a href="
<img src="
</a>
</p>
<p align="center">
<img src=" alt="Hacker GIF" width=200 height=200/>
</p>
This small python script can do really awesome work.
Execution After Redirect (EAR) / Long Response Redirection Scanner written in python3, Can Scan Single & Multiple URLs, MultiThreaded, Fast & Reliable, Can Fuzz All URLs of target website & then can scan them for EAR
Disclaimer
<p align="center">
:computer: This project was created only for good purposes and personal use.
</p>
THIS SOFTWARE IS PROVIDED "AS IS" WITHOUT WARRANTY OF ANY KIND. YOU MAY USE THIS SOFTWARE AT YOUR OWN RISK. THE USE IS COMPLETE RESPONSIBILITY OF THE END-USER. THE DE ASSUME NO LIABILITY AND ARE NOT RESPONSIBLE FOR ANY MISUSE OR DAMAGE CAUSED BY THIS PROGRAM.
Features
Tested On
![Kali)]() Kali Linux
![Windows)]() Windows 10
Prerequisite
How To Use in Linux
How To Use in Windows
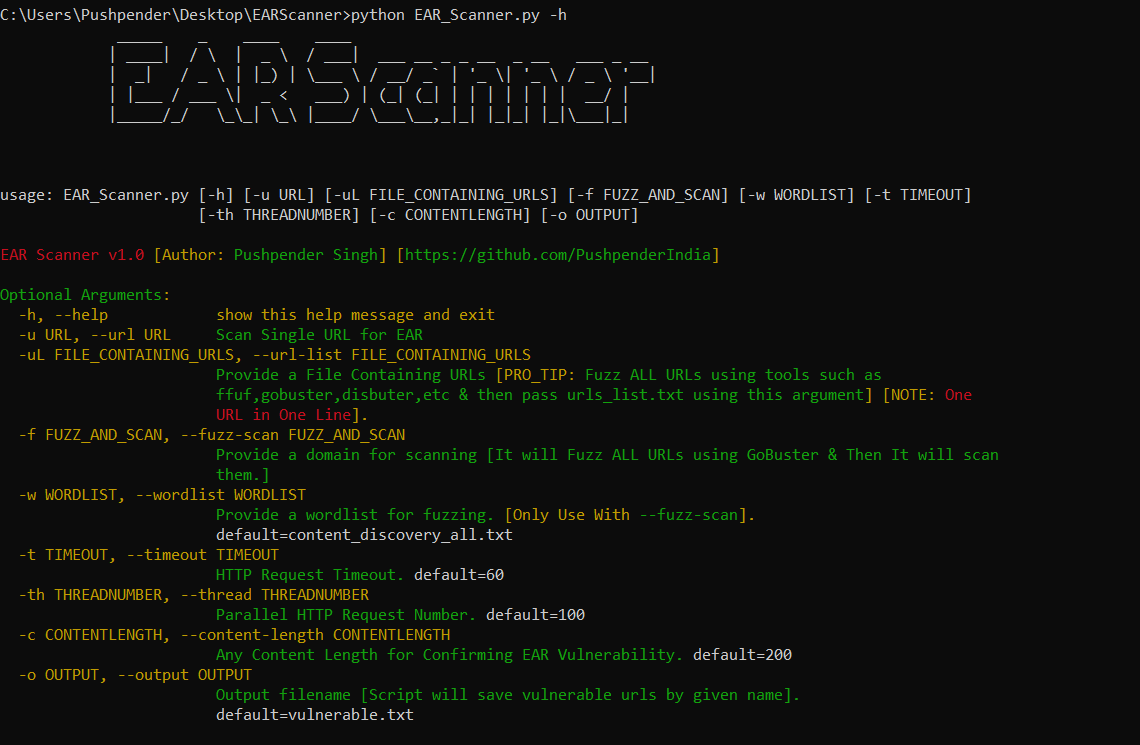
A Arguments
| Short Hand | Full Hand | Description |
| ---------- | --------- | ----------- |
| -h | --help | show this help message and exit |
| -u URL | --url URL | Scan Single URL for EAR |
| -uL FILE_CONTAINING_URLS | --url-list FILE_CONTAINING_URLS | Provide a File Containing URLs [PRO_TIP: Fuzz ALL URLs using tools such as ffuf,gobuster,disbuter,etc & then pass urls_list.txt using this argument] [NOTE: One URL in One Line]. |
| -f FUZZ_AND_SCAN | --fuzz-scan FUZZ_AND_SCAN | Provide a domain for scanning [It will Fuzz ALL URLs using GoBuster & Then It will scan them.] |
| -w WORDLIST | --wordlist WORDLIST | Provide a wordlist for fuzzing. [Only Use With --fuzz-scan]. default=content_disco.txt |
| -t TIMEOUT | --timeout TIMEOUT | HTTP Request Timeout. default=60 |
| -th THREADNUMBER | --thread THREADNUMBER | Parallel HTTP Request Number. default=100 |
| -c CONTENTLENGTH | --content-length CONTENTLENGTH | Any Content Length for Confirming EAR . default=200 |
| -o OUTPUT | --output OUTPUT | Output filename [Script will sa urls by given name]. default=.txt |
Screenshots:
#### Help Menu

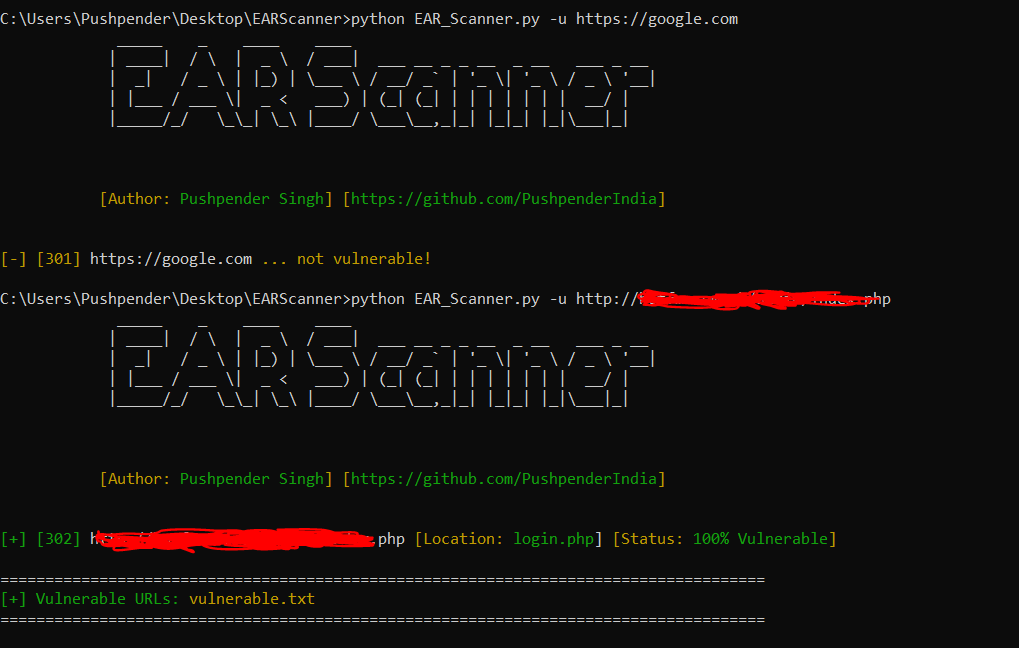
#### Single URL Scan

#### Multiple URL Scan

#### Auto FUZZ & Scan

Contribute
* All Contributors are welcome, this repo needs contributors who will improve this tool to make it best.
项目信息
开发语言:Python
Star 数:9
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Execution After Redirect (EAR) / Long Response Redirection Vulnerability Scanner written in python3, It Fuzzes All URLs of target website & then scan them for EAR展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | EARScanner - Execution After Redirect (EAR) / Long Response Red |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:03:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 409 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |