 安全软件
点击放大
FirewallXPL-Forge - Perimeter security exploitation framework — 164 mo
项目说明
<p align="center">
<img src="docs/img/firewallxpl-forge-banner_16x9.png" alt="FirewallXPL-Forge Banner" width="100%"/>
</p>
!Python


![XPL Suite]()
![Issues]()
![Last Commit]()
---
> Platform Note: This framework is designed and tested primarily on Linux (Debian/Ubuntu/Kali). Most hardware-dependent modules (wireless adapters, USB devices, raw socket access, firmware tools) require Linux. Running on Windows or macOS may cause errors or limited functionality in many modules. Linux is strongly recommended for maximum compatibility.
---
FirewallXPL-Forge
> ⚠ MIGRATION NOTICE — v2.1.0 (Final Release)
>
> FirewallXPL-Forge has been merged into EmbedXPL-Forge.
> All 81 unique modules (Fortinet, Cisco, Palo Alto, SonicWall, Sophos, Juniper, F5 BIG-IP,
> Citrix, Barracuda, A10, Imperva, NAC, pfSense, OT perimeter) are now a under
> embedxpl/modules/exploits/firewalls/ and related paths.
>
> To migrate:
>
> FirewallXPL-Forge v2.1.0 is the final standalone release. This repository will remain
> archived for reference but will not receive new modules or C.
---
Perimeter security exploitation framework — 164 modules co FW, NGFW, UTM, WAF, VPN, NAC, LB, and OT/ICS industrial firewalls across 23 and 51+ CVEs.
Author: André Henrique () \| União Geek
Language: English (en-US) — default. Português (pt-BR): README.pt-BR.md
---
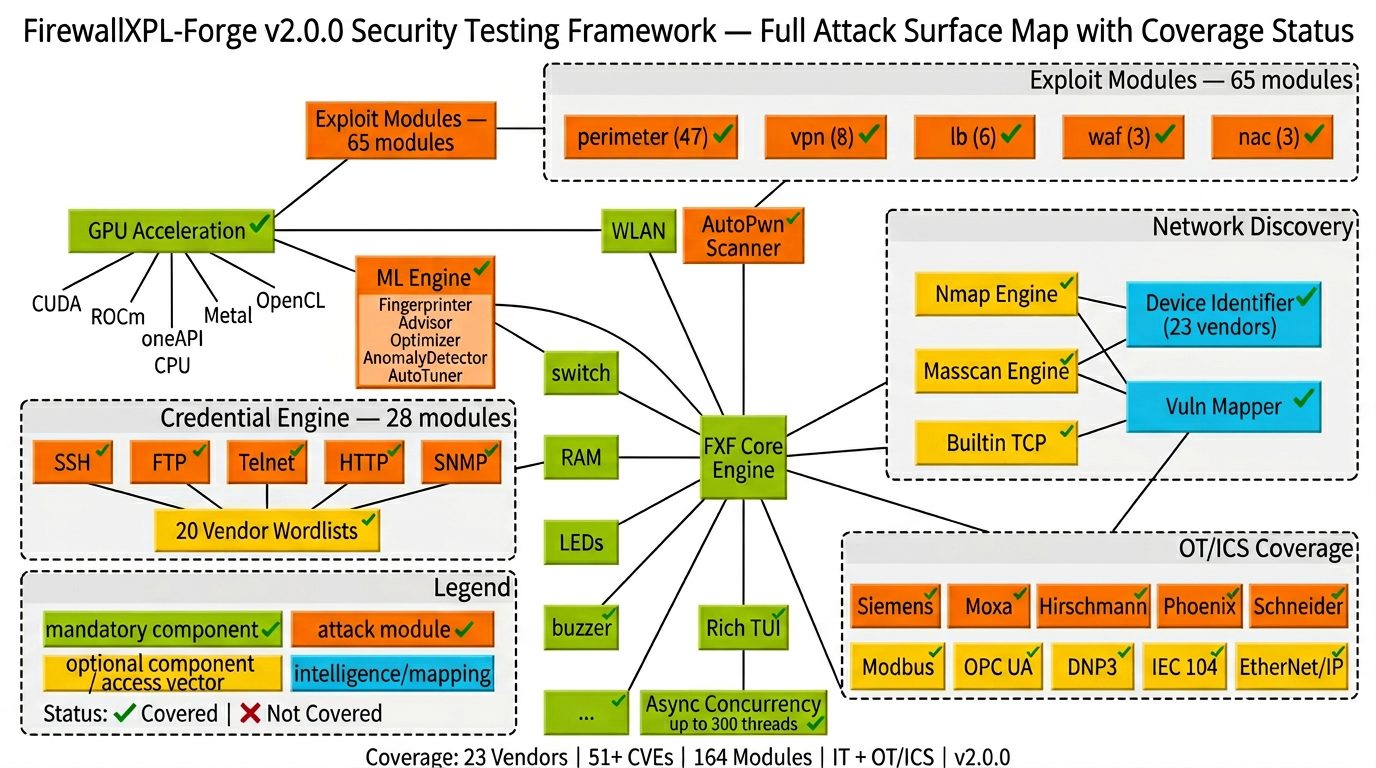
Architecture & Attack Surface Map
!FirewallXPL-Forge v2.0.0 — Full Attack Surface Map with Co Status
---
Install
En diagnostics
---
What the project does
FirewallXPL-Forge provides modules for authorized security testing against perimeter devices (pentest, lab, controlled red team). Target classes: perimeter, waf, vpn, nac, lb.
| Type | Role |
|------|------|
| exploits | Abuse known — check() + run() per module |
| creds | Default credentials and brute force against SSH, FTP, Telnet, HTTP, SNMP |
| scanners | Weakness identification; AutoPwn orchestrates all modules with Nmap-style timing (T0–T5) |
| payloads | Payload generation by architecture (ARM/MIPS/x86/x64, reverse/bind shells) |
| encoders | Payload encoding (Python, PHP, Perl) |
| generic | Cross-cutting utilities: C, SNMP, SSDP, wordlist generator |
Out of scope: IP cameras, printers, DVRs, consumer routers.
---
co (23 , 51+ CVEs)
IT Security Appliances
| | Modules | Key CVEs |
|--------|---------|----------|
| Fortinet FortiOS/FortiGate | 9 | C, C, C, C |
| Cisco ASA/FTD/IOS XE | 4 | C, C, C |
| Palo Alto PAN-OS | 6 | C (auth bypass CISA KE), C, C, C |
| F5 BIG-IP | 6 | C, C, C |
| Citrix/NetScaler | 3 | C, C, C |
| SonicWall | 6 | C, C, C |
| Ivanti/Pulse Secure | 3 | C, C+21887, C |
| Juniper SRX/EX | 2 | C, C |
| Sophos XG | 3 | C, C, C |
| Check Point | 1 | C |
| WatchGuard | 2 | XCS RCE, C |
| Zyxel USG | 3 | C, C, C |
| pfSense | 3 | C, C, C |
| Barracuda | 3 | C, C, SecureSphere SQLi |
OT/ICS Industrial Firewalls
| | Modules | Key CVEs |
|--------|---------|----------|
| Siemens SCALANCE/SINEMA/RUGGEDCOM | 3 | C, C, C |
| Moxa EDR | 2 | C (CVSS 9.9), C |
| Hirschmann EAGLE | 1 | C |
| Phoenix Contact mGuard | 1 | C |
| Schneider ConneXium/Tofino | 1 | C |
| Cisco ISA-3000 | 1 | C (CVSS 10.0) |
| Secomea GateManager | 1 | C (CVSS 10.0) |
| Ewon/HMS Cosy+ | 1 | C |
OT Protocol Bypass
Modbus TCP, OPC UA, DNP3, IEC 60870-5-104, EtherNet/IP CIP
Generic Techniques
HTTP Request Smuggling, VLAN Hopping, Heartbleed, Shellshock, SSH Auth Keys
---
Usage
Interacti
AutoPwn with ML
Non-interactive mode
Search
NSE script installer
Install the bundled firewall-specific Nmap scripts into your nmap scripts directory:
Bundled scripts:
| Script | Purpose |
|--------|---------|
| fxf-firewall-fingerprint.nse | Generic firewall fingerprinting (11 ) |
| fxf-globalprotect-detect.nse | Palo Alto GlobalProtect portal/gateway detection |
| fxf-globalprotect-auth-bypass-c.nse | C passi |
| fxf-fortios-detect.nse | Fortinet FortiOS detection |
| fxf-cisco-asa-detect.nse | Cisco ASA/FTD detection |
See docs/wiki/en-US/12-nse-scripts.md for the full NSE reference.
---
Core engines
| Engine | Description |
|--------|-------------|
| Async Concurrency | asyncio + ThreadPool (up to 300 threads) + ProcessPool + ConnectionPool + Pipeline |
| GPU Acceleration | NVIDIA CUDA, AMD ROCm, Intel oneAPI, Apple Metal, OpenCL, CPU fallback |
| ML Engine | Ser, AttackOptimizer (Thompson Sampling), AnomalyDetector, AutoTuner, CredentialMutator |
| Network Discovery | Nmap/Masscan integration + builtin TCP fallback + device identification (23 ) + mapping |
| Rich TUI | Styled banner, panels, tables, progress bars, full-screen dashboard |
---
Compatibility
| Platform | Status |
|----------|--------|
| Windows 10/11 | CI + local |
| WSL / Debian / Ubuntu | CI + local |
| Kali Linux | locally |
| macOS | CI |
Python: 3.9 through 3.13. Includes shim for removed telnetlib on 3.13+.
---
Documentation
---
BLOCO J - Attack Categories (v2.0.0)
> LEGAL WARNING: All modules in this section are for authorized security testing, research, and educational use only. Execution against production firewalls or routers without explicit written authorization is a federal crime. The authors and Uniao Geek assume no liability for misuse.
Routing Attacks
> WARNING: Routing injection attacks redirect network traffic, may disrupt perimeter security and production services. Authorized lab use only.
| Module | Path | Impact | Reference |
|--------|------|--------|-----------|
| rip_ | exploits/routing/ | HIGH | C, RFC 1058 |
| | exploits/routing/ | HIGH | RFC 3768, MITRE T1557 |
MiTM Proxies
> WARNING: MiTM proxy modules intercept and potentially modify management traffic to network devices. May expose credentials and enable unauthorized configuration changes. Requires ARP poisoning as prerequisite.
| Module | Path | Impact | Reference |
|--------|------|--------|-----------|
| tr069_mitm_proxy | exploits/mitm/ | CRITICAL | TR-069 Amendment 6, C |
| ssl_strip_embedded | exploits/mitm/ | HIGH | BlackHat DC 2009 (Marlinspike), MITRE T1557.002 |
Co Summary
| Category | Modules | Default Mode |
|----------|---------|-------------|
| Routing Attacks | rip_, | simulate=True |
| MiTM Proxies | tr069_mitm_proxy, ssl_strip_embedded | simulate=True |
| Perimeter Exploits | fortios_ssl, cisco_asa_ftd_firestarter_chain, + 10+ | simulate=True |
| Credentials | perimeter_auth_bruteforce | simulate=True |
All modules default to simulate=True. Li requires destructive=True set explicitly after re the simulated output.
---
Go
| English (default) | Português (pt-BR) |
|-------------------|---------------------|
| CONTRIBUTING.md | CONTRIBUTING.pt-BR.md |
| CODE_OF_CONDUCT.md | CODE_OF_CONDUCT.pt-BR.md |
| SECURITY.md | SECURITY.pt-BR.md |
| CONTRIBUTORS.md | CONTRIBUTORS.pt-BR.md |
---
License
BSD — see LICENSE.
---
> Author: André Henrique () \| União Geek —
---
Contact
Support / general inquiries:
Security issues: SECURITY.md
---
André Henrique
| | |
|---|---|
| GitHub | |
| X / Twitter | |
| LinkedIn | mrhenrike |
União Geek
| | |
|---|---|
| Website | uniaogeek.com.br |
| Blog | uniaogeek.com.br/blog |
| GitHub | Uniao-Geek |
| Instagram | |
---
License: BSD-3-Clause License - Copyright (c) 2026 União Geek
Created by: André Henrique () | União Geek
Leia em Português - Command co - Wiki
项目信息
开发语言:Python
Star 数:9
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Perimeter security exploitation framework — 164 modules covering FW, NGFW, UTM, WAF, VPN, NAC, LB, and OT/ICS firewalls (Fortinet, Cisco, Palo Alto, F5, Citrix, Check Point, SonicWall, Ivanti, Siemens, Moxa, +13 vendors). GPU-accelerated, ML-driven, async concurrency, Rich TUI.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | FirewallXPL-Forge - Perimeter security exploitation framework — 164 mo |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:04:18 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 504 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |