 安全软件
点击放大
CMScan - CMS scanner (Wordpress, Joomla, Drupal...)
项目说明
CMScan
No API key, no limitation
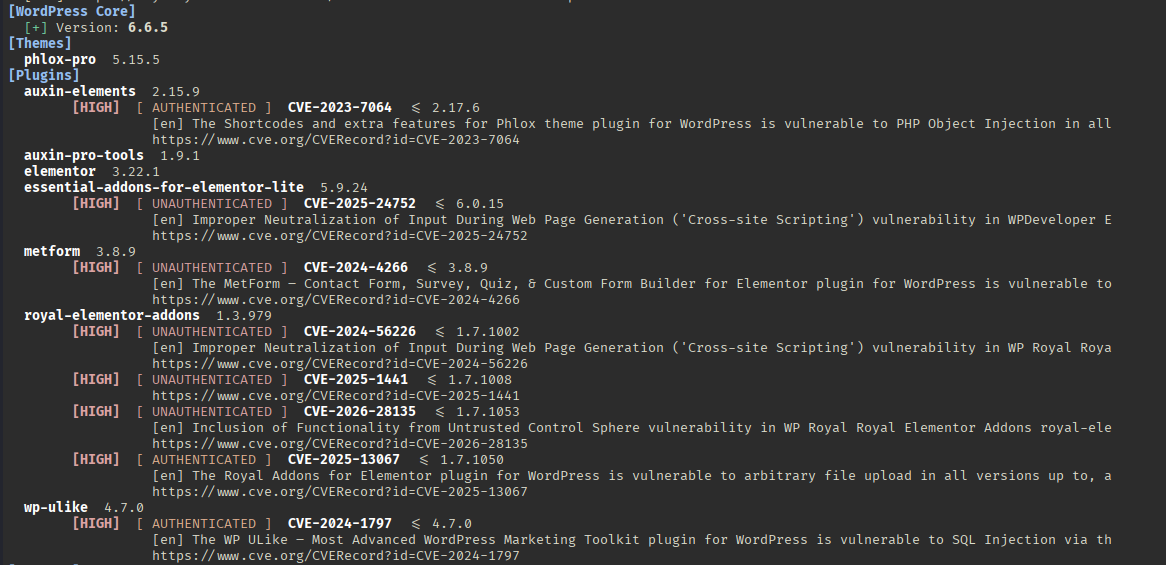
!CMScan screenshot
CMScan is a unified security scanner for WordPress, Drupal, Joomla, PrestaShop, Shopify, Magento, TYPO3, and OpenCart websites.
It detects CMS , enumerates users, checks for known , and exports the results to CSV.
Features
- wp.net
- OSV.dev
- FriendsOfPHP Security Ad
- NVD API
--host mode support for shared hosting enInstallation
Using the installer (recommended)
Usage
📖 CMScan Documentation
CMScan is a multi-CMS security scanner designed to detect CMS installations, , themes, plugins/modules, known , and exposed sensiti.
---
Command-line Options
| Option | Description |
|--------|-------------|
| -L <TARGET> | Scan a single URL or a text file containing multiple URLs. |
| -v, -- | mode. Display every HTTP request and detection. |
| --force | Force scanning of all supported CMSs, even if WordPress is detected first. |
| --stealth | Disable exposed-path checks to reduce the number of HTTP requests and make scans more discreet. |
| -o, --output | Output CS (default: automatically generated). |
| --update | Update databases (WordPress and FriendsOfPHP). |
---
Usage Examples
Scan a single website
mode
Scan multiple targets
Stealth mode
Force detection of every supported CMS
Combine multiple options
Update databases
---
Detection Priority
CMScan attempts to determine the CMS using the following priority order:
1. readme.txt / README.txt
2. Translation files (*.pot, Project-Id-)
3. ES module imports (e.g. workbox-v7.3.0)
4. HTML meta tags and comments (passi)
5. ?ver= parameters in asset URLs (fallback)
---
Automatic Updates
CMScan can automatically check GitHub for new releases.
When a newer is a, it downloads the update and restarts automatically.
---
Generated Files
The CS includes:
---
Stealth Mode (--stealth)
Stealth mode disables exposed-path enumeration to reduce the number of HTTP requests and lower the scan footprint.
Typical skipped paths include:
/wp-config.php.*/.git//.env/wp-content/debug.log/wp-content/uploads//xmlrpc.php/wp-admin//wp-login.php/wp-cron.php/wp-content/plugins//wp-content/themes//readme.html/license.txt---
Supported CMS
| CMS | Features |
|------|----------|
| ✅ WordPress | Core , themes, plugins, |
| ✅ Drupal | , modules, exposed paths |
| ✅ Joomla | , extensions, exposed paths |
| ✅ PrestaShop | , modules, exposed paths |
| ✅ Magento | , extensions, exposed paths |
| ✅ Shopify | Theme detection |
| ✅ TYPO3 | , extensions |
| ✅ OpenCart | , extensions |
---
Legal Notice
CMScan should only be used against systems that you own or for which you ha written authorization.
Unauthorized security testing may applicable laws.
---
License
CMScan is released under the MIT License.
You are free to use, modify, and redistribute it in accordance with the license terms.
项目信息
开发语言:Python
Star 数:9
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕CMS scanner (Wordpress, Joomla, Drupal...)展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | CMScan - CMS scanner (Wordpress, Joomla, Drupal...) |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:04:22 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 507 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |