 安全软件
点击放大
项目说明
mycop
AI Code Security Scanner — detect and auto-fix in AI-generated code.
![CI]()
![Crates.io]()
![Downloads]()

![GitHub stars]()
![Made with Rust]()
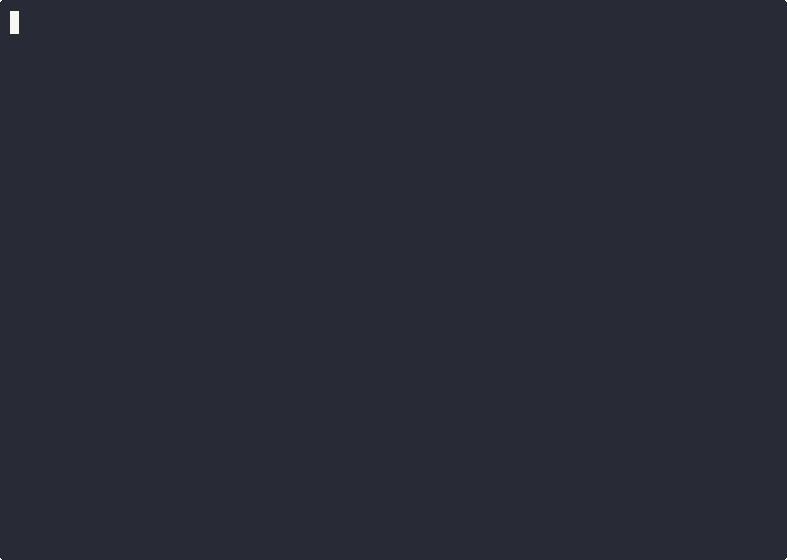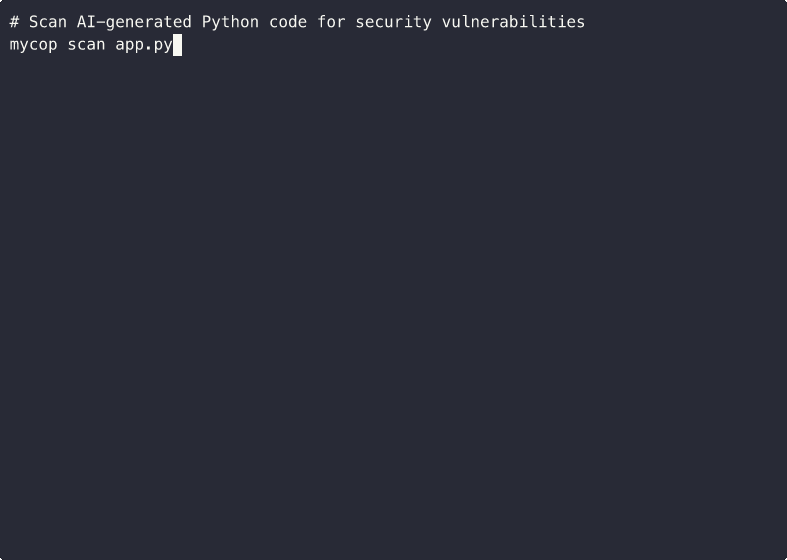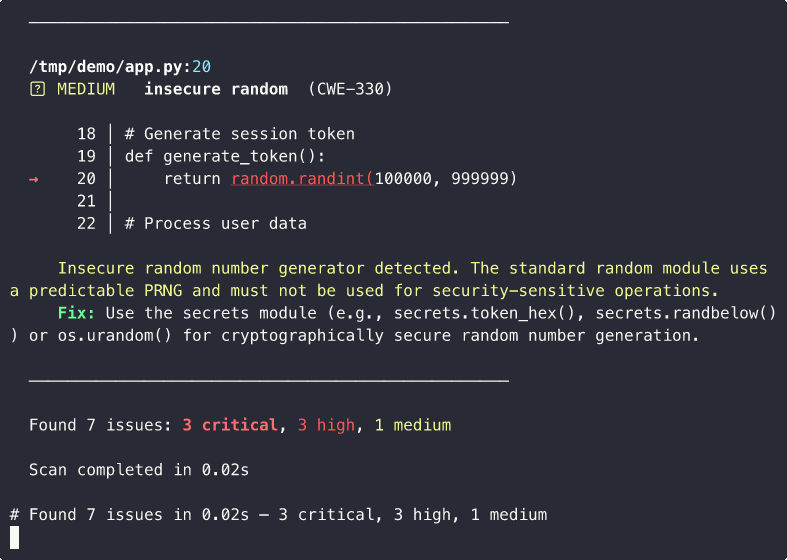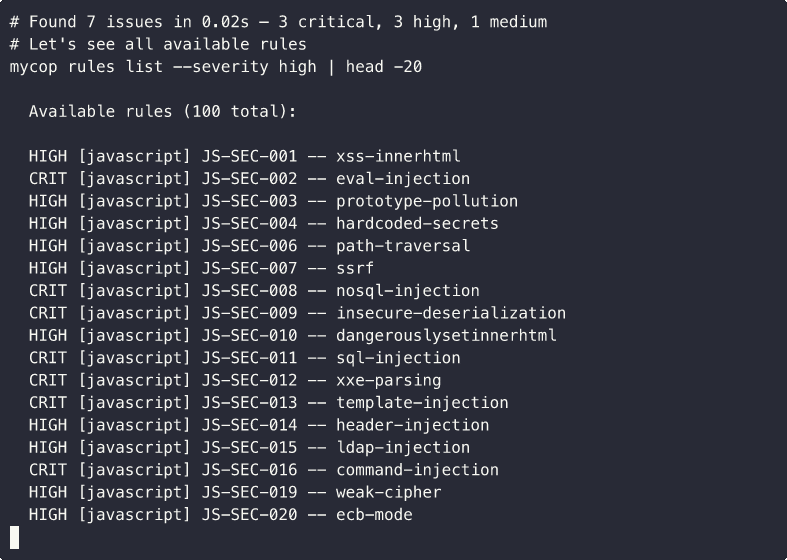
mycop scans Python, Ja, TypeScript, Go, and Ja for security using pattern matching, AST analysis, and optional AI-powered explanations and auto-fix. It ships with 200 built-in security rules co OWASP Top 10 and CWE Top 25 categories.
<p align="center">
<img src="docs/demo.gif" alt="mycop demo — scanning Python code for security " width="750">
</p>
Why mycop?
AI-generated code is fast, but it is not safe. Research from shows that 45% of AI-generated code contains security . Copilot, ChatGPT, and other AI assistants produce functional code that often includes SQL injection, hardcoded secrets, command injection, and other critical flaws.
mycop was built specifically to solve this problem:
mycop fix command rewrites insecure code using AI while preserving functionality.mycop scan . and go.Installation
Install script (macOS / Linux)
Homebrew
Cargo
Docker
Build from source
Quick Start
Commands
mycop scan
Scan files for security .
Exit code 1 when findings meet the --fail-on threshold (default: high).
mycop fix
Auto-fix security using AI. Groups all findings per file, sends the entire file to an AI provider, and writes back the fixed .
mycop review
Deep AI-powered security review of a single file. Goes beyond rule matching to find logic flaws, race conditions, and architectural issues.
mycop init
Generate a .scanrc.yml configuration file. Automatically detects your project type (Python, Ja/TypeScript, Rust) and pre-populates language-specific ignore patterns.
mycop rules list
List all a security rules.
mycop deps check
Check dependencies for issues (hallucinated packages).
mycop mcp
Start an MCP (Model Context Protocol) server o for agentic tool integration. This lets AI coding assistants call mycop's scanning, fixing, and review capabilities directly.
Tools exposed:
| Tool | Description |
|------|-------------|
| scan | Scan files/directories for with se filtering |
| list_rules | Browse/filter the 200 built-in security rules |
| explain_finding | Detailed explanation of a specific finding with CWE/OWASP info |
| review | Deep AI security review of a file |
| check_deps | Detect hallucinated packages in dependencies |
> Note: The CLI mycop fix command is still a for standalone use. In MCP mode, the agent reads scan findings (with fix_hint) and applies fixes directly — no redundant AI-to-AI call needed.
Resources: mycop://rules/catalog (full JSON catalog) and mycop://config/schema (config template).
Configure in Claude Code (~/.claude/settings.json):
Configure in Cursor (.cursor/mcp.json):
Configure in Windsurf (.windsurf/mcp.json):
Works with any MCP-compatible client including Codex CLI, Gemini CLI, and other agentic IDEs.
Inline Ignore
Suppress specific findings with inline comments:
Works with # (Python), // (Ja/TypeScript/Go/Ja styles. Place the comment on the same line or the line above.
AI Pro
mycop auto-detects a AI pro in this order:
1. Claude CLI — claude command installed
2. Anthropic API — ANTHROPIC_API_KEY en
3. OpenAI API — OPENAI_API_KEY en
4. Ollama — local Ollama ser on port 11434
5. Rule-based — offline fallback using fix hints from rules
O with --ai-provider:
Configuration
Create a .scanrc.yml (or .mycop.yml) in your project root, or run mycop init to generate one:
CLI flags always take priority o file .
Security Rules
200 built-in rules (50 Python + 50 Ja + 50 Go + 50 Ja OWASP Top 10, CWE Top 25, and more:
| Category | Python | Ja |
|----------|--------|------------|
| SQL Injection (CWE-89) | PY-SEC-001, PY-SEC-042 | JS-SEC-011 |
| Command Injection (CWE-78) | PY-SEC-002, PY-SEC-045, PY-SEC-050 | JS-SEC-016 |
| Hardcoded Secrets (CWE-798) | PY-SEC-003, PY-SEC-034, PY-SEC-043 | JS-SEC-004, JS-SEC-034 |
| Insecure Random (CWE-330) | PY-SEC-004 | JS-SEC-005 |
| Eval/Exec Injection (CWE-95) | PY-SEC-005 | JS-SEC-002, JS-SEC-049 |
| Path Tra (CWE-22) | PY-SEC-006, PY-SEC-037 | JS-SEC-006, JS-SEC-037 |
| Insecure Deserialization (CWE-502) | PY-SEC-007 | JS-SEC-009 |
| Missing Auth (CWE-862) | PY-SEC-008 | — |
| XSS (CWE-79) | PY-SEC-009, PY-SEC-044 | JS-SEC-001, JS-SEC-010, JS-SEC-041 |
| Log Injection (CWE-117) | PY-SEC-010 | — |
| SSRF (CWE-918) | PY-SEC-011 | JS-SEC-007 |
| XXE (CWE-611) | PY-SEC-012 | JS-SEC-012 |
| LDAP Injection (CWE-90) | PY-SEC-013 | JS-SEC-015 |
| Template Injection (CWE-1336) | PY-SEC-014 | JS-SEC-013 |
| Header Injection (CWE-113) | PY-SEC-015 | JS-SEC-014 |
| XPath Injection (CWE-643) | PY-SEC-016 | — |
| Weak Hash MD5/SHA1 (CWE-328) | PY-SEC-017, PY-SEC-018 | JS-SEC-017, JS-SEC-018 |
| Weak Cipher (CWE-327) | PY-SEC-019, PY-SEC-020 | JS-SEC-019, JS-SEC-020, JS-SEC-022 |
| Hardcoded I) | PY-SEC-021 | — |
| Insecure TLS (CWE-295) | PY-SEC-022 | JS-SEC-021 |
| JWT None Algorithm (CWE-345) | PY-SEC-023 | JS-SEC-023 |
| Weak Password Hash (CWE-916) | PY-SEC-024 | — |
| Session Fixation (CWE-384) | PY-SEC-025 | JS-SEC-024, JS-SEC-025 |
| Missing Security Headers (CWE-319) | PY-SEC-026 | JS-SEC-026 |
| Open Redirect (CWE-601) | PY-SEC-027 | JS-SEC-027 |
| CORS Misconfiguration (CWE-942) | PY-SEC-028 | JS-SEC-028 |
| Mass Assignment (CWE-915) | PY-SEC-029 | JS-SEC-030 |
| IDOR (CWE-639) | PY-SEC-030 | JS-SEC-029 |
| Debug Mode (CWE-215) | PY-SEC-031 | JS-SEC-031 |
| Error Info Leak (CWE-209) | PY-SEC-032 | JS-SEC-032 |
| Sensitive Data Logging (CWE-532) | PY-SEC-033 | JS-SEC-033 |
| Arbitrary File Upload (CWE-434) | PY-SEC-035 | JS-SEC-035 |
| Insecure Temp Files (CWE-377) | PY-SEC-036 | — |
| Zip Slip (CWE-22) | PY-SEC-037 | JS-SEC-037 |
| Unencrypted Transport (CWE-319) | PY-SEC-038 | JS-SEC-038 |
| Prototype Pollution (CWE-1321) | — | JS-SEC-003 |
| NoSQL Injection (CWE-943) | — | JS-SEC-008 |
| Timing Attack (CWE-208) | PY-SEC-046 | JS-SEC-046 |
| ReDoS (CWE-1333) | PY-SEC-047 | JS-SEC-047 |
| TOCTOU (CWE-367) | PY-SEC-048 | JS-SEC-048 |
| Bare/Empty Catch (CWE-390) | PY-SEC-040 | JS-SEC-040 |
Run mycop rules list to see all 200 rules with their se levels.
Comparison
How does mycop compare to other security tools?
| Feature | mycop | Semgrep | Snyk Code | Bandit | ESLint Security |
|---------|:-----:|:-------:|:---------:|:------:|:---------------:|
| AI code focus | Yes | No | No | No | No |
| Built-in rules (no download) | 200 | Requires registry | Cloud-based | ~100 (Python only) | ~30 (JS only) |
| AI auto-fix | Yes | No | Paid | No | No |
| Multi-language | Py, JS, TS, Go, Java | 30+ | 10+ | Python only | JS/TS only |
| MCP server | Yes | No | No | No | No |
| Zero config | Yes | Needs rules config | Needs project setup | Minimal | Needs .eslintrc |
| SARIF output | Yes | Yes | Yes | Yes | |
| Price | Free (MIT) | Free tier / Paid | Paid | Free | Free |
mycop is purpose-built for the AI coding era. Other tools are general-purpose scanners that were designed before AI code generation became mainstream.
Output Formats
Integrations
MCP Server (Agentic Tools)
mycop includes a built-in MCP server that exposes all capabilities to agentic coding tools. Run mycop mcp and configure your tool — see the mycop mcp section above for setup instructions.
Supported clients: Claude Code, Cursor, Windsurf, Codex CLI, Gemini CLI, and any MCP-compatible IDE or agent.
A on:
GitHub Action
Add mycop to your CI pipeline with the official GitHub Action:
| Input | Default | Description |
|-------|---------|-------------|
| paths | . | Files or directories to scan |
| se | | Minimum se to report |
| fail-on | high | Minimum se to fail the check |
| format | terminal | Output format (terminal, json, sarif) |
| | latest | mycop to install |
| diff-only | false | Only scan files changed in the PR |
Upload SARIF results to GitHub Code Scanning:
Pre-commit Hook
Add mycop as a pre-commit hook:
VS Code Extension (Coming Soon)
The / directory contains a VS Code extension that provides:
See /README.md for setup instructions.
Docker
Contributing
Contributions are welcome! Whether it is a bug report, a new security rule, a feature request, or a pull request, we appreciate your help in making mycop better.
To get started:
1. Fork the repository and create your branch from main.
2. Make your changes and ensure all checks pass:
3. Open a pull request with a clear description of your changes.
Browse open issues to find something to work on, or open a new one to suggest an impro.
If you find mycop useful, consider sponsoring the project to support ongoing de.
Star History
![Star History Chart]()
License
MIT
项目信息
开发语言:Rust
Star 数:9
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕安全软件相关项目展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | mycop - 安全软件相关项目 |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:04:23 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 290 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |