 安全软件
点击放大
HADES_SENTINEL - Local-only network vulnerability scanner that auto
项目说明
<di="center">
<img src="assets/logo_hades_sentinel_doc.png" alt="HADES SENTINEL" height="160">
HADES SENTINEL
From to ISO 27001 compliance in one click.
🇬🇧 English | 🇪🇸 Español


![Stars]()
![Issues]()
The 100% local network audit agent that turns a live LAN scan into a white-labeled, ISO 27001:2022-aligned executi — for CISOs, compliance teams, and pentesters who can't send data to the cloud.
🖥️ The audit in action — what runs on your network (100% on-premise, zero cloud)
<table>
<tr>
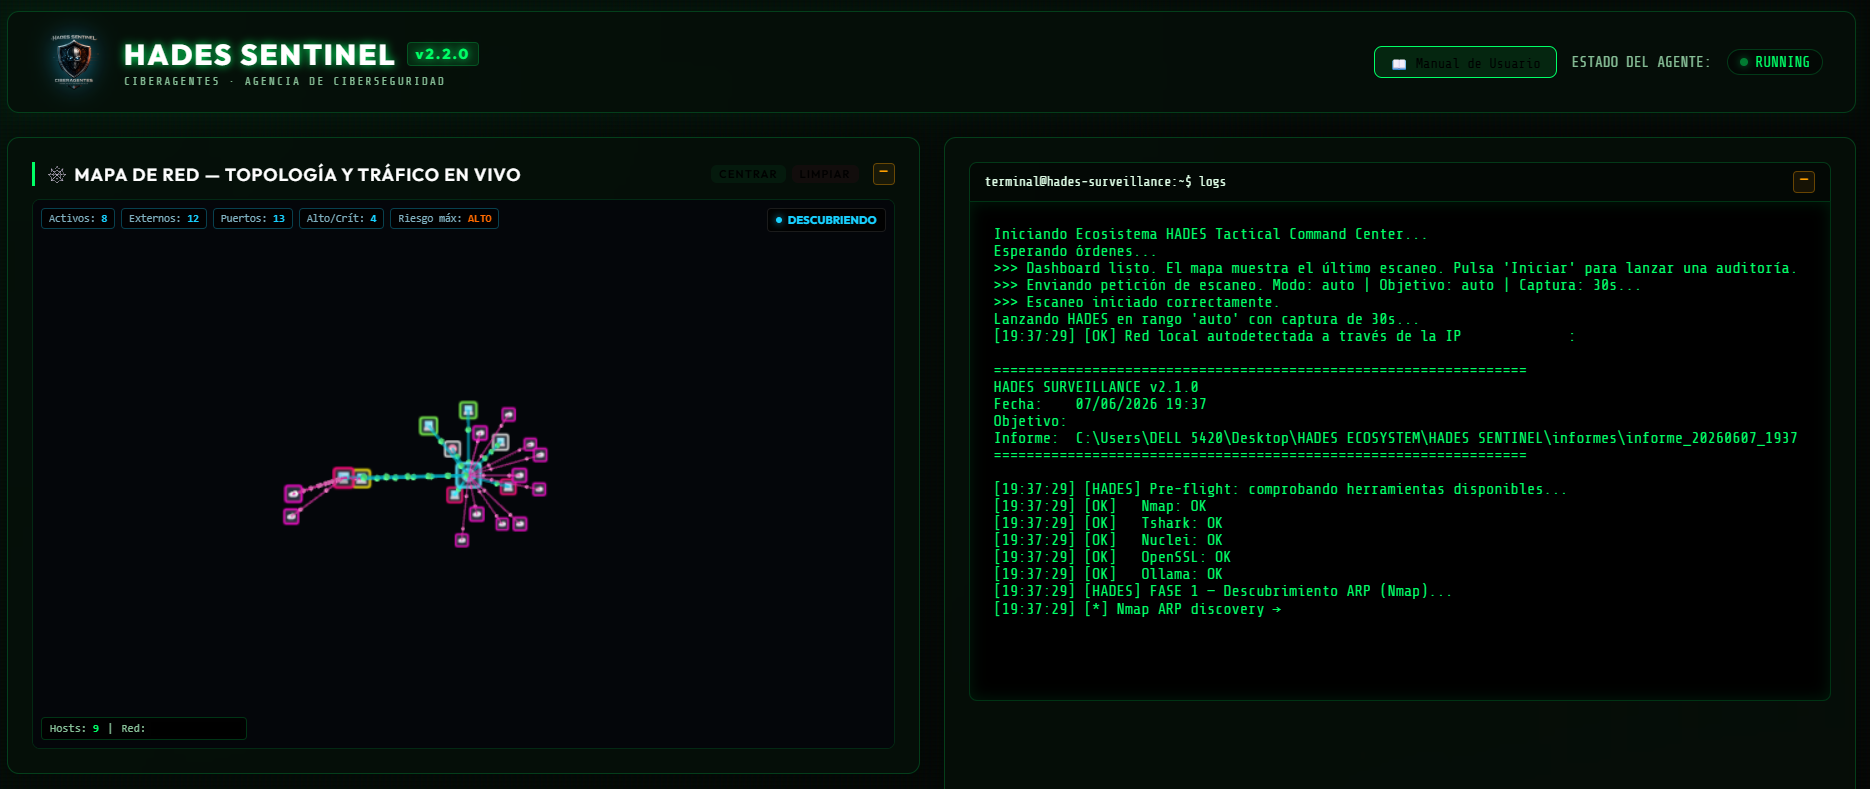
<td align="center"><img src="assets/screenshots/01_dashboard_live.png" alt="HADES dashboard with li map and console" width="320"><br><sub><b>Li map + console</b><br>9 hosts, 12 external IPs, 4 critical findings detected in real time</sub></td>
<td align="center"><img src="assets/screenshots/02_dashboard_resources.png" alt="HADES dashboard control panel with system resources and Ollama AI" width="320"><br><sub><b>Control panel + local AI</b><br>5-phase scan flow, CPU/GPU/RAM monitors, Ollama LLM running on-device</sub></td>
<td align="center"><img src="assets/screenshots/03_traffic_capture.png" alt="HADES Tshark li capture output" width="320"><br><sub><b>Li capture</b><br>Tshark sniff with protocol breakdown and per-host activity</sub></td>
</tr>
</table>
📄 What your business receives — board-ready, audit-ready, white-labeled with your brand
<table>
<tr>
<td align="center"><img src="assets/screenshots/04_se.png" alt="HADES se findings table from the ISO 27001 report" width="320"><br><sub><b>Findings by se</b><br>every asset classified Critical / High / Medium / Low with business impact</sub></td>
<td align="center"><img src="assets/screenshots/05_risk_matrix.png" alt="HADES color-coded risk matrix probability " width="320"><br><sub><b>Color-coded risk matrix</b><br>probability × impact, deterministic scoring, board-ready</sub></td>
<td align="center"><img src="assets/screenshots/06_iso27001_mapping.png" alt="HADES ISO 27001 Annex A control mapping table" width="320"><br><sub><b>ISO 27001 Annex A mapping</b><br>findings auto-mapped to controls A.5.x / A.8.x — sa per audit</sub></td>
</tr>
</table>
⭐ Star this repo if it saved you a compliance audit.
</div>
---
🎯 Why HADES?
.docx.---
📦 What you get
Every audit produces a timestamped folder containing:
1. Executi — INFORME_EJECUTI.docx aligned to ISO/IEC 27001:2022, white-labeled with your brand.
2. Technical Consolidated Report — INFORME_MAESTRO.md with full e, host-by-host.
3. Risk Matrix — color-coded (critical / high / medium / low) with deterministic scoring.
4. Traffic Capture — trafico_red.txt with flows, ports, protocols and external endpoints contacted.
5. ISO 27001 Annex A Control Mapping — each finding tied to its corresponding control (A.5–A.8).
6. Per-Host Detail Reports — host_XXX_XXX_XXX_XXX.txt with ports, banners, TLS audit and C.
---
🚀 Quick start
Prefer headless? Run LANZAR_HADES.bat for a full pipeline audit in console mode.
---
🧠 How it works
A deterministic 5-phase pipeline. The AI layer (local Ollama) is consultati — risk scoring stays e.
Phase 4 per host runs: deep Nmap (ports, services, OS) → Nuclei (web vulns) → OpenSSL (TLS audit) → Ollama (consultati only).
---
🎨 Customize your brand (white-label compliance)
Open hades_report_docx.py and edit the BRANDING dict at the top:
Every .docx report now ships with your customer's logo, colors and footer. Resell the audit under your own brand.
---
🏗️ Architecture
| File | Role |
|------|------|
| hades_server.py | Dashboard backend (port 8080, CSRF-protected, multi-thread). |
| hades_sur.py | Pipeline orchestrator (5 phases). |
| hades_win_master_ad.py | Tool engine — Nmap, Nuclei, Tshark, OpenSSL, Ollama. |
| hades_report_docx.py | ISO 27001:2022 .docx report generator. |
| LANZAR_DASHBOARD.bat | One-click dashboard launcher. |
| LANZAR_HADES.bat | One-click console audit. |
| DETENER_HADES.bat | Emergency stop (kills all agent processes cleanly). |
External binaries are resolved from WIN_PATHS in hades_win_master_ad.py — edit it if you installed Nmap/Tshark/OpenSSL/Nuclei in a non-standard path.
---
🔐 Security & Privacy
127.0.0.1:11434. Risk scoring is deterministic and traceable to e..gitignore excludes informes/ — scan results (IPs, MACs, banners, TLS data) never leak into control.nmap.exe, tshark.exe, nuclei.exe, openssl.exe, python*.exe) — no orphan processes.---
⚖️ Legal notice
For authorized security audits only. Use exclusively on networks and systems you own or ha written permission to test. Unauthorized scanning may be illegal in your jurisdiction (e.g. Chile Law 21.459, EU Budapest Con, US CFAA). The authors accept no liability for misuse. You are solely responsible for how you use this tool.
---
📜 License
Dual-licensed under MIT OR Apache-2.0. Pick whichever fits your project. See LICENSE and LICENSE-APACHE.
---
🤝 Contributing
PRs, issues and feature requests are welcome. Please read CONTRIBUTING.md and use the templates in .github/ISSUE_TEMPLATE/ before opening an issue.
Using HADES in your organization? Open an issue and tell us — we'll feature your use case (with permission).
---
<di="center">
⭐ Found this useful? Star the repo — it's the single biggest signal that keeps this project alive.
</div>
---
---
🇪🇸 Español
<di="center">
<img src="assets/logo_hades_sentinel_doc.png" alt="HADES SENTINEL" height="160">
HADES SENTINEL
De a compliance ISO 27001 en un click.


El agente local de auditoría de red que con un escaneo LAN en vivo en un informe ejecutivo .docx con tu marca, alineado a ISO 27001:2022 — para CISOs, equipos de compliance y pentesters que no pueden enviar datos a la nube.
🖥️ La auditoría en acción — lo que corre en tu red (100 % on-premise, cero nube)
<table>
<tr>
<td align="center"><img src="assets/screenshots/01_dashboard_live.png" alt="Dashboard HADES con mapa de red en vivo y consola" width="320"><br><sub><b>Mapa de red + consola en vivo</b><br>9 hosts, 12 IPs externas, 4 hallazgos críticos detectados en tiempo real</sub></td>
<td align="center"><img src="assets/screenshots/02_dashboard_resources.png" alt="Panel de control HADES con recursos del sistema y Ollama IA" width="320"><br><sub><b>Panel de control + IA local</b><br>flujo de 5 fases, monitores CPU/GPU/RAM, Ollama LLM en el dispositivo</sub></td>
<td align="center"><img src="assets/screenshots/03_traffic_capture.png" alt="Captura de tráfico Tshark en vivo de HADES" width="320"><br><sub><b>Captura de tráfico en vivo</b><br>sniffing Tshark con desglose por protocolo y actividad por host</sub></td>
</tr>
</table>
📄 Lo que tu negocio recibe — listo para directorio, listo para auditoría, con tu marca
<table>
<tr>
<td align="center"><img src="assets/screenshots/04_se.png" alt="Tabla de hallazgos clasificados por se de HADES" width="320"><br><sub><b>Hallazgos por se</b><br>cada acti Crítico / Alto / Medio / Bajo con impacto al negocio</sub></td>
<td align="center"><img src="assets/screenshots/05_risk_matrix.png" alt="Matriz de riesgo color-coded probabilidad de HADES" width="320"><br><sub><b>Matriz de riesgo coloreada</b><br>probabilidad × impacto, scoring determinista, lista para directorio</sub></td>
<td align="center"><img src="assets/screenshots/06_iso27001_mapping.png" alt="Tabla de mapeo a controles ISO 27001 Anexo A de HADES" width="320"><br><sub><b>Mapeo a ISO 27001 Anexo A</b><br>hallazgos auto-mapeados a controles A.5.x / A.8.x — ahorra semanas por auditoría</sub></td>
</tr>
</table>
⭐ Dale star si te ahorró una auditoría de compliance.
</div>
---
🎯 ¿Por qué HADES?
.docx.---
📦 Lo que obtienes
Cada auditoría crea una carpeta con marca temporal que contiene:
1. Informe Ejecutivo — INFORME_EJECUTI.docx alineado a ISO/IEC 27001:2022, con tu marca.
2. Informe Técnico Consolidado — INFORME_MAESTRO.md con e completa, host por host.
3. Matriz de Riesgo — coloreada (crítico / alto / medio / bajo) con scoring determinista.
4. Captura de Tráfico — trafico_red.txt con flujos, puertos, protocolos y endpoints externos contactados.
5. Mapeo a Controles del Anexo A de ISO 27001 — cada hallazgo ligado a su control correspondiente (A.5–A.8).
6. Reportes de Detalle por Host — host_XXX_XXX_XXX_XXX.txt con puertos, banners, auditoría TLS y C.
---
🚀 Inicio rápido
¿Prefieres modo headless? Ejecuta LANZAR_HADES.bat para una auditoría completa en consola.
---
🧠 Cómo funciona
Pipeline determinista de 5 fases. La capa de IA (Ollama local) es consulti decisoria — el scoring de riesgo se mantiene basado en e.
La Fase 4 por host ejecuta: Nmap profundo (puertos, ser, SO) → Nuclei (vulns web) → OpenSSL (auditoría TLS) → Ollama (análisis consultivo).
---
🎨 Personaliza tu marca (compliance white-label)
Abre hades_report_docx.py y edita el dict BRANDING al inicio:
Cada informe .docx lleva el logo, colores y pie de página de tu cliente. Revende la auditoría bajo tu propia marca.
---
🏗️ Arquitectura
| Archivo | Rol |
|---------|-----|
| hades_server.py | Backend del dashboard (puerto 8080, CSRF, multihilo). |
| hades_sur.py | Orquestador del pipeline (5 fases). |
| hades_win_master_ad.py | Motor de herramientas — Nmap, Nuclei, Tshark, OpenSSL, Ollama. |
| hades_report_docx.py | Generador del informe ISO 27001:2022 .docx. |
| LANZAR_DASHBOARD.bat | Lanzador del dashboard en un click. |
| LANZAR_HADES.bat | Auditoría por consola en un click. |
| DETENER_HADES.bat | Parada de emergencia (cierre limpio de procesos). |
Los binarios externos se resuel WIN_PATHS en hades_win_master_ad.py — edítalo si instalaste Nmap/Tshark/OpenSSL/Nuclei en rutas no estándar.
---
🔐 Seguridad y Pri
127.0.0.1:11434. El scoring de riesgo es determinista y trazable a e..gitignore excluye informes/ — los resultados (IPs, MACs, banners, datos TLS) nunca acaban en el control de .nmap.exe, tshark.exe, nuclei.exe, openssl.exe, python*.exe) — sin procesos huérfanos.---
⚖️ Aviso legal
Solo para auditorías de seguridad autorizadas. Úsala exclusi en redes y sistemas de tu propiedad o sobre los que tengas permiso explícito por escrito. El escaneo no autorizado puede ser ilegal en tu jurisdicción (p. ej. Chile Ley 21.459, Convenio de Budapest a ni, CFAA en EE. UU.). Los autores no se hacen responsables del mal uso. Tú eres el único responsable del uso que le des.
---
📜 Licencia
Licencia dual MIT OR Apache-2.0. Elige la que mejor encaje con tu proyecto. Ver LICENSE y LICENSE-APACHE.
---
🤝 Contribuir
PRs, issues y solicitudes de features son bien. Lee CONTRIBUTING.md y usa las plantillas en .github/ISSUE_TEMPLATE/ antes de abrir un issue.
¿Usas HADES en tu organización? Abre un issue y cuéntanoslo — destacaremos tu caso de uso (con tu permiso).
---
<di="center">
⭐ ¿Te resultó útil? Dale star al repo — es la señal más fuerte que mantiene vivo este proyecto.
</div>
项目信息
开发语言:Python
Star 数:8
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Local-only network vulnerability scanner that auto-maps findings to ISO/IEC 27001:2022 Annex A controls and generates white-label executive .docx reports. Air-gapped, zero-cloud, zero-telemetry. Built on Nmap, Nuclei, Tshark, OpenSSL, Ollama LLM + WebAuthn. Windows 10/11. MIT + Apache-2.0.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | HADES_SENTINEL - Local-only network vulnerability scanner that auto |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:05:58 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 351 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |