 安全软件
点击放大
YeepForge - Automated web application penetration testing fram
项目说明
<di="center">
YeepForge Agent
The AI Penetration Tester That Works While You Sleep
capture0x - powered by tmrswrr

![OWASP]()

![Python]()
![Ollama]()

> Give it a URL. Give it source code. Watch it hack.
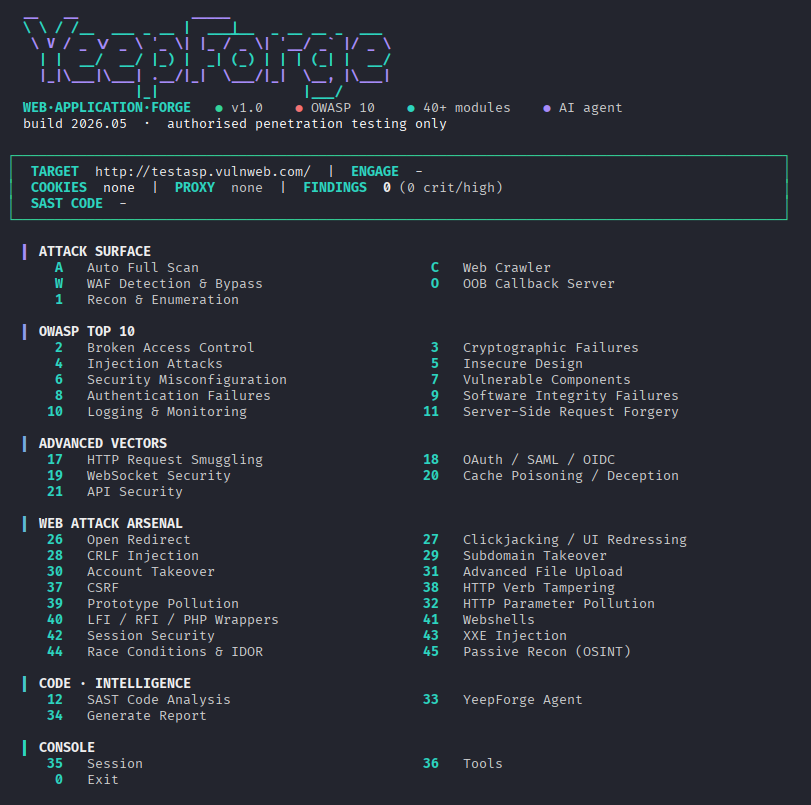
<img src="assets/1.png" alt="YeepForge" width="800">
</div>
---
What Makes YeepForge Different?
Most security tools are menus of commands you run manually.
YeepForge Agent is different. It's an AI that *thinks like a penetration tester* - it reads the target, decides what to attack next, chains findings together, and delivers a professional C report. You provide a URL. The Agent does the rest.
---
<di="center">
<a id="agent"></a>
The Agent
</div>
How It Thinks
The Agent doesn't run tools randomly. After every result, it analyzes what it found and decides the smartest next move:
One command. Full assessment. Professional report.
---
Agent Intelligence - Context-Aware Decision Making
| What the Agent discovers | What it does next |
|--------------------------|-------------------|
| Login form on any page | → Jumps to test_authentication immediately |
| WordPress / Drupal / Joomla | → Prioritizes CMS scan |
| SQL error in any response | → Escalates test_sql_injection |
| .git or .env exposed | → Flags Critical, digs deeper |
| API endpoints in JS files | → Switches to GraphQL/JSON dir scan |
| WAF blocking requests | → Activates WAF bypass payloads |
| Source code provided | → Runs SAST before dynamic tests |
| SAST finds SQLi in code | → Confirms with dynamic test_sql_injection |
| PHP detected | → Prioritizes path tra + file inclusion |
---
Agent Modes
---
Agent Backends - Free Local or Cloud
| Backend | Cost | Speed | Quality | Setup |
|---------|------|-------|---------|-------|
| Ollama - mistral (default) | Free | Fast | Great | ollama pull mistral |
| Ollama - llama3.2:3b | Free | Fastest | Good | ollama pull llama3.2:3b |
| Ollama - qwen2.5-coder | Free | Medium | Great | ollama pull qwen2.5-coder |
| Claude API | Paid | Medium | Excellent | ANTHROPIC_API_KEY=sk-ant-... |
No API key required. Run entirely offline with Ollama.
MCP Server - dri from Claude Code / Cursor / Claude Desktop
YeepForge also ships as an MCP server: it
exposes all 28 scan tools (recon_target, crawl_target, test_sql_injection,nuclei_scan, …) plus set_engagement over the Model Context Protocol, and a
host that already has an LLM drives the engagement with its own subscription -
no ANTHROPIC_API_KEY, no local model needed on YeepForge's side. The host is the
brain; YeepForge is the toolbox.
Set the target once with set_engagement and YeepForge injects it (plus
cookies/proxy/auth) into every later call. Full setup for Claude Code, Cursor and
Claude Desktop: docs/mcp.md.
---
Agent Skills - guided pentest workflows
YeepForge bundles Claude Agent Skills
under .claude/skills/, auto-discovered by Claude Code:
yeepforge-pentest - orchestrates a full engagement through the MCP tools:authorization gate → recon → crawl → OWASP Top 10 testing → exploit → report.
yeepforge-sast - dri analysis (analyze_source_code).security-fuzzing · security-payloads · security-patterns - SecListspayload/wordlist/secret-pattern references for manual testing.
The three security-* skills are from
awesome-skills-security
(MIT, a SecLists redistribution); web-shell samples were excluded on purpose. See.claude/skills/NOTICE.md for attribution.
---
<a id="code-analysis"></a>
SAST Code Analysis - 14 AI Skills
The Agent can analyze source code alongside dynamic testing. When you provide a codebase:
1. Agent reads architecture, frameworks, entry points
2. Traces every user input through the code
3. Finds SQLi/XSS/RCE/SSRF/JWT/IDOR in source
4. Then confirms findings with dynamic testing
5. Combined report: static + dynamic findings
---
Full Feature Set
Automated Engine
| Key | Module | What it does |
|-----|--------|-------------|
|
[A] | Auto Full Scan | Crawl → test all OWASP → nikto → nuclei → C ||
[C] | Web Crawler | Links, forms, JS APIs, robots.txt, sitemap - plus optional headless rendering for SPAs ||
[W] | WAF Bypass | 14+ WAF fingerprints · 100+ bypass payloads per category ||
[O] | OOB Collaborator | interactsh-backed callbacks confirming blind SQLi, SSRF, XXE, Log4Shell, CMDi ||
[33]| AI Agent | Autonomous pentest · chat · payloads · SAST code analysis |OWASP Top 10 (2021)
| Category | Module | Co |
|----------|--------|---------|
| A01 Broken Access Control |
[2] | IDOR · path tra · forced browsing · JWT || A02 Cryptographic Failures |
[3] | Sensiti · cleartext · weak hashes · JS secrets || A03 Injection |
[4] | SQLi · XSS · SSTI · CMDi · XXE · NoSQL · LDAP || A04 Insecure Design |
[5] | Business logic · race conditions · mass assignment || A05 Security Misconfiguration |
[6] | Headers · CORS · debug endpoints · default creds || A06 Components |
[7] | CVE scan · nikto · CMS scanner · Log4Shell || A07 Authentication Failures |
[8] | Brute force · session · MFA bypass · credential stuffing || A08 Integrity Failures |
[9] | Deserialization · SRI · CI/CD exposure || A09 Logging Failures |
[10] | Log injection · stack trace exposure · lockout testing || A10 SSRF |
[11] | Internal ports · cloud metadata · gopher · blind OOB |Ad Exploitation
| Module | Techniques |
|--------|-----------|
|
[17] HTTP Request Smuggling | CL.TE · TE.CL · TE obfuscation · H2.TE downgrade ||
[18] OAuth / SAML / OIDC | Redirect URI bypass · state CSRF · SAML XSW/XXE/replay ||
[19] WebSocket Security | CSWSH · message injection · origin bypass ||
[20] Cache Poisoning | Unkeyed headers · fat GET · cache deception · DoS ||
[21] API Security | GraphQL introspection · batch abuse · REST enumeration |Web Application Attacks
| Module | Techniques |
|--------|-----------|
|
[26] Open Redirect | 17 bypass · scheme abuse · ATO chain ||
[27] Clickjacking | Frame detection · PoC generator · sandbox bypass ||
[28] CRLF Injection | Header injection · response splitting · log injection ||
[29] Subdomain Takeover | 25 service fingerprints · CNAME hijacking · nuclei ||
[30] Account Takeover | Password reset · email change · 2FA bypass ||
[31] Ad File Upload | Polyglot · SVG XSS · ZIP slip · ImageMagick ||
[32] HTTP Parameter Pollution | WAF bypass · business logic · DOM HPP ||
[37] CSRF | Token detection · bypass · PoC generator · SameSite ||
[38] HTTP Verb Tampering | PUT/DELETE/TRACE · XST · method o ||
[39] Prototype Pollution | JS __proto__ · PHP type juggling · XPath · email injection ||
[40] LFI / RFI / PHP Wrappers | Local/remote inclusion · log poisoning · php:// filters ||
[41] Webshells | Generate · upload · interact · obfuscate · reverse shell ||
[42] Session Security | Cookie attributes · fixation · timeout · logout · cache ||
[43] XXE Injection | Classic · blind OOB · billion laughs · SSRF via XXE ||
[44] Race Conditions & IDOR | TOCTOU · limit-o · IDOR automation · business logic ||
[45] Passi (OSINT) | DNS · Google dorks · GitHub leaks · Shodan · certs - zero target traffic |---
Quick Start
1. Install
2. Start Ollama (free AI backend)
3. Launch Agent
Agent + SAST (when you ha code)
---
Reports
Every assessment produces a professional report:
Formats: HTML (print-ready) · Markdown · JSON (CI/CD ready)
---
Installation & Requirements
Dependencies
AI Backend Setup
Configuration (.env)
---
Module Reference
---
Architecture
---
CLI Reference
---
Engagement Safety - scope, rate limiting, e
Every request made through the engine in utils/http.py is:
your machine. With no explicit
--scope, the target host and its subdomainsare the scope, so a scan cannot wander onto someone else's asset.
--rps, default 10),with
Retry-After honoured. This is what keeps you off a program's ban list.--proxy applies to every request, so Burp's history is thecomplete engagement record.
plus a
curl reproduction line, rendered into the HTML and Markdown reports.Findings also carry a confidence level (
Confirmed / Firm / Tentative).See docs/engine.md for the full configuration reference and
for how to write a module against the client.
---
Ethical Use & Legal
YeepForge is built for:
Never test systems without explicit written authorization.
The author assumes no liability for misuse. By using YeepForge, you confirm you ha authorization for all targets.
YeepForge runs attacker-controlled data on your machine - see
SECURITY.md for the tool's own security posture, how to run it
safely, and how to report a in YeepForge itself.
---
Contributing
Pull requests are welcome. CONTRIBUTING.md covers the dev
setup, how to add a module, and the two non-negotiable rules: all HTTP goes
through utils/http.py, and no value is e into a shell string.
---
<di="center">
YeepForge v1.0 - Agent-First Web Security
*capture0x - powered by tmrswrr*
./run.sh → [33] YeepForge Agent → The AI does the rest.
</div>
项目信息
开发语言:Python
Star 数:8
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Automated web application penetration testing framework: OWASP Top 10 + advanced attacks, an autonomous AI agent (Ollama/Claude/OpenAI), SAST source-code analysis, and an MCP server, with professional CVSS-scored reports.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | YeepForge - Automated web application penetration testing fram |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:06:41 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 278 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |