 安全软件
点击放大
whalescan - Vulnerability scanner for Windows containers
项目说明
Whalescan
scanner for windows containers.
Getting Started
O
Whalescan performs several benchmark checks, as well as checking for CVEs. This tool can be used as part of a windows
container review on local copies of the containers, and on the host itself to enhance security
* Container checks
* Checks if containers are stored under C: drive - this could raise issues if there is a DoS attack,
filling up the C: drive and making the host unresponsive
* Checks if container is running as a process or hyper- isolation offers enhanced security of containers
* Checks if there are any pending updates in the containers, and if so, how to update.
!Container checks
* Image checks
* Checks for unsafe commands being used in the dockerfile, for example docker ADD instead of docker COPY.
* Checks if hash is being performed on any files downloaded.
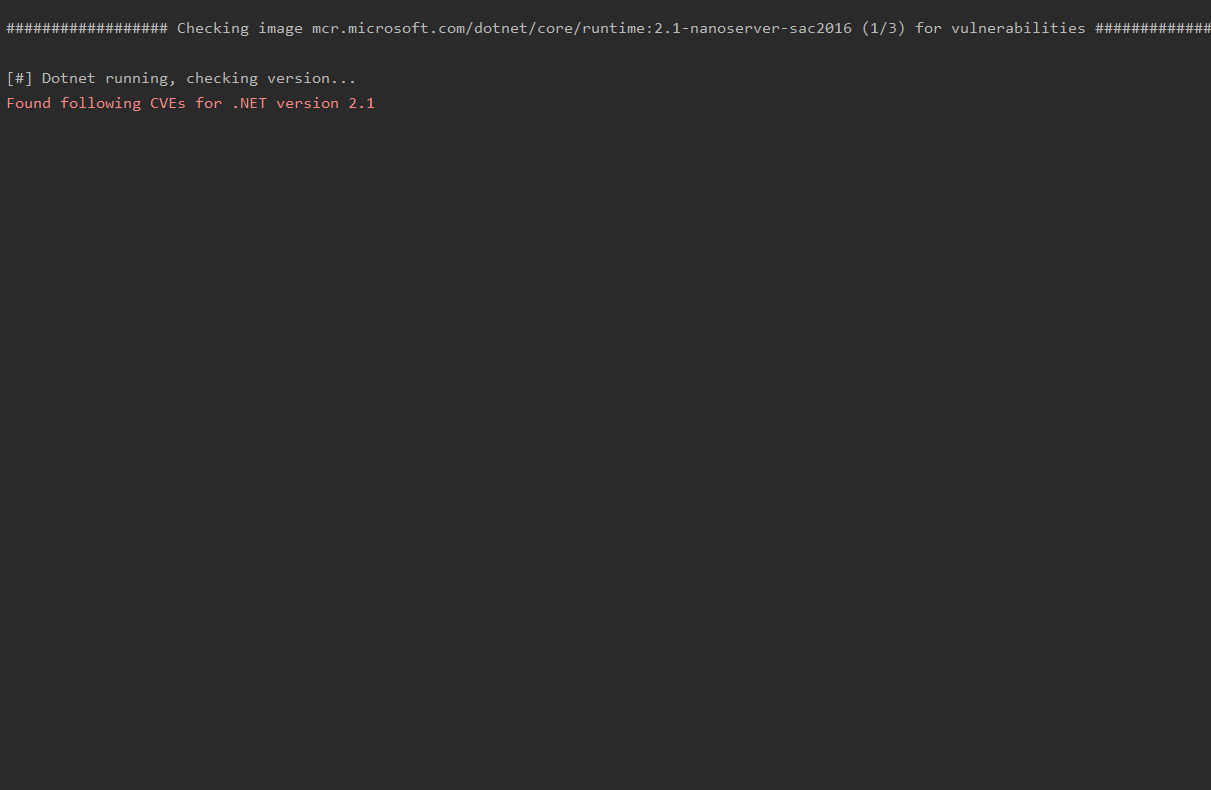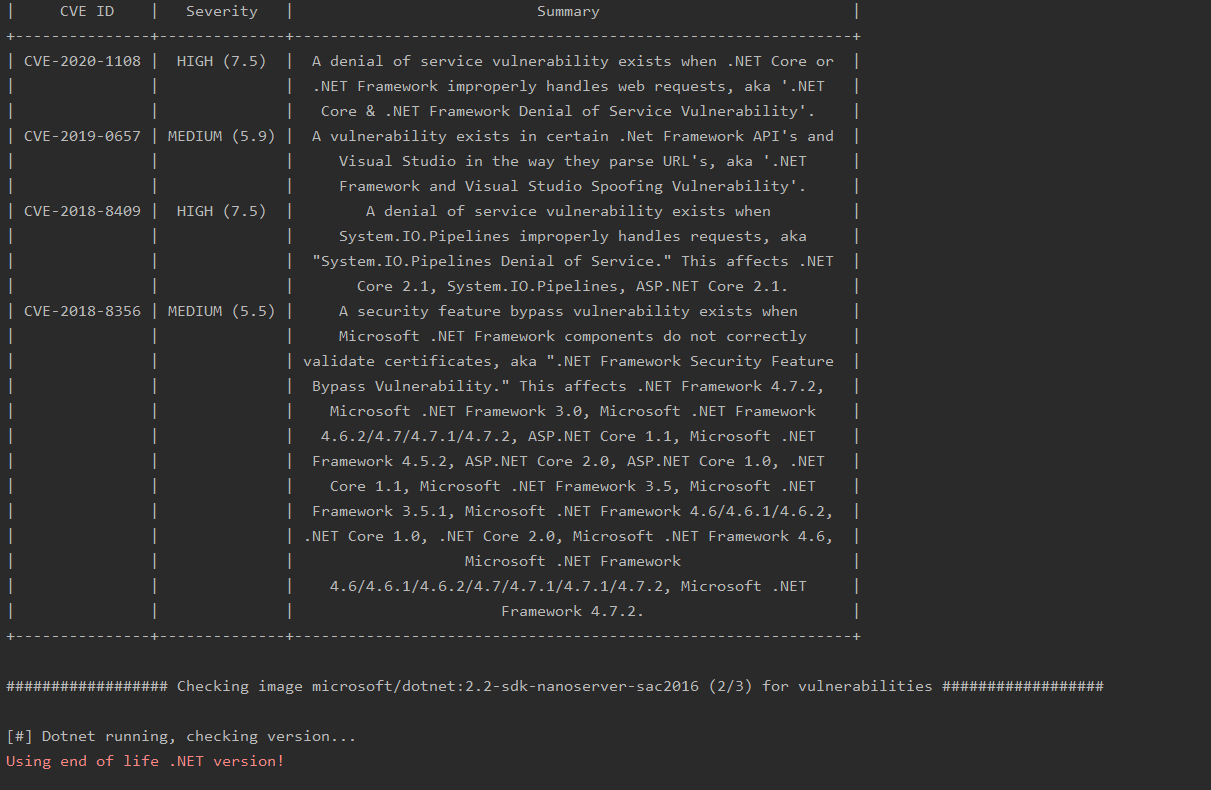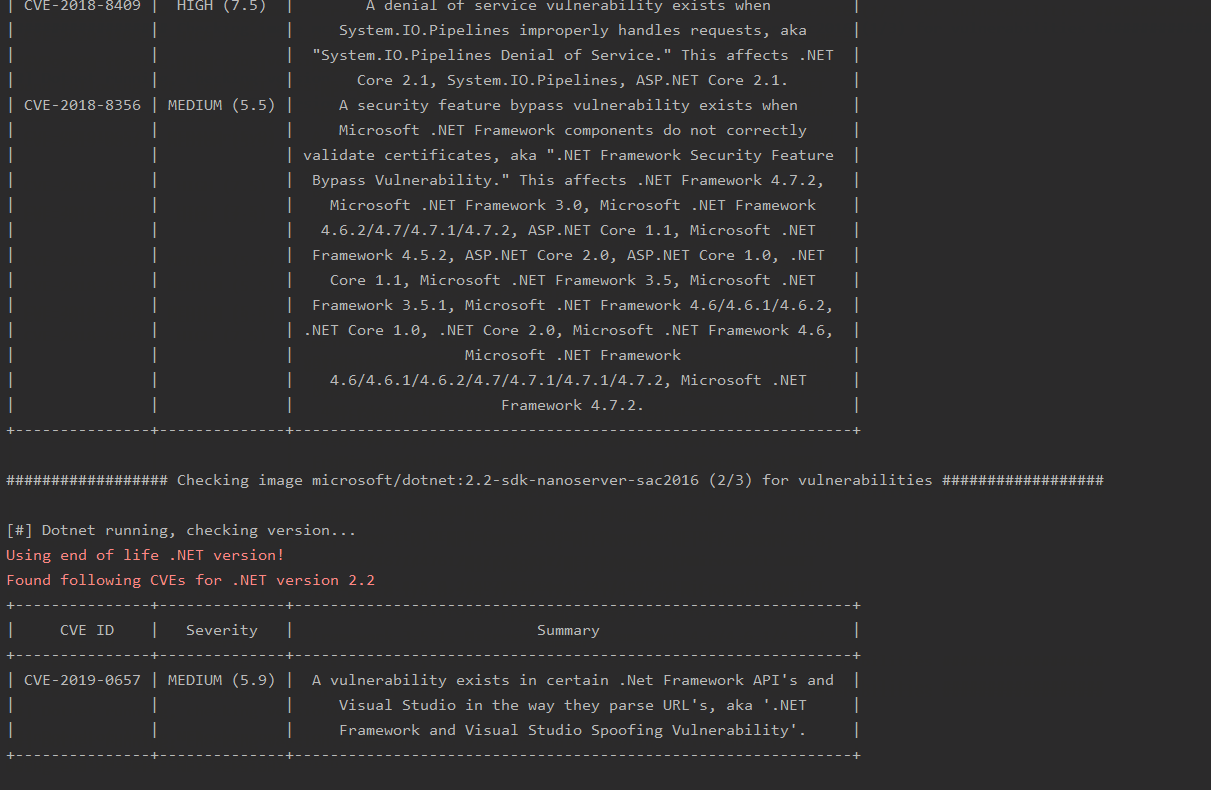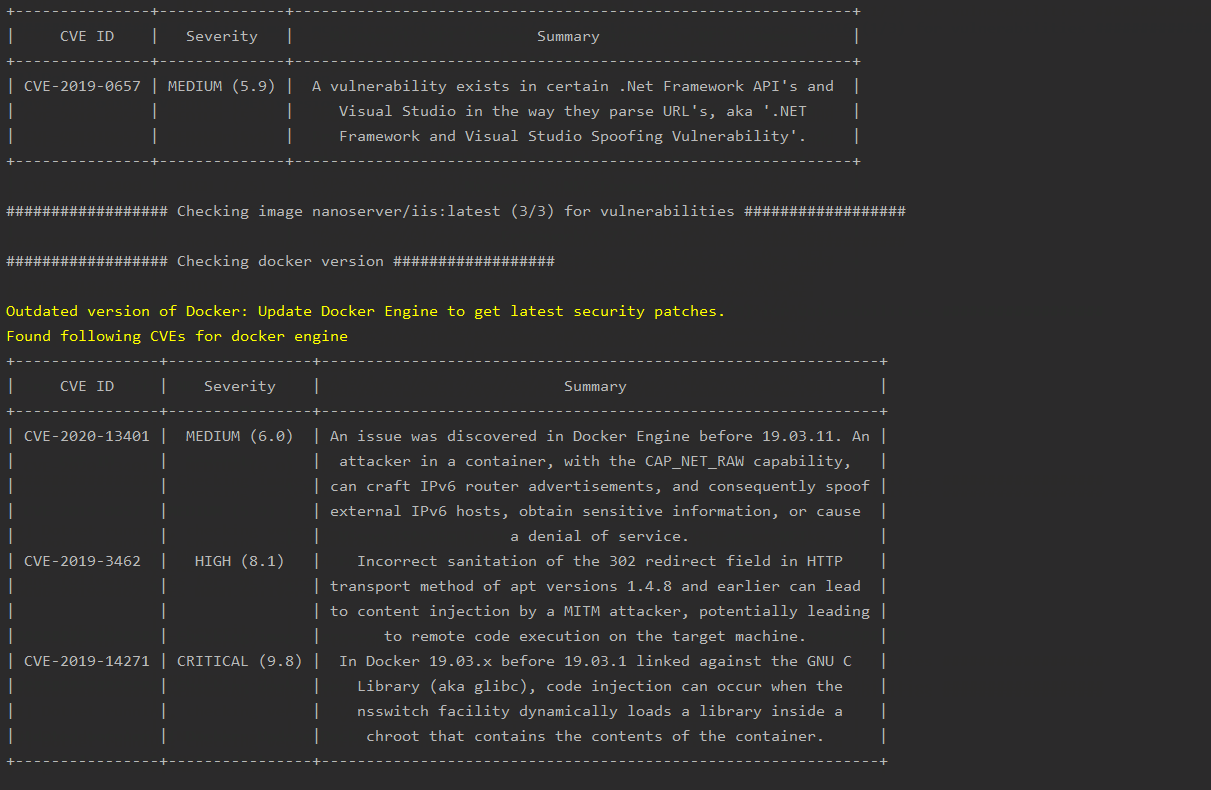
* Checks if any packages are on the container, and pulls relevant C
* Checks if .NET being used is End Of Life
* Checks if Docker Engine is updated, and if not, gathers a list of CVEs for the being used
!C demo
* Checks permissions of docker configuration files
* Checks if additional devices have been mapped to containers
License
This project is licensed under the MIT License - see the LICENSE.md file for details
项目信息
开发语言:Python
Star 数:7
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Vulnerability scanner for Windows containers展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | whalescan - Vulnerability scanner for Windows containers |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:07:26 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 342 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |