 病毒分析
点击放大
al-khaser - Public malware techniques used in the wild: Virtua
项目说明
Al-Khaser v0.81
!Logo
Content
- Anti-debugging attacks
- Anti-Dumping
- Timing Attacks
- Human Interaction
- Anti-VM
- Anti-Disassembly
Introduction
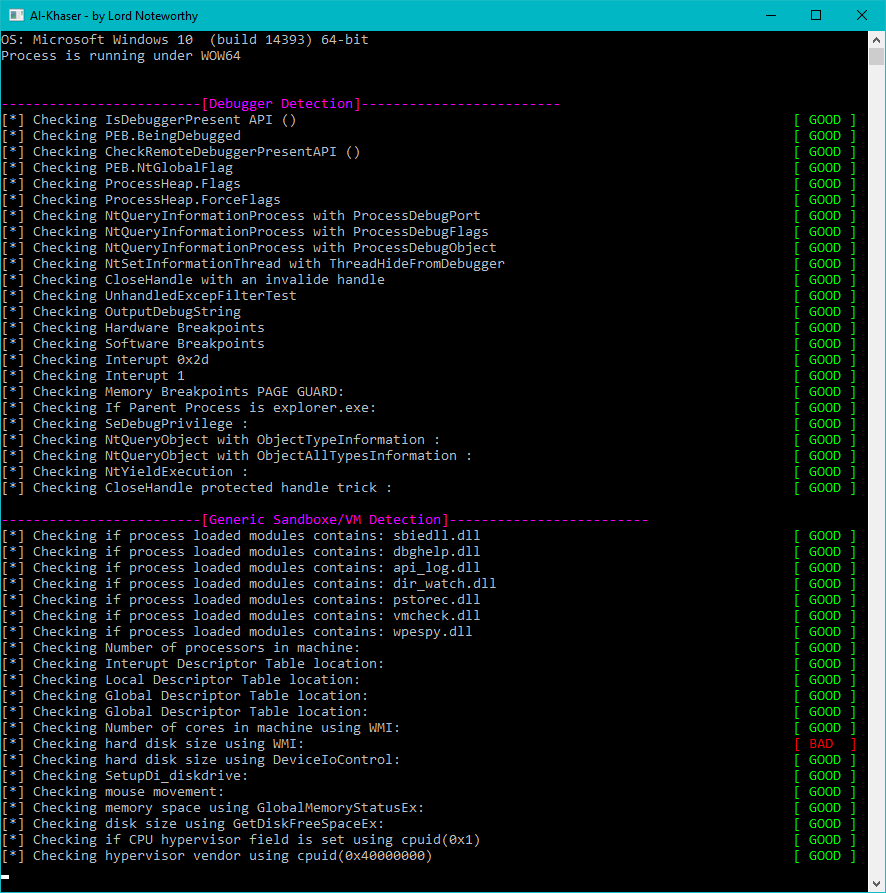
al-khaser is a PoC "malware" application with good intentions that aims to stress your anti-malware system.
It performs a bunch of common malware tricks with the goal of seeing if you stay under the radar.
!Logo
Usage
Download
You can download built binaries (x86, x64) from this project's releases page. The password for the 7zs can be found here.
Possible uses
Please, if you encounter any of the anti-analysis tricks which you have seen in a malware, don't hesitate to contribute.
Features
Anti-debugging attacks
Anti-injection
Anti-Dumping
Timing Attacks [Anti-Sandbox]
Human Interaction / Generic [Anti-Sandbox]
sample.exe or sandbox.exe.
Anti- / Full-System Emulation
- HARDWARE\\DE\\Scsi\\Scsi Port 0\\Scsi Bus 0\\Target Id 0\\Logical Unit Id 0 (Identifier) (VBOX)
- HARDWARE\\DE\\Scsi\\Scsi Port 0\\Scsi Bus 0\\Target Id 0\\Logical Unit Id 0 (Identifier) (QEMU)
- HARDWARE\\Description\\System (SystemBios) (VBOX)
- HARDWARE\\Description\\System (SystemBios) (QEMU)
- HARDWARE\\Description\\System () ()
- HARDWARE\\Description\\System (SystemBiosDate) (06/23/99)
- HARDWARE\\DE\\Scsi\\Scsi Port 0\\Scsi Bus 0\\Target Id 0\\Logical Unit Id 0 (Identifier) ()
- HARDWARE\\DE\\Scsi\\Scsi Port 1\\Scsi Bus 0\\Target Id 0\\Logical Unit Id 0 (Identifier) ()
- HARDWARE\\DE\\Scsi\\Scsi Port 2\\Scsi Bus 0\\Target Id 0\\Logical Unit Id 0 (Identifier) ()
- SYSTEM\\ControlSet001\\Control\\SystemInformation (SystemManufacturer) ()
- SYSTEM\\ControlSet001\\Control\\SystemInformation (SystemProductName) ()
- HARDWARE\\ACPI\\DSDT\\ (VBOX)
- HARDWARE\\ACPI\\FADT\\ (VBOX)
- HARDWARE\\ACPI\\RSDT\\ (VBOX)
- SOFTWARE\\Oracle\\ Guest Additions (VBOX)
- SYSTEM\\ControlSet001\\Services\\ (VBOX)
- SYSTEM\\ControlSet001\\Services\\ (VBOX)
- SYSTEM\\ControlSet001\\Services\\ (VBOX)
- SYSTEM\\ControlSet001\\Services\\ (VBOX)
- SYSTEM\\ControlSet001\\Services\\ (VBOX)
- SOFTWARE\\, Inc.\\ Tools ()
- SOFTWARE\\Wine (WINE)
- SOFTWARE\Microsoft\ Machine\Guest\Parameters (HYPER-V)
- SYSTEM\\CurrentControlSet\\Services\\Disk\\Enum
- SYSTEM\\CurrentControlSet\\Enum\\IDE
- SYSTEM\\CurrentControlSet\\Enum\\SCSI
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.dll"
- "system32\\.exe"
- "system32\\.exe"
- "system32\\.exe"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\vmci.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "system32\\drivers\\.sys"
- "%PROGRAMFILES%\\oracle\\ guest additions\\"
- "%PROGRAMFILES%\\\\"
- Interupt Descriptor Table (IDT) location
- Local Descriptor Table (LDT) location
- Global Descriptor Table (GDT) location
- Task state segment trick with STR
- "\x08\x00\x27" (VBOX)
- "\x00\x05\x69" ()
- "\x00\x0C\x29" ()
- "\x00\x1C\x14" ()
- "\x00\x50\x56" ()
- "\x00\x1C\x42" (Parallels)
- "\x00\x16\x3E" (Xen)
- "\x0A\x00\x27" (Hybrid Analysis)
- "\\\\.\\"
- "\\\\.\\"
- "\\\\.\\pipe\\"
- "\\\\.\\"
- "\\\\.\\pipe\\")
- "\\\\.\\HGFS"
- "\\\\.\\vmci"
- SetupAPI SetupDiEnumDe (GUID_DE)
- QEMU
-
- VBOX
- HD
- Power policies (S1-S4 states, thermal control)
- SMBIOS string checks ()
- SMBIOS string checks ()
- SMBIOS string checks (Qemu)
- SMBIOS number of tables (Qemu, )
- ACPI string checks (WAET table, PNP devices, PM state with battery checks)
- ACPI string checks ()
- ACPI string checks ()
- ACPI string checks (Qemu)
-
-
-
-
-
- Shared Folders
- .exe (VBOX)
- .exe (VBOX)
- .exe()
- .exe()
- ()
- .exe ()
- .exe ()
- .exe()
- .exe()
- prl_cc.exe(Parallels)
- prl_tools.exe(Parallels)
- xenservice.exe(Citrix Xen)
- qemu-ga.exe (QEMU)
- looking-glass-host.exe (GENERIC)
- .exe (GENERIC)
- SELECT * FROM Win32_Bios (SerialNumber) (GENERIC)
- SELECT * FROM Win32_PnPEntity (De) (VBOX)
- SELECT * FROM Win32_NetworkAdapterConfiguration (MACAddress) (VBOX)
- SELECT * FROM Win32_NTE (VBOX)
- SELECT * FROM Win32_Processor (NumberOfCores and ProcessorId) (GENERIC)
- SELECT * FROM Win32_LogicalDisk (Size) (GENERIC)
- SELECT * FROM Win32_ComputerSystem (Model and Manufacturer) (GENERIC)
- SELECT * FROM MSAcpi_ThermalZoneTemperature CurrentTemperature) (GENERIC)
- SELECT * FROM Win32_Fan (GENERIC)
- a.dll (AVG)
- a.dll (AVG)
- snxhk.dll (Avast)
- kernel32.dll!wine_get_unix_file_nameWine (Wine)
- sbiedll.dll (Sandboxie)
- dbghelp.dll (MS debugging support routines)
- api_log.dll (iDefense Labs)
- dir_watch.dll (iDefense Labs)
- pstorec.dll (SunBelt Sandbox)
- .dll ( PC)
- wpespy.dll (WPE Pro)
- cmdvrt32.dll (Comodo Container)
- cmdvrt64.dll (Comodo Container)
- Hypervisor presence using (EAX=0x1)
- Hypervisor using (EAX=0x40000000)
- "K\0\0\0" (KVM)
- "Microsoft Hv"(Microsoft Hyper-V or Windows PC)
- ""()
- "Xen"(Xen)
- "prl hyperv "( Parallels)
-""( )
Anti-Analysis
- OllyDBG / ImmunityDebugger / WinDbg / IDA Pro / X64dbg / Cheat Engine
- SysInternals Suite Tools (Process Explorer / Process Monitor / Regmon / Filemon, TCPView, Autoruns)
- Wireshark / Dumpcap / Fiddler / Http Debugger
- ProcessHacker / SysAnalyzer / HookExplorer / SysInspector
- ImportREC / PETools / LordPE
- JoeBox Sandbox
- Resource Hacker
- Frida
Anti-Disassembly
Macro malware attacks
Code/DLL Injections techniques
Authors
Pull requests welcome. Please read the De Guidelines on our wiki if you wish to contribute to the project.
References
项目信息
开发语言:C++
Star 数:7140
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Public malware techniques used in the wild: Virtual Machine, Emulation, Debuggers, Sandbox detection. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | al-khaser - Public malware techniques used in the wild: Virtua |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:11:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 234 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |