 病毒分析
点击放大
Malware - Course materials for Malware Analysis by RPISEC

项目说明
Malware Analysis - CSCI 4976
This repository contains the materials as de and used by RPISEC to
teach Malware Analysis at Rensselaer Polytechnic Institute in
Fall 2015. This was a uni course de and run soley by students, primarily using the
Practical Malware Analysis
book by Michael Sikorski and Andrew Honig, to teach skills in reverse engineering, malicious behaviour, malware,
and anti-analysis techniques.
<p align="center">
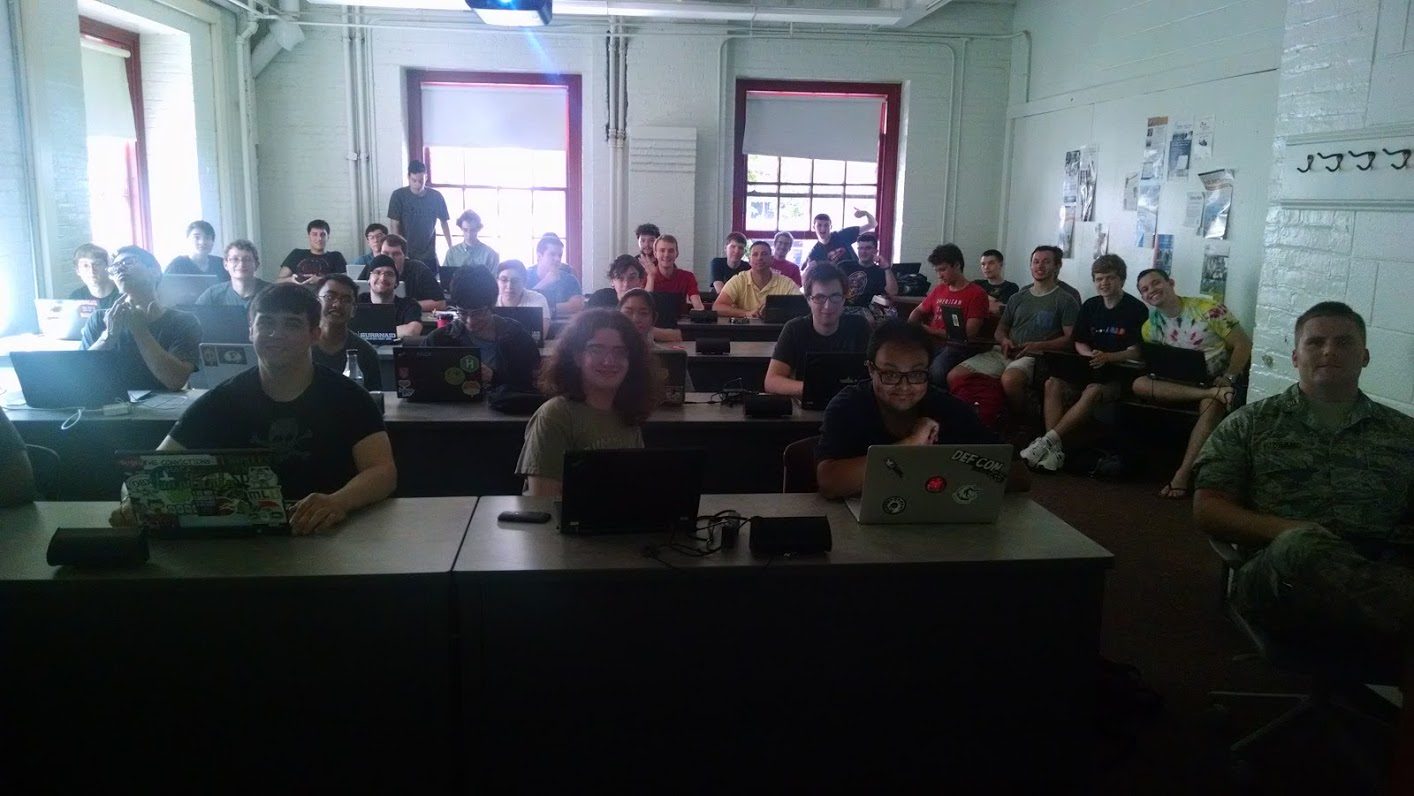
<img width="700px" src="/resources/images/class.png" alt="Malware"/>
</p>
About the Course
The Practical Malware Analysis (PMA) book is where many RPISEC members and alumn started. The book reads very well,
is full of information, and the lab walkthroughs in the back are in. We didn't want to re-invent the wheel so
we structured most of the class around the book. Students were expected to have read the relevant PMA book chapters
before class, allowing us to spend much more class time demonstrating skills and techniques and walking through
hands-on examples with the students.
Syllabus:
Note: Most of the samples used in this course are malicious in nature, treat them carefully!
To help protect people from accidentaly running samples on an important machine, and to prevent anti-malware suites from
blocking the course material, all of the samples are compressed and encrypted with a password of 'infected'.
Course Abstract
>_With the increased use of the Internet and pre of computing systems in critical infrastructure, technology is undoubtedly a vital part of modern daily life. Unfortunately, the increasingly networked nature of the modern world has also enabled the spread of malicious software, or “malware”, ranging from annoying adware to ad nation-state sponsored cyber-weaponry. As a result, the ability to detect, analyze, understand, control, and eradicate malware is an increasingly important issue of economic and national security._
>_This course will introduce students to modern malware analysis techniques through readings and hands-on interacti of real-world samples. After taking this course students will be equipped with the skills to analyze ad contemporary malware using both static and dynamic analysis._
Prerequisite Knowledge
This course carried a prereq of
Computer Organization - CSCI 2500
at RPI. Computer Organization is RPI's basic computer architecture course that teaches
things like C, MIPS assembly, x86 assembly, Datapaths, CPU Pipelining, CPU Caching,
Memory Mapping, etc.
Our expected demographic for Malware Analysis was students with zero reverse
engineering experience. That said, to be able to take this course
you will probably need at least the following skills.
* Working knowledge of C/C++
* Any assembly le
Lecture Breakdown
Lecture | Title | Topics
------- | ----- | ------
01 | Introduction | Syllabus, Basic Static Analysis, Basic Dynamic Analysis
02 | Ad Static Analysis | x86, IDA, Code Constructs
03 | Analyzing Windows Programs | WinAPI, Handles, Windows Internals, Networking, COM
04 | Ad Dynamic Analysis | Debugging Concepts and Tools
05 | Malware Behavior | Malicious Acti and Techniques
06 | Data Encoding and Malware Countermeasures | Hiding Data, Malware Countermeasures
07 | Covert Malware Launching | Covert Launching and Execution
08 | Anti-Analysis | Anti-Disassembly, Anti-, Anti-AV
09 | Packing and Unpacking | Packers, Packing, and Unpacking
10 | Intro to Windows Kernel | Kernel Basics, Windows Kernel API, Windows Drivers, Kernel Debugging
11 | Rootkit Techniques | Hooking, Patching, Direct Kernel Object Manipulation
12 | Rootkit Anti-Forensics and Covert Channels | Anti-forensics, Covert Channels
Lab Breakdown
Lab | Topic
--- | -----
01 | Basic Analysis
02 | Ad Static Analysis
03 | Analyzing Windows Programs
04 | Ad Dynamic Analysis
05 | Malware Behavior
06 | Data Encoding and Malware Countermeasures
07 | Covert Malware Launching
08 | Anti Analysis
09 | Packing and Unpacking
10 | Windows Kernel
Project Breakdown
Project | Topic
------- | -----
01 | Malware Behavior
02 | Runtime Process Manipulation
03 | Unpacking and Automation
04 | APT Sample Analysis
Links for additional exercises:
* Practical Malware Analysis Labs
* Practical Reverse Engineering Labs
Analysis En
Setting up a "safe" and usable analysis en can range from easy to impossible,
depending on how far you want to go. The PMA book devotes an
entire chapter (Chapter 2) to this problem. For the purposes of this class, we
decided to set up a Windows 7 32-bit machine. Unfortunately, while all the software
we used for the class is free, Windows is not, thus we cannot distribute this VM like we
distributed the Warzone for MBE. We ha, included a comprehensive list, and a
collection of installers, of all the tools we used throughout the course. There are a few
"essentials" that we haven't listed but are still included in the installer package
(python, cygwin, etc).
Visit the releases page for the latest package.
Tools
* Dependency Walker
* Fakenet
* FileAlyzer 2.0
* HxD
* IDA Free
* ImpREC
* LordPE
* Malcode Analyst Pack
* OllyDbg
* PEiD
* PEview
* Regshot
* Resource Hacker
* Sysinternals Suite
* UPX
* Studio
* Windbg.aspx)
* Wireshark
Frequently Asked Questions
If you are e on a problem or have any questions, you're more than welcome to
ask on IRC.
#### What is the password to the zip files?
'infected', no quotes.
#### Are these files malicious/dangerous?
Yes. Not all of them are malicious in nature, but most are. Always keep them inside a
proper analysis en.
#### Why are the lecture slides for XYZ so sparse?
Much of lecture time was spent in hands on examples, with the expectation that students
had read the material in the PMA book ahead of time. Thus the slide content referring
to material from the PMA book is meant as more of an outline. Read the chapters and then
go through the lab walkthroughs in the back of the PMA book, they are a great resource.
#### Do you ha of the lectures?
Sadly we did not record any of the lectures, maybe next time.
#### Where can I learn more?
Play more wargames:
* IO Wargame
* Pwnable KR
* Pwnable TW
* O
* Re KR
* W3Challs
* crackmes.de
Reverse more samples:
* Contagio
* Kernelmode.info
* Malware.lu
* malwr
* Hybrid Analysis
The following books are excellent resources for expanding your knowledge of malware analysis and reverse engineering. We recommend working through them in the following order:
* Practical Malware Analysis
* Practical Reverse Engineering
* Rootkits: Sub the Windows Kernel
* The Rootkit Arsenal: Escape and E in the Dark Corners of the System
* Rootkits and Bootkits: Re Modern Malware and Next Generation Threats
These three books are also excellent:
* The Antivirus Hacker's Handbook
* The Art of Memory Forensics
* Windows Internals
And when they're happening, play CTFs!
#### <a name="contact"></a>I have a question, how can I get in touch with you?
Our club keeps a pretty active IRC presence. Someone there can probably
answer your question.
Server: irc.rpis.ec
Port: 6667, or 6697 (SSL)
If you would like a more formal means of communication, you can reach us at contact [at] rpis.ec
Licensing
This course was explicitly designed for academic & educational use only. Please keep this
in mind when sharing and distributing our course material. The specific licenses in
can be found below.
Lecture Slides
The lectures are covered by the Creati Attribution-NonCommercial 4.0
International license CC BY-NC 4.0.
<p align="center">
<a href=" src="/resources/images/cc-by-nc.png" alt="CC BY-NC 4.0"/></a>
</p>
Acknowledgements
Hundreds of hours and countless all nighters went into the production and execution of
this course. This section serves to recognize those who made all of this possible.
Original Authors
* Branden Clark
* Austin Ralls
* Aaron Sedlacek
Special Thanks
* The RPI CS Department for giving us this opportunity and letting us run with it
* Professor Bülent Yener for sponsoring such a course
* Our students who put up with us all semester
项目信息
开发语言:未知
Star 数:4212
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Course materials for Malware Analysis by RPISEC展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Malware - Course materials for Malware Analysis by RPISEC |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:11:23 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 447 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |