 病毒分析
点击放大
drakvuf-sandbox - DRAKVUF Sandbox - automated hypervisor-level malwa
项目说明
DRAK
> [!WARNING]
> Here be dragons 🐉. Maintaining your own sandbox is a difficult task and this project uses technology that is not user-friendly.
> Be prepared to brush up on your debugging skills as bugs may be reproducible only on your configuration.
> On the other hand, it's not purely an R&D project and it is used in production! Source code and issues section on both
> DRAK and DRAK projects are your best friend.
DRAK is an automated black-box malware analysis system with DRAKVUF engine under the hood, which does not require an agent on guest OS.
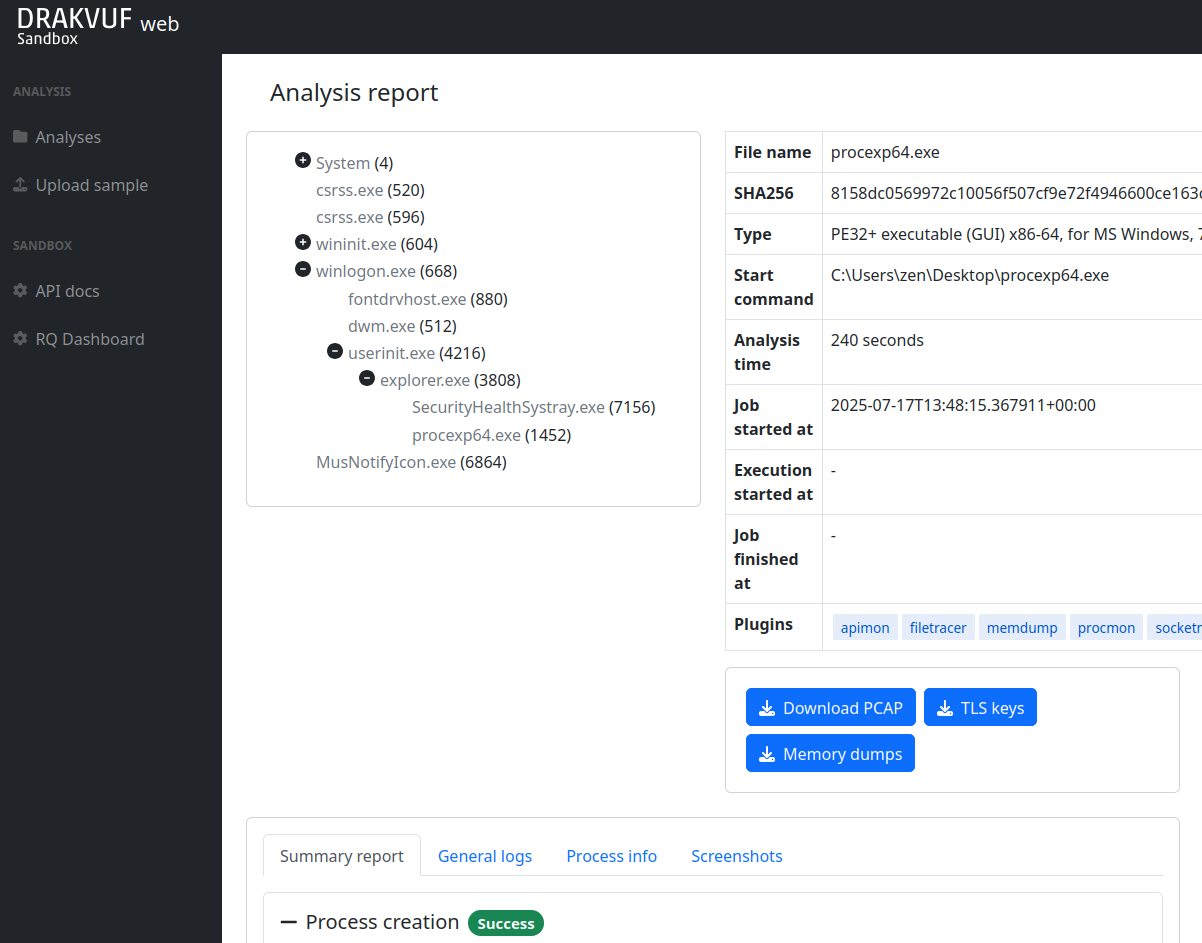
This project provides you with a friendly web interface that allows you to upload suspicious files to be analyzed. Once the sandboxing job is finished, you can explore the analysis result through the mentioned interface and get an insight on whether the file is truly malicious or not.
Because it is usually pretty hard to set up a malware sandbox, this project also provides you with an installer app that would guide you through the necessary steps and configure your system using settings that are recommended for beginners. At the same time, experienced users can tweak some settings or e some infrastructure parts to better suit their needs.
Quick start
* 👋 Getting started
* Latest releases
* Latest docs
!DRAK - Analysis view
Recommended hardware & software
In order to run DRAK, your setup should fulfill all the listed requirements.
* Processor:
* ✔️ Required Intel processor with Intel Technology (VT-x) and Extended Page Tables (EPT) features
* Host system with at least 2 core CPU and 5 GB RAM, running GRUB as bootloader, one of:
* ✔️ Debian 12 Bookworm
* ✔️ Ubuntu 22.04 Jammy
* Guest system, one of:
* ✔️ Windows 10 build at least 2004 (x64), recommended 22H2
* ✔️ Windows 7 (x64)
Nested :
* ✔️ Xen - works out of the box.
* ✔️ KVM - works, we often use it for de purposes. If you experience any bugs, please report them to us for further in.
* ✔️ Workstation Player - works, but you need to check EPT option for a processor with EPT still required.
* ❌ AWS, GCP, Azure - due to lack of exposed CPU features, hosting DRAK in the cloud is not supported (although it might change in the future).
* ❌ Hyper-'t work.
* ❌ Fusion (Mac) - doesn't work.
Maintainers/authors
Feel free to contact us if you have any questions or comments.
General contact email: (fastest response)
You can also chat with us about this project on Discord:
This project is authored by:
* Michał Leszczyński ()
* Adam Kliś ()
* Hubert Jasudowicz ()
* Paweł Srokosz ()
* Konstanty Cieśliński ()
* Arkadiusz Wróbel ()
* Jarosław Jedynak (@msm-cert)
If you have any questions about DRAKVUF engine itself, contact
Acknowledgements
This project was created and/or upgraded thanks to the following organizations and initiatives:
Connecting Europe Facility of the European Union
<a href=" <img style="border: 0.2px solid black" src=".github/screenshots/cef.png" alt="Co-financed by the Connecting Europe Facility of the European Union"> </a>
The Honeynet Project
<a href=" <img style="border: 0.2px solid black" src=".github/screenshots/honeynet.png" alt="Contributed by The Honeynet Project"> </a>
CERT Polska
<a href=" <img style="border: 0.2px solid black" src=".github/screenshots/cert.png" alt="Maintained by CERT Polska"> </a>
项目信息
开发语言:Python
Star 数:1351
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕DRAKVUF Sandbox - automated hypervisor-level malware analysis system展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | drakvuf-sandbox - DRAKVUF Sandbox - automated hypervisor-level malwa |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:13:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 79 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |