 病毒分析
点击放大
YaraHunter - 🔍🔍 Malware scanner for cloud-native, as part of C
项目说明
<img src="
![GitHub license]()
![GitHub stars]()
![GitHub issues]()
![Slack]()
YaraHunter
Deepfence YaraHunter scans container images, running Docker containers, and filesystems to find indicators of malware. It uses a YARA ruleset to identify resources that match known malware signatures, and may indicate that the container or filesystem has been compromised.
YaraHunter can be used in the following ways:
Key capabilities:
YaraHunter is a work-in-progress (check the Roadmap and issues list), and will be integrated into the ThreatMapper threat discovery platform. We welcome any contributions to help to improve this tool.
Quick Start
For full instructions, refer to the YaraHunter Documentation.
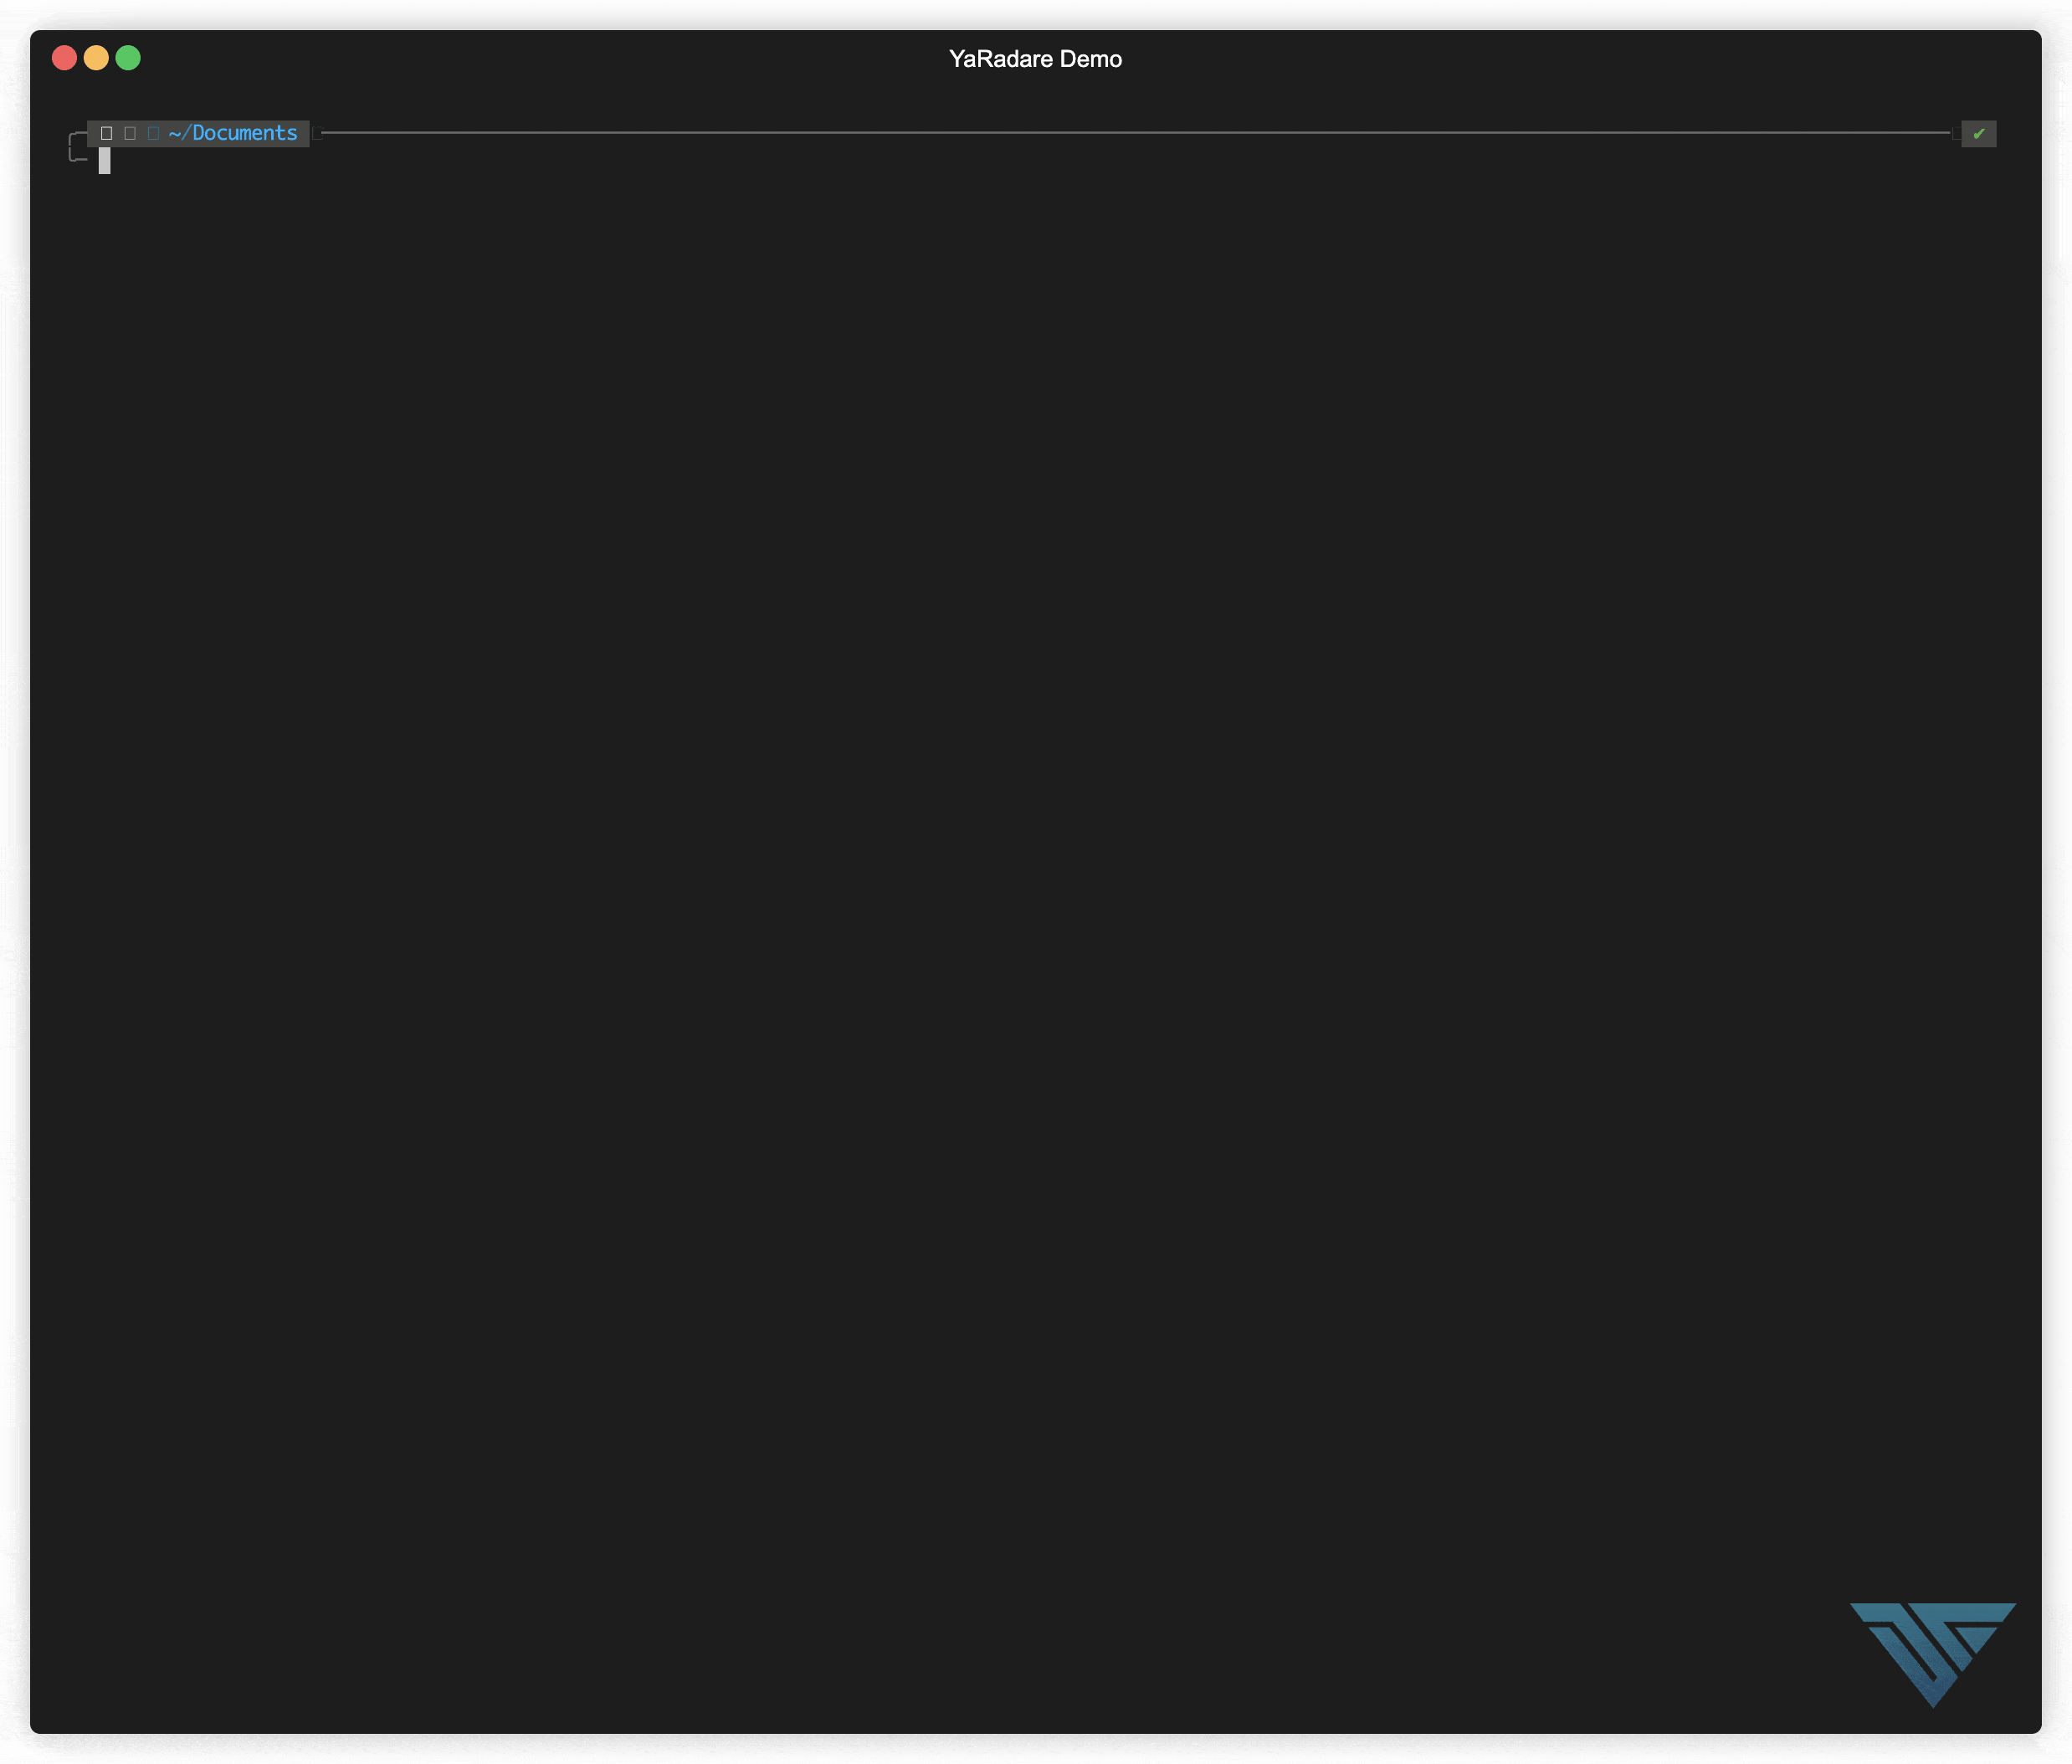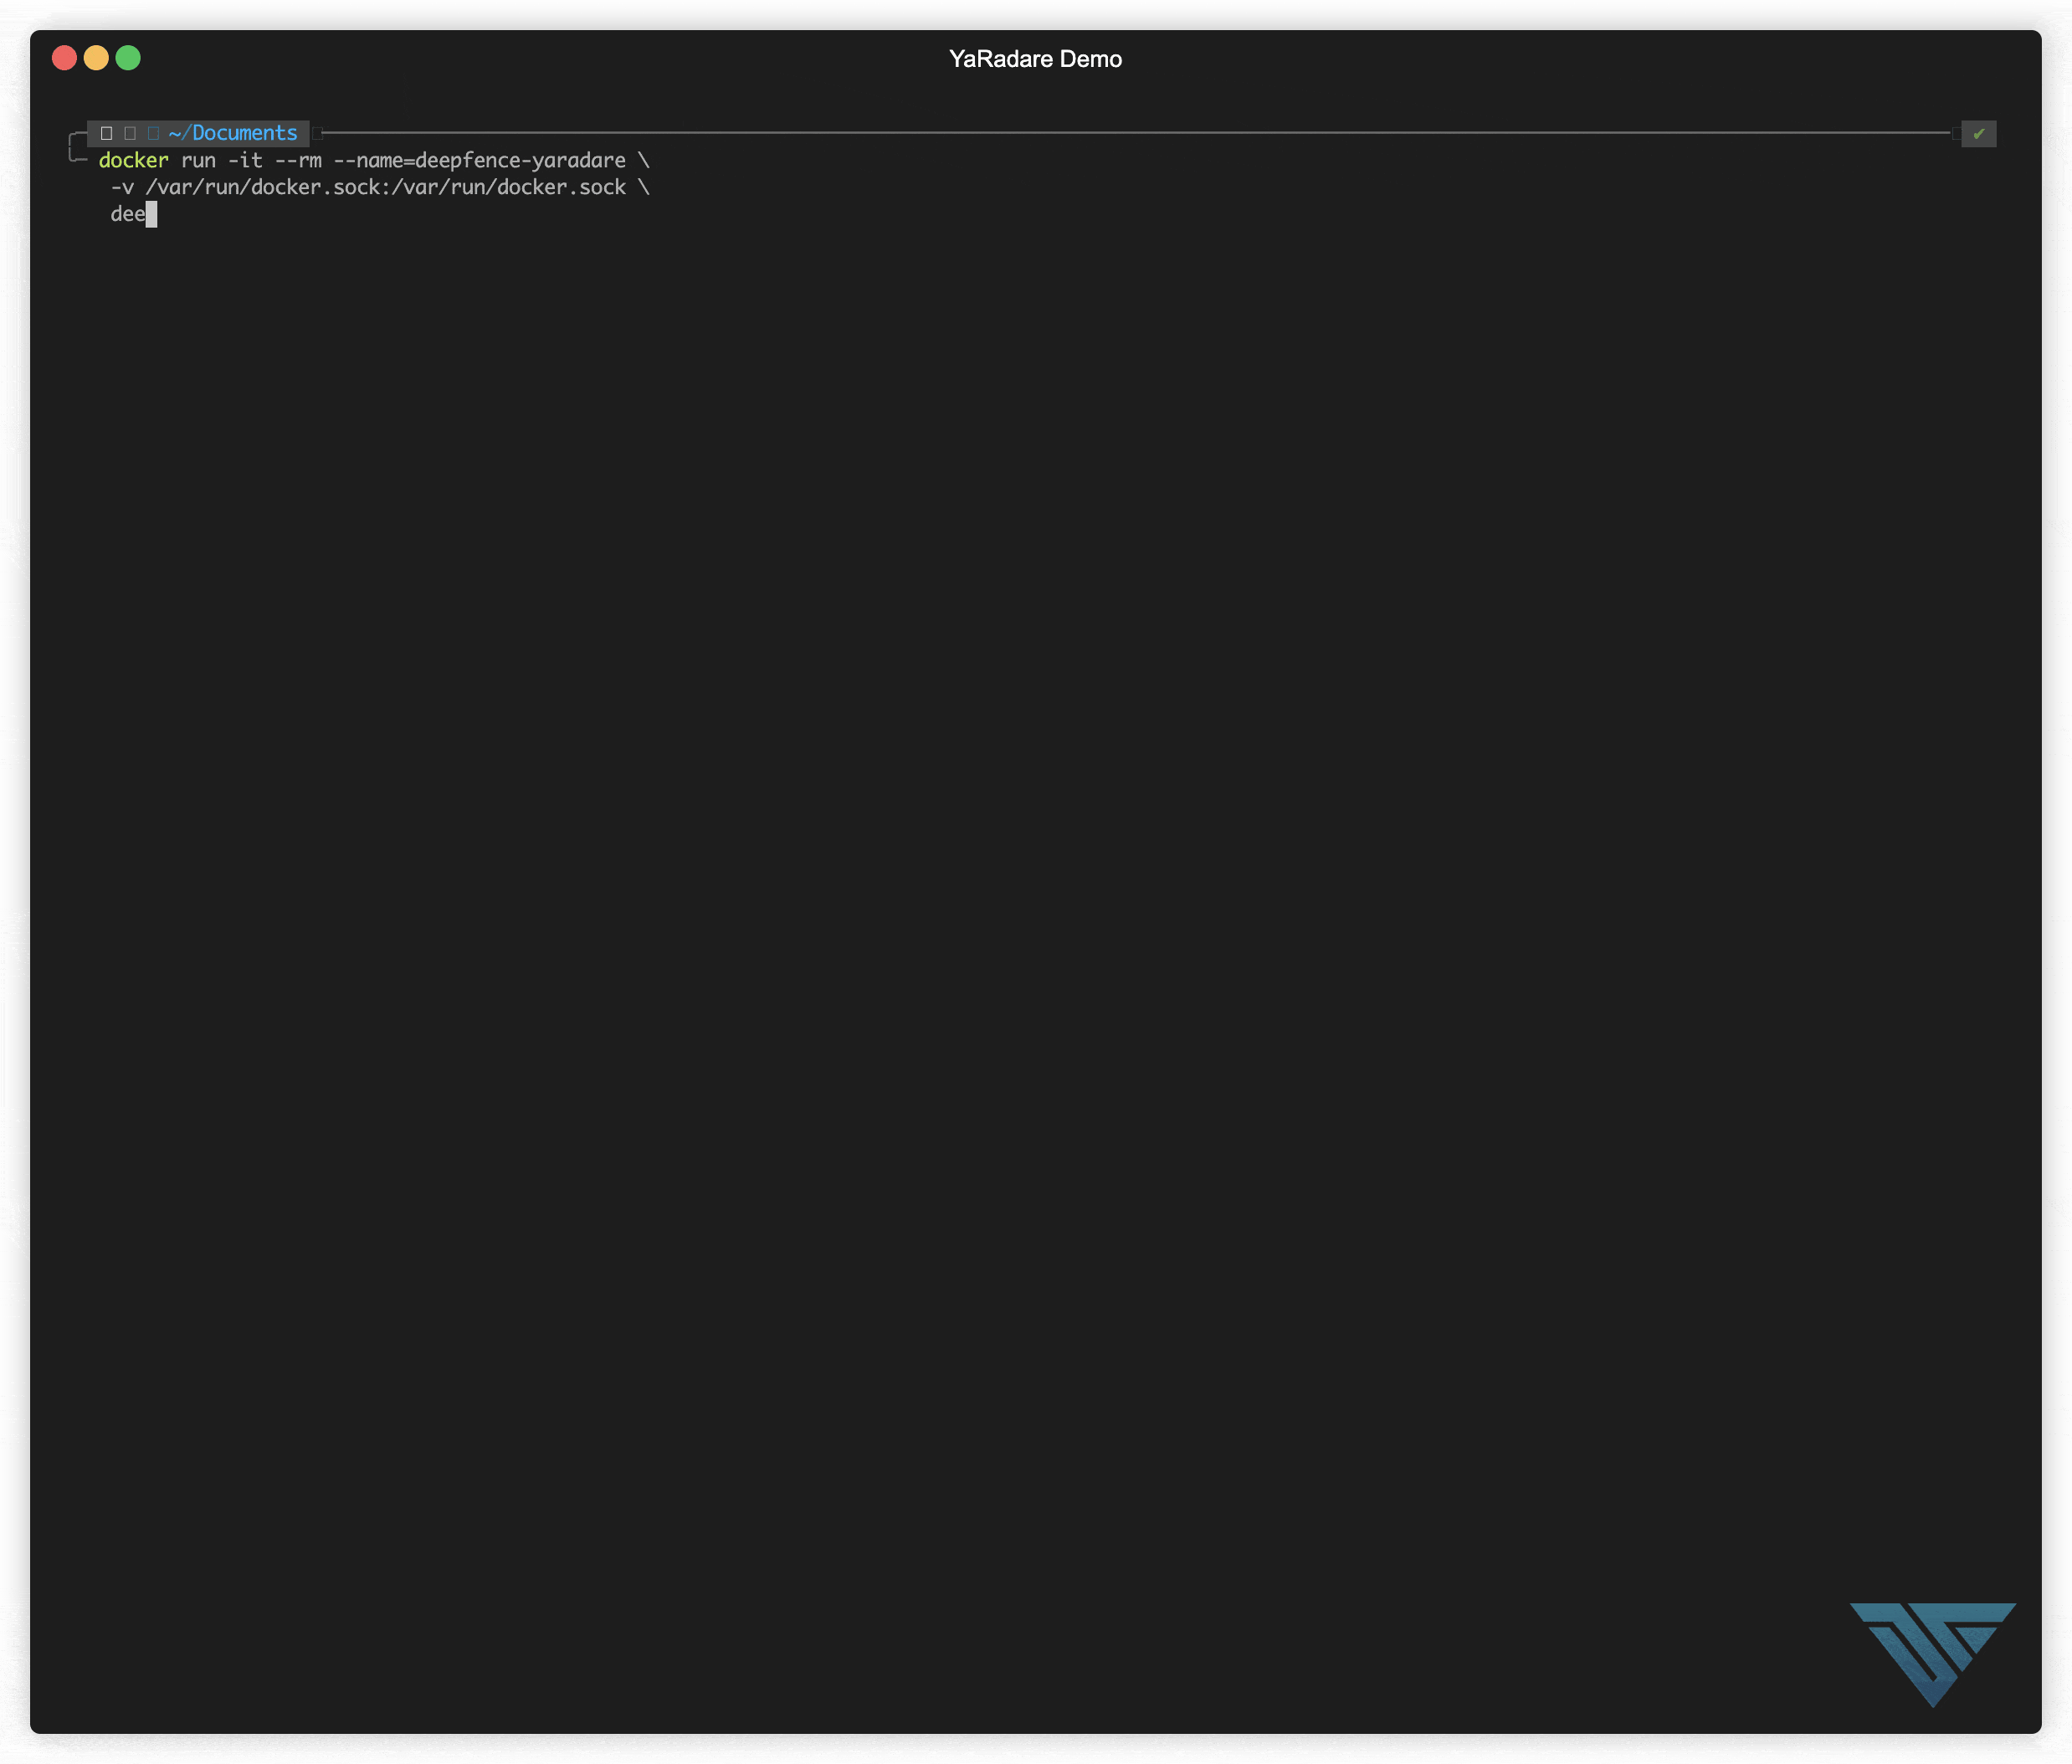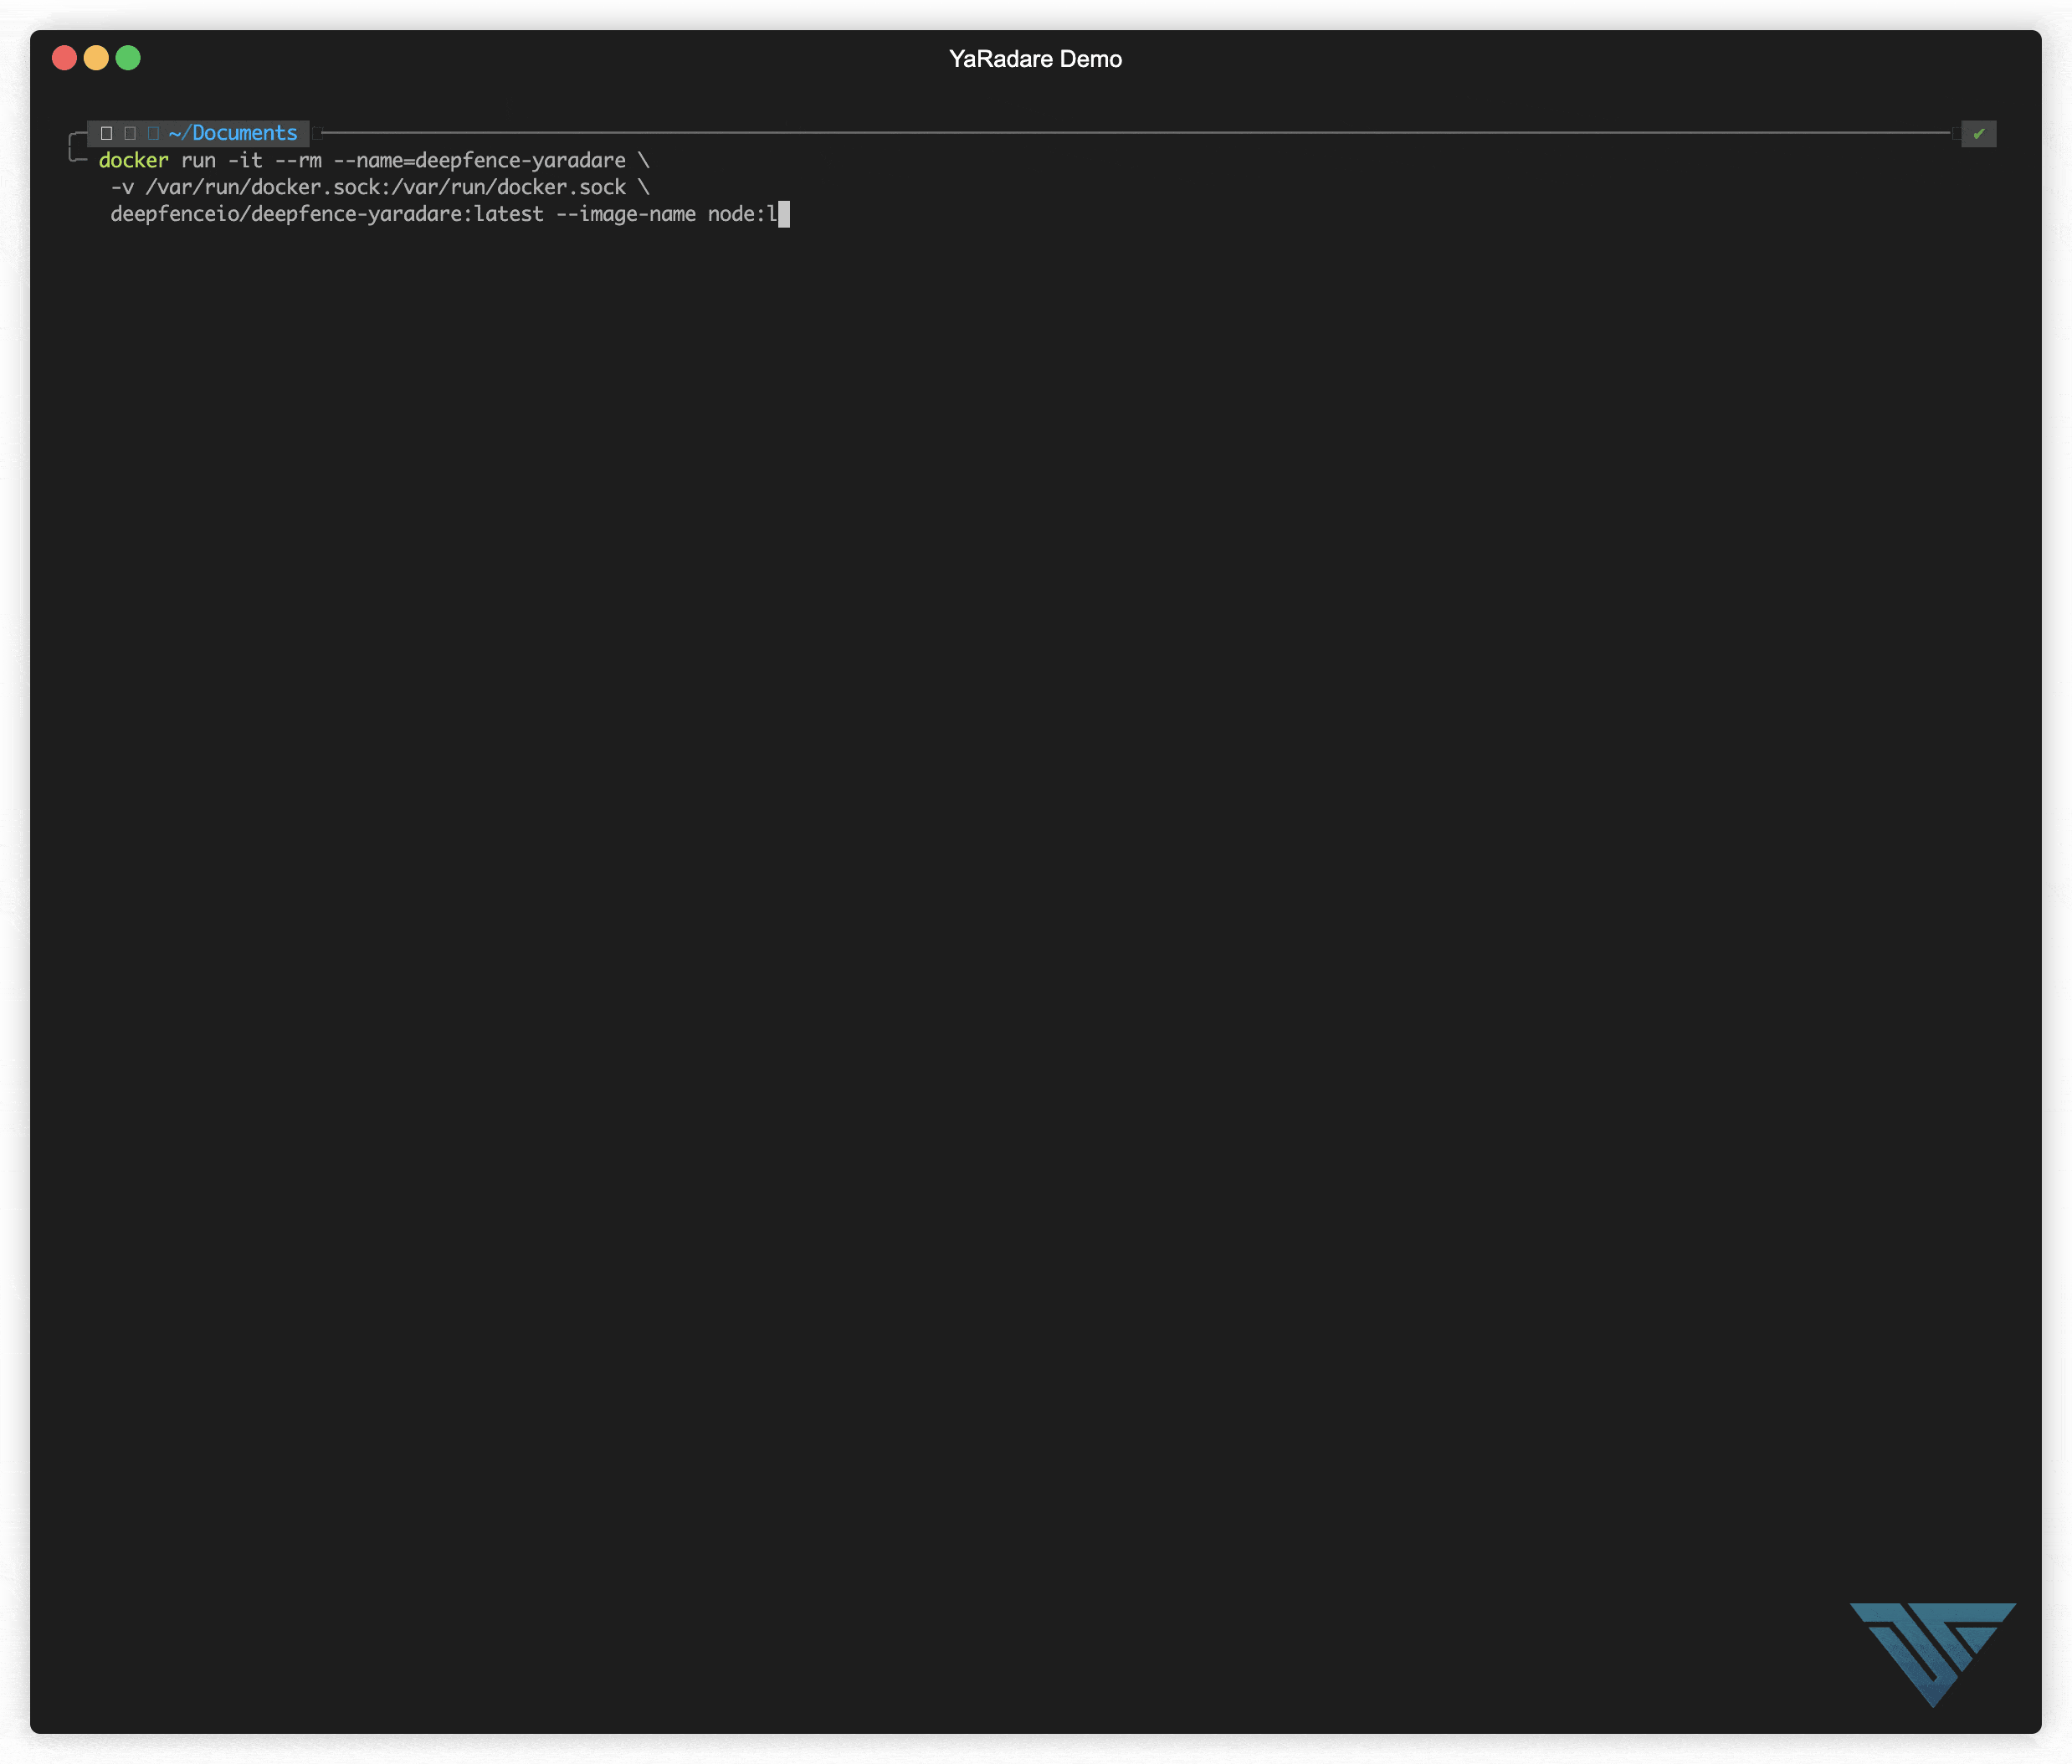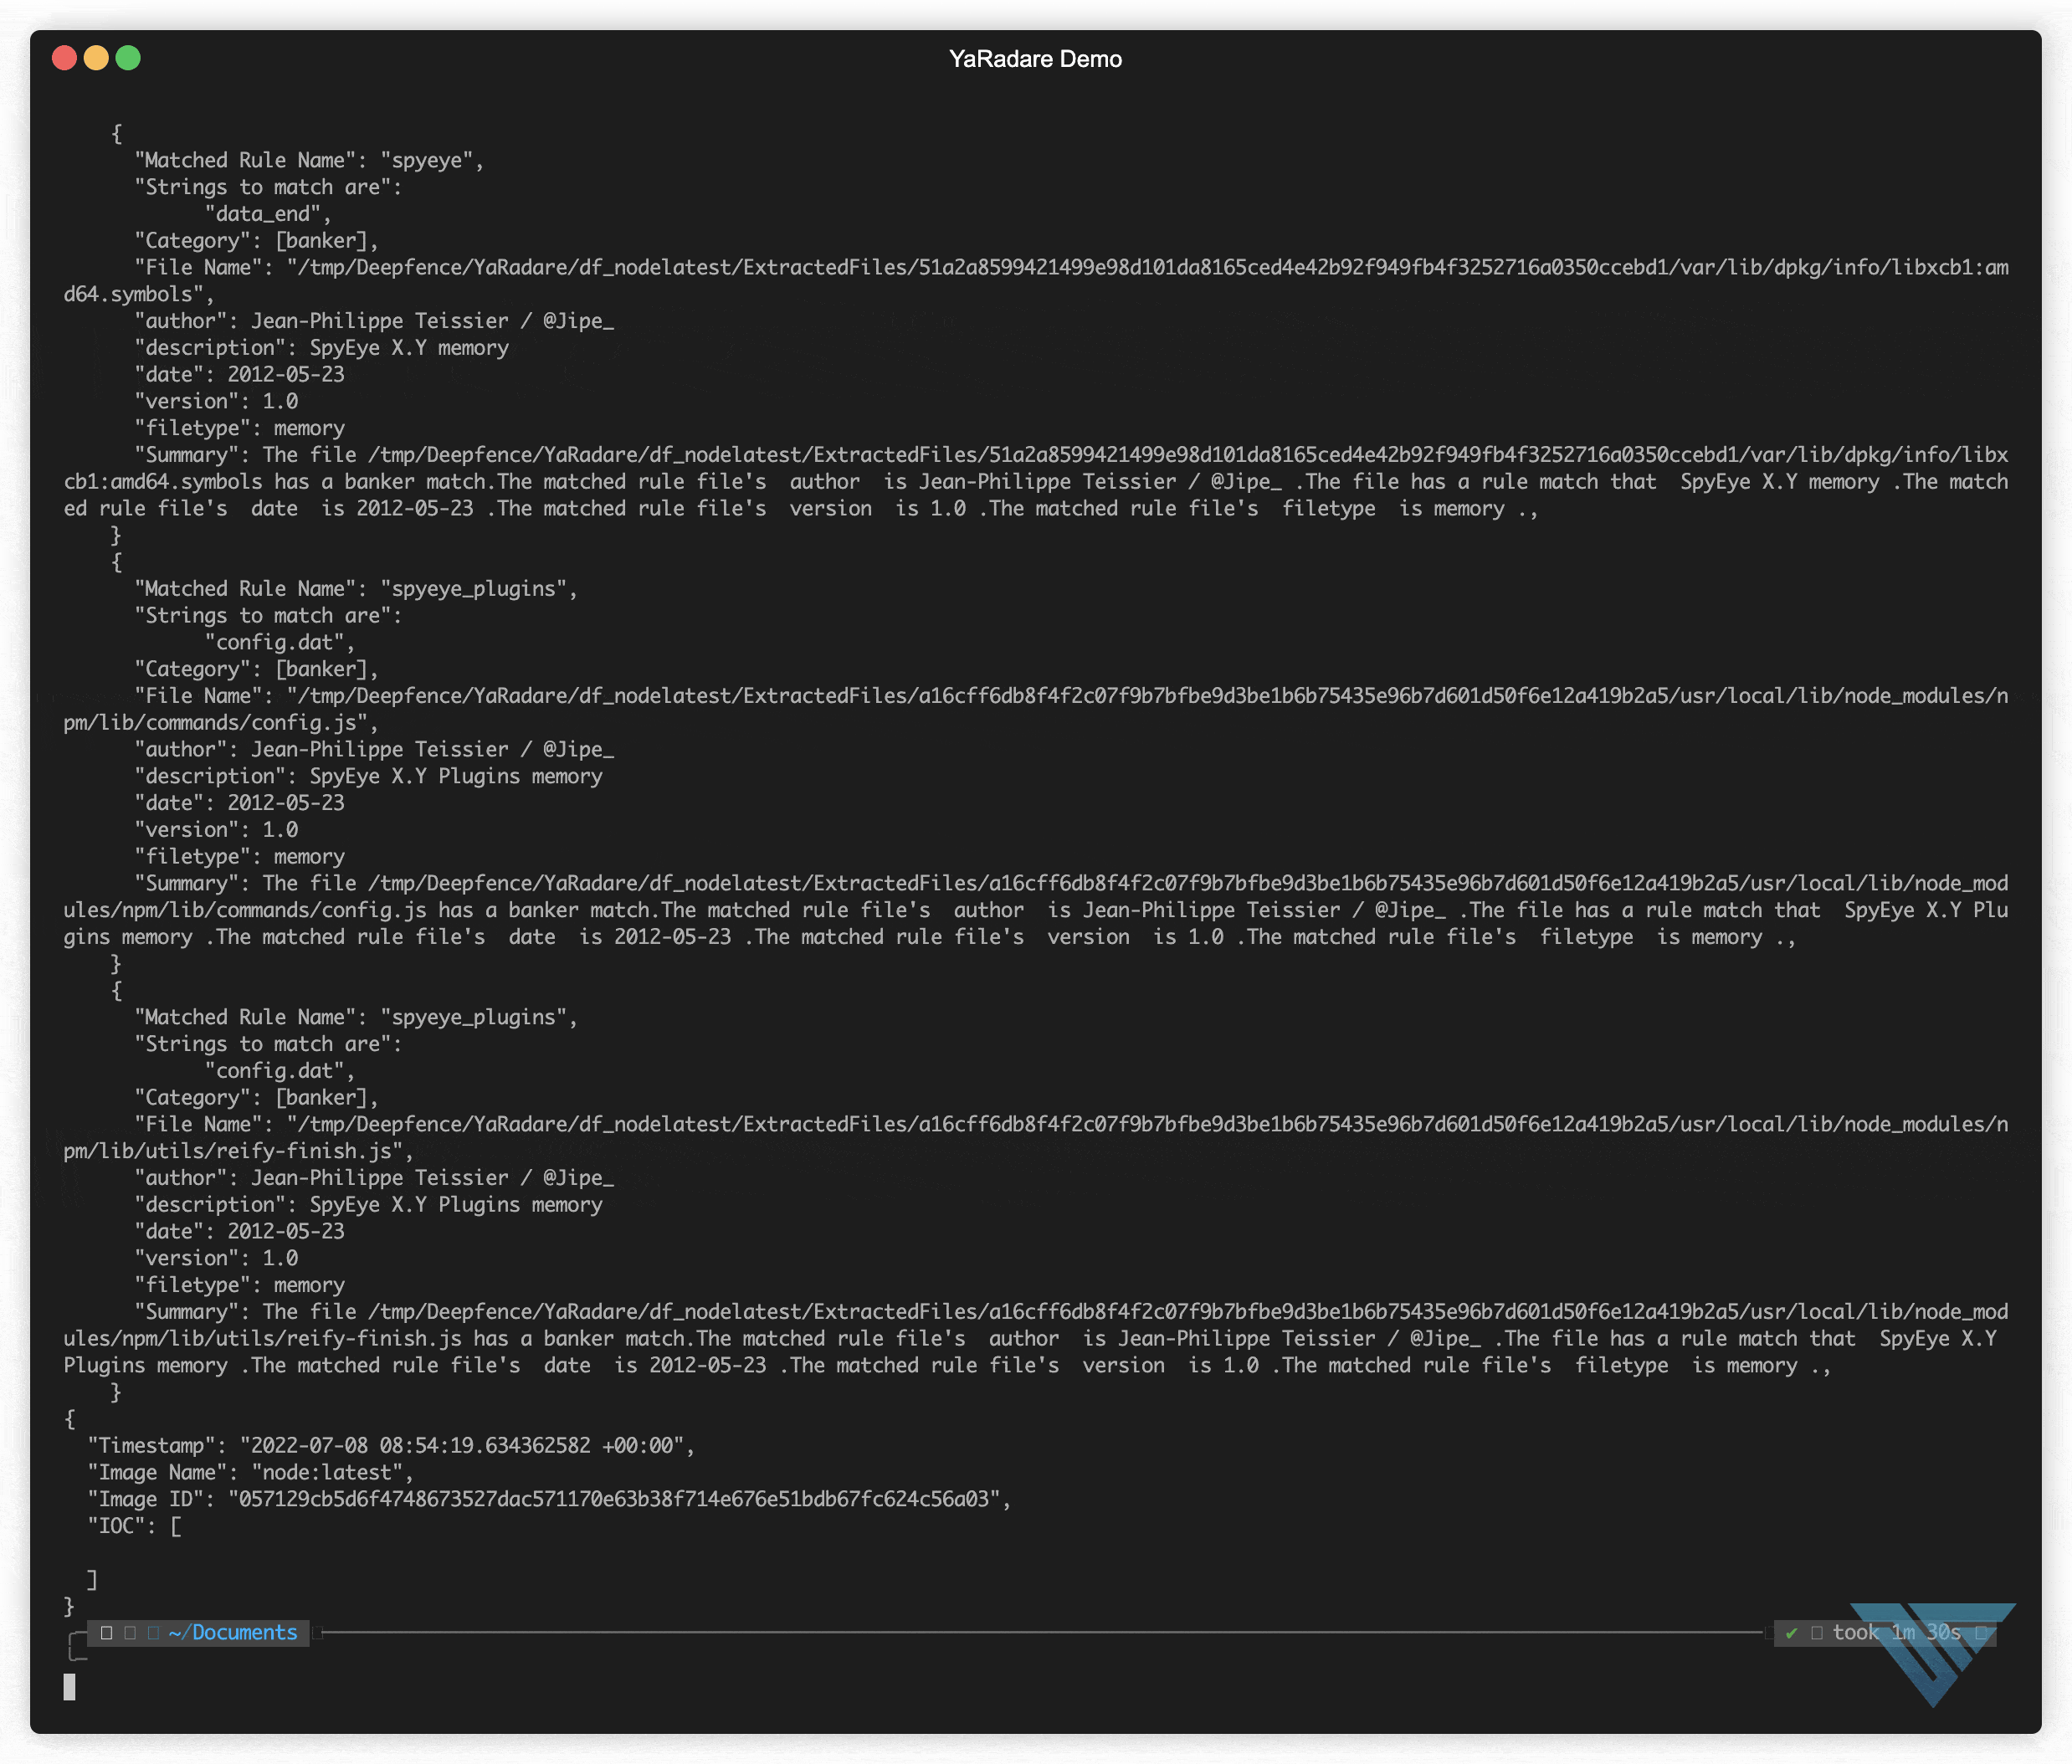
!demo gif
Example: Finding Indicators of Compromise in a container image
Images may be compromised with the installation of a cryptominer such as XMRig. In the following example, we'll scan a legitimiate cryptominer image that contains the same xmrig software that is often installed through an exploit:
Pull the official yarahunter image:
or Build it from source clone this repo and run below command
Scan
Pull the image that needs to be scanned for example metal3d/xmrig and scan it:
Scan the image:
This returns, among other things, clear indication of the presence of XMRig. Note that we store the output (xmrig-scan.json) for quick and easy manipulation:
Rules can also be cached to use next run by mounting a separate path and passing rules-path argument
This returns a list of the IOCs identified in the container we scanned.
To get table formatted output omit --output=json flag
Get in touch
Thank you for using YaraHunter.
Security and Support
For any security-related issues in the YaraHunter project, contact productsecurity _at_ deepfence _dot_ io.
Please file GitHub issues as needed, and join the Deepfence Community Slack channel.
License
The Deepfence YaraHunter project (this repository) is offered under the Apache2 license.
Contributions to Deepfence YaraHunter project are similarly accepted under the Apache2 license, as per GitHub's inbound=outbound policy.
Disclaimer
This tool is not meant to be used for hacking. Please use it only for legitimate purposes like detecting indicator of compromise on the infrastructure you own, not on others' infrastructure. DEEPFENCE shall not be liable for loss of profit, loss of business, other financial loss, or any other loss or damage which may be caused, directly or indirectly, by the inadequacy of YaraHunter for any purpose or use thereof or by any defect or deficiency therein.
项目信息
开发语言:Go
Star 数:1319
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🔍🔍 Malware scanner for cloud-native, as part of CI/CD and at Runtime 🔍🔍展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | YaraHunter - 🔍🔍 Malware scanner for cloud-native, as part of C |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:13:33 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 269 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |