 病毒分析
点击放大
antispy - AntiSpy is a free but powerful anti virus and root
项目说明
AntiSpy
!avatar
English | 简体中文
A powerful anti rootkit toolkit
AntiSpy is a free but powerful anti virus and rootkits toolkit.
It offers you the ability with the highest pri that can detect,analyze and restore kernel modifications and hooks.
With its assistance,you can easily spot and neutralize malwares hidden from normal detectors.
De
* IDE: Studio 2008
* Userspace: MFC
* WDK: WDK7600
* Third-party Library: Codejock toolkit pro
Code Structure
Features
Currently,the following features are a(including but not limited to):
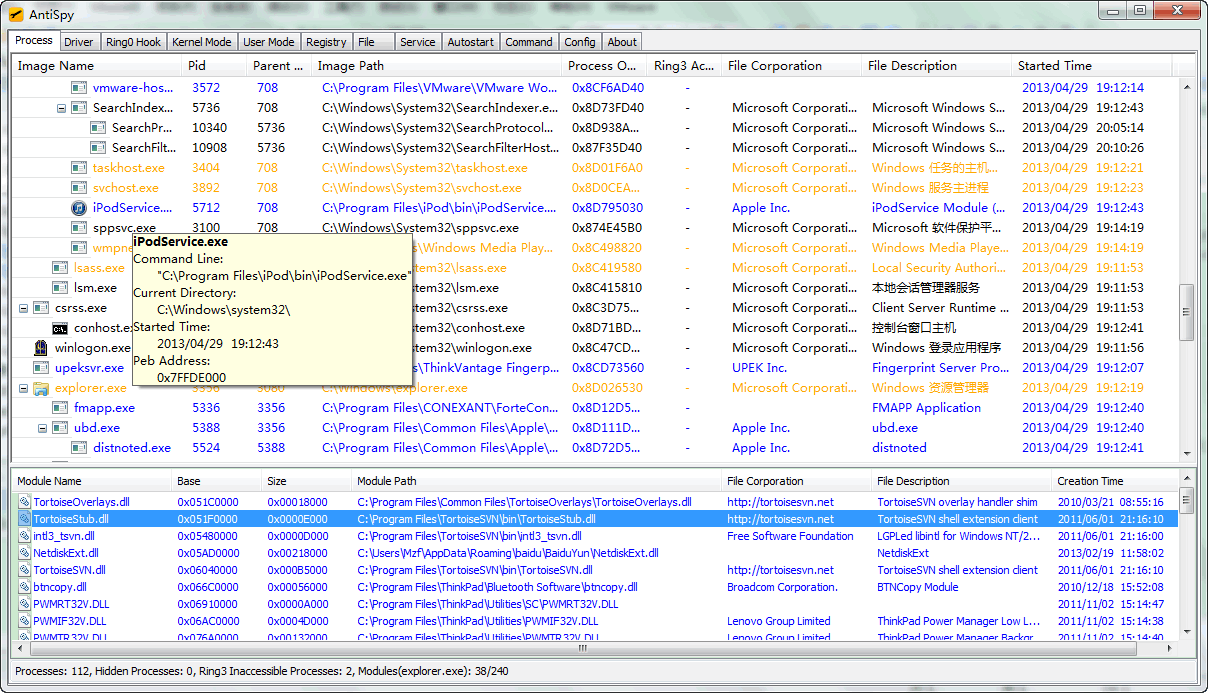
Process Manager
* Display system process and thread basic informations.
* Detect hidden processes,threads,process modules.
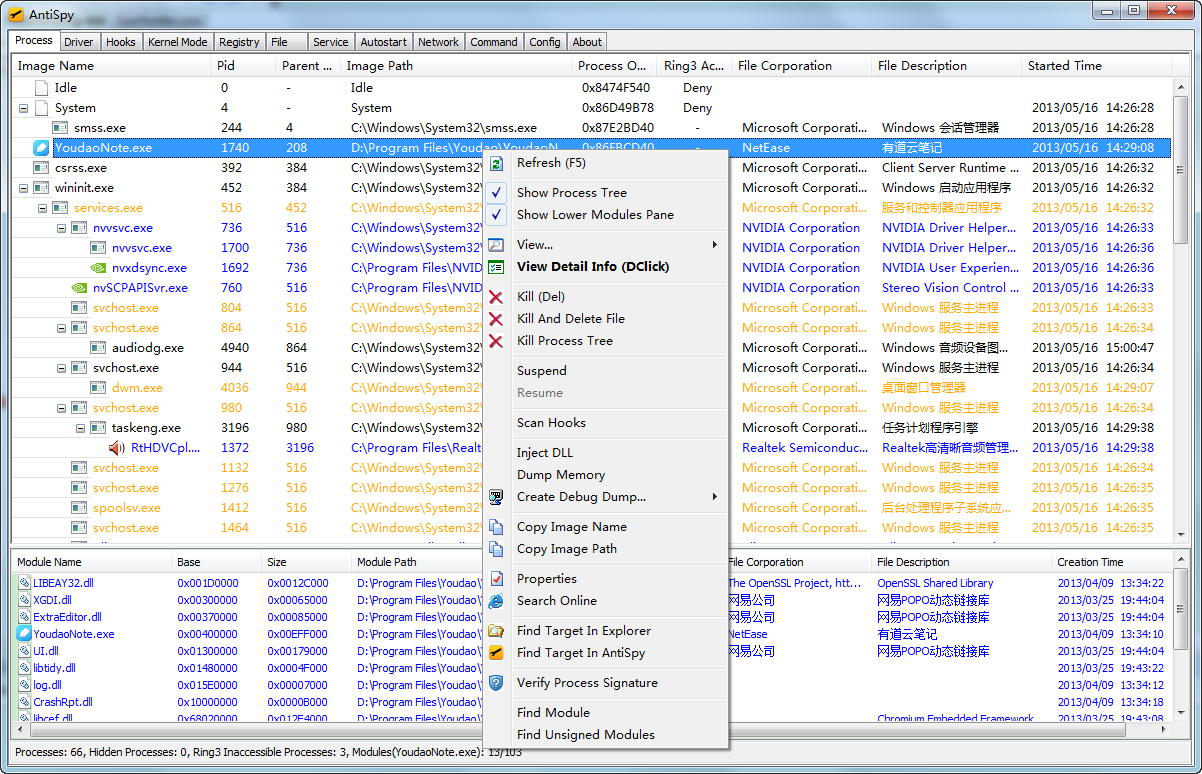
* Terminate, suspend and resume processes and threads.
* View and manipulate process handles,windows and memory regions.
* View and manipulate process hotkeys,pri,and timers.
* Detect and restore process hooks incluing inline hooks,patches,iat and eat hooks.
* Inject dll,dump process memory.
* Create debug dump,include mini dump and full dump.
Kernel Module
* Display kernel module basic information,include image base,size,dri,and so on.
* Detect hidden kernel modules.
* Unload kernel modules.
* Dump kernel image memory.
* Display and delete system dri informations.
Hook Detector
* Detect and restore SSDT,Shadow SSDT,sysenter and int2e hooks.
* Detect and restore FSD and keyboard disptach hooks.
* Detect and restore kernel code hooks including kernel inline hooks,patches,iat and eat hooks.
* Detect and restore message hooks,both global and local.
* Detect and restore kernel ObjectType hooks.
* Display Interrupt Descriptor Table(IDT).
Other Kernel Information
* View and remo notifications.
* View filters for common devices include disk,,keyboard and network devices.
* View IO timers,DPC timers,system threads,and so on.
Registry Manager
* View and edit system registry.
* Detect hidden registry entries using li hi.
File Manager
* Display file basic information,include file name,size,attributes,and so on.
* Detect hidden files.
* View and delete locked files and folders.
Service Manager
* Display system services basic informations.
* Control services status.
* Modify services startup type.
Autorun Manager
* Display almost all kinds of system autorun types.
* Enable,disable or permanently delete autoruns.
Network
* Display current network connections,include TCP and UDP informations.
* View and delete IE plugins and context menu.
* Display winsock pro(LSP).
* View and edit hosts file.
Other Tools
* Hex Editor - View and edit memory,include ring3 process memory and ring0 system memory.
* Disassembler - Like OllyDBG,support ring3 process memory and ring0 system memory.
Settings
* Custom color settings.
User Interfaces
Process Tree
!avatar
Process Menu
!avatar
Network
!avatar
File Manager
!avatar
AutoRun Manager
!avatar
Contact Me
Email:
If you have any need,please feel free to contact with me.
License
Copyright (c) [2010-2019] rights reserved.
AntiSpy is licensed under the Mulan PSL v1.
You can use this software according to the terms and conditions of the Mulan PSL v1.
You may obtain a copy of Mulan PSL v1 at:
THIS SOFTWARE IS PROVIDED ON AN "AS IS" BASIS, WITHOUT WARRANTIES OF ANY KIND, EITHER
EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO NON-INFRINGEMENT, MERCHANTABILITY OR
FIT FOR A PARTICULAR PURPOSE.
See the Mulan PSL v1 for more details.
项目信息
开发语言:C
Star 数:1108
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and restore various kernel modifications and hooks.With its assistance,you can easily spot and neutralize malwares hidden from normal detectors.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | antispy - AntiSpy is a free but powerful anti virus and root |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:14:11 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 464 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |