 病毒分析
点击放大
toolkit - The essential toolkit for reversing, malware analy
项目说明
English | Español
Indetectables Toolkit
Designed as a Swiss Army knife, this curated toolkit is in for malware analysts, crackers, and cybersecurity experts. It is meticulously crafted to support both novice and experienced users.
This toolkit complements the manuals and the numbered theories mirror from our site.

Ad
1. Comprehensive: Contains all essential tools for both simple and complex scenarios.
2. Automated Updates: Integrated with a custom Uni Updater to keep tools updated automatically.
3. Extensible: Easily add new tools by updating bin\updater\tools.ini and linking them in bin\sendto\sendto.
4. Automatic Setup: The installer handles dependencies, en , and can schedule weekly updates.
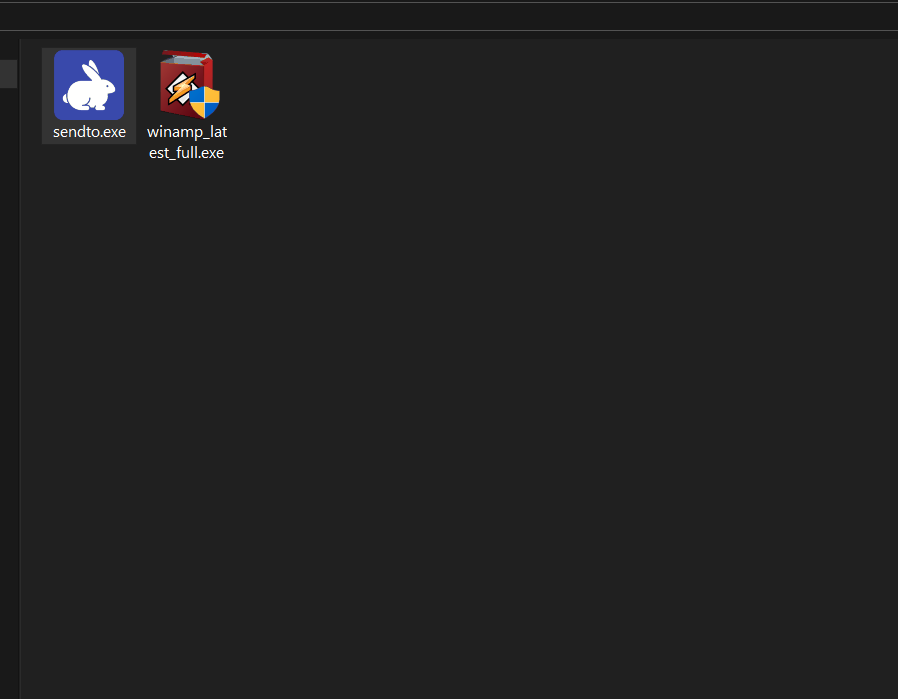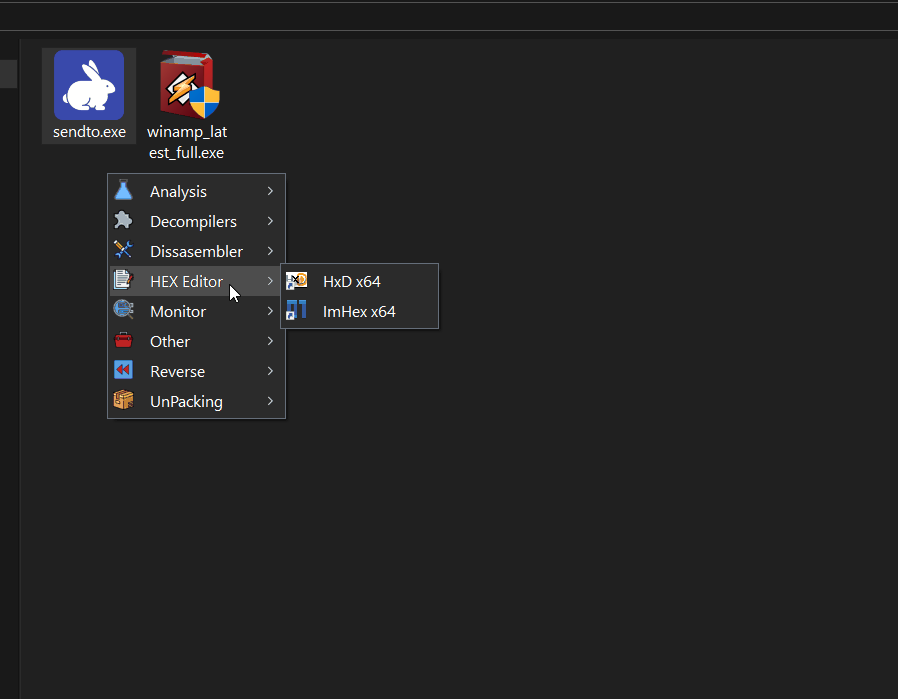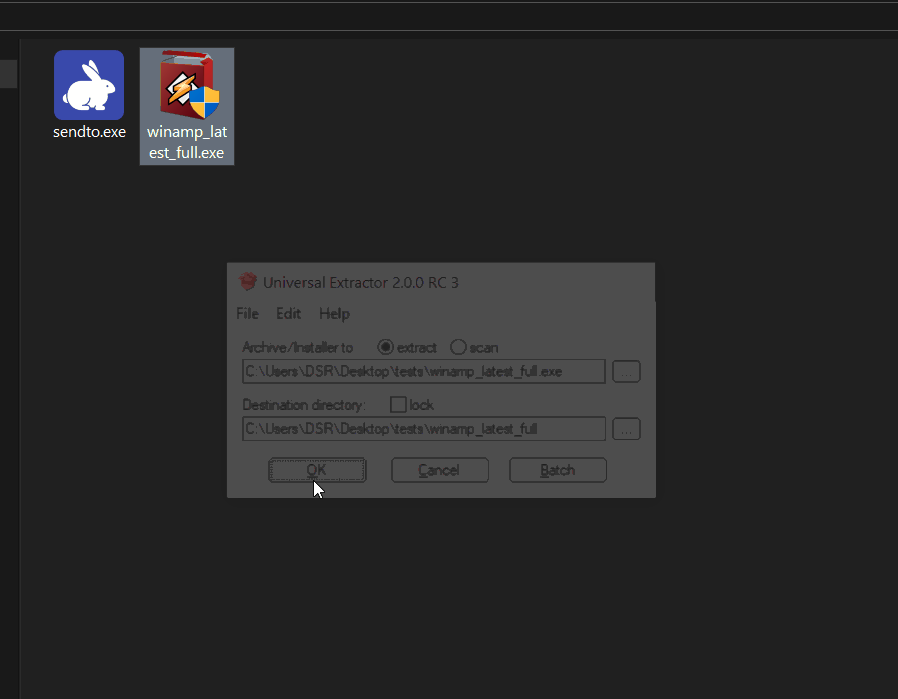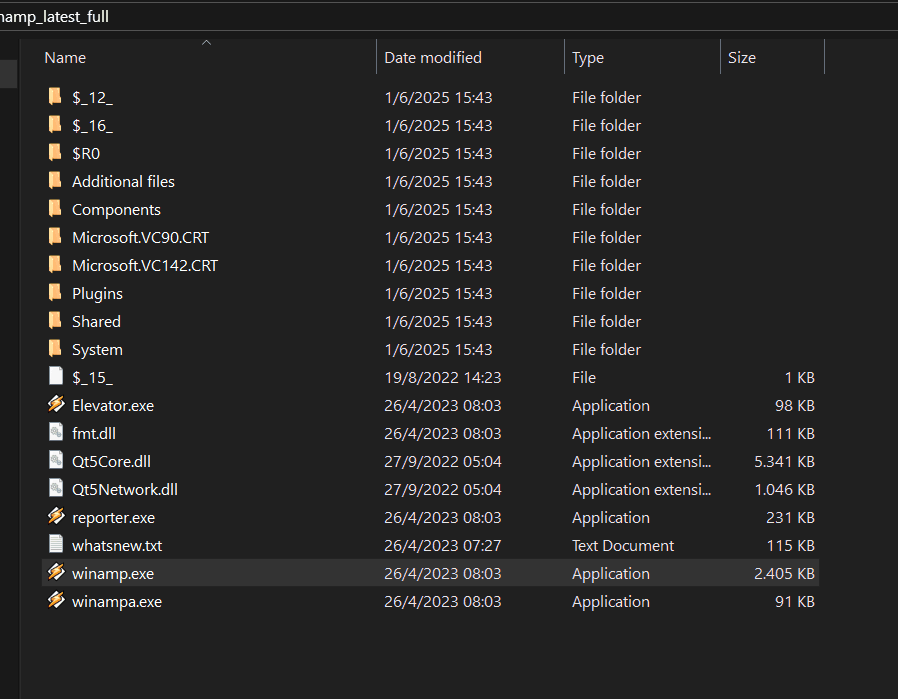
5. Context menu integration: Registers SendTo Recomposed in the Windows right-click menu for files.
Installation
1. Download the stable from the release section.
2. Use the Uni Updater in bin\updater\updater.exe to keep tools updated.
3. If you need to download a specific tool, they are all compressed in the toolkit folder of this repo.
Each release ships two installers: full (toolkit-{}.exe), with every tool listed below, and lite (toolkit-{}-lite.exe), a leaner selection — see the lite tool list. A handful of tools also ship as separate, optional extras packs (extras-{}-{name}.exe: ghidra, oldies, unpacking, vbdec), a on the same releases page and marked in TOOLS.md as *A using the extra called: X*.
The Tool Set
The toolkit includes 102 apps co a wide range of needs. It features both well-known tools and lesser-known, yet highly useful ones, as well as rare tools that are hard to find. All tools are sourced from their official websites, but exercise caution, especially with tools from forum threads. View the complete tool list here.
This toolset is inspired by the old *Crackers Kits* that gained popularity around 2010, but with all their limitations and flaws addressed. We based it on the tools we ha recommended within our community.
Our first release was 2020.2, published on February 17, 2020, which makes this a more —and actively maintained— project than many current alternatives.
Contributions
Pull Requests are welcome. For major changes, create an Issue for discussion. Tools are compressed with 7-zip, using the format {name} - {}.7z.
项目信息
开发语言:Inno Setup
Star 数:1009
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The essential toolkit for reversing, malware analysis, and cracking展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | toolkit - The essential toolkit for reversing, malware analy |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:14:30 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 514 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |