 病毒分析
点击放大
offensive-bookmarks - A collection of bookmarks for penetration testers,
项目说明
Offensi
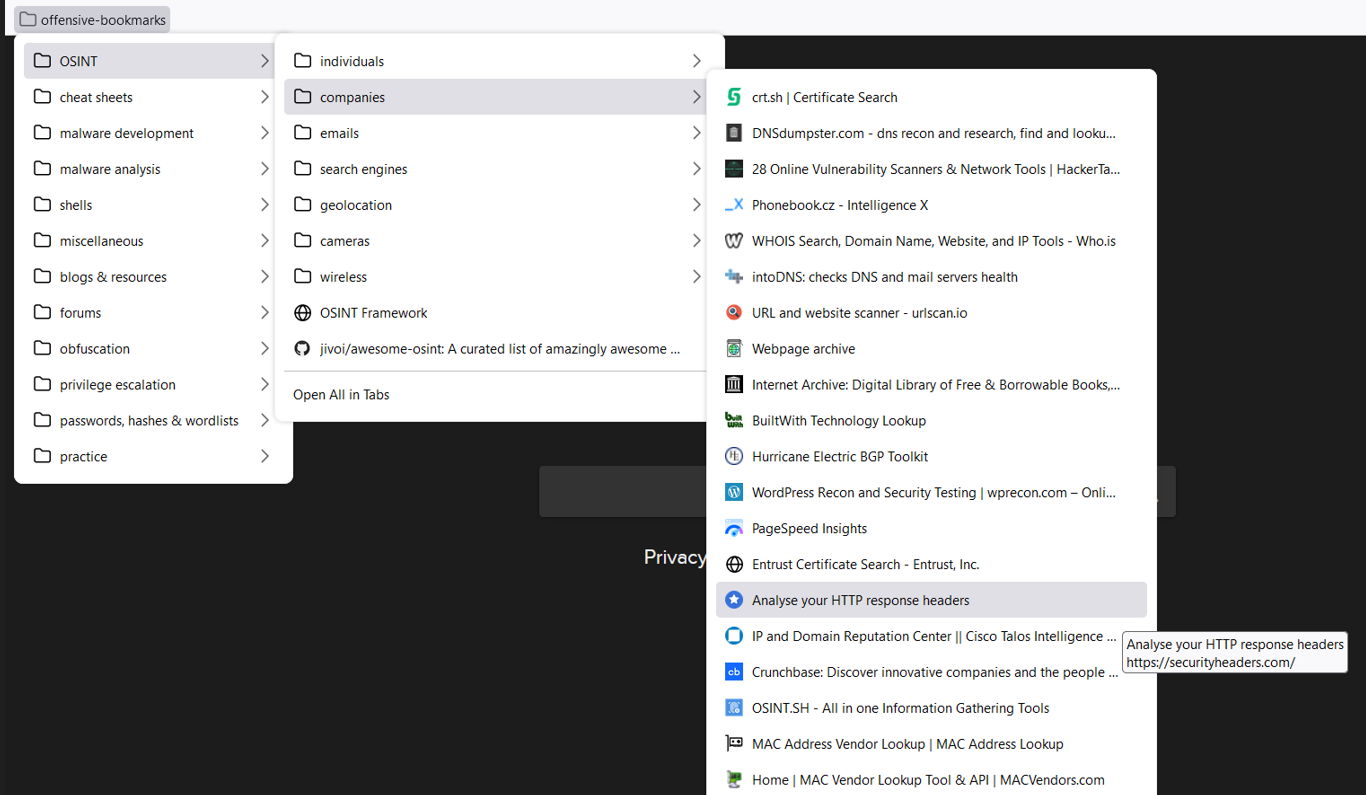
A collection of bookmarks for penetration testers, bug bounty hunters, malware de, reverse engineers and anyone who is just interested in infosec topics.
!offensi
Description
Offensi is a curated collection of browser bookmarks specifically designed for security professionals, including penetration testers, malware de, and reverse engineers. This comprehensi provides a resource for indi in in cybersecurity research, assessment, and offensi acti.
How to install
* Download offensi.html
* Firefox: Bookmarks -> Manage bookmarks -> Import and Backup -> Import Bookmarks from HTML -> select offensi.html
* Edge: Settings -> Profiles -> Import browser data -> Import from other browsers -> Import from Fa or bookmarks HTML file -> select offensi.html
* Chrome: Bookmarks -> Import bookmarks and settings -> Bookmarks HTML file -> select offensi.html
Key features
The general categories are:
* OSINT
>face recognition, username lookup, subdomains, SSL certificates, web technologies, assets, urls, whois info, online scanners, web archives, mac address lookup, email lookup, search engines, geolocation, camera, wireless
* cheat sheets
>web cheat sheets, linux cheat sheets, windows cheatsheets, offensi cheat sheets
* malware de
>code repositories, blogs, youtube channels
* malware analysis
>tools, sandboxes, resources
* shells
>collection of reverse shells
* miscellaneous
>encoders, decoders, file transfers, file formatting
* blogs & resources
>general info blogs, youtube channels
* forums
>forums
* obfuscation
>command prompt obfuscators, powershell obfuscators, python obfuscators, ja obfuscators, php obfuscators, C/C++ obfuscators, .NET obfuscators
* pri escalation
>windows pri escalation, linux pri escalation
* passwords, hashes & wordlists
>default passwords, wordlists, cracking tools
* practice
>cybersecurity labs
项目信息
开发语言:HTML
Star 数:922
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A collection of bookmarks for penetration testers, bug bounty hunters, malware developers, reverse engineers and anyone who is just interested in infosec topics.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | offensive-bookmarks - A collection of bookmarks for penetration testers, |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:14:57 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 415 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |