 病毒分析
点击放大
misp-galaxy - Clusters and elements to attach to MISP events or
项目说明
misp-galaxy
!misp galaxy logo
!Python application
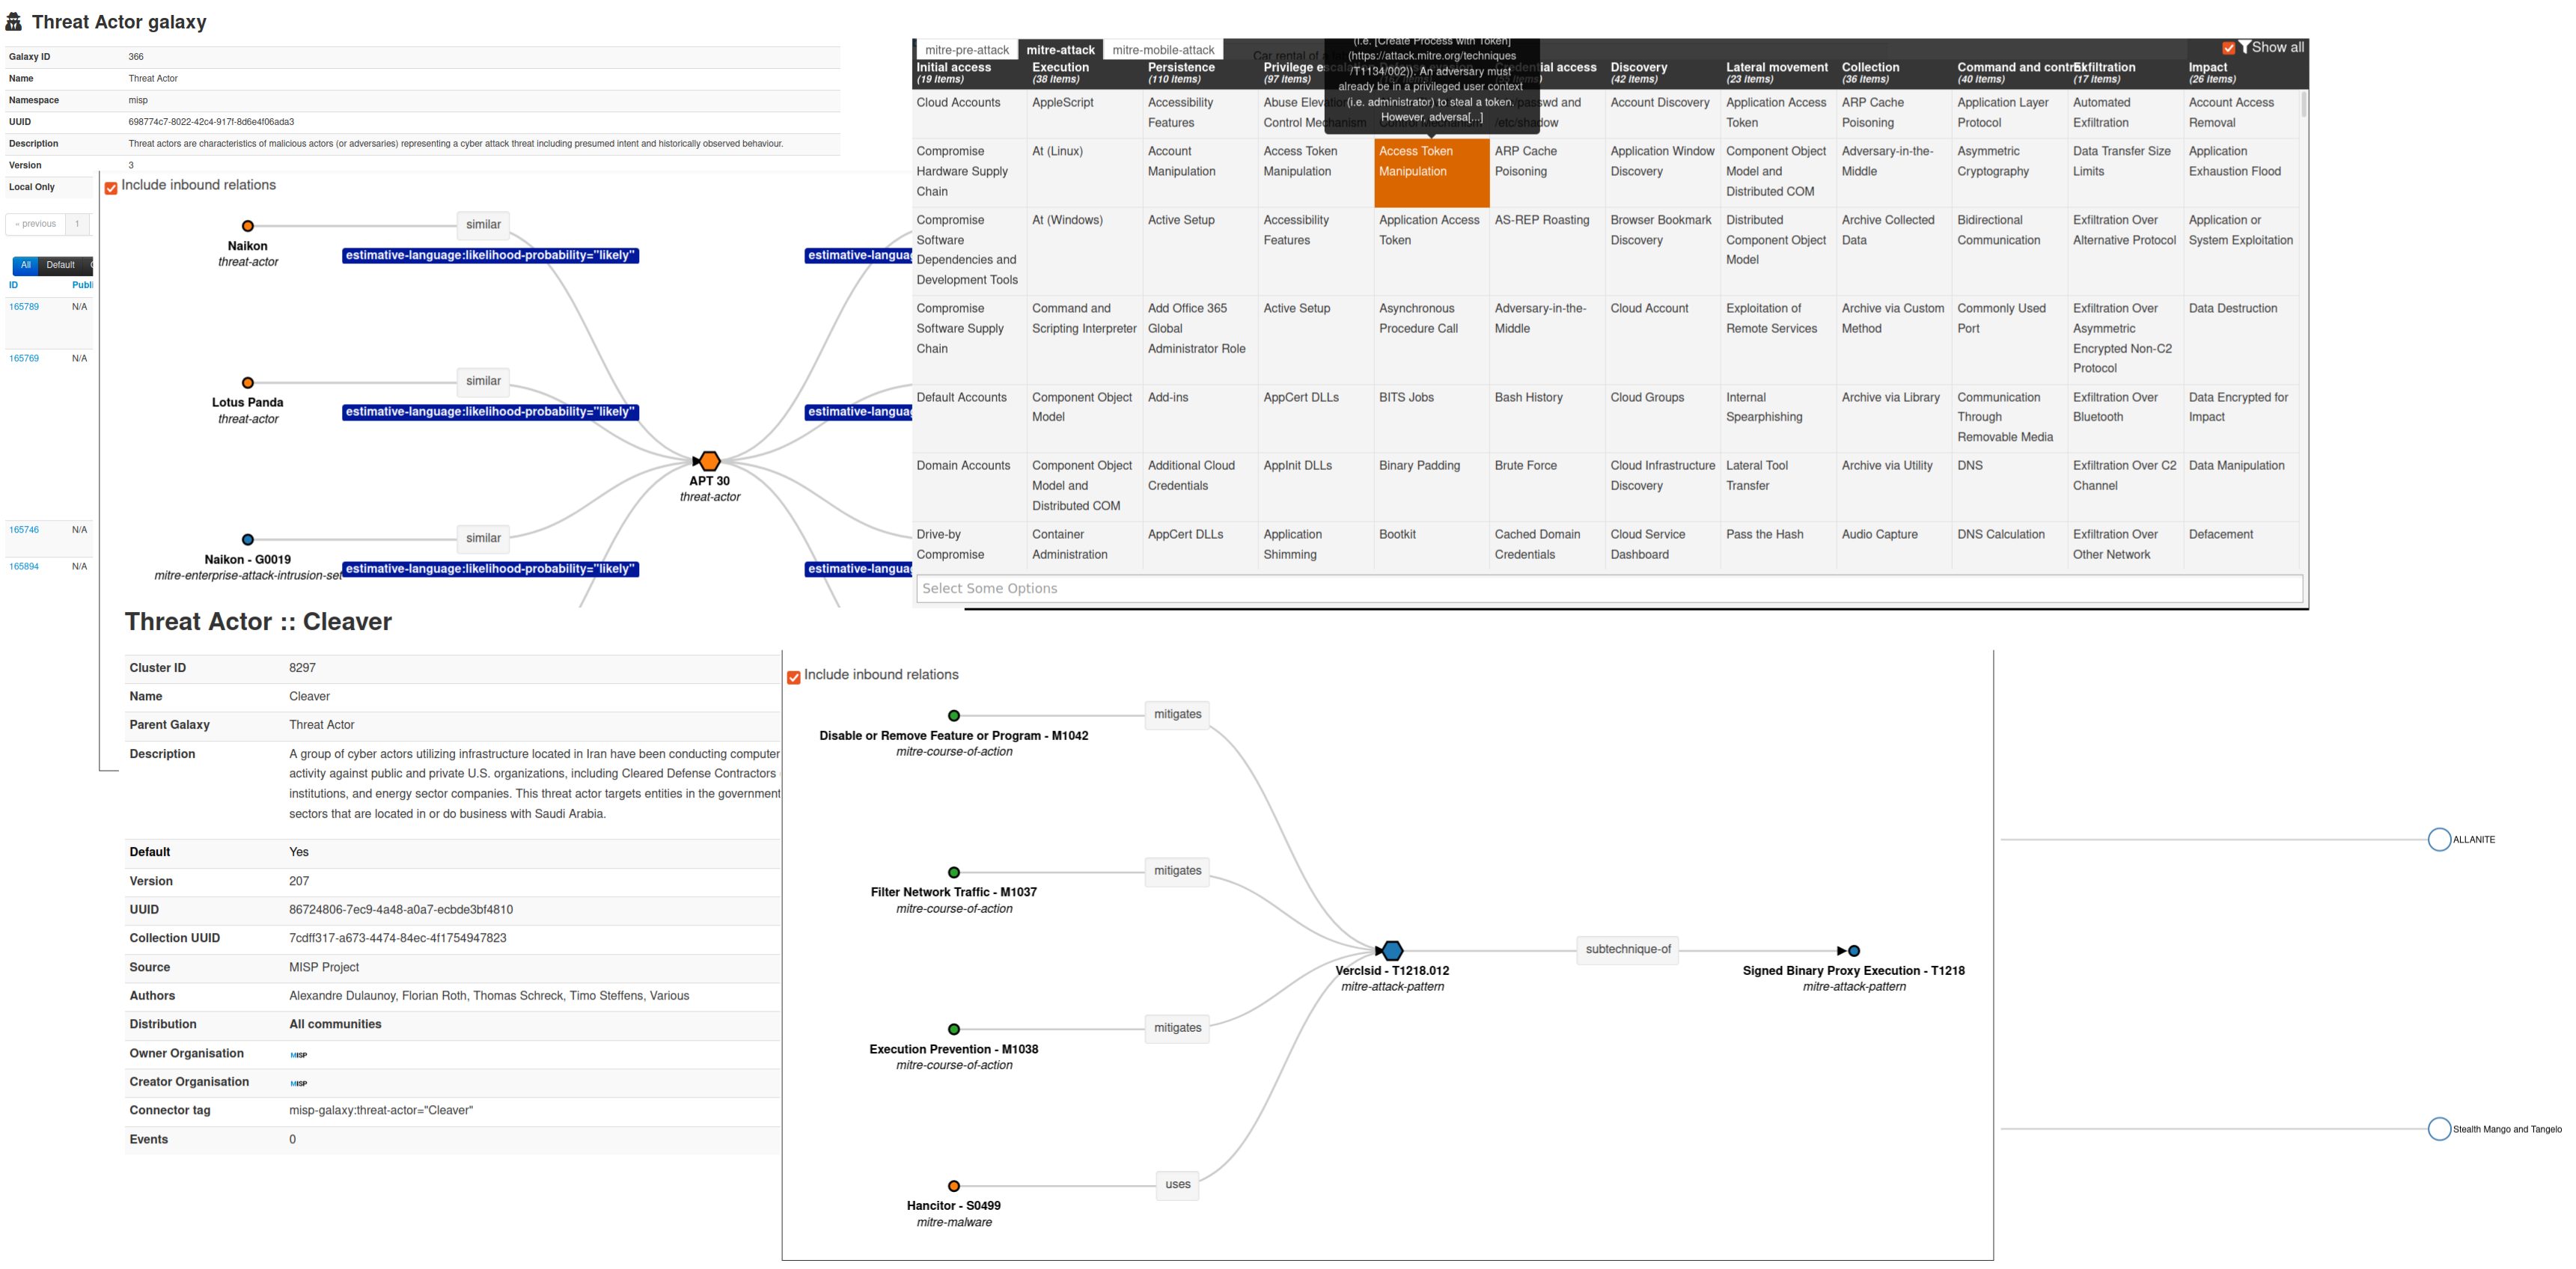
!Screenshot - MISP galaxy integeration in MISP threat intelligence platform
MISP galaxy is a simple method to express a large object called cluster that can be attached to MISP events or
attributes. A cluster can be composed of one or more elements. Elements are expressed as key-. There
are default knowledge base (such as Threat Actors, Tools, Ransomware, ATT&CK matrixes) a in MISP galaxy
but those can be o, replaced, updated, forked and shared as you wish.
Existing clusters and can be used as-is or as a common knowledge base. MISP distribution can be applied
to each cluster to permit a limited or broader distribution scheme.
Galaxies can be also used to expressed existing matrix-like standards such as MITRE ATT&CK(tm) or custom ones.
The objective is to have a comment set of clusters for organizations starting analysis but that can be expanded
to localized information (which is not shared) or additional information (that can be shared).
A Galaxy - clusters
360.net Threat Actors
360.net Threat Actors - Known or estimated ad groups as identified by 360.net.
Category: *actor* - source: * - total: *42* elements
[HTML] - [JSON]
Agent Threat Rules
Agent Threat Rules - Open detection rules for AI agent threats — prompt injection, tool poisoning, MCP ser, skill compromise. Each cluster value is one ATR rule with category, se, and C/MITRE ATLAS references where mapped.
Category: *agent-threat-rules* - source: * - total: *713* elements
[HTML] - [JSON]
Ammunitions
Ammunitions - Common ammunitions galaxy
Category: *firearm* - source: * - total: *409* elements
[HTML] - [JSON]
Android
Android - Android malware galaxy based on multiple open sources.
Category: *tool* - source: *Open Sources* - total: *450* elements
[HTML] - [JSON]
Azure Threat Research Matrix
Azure Threat Research Matrix - The purpose of the Azure Threat Research Matrix (ATRM) is to educate readers on the potential of Azure-based tactics, techniques, and procedures (TTPs). It is not to teach how to weaponize or specifically abuse them. For this reason, some specific commands will be obfuscated or parts will be omitted to prevent abuse.
Category: *atrm* - source: * - total: *90* elements
[HTML] - [JSON]
attck4fraud
attck4fraud - attck4fraud - Principles of MITRE ATT&CK in the fraud domain
Category: *guidelines* - source: *Open Sources* - total: *71* elements
[HTML] - [JSON]
Backdoor
Backdoor - A list of backdoor malware.
Category: *tool* - source: *Open Sources* - total: *29* elements
[HTML] - [JSON]
Banker
Banker - A list of banker malware.
Category: *tool* - source: *Open Sources* - total: *53* elements
[HTML] - [JSON]
Bhadra Framework
Bhadra Framework - Bhadra Threat Modeling Framework
Category: *mobile* - source: * - total: *47* elements
[HTML] - [JSON]
Busy is the New Stupid framework
Busy is the New Stupid framework - Busy is the New Stupid framework - A tactical framework, examining how busyness compromises cogniti, strategic thinking, and effecti. Created by Ross Young.
Category: *user-tie* - source: * - total: *40* elements
[HTML] - [JSON]
Botnet
Botnet - Botnet galaxy.
Category: *tool* - source: *MISP Project* - total: *148* elements
[HTML] - [JSON]
Branded
Branded - List of known and attacks with a branding
Category: ** - source: *Open Sources* - total: *14* elements
[HTML] - [JSON]
Cert EU Go
Cert EU Go - Cert EU Go
Category: *sector* - source: *CERT-EU* - total: *6* elements
[HTML] - [JSON]
China Defence Uni Tracker
China Defence Uni Tracker - The China Defence Uni Tracker is a database of Chinese institutions engaged in military or security-related science and technology research. It was created by ASPI’s International Cyber Policy Centre.
Category: *academic-institution* - source: *ASPI International Cyber Policy Centre* - total: *159* elements
[HTML] - [JSON]
Concealment Layers for Online Anonymity and Knowledge (CLOAK)
Concealment Layers for Online Anonymity and Knowledge (CLOAK) - Concealment Layers for Online Anonymity and Knowledge (CLOAK) is a knowledge base of cybercriminal concealment measures inspired by MITRE ATT&CK. This matrix-like galaxy organises concealment practices across technical, beha, and physical layers to support in, common referencing, gap analysis, and defensi. The source project describes CLOAK as derived from qualitati over more than 200 OpSec guides and its initial public as containing 13 tactics, 109 techniques, 679 sub-techniques, and 586 procedures.
Category: *concealment* - source: * - total: *13* elements
[HTML] - [JSON]
CONCORDIA Mobile Modelling Framework - Attack Pattern
CONCORDIA Mobile Modelling Framework - Attack Pattern - A list of Techniques in CONCORDIA Mobile Modelling Framework.
Category: *cmtmf-attack-pattern* - source: * - total: *93* elements
[HTML] - [JSON]
Country
Country - Country meta information based on the database provided by geonames.org.
Category: *country* - source: *MISP Project* - total: *252* elements
[HTML] - [JSON]
Cryptominers
Cryptominers - A list of cryptominer and cryptojacker malware.
Category: *Cryptominers* - source: *Open Source Intelligence* - total: *5* elements
[HTML] - [JSON]
CTI-CMM 1.3
CTI-CMM 1.3 - Cyber Threat Intelligence Capability Maturity Model (CTI-CMM) 1.3 maturity-indicator practices represented as a matrix-like galaxy by stakeholder domain.
Category: *cyber-threat-intelligence-maturity-model* - source: * - total: *199* elements
[HTML] - [JSON]
CyberFundamentals 2023 Assurance Requirements
CyberFundamentals 2023 Assurance Requirements - CyberFundamentals 2023 assurance-le matrix for MISP. Each cluster value is a le control instance with pro and key-measure metadata; normative text is referenced, not embedded.
Category: *cybersecurity-framework* - source: * - total: *233* elements
[HTML] - [JSON]
CyberFundamentals 2023 Control Catalogue
CyberFundamentals 2023 Control Catalogue - Normalized CyberFundamentals 2023 control catalogue. preser, assurance-le, official pro, and key-measure mapping without reproducing normative text.
Category: *cybersecurity-framework* - source: * - total: *107* elements
[HTML] - [JSON]
DIMA Techniques
DIMA Techniques - DIMA is a social engineering and cogniti framework organized by phase, tactic, and technique.
Category: *dima* - source: * - total: *44* elements
[HTML] - [JSON]
Actor Types
Actor Types - DISARM is a framework designed for describing and understanding disinformation incidents.
Category: *disarm* - source: * - total: *33* elements
[HTML] - [JSON]
Countermeasures
Countermeasures - DISARM is a framework designed for describing and understanding disinformation incidents.
Category: *disarm* - source: * - total: *139* elements
[HTML] - [JSON]
Detections
Detections - DISARM is a framework designed for describing and understanding disinformation incidents.
Category: *disarm* - source: * - total: *94* elements
[HTML] - [JSON]
Techniques
Techniques - DISARM is a framework designed for describing and understanding disinformation incidents.
Category: *disarm* - source: * - total: *298* elements
[HTML] - [JSON]
Election guidelines
Election guidelines - Uni De and Security Guidelines as Applicable to Election Technology.
Category: *guidelines* - source: *Open Sources* - total: *23* elements
[HTML] - [JSON]
Entity
Entity - Description of entities that can be in in events.
Category: *actor* - source: *MISP Project* - total: *4* elements
[HTML] - [JSON]
Synthetic Exercise World
Synthetic Exercise World - Self-contained fictional world dataset for cyber exercises and standards documents.
Category: *tool* - source: * - total: *60* elements
[HTML] - [JSON]
Exploit-Kit
Exploit-Kit - Exploit-Kit is an enumeration of some exploitation kits used by ad. The list includes document, browser and router exploit kits.It's not meant to be totally exhaustive but aim at co the most seen in the past 5 years
Category: *tool* - source: *MISP Project* - total: *54* elements
[HTML] - [JSON]
Firearms
Firearms - Common firearms galaxy
Category: *firearm* - source: * - total: *5953* elements
[HTML] - [JSON]
FireHOL IPsets
FireHOL IPsets - FireHOL IPsets Knowlege Base
Category: *IPset* - source: * - total: *194* elements
[HTML] - [JSON]
FIRST CSIRT Services Framework
FIRST CSIRT Services Framework - The Computer Security Incident Response Team (CSIRT) Services Framework is a high-le describing in a structured way a collection of cyber security services and associated functions that Computer Security Incident Response Teams and other teams pro incident management related services may provide
Category: *csirt* - source: * - total: *97* elements
[HTML] - [JSON]
FIRST DNS Abuse Techniques Matrix
FIRST DNS Abuse Techniques Matrix - The Domain Name System (DNS) is a critical part of the Internet, including mapping domain names to IP addresses. Malicious threat actors use domain names, their corresponding technical resources, and other parts of the DNS infrastructure, including its protocols, for their malicious cyber operations. CERTs are confronted with reported DNS abuse on a continuous basis, and rely heavily on DNS analysis and infrastructure to protect their constituencies. Understanding the international customary norms applicable for detecting and mitigating DNS abuse from the perspective of the global incident response community is critical for the open Internet’s stability, security and resiliency. See also for more information.
Category: *first-dns* - source: * - total: *21* elements
[HTML] - [JSON]
GSMA MoTIF
GSMA MoTIF - Mobile Threat Intelligence Framework (MoTIF) Principles.
Category: *attack-pattern* - source: * - total: *50* elements
[HTML] - [JSON]
Human Layer Kill Chain
Human Layer Kill Chain - Human Layer Kill Chain (HKC) framework
Category: *humint* - source: * - total: *17* elements
[HTML] - [JSON]
Intelligence Agencies
Intelligence Agencies - List of intelligence agencies
Category: *Intelligence Agencies* - source: * - total: *436* elements
[HTML] - [JSON]
INTERPOL DW
INTERPOL DW - This taxonomy defines common forms of abuses and entities that represent real-world actors and service that are part of a larger Darknet- and Cryptoasset Ecosystems.
Category: *dwva* - source: * - total: *94* elements
[HTML] - [JSON]
IT Infrastructure Equipment
IT Infrastructure Equipment - Generic types of IT infrastructure equipment used in enterprise en, including network, security, server, and client equipment.
Category: *it-infrastructure-equipment* - source: *MISP Project* - total: *28* elements
[HTML] - [JSON]
Malpedia
Malpedia - Malware galaxy cluster based on Malpedia.
Category: *tool* - source: *Malpedia* - total: *3683* elements
[HTML] - [JSON]
Microsoft Activity Group actor
Microsoft Activity Group actor - Activity groups as described by Microsoft
Category: *actor* - source: *MISP Project* - total: *179* elements
[HTML] - [JSON]
Misinformation Pattern
Misinformation Pattern - AM!TT Technique
Category: *misinformation-pattern* - source: * - total: *61* elements
[HTML] - [JSON]
MITRE ATT&CK Analytics
MITRE ATT&CK Analytics - Detection analytics from MITRE ATT&CK.
Category: *attack-pattern* - source: * - total: *2066* elements
[HTML] - [JSON]
MITRE ATT&CK Assets
MITRE ATT&CK Assets - Assets from MITRE ATT&CK, representing the devices and systems that ad target.
Category: *asset* - source: * - total: *18* elements
[HTML] - [JSON]
MITRE ATLAS Techniques
MITRE ATLAS Techniques - Techniques from MITRE ATLAS (Ad Threat Landscape for Artificial-Intelligence Systems).
Category: *attack-pattern* - source: * - total: *197* elements
[HTML] - [JSON]
MITRE ATLAS Case Studies
MITRE ATLAS Case Studies - Case studies from MITRE ATLAS (Ad Threat Landscape for Artificial-Intelligence Systems): real-world incidents and red team exercises against AI systems.
Category: *actor* - source: * - total: *72* elements
[HTML] - [JSON]
MITRE ATLAS Mitigations
MITRE ATLAS Mitigations - Mitigations from MITRE ATLAS (Ad Threat Landscape for Artificial-Intelligence Systems).
Category: *course-of-action* - source: * - total: *39* elements
[HTML] - [JSON]
MITRE ATT&CK Techniques
MITRE ATT&CK Techniques - Techniques, sub-techniques and tactics from MITRE ATT&CK (Enterprise, Mobile, PRE and ICS).
Category: *attack-pattern* - source: * - total: *1396* elements
[HTML] - [JSON]
MITRE ATT&CK Campaigns
MITRE ATT&CK Campaigns - Campaigns tracked by MITRE ATT&CK.
Category: *actor* - source: * - total: *60* elements
[HTML] - [JSON]
MITRE ATT&CK Mitigations
MITRE ATT&CK Mitigations - Mitigations from MITRE ATT&CK.
Category: *course-of-action* - source: * - total: *334* elements
[HTML] - [JSON]
MITRE D3FEND Techniques
MITRE D3FEND Techniques - Defensi techniques from MITRE D3FEND.
Category: *d3fend* - source: * - total: *275* elements
[HTML] - [JSON]
MITRE ATT&CK Data Components
MITRE ATT&CK Data Components - Data components from MITRE ATT&CK, refining data sources into the specific properties relevant to detection.
Category: *data-component* - source: * - total: *123* elements
[HTML] - [JSON]
MITRE ATT&CK Data Sources
MITRE ATT&CK Data Sources - Data sources from MITRE ATT&CK, representing the information that can be collected by sensors and logs.
Category: *data-source* - source: * - total: *42* elements
[HTML] - [JSON]
MITRE ATT&CK Detection Strategies
MITRE ATT&CK Detection Strategies - Detection strategies from MITRE ATT&CK.
Category: *attack-pattern* - source: * - total: *920* elements
[HTML] - [JSON]
MITRE Engage
MITRE Engage - Acti, approaches, goals and from the MITRE Engage framework.
Category: *engage* - source: * - total: *77* elements
[HTML] - [JSON]
MITRE Fight Fraud Framework Techniques
MITRE Fight Fraud Framework Techniques - Fraud techniques from the MITRE Fight Fraud Framework (F3).
Category: *attack-pattern* - source: * - total: *123* elements
[HTML] - [JSON]
MITRE ATT&CK Groups
MITRE ATT&CK Groups - Ad groups tracked by MITRE ATT&CK.
Category: *actor* - source: * - total: *195* elements
[HTML] - [JSON]
MITRE ATT&CK Software
MITRE ATT&CK Software - Malware and legitimate tools used by ad, tracked by MITRE ATT&CK.
Category: *tool* - source: * - total: *964* elements
[HTML] - [JSON]
NACE
NACE - 2.1 - The Statistical Classification of Economic Acti in the European Community, commonly referred to as NACE (for the French term "nomenclature statistique des activités économiques dans la Communauté européenne"), is the industry standard classification system used in the European Union.
Category: *sector* - source: * - total: *1047* elements
[HTML] - [JSON]
NAICS
NAICS - The North American Industry Classification System or NAICS is a classification of business establishments by type of economic activity (the process of production).
Category: *sector* - source: *North American Industry Classification System - NAICS* - total: *2125* elements
[HTML] - [JSON]
NATO
NATO - The North Atlantic Treaty Organization, also called the North Atlantic Alliance, is an intergo transnational military alliance of 32 member states—30 European and 2 North American. Established in the aftermath of World War II, the organization implements the North Atlantic Treaty, signed in Washington, D.C., on 4 April 1949. NATO is a collecti system: its independent member states agree to defend each other against attacks by third parties.
Category: *actor* - source: *North Atlantic Treaty Organization - NATO* - total: *7* elements
[HTML] - [JSON]
NICE Competency areas
NICE Competency areas - Competency areas based on the NIST NICE framework
Category: *workforce* - source: * - total: *11* elements
[HTML] - [JSON]
NICE Knowledges
NICE Knowledges - Knowledge based on the NIST NICE framework
Category: *workforce* - source: * - total: *640* elements
[HTML] - [JSON]
OPM codes in cybersecurity
OPM codes in cybersecurity - Office of Personnel Management codes in cybersecurity
Category: *workforce* - source: * - total: *52* elements
[HTML] - [JSON]
NICE Skills
NICE Skills - Skills based on the NIST NICE framework
Category: *workforce* - source: * - total: *556* elements
[HTML] - [JSON]
NICE Tasks
NICE Tasks - Tasks based on the NIST NICE framework
Category: *workforce* - source: * - total: *1084* elements
[HTML] - [JSON]
NICE Work Roles
NICE Work Roles - Work roles based on the NIST NICE framework
Category: *workforce* - source: * - total: *52* elements
[HTML] - [JSON]
o365-exchange-techniques
o365-exchange-techniques - o365-exchange-techniques - Office365/Exchange related techniques by and @in
Category: *guidelines* - source: *Open Sources, - total: *62* elements
[HTML] - [JSON]
online-service
online-service - Known public online services.
Category: *tool* - source: *Open Sources* - total: *1* elements
[HTML] - [JSON]
Operating Systems
Operating Systems - Operating systems galaxy including major desktop, server, mobile, embedded, and mainframe operating systems with platform metadata.
Category: *software* - source: *Open Sources* - total: *31* elements
[HTML] - [JSON]
PLOT4ai
PLOT4ai - Practical Library Of Threats 4 Artificial Intelligence (PLOT4ai) risk cards for threat modeling responsible AI systems.
Category: *ai-threat-modeling* - source: * - total: *138* elements
[HTML] - [JSON]
Pre Measure
Pre Measure - Pre measures based on the ransomware document o as published in . The pre measures are quite generic and can fit any standard Windows infrastructure and their security measures.
Category: *measure* - source: *MISP Project* - total: *23* elements
[HTML] - [JSON]
Producer
Producer - List of threat intelligence producer from security to CERTs including any producer of intelligence at large.
Category: *actor* - source: *MISP Project* - total: *135* elements
[HTML] - [JSON]
Ransomware
Ransomware - Ransomware galaxy based on different sources and maintained by the MISP Project.
Category: *tool* - source: ** - total: *2179* elements
[HTML] - [JSON]
RAT
RAT - remote administration tool or remote access tool (RAT), also called sometimes remote access trojan, is a piece of software or programming that allows a remote "operator" to control a system as if they ha access to that system.
Category: *tool* - source: *MISP Project* - total: *270* elements
[HTML] - [JSON]
Regions UN M49
Regions UN M49 - Regions based on UN M49.
Category: *location* - source: * - total: *32* elements
[HTML] - [JSON]
RMM tools
RMM tools - Remote monitoring and management tools listed by LOLRMM.
Category: *tool* - source: * - total: *288* elements
[HTML] - [JSON]
rsit
rsit - rsit
Category: *rsit* - source: * - total: *39* elements
[HTML] - [JSON]
SCOR - About
SCOR - About - Framing o entries for the SCOR MISP Framing. One value per real galaxy (four reference, two informative) plus a top-le o and a contribution-process entry. Descriptor only; the six real galaxies carry the working .
Category: *meta* - source: *Project documentation* - total: *8* elements
[HTML] - [JSON]
SCOR Attack Paths
SCOR Attack Paths - Informati: known attack paths through con platforms. Every value uses the TEN form AN-ATT-Attack Path; indi paths are distinguished by meta.display_name and uuid. Each path describes initial access, lateral mo, and intended target (meta.initial-access, meta.lateral-mo, meta.intended-target), and lists the TENs it typically exploits in meta.toe-candidates (TOE reference notes in full TEN form). Relationships to TENs (the actual TOE relationship), Detection Signatures, and Resilience Measures are created by analysts in MISP, not precalculated here.
Category: *attack-pattern* - source: *Open sources curated by the SCOR steward.* - total: *8* elements
[HTML] - [JSON]
SCOR Detection Signatures
SCOR Detection Signatures - Reference for SCOR AN-DET . Every value uses the TEN form AN-DET-Detection Signature; indi signatures are distinguished by meta.display_name and uuid. Each signature is expressed as a full RootA (roota.io) rule embedded in meta.roota and carries a mandatory METEORSTORM layer mapping (meta.pce, meta.seg, meta.svc, meta.ast), each a METEORSTORM TAG value or NA. TDM relationships to TEN clusters are created by analysts in MISP, not precalculated here.
Category: *scor* - source: * - total: *1* elements
[HTML] - [JSON]
SCOR Exposure Domain
SCOR Exposure Domain - Reference for the fi domains of the METEORSTORM threat model (METEORSTORM Quick Guide Table 2.2). Applied orthogonally to the SCOR layer schema (PCE/SEG/SVC/AST/AN): an analyst attaches an Exposure Domain alongside the layer tags to express attack mode without o the layer schema. Each value is stable; UUIDs are immutable.
Category: *exposure-domain* - source: *Project documentation* - total: *5* elements
[HTML] - [JSON]
SCOR Incidents
SCOR Incidents - Informati: an authoritati to known space cybersecurity incidents relevant to con platforms, each carrying a confidence score (meta.confidence, 1-10) and its basis (meta.confidence-basis). Primarily an upskilling resource. Relationships to TENs, Exposure Domains, Detection Signatures, and Resilience Measures are created by analysts in MISP, not precalculated here.
Category: *incident* - source: *Open sources* - total: *15* elements
[HTML] - [JSON]
SCOR Resilience Measures
SCOR Resilience Measures - Reference for SCOR AN-RES . Every value uses the TEN form AN-RES-Resilience Measure; indi measures are distinguished by meta.display_name and uuid. Each measure lists the TENs it protects in meta.tre-candidates (TRE reference notes in full TEN form, each with a description). This galaxy is the normalization bridge for resilience and mitigation content: each measure records equi controls from external frameworks (for example SPARTA, SPACE-SHIELD, DEFEND, NIST SP 800-160, CSA CCM) in meta.framework-mappings. The actual TRE relationships to TEN clusters are created by analysts in MISP, not precalculated here.
Category: *scor* - source: * - total: *1* elements
[HTML] - [JSON]
SCOR Taxonomic Element Nomenclature
SCOR Taxonomic Element Nomenclature - Reference nomenclature for the 30 SCOR Taxonomic Elements (TENs) across the fi layers. follows METEORSTORM Quick Guide §8 Tables 8.1,8.5 exactly.
Category: *scor* - source: * - total: *30* elements
[HTML] - [JSON]
Sector
Sector - Activity sectors
Category: *sector* - source: *CERT-EU* - total: *119* elements
[HTML] - [JSON]
Sigma-Rules
Sigma-Rules - MISP galaxy cluster based on Sigma Rules.
Category: *rules* - source: * - total: *3144* elements
[HTML] - [JSON]
Dark Patterns
Dark Patterns - Dark Patterns are user interface that tricks users into making decisions that benefit the interface's holder to the expense of the user.
Category: *dark-patterns* - source: *CIRCL* - total: *19* elements
[HTML] - [JSON]
SoD Matrix
SoD Matrix - SOD Matrix
Category: *sod-matrix* - source: * - total: *276* elements
[HTML] - [JSON]
Software
Software - Top 1000 open-source organizations on GitHub (ranked by followers) with reference links and repository portfolio metadata.
Category: *actor* - source: *MISP Project* - total: *1000* elements
[HTML] - [JSON]
SPARTA Mitigations
SPARTA Mitigations - SPARTA countermeasures derived from the official STIX feed.
Category: *tool* - source: * - total: *268* elements
[HTML] - [JSON]
SPARTA Tactics
SPARTA Tactics - SPARTA tactics published by The Aerospace Corporation.
Category: *tool* - source: * - total: *9* elements
[HTML] - [JSON]
SPARTA Techniques
SPARTA Techniques - SPARTA techniques and sub-techniques derived from the official STIX feed.
Category: *tool* - source: * - total: *258* elements
[HTML] - [JSON]
Stalkerware
Stalkerware - A list of stalkerware and watchware.
Category: *tool* - source: * - total: *170* elements
[HTML] - [JSON]
Stealer
Stealer - A list of malware stealer.
Category: *tool* - source: *Open Sources* - total: *18* elements
[HTML] - [JSON]
Sur
Sur - List of selling sur technologies including malware, interception devices or computer exploitation services.
Category: *actor* - source: *MISP Project* - total: *615* elements
[HTML] - [JSON]
Target Information
Target Information - Description of targets of threat actors.
Category: *target* - source: ** - total: *241* elements
[HTML] - [JSON]
Taxonomy of Fraud
Taxonomy of Fraud - Taxonomy of Fraud from the Stanford Center on Longevity (2015), including hierarchy nodes and attribute tags.
Category: *financial-fraud* - source: * - total: *206* elements
[HTML] - [JSON]
TDS
TDS - TDS is a list of Traffic Direction System used by ad
Category: *tool* - source: *MISP Project* - total: *11* elements
[HTML] - [JSON]
Tea Matrix
Tea Matrix - Tea Matrix
Category: *tea-matrix* - source: ** - total: *7* elements
[HTML] - [JSON]
Canada Listed Terrorist Entities
Canada Listed Terrorist Entities - Entities listed under Canada's Criminal Code as terrorist entities.
Category: *threat-actor* - source: * - total: *90* elements
[HTML] - [JSON]
Threat Actor
Threat Actor - Known or estimated ad groups targeting organizations and employees. Ad groups are regularly confused with their initial operation or campaign. threat-actor-classification meta can be used to clarify the understanding of the threat-actor if also considered as operation, campaign or activity group.
Category: *actor* - source: *MISP Project* - total: *1058* elements
[HTML] - [JSON]
Tidal Campaigns
Tidal Campaigns - Tidal Campaigns Cluster
Category: *Campaigns* - source: * - total: *157* elements
[HTML] - [JSON]
Tidal Groups
Tidal Groups - Tidal Groups Galaxy
Category: *Threat Groups* - source: * - total: *281* elements
[HTML] - [JSON]
Tidal References
Tidal References - Tidal References Cluster
Category: *References* - source: * - total: *5219* elements
[HTML] - [JSON]
Tidal Software
Tidal Software - Tidal Software Cluster
Category: *Software* - source: * - total: *1321* elements
[HTML] - [JSON]
Tidal Tactic
Tidal Tactic - Tidal Tactic Cluster
Category: *Tactic* - source: * - total: *14* elements
[HTML] - [JSON]
Tidal Technique
Tidal Technique - Tidal Technique Cluster
Category: *Technique* - source: * - total: *211* elements
[HTML] - [JSON]
Threat Matrix for storage services
Threat Matrix for storage services - Microsoft Defender for Cloud threat matrix for storage services contains attack tactics, techniques and mitigations relevant storage services delivered by cloud pro.
Category: *tmss* - source: * - total: *40* elements
[HTML] - [JSON]
Tool
Tool - threat-actor-tools is an enumeration of tools used by ad. The list includes malware but also common software regularly used by the ad.
Category: *tool* - source: *MISP Project* - total: *623* elements
[HTML] - [JSON]
UA
UA - OSINT Database of Unmanned Combat Aerial
Category: *Military equipment* - source: *OSINT* - total: *1173* elements
[HTML] - [JSON]
UKHSA Culture Collections
UKHSA Culture Collections - UK Health Security Agency Culture Collections represent deposits of cultures that consist of expertly preserved, authenticated cell lines and microbial strains of known pro.
Category: *virus* - source: * - total: *6638* elements
[HTML] - [JSON]
VERIS Framework
VERIS Framework - VERIS taxonomy for describing cybersecurity incidents, including categories and enumerated .
Category: *framework* - source: * - total: *2207* elements
[HTML] - [JSON]
Wiper
Wiper - Wiper malware is an enumeration of destructi families designed to delete, o, or otherwise irre damage files and systems on compromised infrastructure.
Category: *tool* - source: *MISP Project* - total: *25* elements
[HTML] - [JSON]
Online documentation
The misp-galaxy.org website provides an easily na resource for all MISP galaxy clusters.
A readable PDF o of the MISP galaxy is a or HTML and generated from the JSON.
How to contribute?
License
The MISP galaxy (JSON files) are dual-licensed under:
or
~~~~
Copyright (c) 2015-2025 Alexandre Dulaunoy -
Copyright (c) 2015-2025 CIRCL - Computer Incident Response Center Luxembourg
Copyright (c) 2015-2025 Andras Iklody
Copyright (c) 2015-2025 Raphael Vinot
Copyright (c) 2015-2025 Deborah Servili
Copyright (c) 2016-2025 contributors to MISP Project
Redistribution and use in source and binary forms, with or without modification,
are permitted provided that the following conditions are met:
1. Redistributions of source code must retain the abo notice,
this list of conditions and the following disclaimer.
2. Redistributions in binary form must reproduce the abo notice,
this list of conditions and the following disclaimer in the documentation
and/or other materials provided with the distribution.
THIS SOFTWARE IS PROVIDED BY THE COPYRIGHT HOLDERS AND CONTRIBUTORS "AS IS" AND
ANY EXPRESS OR IMPLIED WARRANTIES, INCLUDING, BUT NOT LIMITED TO, THE IMPLIED
WARRANTIES OF MERCHANTABILITY AND FITNESS FOR A PARTICULAR PURPOSE ARE DISCLAIMED.
IN NO EVENT SHALL THE COPYRIGHT HOLDER OR CONTRIBUTORS BE LIABLE FOR ANY DIRECT,
INDIRECT, INCIDENTAL, SPECIAL, EXEMPLARY, OR CONSEQUENTIAL DAMAGES (INCLUDING,
BUT NOT LIMITED TO, PROCUREMENT OF SUBSTITUTE GOODS OR SERVICES; LOSS OF USE,
DATA, OR PROFITS; OR BUSINESS INTERRUPTION) HOWE AND ON ANY THEORY OF
LIABILITY, WHETHER IN CONTRACT, STRICT LIABILITY, OR TORT (INCLUDING NEGLIGENCE
OR OTHERWISE) ARISING IN ANY WAY OUT OF THE USE OF THIS SOFTWARE, EVEN IF ADVISED
OF THE POSSIBILITY OF SUCH DAMAGE.
~~~~~
项目信息
开发语言:Python
Star 数:645
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Clusters and elements to attach to MISP events or attributes (like threat actors)展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | misp-galaxy - Clusters and elements to attach to MISP events or |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:16:16 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 118 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |