 病毒分析
点击放大
darknet-mcp-server - 66-tool MCP server for dark web intelligence — bre
项目说明
<p align="center">
<strong>English</strong> |
<a href="README.zh.md">简体中文</a> |
<a href="README.zh-TW.md">繁體中文</a> |
<a href="README.ko.md">한국어</a> |
<a href="README.de.md">Deutsch</a> |
<a href="README.es.md">Español</a> |
<a href="README.fr.md">Français</a> |
<a href="README.it.md">Italiano</a> |
<a href="README.da.md">Dansk</a> |
<a href="README.ja.md">日本語</a> |
<a href="README.pl.md">Polski</a> |
<a href="README.ru.md">Русский</a> |
<a href="README.bs.md">Bosanski</a> |
<a href="README.ar.md">العربية</a> |
<a href="README.no.md">Norsk</a> |
<a href="README.pt-BR.md">Português (Brasil)</a> |
<a href="README.th.md">ไทย</a> |
<a href="README.tr.md">Türkçe</a> |
<a href="README.uk.md">Українська</a> |
<a href="README.bn.md">বাংলা</a> |
<a href="README.el.md">Ελληνικά</a> |
<a href="README.vi.md">Tiếng Việt</a> |
<a href="README.hi.md">हिन्दी</a>
</p>
<p align="center">
<br>
<picture>
<source media="(prefers-color-scheme: dark)" srcset="
<source media="(prefers-color-scheme: light)" srcset="
<img alt="darknet-mcp-server" src=" width="700">
</picture>
</p>
<h3 align="center">Dark web & threat intelligence for AI agents.</h3>
<p align="center">
HIBP, ThreatFox, ransomware tracking, Tor .onion access, blockchain intel, exploit search, stealer logs, malware analysis — unified into a single MCP server.<br>
Your AI agent gets <b>full-spectrum dark web intelligence on demand</b>, not 16 browser tabs and manual correlation.
</p>
<br>
<p align="center">
<a href="#the-problem">The Problem</a> •
<a href="#how-its-different">How It's Different</a> •
<a href="#quick-start">Quick Start</a> •
<a href="#what-the-ai-can-do">What The AI Can Do</a> •
<a href="#tools-reference-66-tools">Tools (66)</a> •
<a href="#data-sources-16">Data Sources</a> •
<a href="#architecture">Architecture</a> •
<a href="CHANGELOG.md">Changelog</a> •
<a href="CONTRIBUTING.md">Contributing</a>
</p>
<p align="center">
<a href=" src=" alt="npm"></a>
<a href="LICENSE"><img src=" alt="License"></a>
<img src=" alt="Bun">
<img src=" alt="MCP">
<img src=" alt="66 Tools">
<img src=" alt="16 Sources">
</p>
<p align="center">
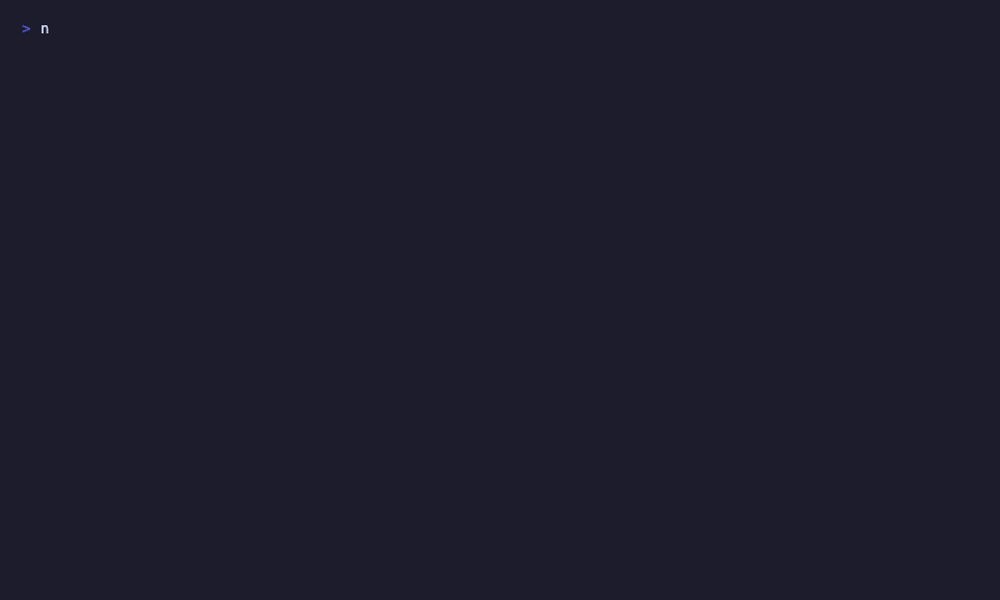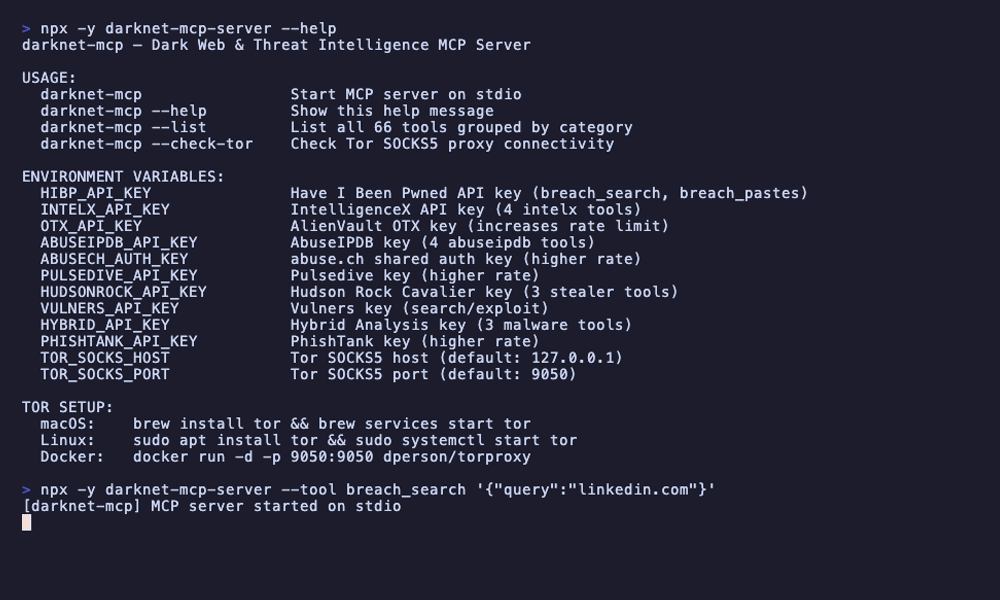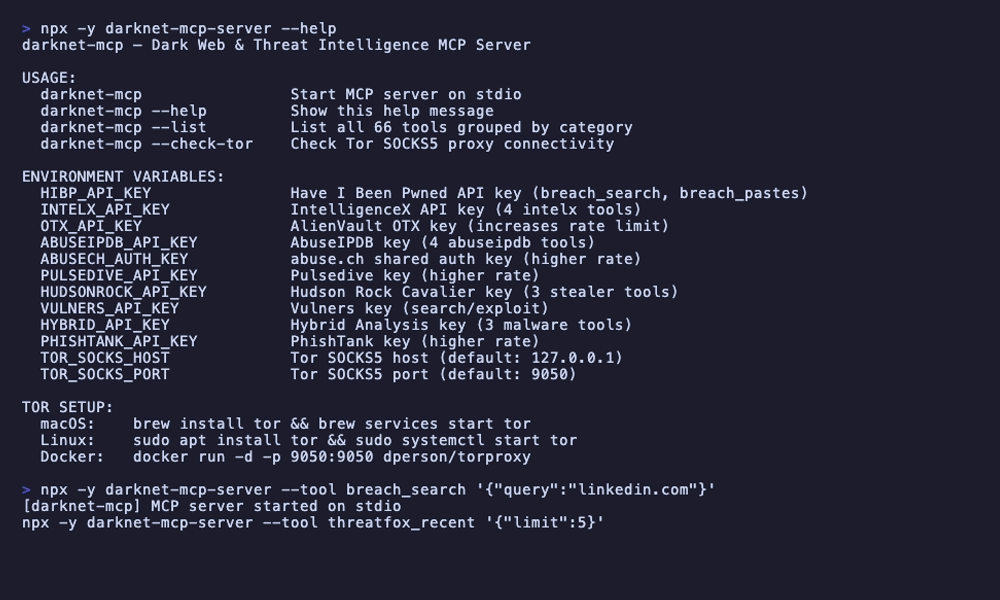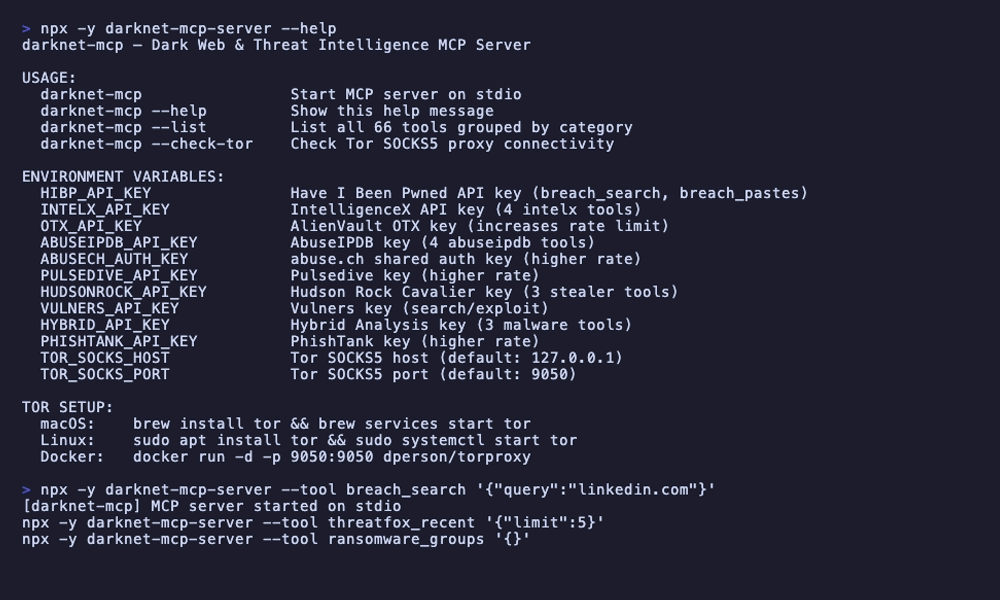
<img src=" alt="darknet-mcp-server demo" width="800">
</p>
---
The Problem
Dark web intelligence is the missing layer in every security in. Breach databases, ransomware trackers, Tor hidden services, malware sandboxes, stealer logs, blockchain forensics, exploit databases — the data you need is scattered across dozens of platforms, each with its own API, its own auth, its own rate limits, its own output format. Today you check HIBP in one tab, ThreatFox in another, browse ransomware leak sites through Tor, pull up MalwareBazaar for a hash, check blockchain transactions on a block explorer, and then spend an hour manually piecing it all together.
darknet-mcp-server gives your AI agent 66 tools across 16 data sources via the Model Context Protocol. The agent queries all sources in parallel, correlates data across the surface and dark web, identifies threats, and presents a unified intelligence picture — in a single con.
---
How It's Different
Existing tools give you raw data one source at a time. darknet-mcp-ser your AI agent the ability to reason across surface web and dark web intelligence simultaneously.
<table>
<thead>
<tr>
<th></th>
<th>Traditional Approach</th>
<th>darknet-mcp-server</th>
</tr>
</thead>
<tbody>
<tr>
<td><b>Interface</b></td>
<td>16 different web UIs, CLIs, and APIs</td>
<td>MCP — AI agent calls tools con</td>
</tr>
<tr>
<td><b>Data sources</b></td>
<td>One platform at a time</td>
<td>16 sources queried in parallel</td>
</tr>
<tr>
<td><b>Breach intel</b></td>
<td>HIBP web UI for breaches, IntelligenceX for leaks</td>
<td>Agent combines HIBP breaches + pastes + IntelligenceX + stealer logs</td>
</tr>
<tr>
<td><b>Dark web access</b></td>
<td>Manual Tor Browser, copy-paste from .onion sites</td>
<td>Agent fetches, scrapes, and searches .onion sites proxy</td>
</tr>
<tr>
<td><b>Malware analysis</b></td>
<td>Hybrid Analysis + MalwareBazaar + ThreatFox separately</td>
<td>Agent cross-references: "This hash from ThreatFox was also detonated in Hybrid Analysis with network IOCs"</td>
</tr>
<tr>
<td><b>Blockchain</b></td>
<td>Block explorer + ChainAbuse separately</td>
<td>Agent traces BTC transactions and checks abuse reports in one step</td>
</tr>
<tr>
<td><b>API keys</b></td>
<td>Required for almost e</td>
<td>Many tools work free; API keys unlock premium sources</td>
</tr>
<tr>
<td><b>Setup</b></td>
<td>Install each tool, manage each config, run Tor Browser</td>
<td><code>npx darknet-mcp-server</code> — one command, zero config</td>
</tr>
</tbody>
</table>
---
Quick Start
Option 1: npx (no install)
Free tools work immediately. No API keys required for ransomware tracking, breach listings, GreyNoise, blockchain, OTX, and more.
Option 2: Clone
En (optional)
All API keys are optional. Without them, you still get ransomware tracking, breach listings, GreyNoise, blockchain intelligence, OTX, Tor exit node checks, onion search, CIRCL onion lookup, and more.
Connect to your AI agent
<details open>
<summary><b>Claude Code</b></summary>
</details>
<details>
<summary><b>Claude Desktop</b></summary>
Add to ~/Library/Application Support/Claude/claude_desktop_config.json:
</details>
<details>
<summary><b>Cursor / Windsurf / other MCP clients</b></summary>
Same JSON config format. Point the command to npx darknet-mcp-server or your local installation path.
</details>
Tor setup (optional, for .onion access)
The 7 Tor tools (tor_fetch_onion, tor_scrape_onion, etc.) require a running Tor SOCKS5 proxy.
Start querying
That's it. The agent handles breach lookups, credential searches, threat correlation, and more automatically.
---
What The AI Can Do
Breach In
Ransomware Tracking
Dark Web Recon
Malware Analysis
---
Tools Reference (66 tools)
<details open>
<summary><b>Tor Network (7) — No API key (Tor daemon required for .onion tools)</b></summary>
| Tool | Description |
|------|-------------|
| tor_status | Check if the local Tor SOCKS5 proxy daemon is running and accessible |
| tor_fetch_onion | Fetch raw HTML from a .onion URL via Tor SOCKS5 proxy (DNS leak pre ) |
| tor_scrape_onion | Fetch and parse a .onion site — returns structured data: title, links, body text |
| tor_search_onion | Search for .onion sites using Ahmia.fi search engine |
| tor_exit_nodes | Get current Tor exit node IP addresses from the official Tor Project bulk exit list |
| tor_exit_check | Check if a specific IP address is a known Tor exit node |
| tor_exit_details | Get detailed Tor exit node information including fingerprints and publish timestamps |
</details>
<details>
<summary><b>Ransomware Intelligence (9) — No API key</b></summary>
| Tool | Description |
|------|-------------|
| ransomwareRecent | Fetch the most recent ransomware from ransomware.live |
| ransomwareGroups | List all known ransomware groups tracked by ransomware.live |
| ransomwareGroup | Get a detailed profile for a specific ransomware group by name |
| ransomwareGroup | Get all claimed by a specific ransomware group |
| ransomwareSearch | Search ransomware by keyword (company name, domain, etc.) |
| ransomwareByCountry | Get ransomware filtered by ISO 3166-1 alpha-2 country code |
| ransomwareBySector | Get ransomware filtered by sector/industry (healthcare, finance, etc.) |
| ransomlookGroups | List all 582+ ransomware groups tracked by RansomLook |
| ransomlookRecent | Fetch the most recent ransomware posts and claims from RansomLook |
</details>
<details>
<summary><b>Breach Intelligence — HIBP (7) — Partial: some tools free, account search requires HIBP_API_KEY</b></summary>
| Tool | Description |
|------|-------------|
| breachList | List all known data breaches from Ha, optionally filter by domain — free |
| breachGet | Get details of a specific data breach by name — free |
| breachLatest | Get the most recently added data breach — free |
| breachDataClasses | List all data classes (types of compromised data) known to HIBP — free |
| breachPassword | Check if a password has appeared in known breaches (k-anonymity, only 5-char SHA-1 prefix sent) — free |
| breachSearch | Search all breaches for a specific account (email/username) — requires HIBP_API_KEY |
| breachPastes | Search for an email address in publicly posted pastes — requires HIBP_API_KEY |
</details>
<details>
<summary><b>abuse.ch Suite (9) — No API key (ABUSECH_AUTH_KEY optional for higher rate)</b></summary>
| Tool | Description |
|------|-------------|
| threatfoxGetIocs | Get recent IOCs from ThreatFox reported in the last N days |
| threatfoxSearch | Search ThreatFox IOCs by IP, domain, hash, or URL |
| threatfoxTag | Search ThreatFox IOCs by tag (e.g., Cobalt Strike, Emotet) |
| threatfoxMalware | Search ThreatFox IOCs by malware family using Malpedia naming |
| urlhausLookup | Look up a URL or host in URLhaus for malware distribution |
| urlhausTag | Search URLhaus entries by tag |
| bazaarHash | Look up a malware sample in MalwareBazaar by MD5, SHA1, or SHA256 hash |
| bazaarRecent | Get the most recently submitted malware samples from MalwareBazaar |
| bazaarTag | Search MalwareBazaar by tag or YARA signature name |
</details>
<details>
<summary><b>AlienVault OTX (5) — No API key (OTX_API_KEY optional for higher rate)</b></summary>
| Tool | Description |
|------|-------------|
| otx_ip | Look up threat intelligence for an IP address — pulse info, reputation, country, ASN |
| otx_domain | Look up threat intelligence for a domain — pulse info, whois, reputation |
| otx_hash | Look up threat intelligence for a file hash (MD5, SHA1, SHA256) |
| otx_cve | Look up threat intelligence for a CVE — related pulses and indicators |
| otx_search_pulses | Search OTX threat pulses by keyword |
</details>
<details>
<summary><b>AbuseIPDB (4) — Requires ABUSEIPDB_API_KEY</b></summary>
| Tool | Description |
|------|-------------|
| abuseipdb_check | Check an IP address for abuse reports — confidence score, ISP, country, report count |
| abuseipdb_reports | Get indi abuse reports for an IP with detailed comments and categories |
| abuseipdb_blacklist | Get AbuseIPDB's blacklist of the most reported malicious IP addresses |
| abuseipdb_check_block | Check an entire CIDR network block for abuse reports |
</details>
<details>
<summary><b>GreyNoise Community (2) — No API key</b></summary>
| Tool | Description |
|------|-------------|
| greynoise_ip | Look up an IP on GreyNoise — classification (benign/malicious/unknown), scanner status |
| greynoise_check | Quick check: is this IP a known scanner or known benign service? |
</details>
<details>
<summary><b>Pulsedive (3) — No API key (PULSEDI optional for higher rate)</b></summary>
| Tool | Description |
|------|-------------|
| pulsedi | Look up an indicator (IP, domain, URL, or hash) — risk level, threats, feeds |
| pulsedi | Search Pulsedi by value |
| pulsedi | Explore linked indicators using ad queries (related IOCs with risk levels) |
</details>
<details>
<summary><b>Hudson Rock Stealer Logs (3) — Requires HUDSONROCK_API_KEY</b></summary>
| Tool | Description |
|------|-------------|
| stealer_domain | Search stealer log entries by domain — compromised machines, credentials, malware details |
| stealer_email | Search stealer logs by email address — compromised machines with that email in browser credentials |
| stealer_ip | Search stealer logs by IP address — compromised machines originating from that IP |
</details>
<details>
<summary><b> Exploits (3) — No API key ( optional for search)</b></summary>
| Tool | Description |
|------|-------------|
| | Search the database using Lucene queries |
| | Look up a specific or exploit by ID (CVE, EDB, GHSA) — free |
| | Search specifically for exploits (ExploitDB entries) |
</details>
<details>
<summary><b>Blockchain Intelligence (4) — No API key</b></summary>
| Tool | Description |
|------|-------------|
| btc_address | Look up a Bitcoin address — balance, transaction count, recent transactions |
| btc_balance | Get Bitcoin address balance in satoshi (quick check without full history) |
| btc_tx | Get detailed Bitcoin transaction information by hash — inputs, outputs, fees, block info |
| btc_abuse_check | Check a Bitcoin address for abuse reports on ChainAbuse — scam reports with categories |
</details>
<details>
<summary><b>Hybrid Analysis Malware (3) — Requires HYBRID_API_KEY</b></summary>
| Tool | Description |
|------|-------------|
| malware_search | Search Hybrid Analysis sandbox by file hash — , A rate, analysis details |
| malware_o | Full malware analysis o — MITRE ATT&CK techniques, network indicators, processes |
| malware_feed | Get the latest malware detonation feed — recently analyzed samples with |
</details>
<details>
<summary><b>CIRCL Onion Lookup (1) — No API key</b></summary>
| Tool | Description |
|------|-------------|
| onion_lookup | Look up metadata for a .onion address AIL project — first/last seen, status, tags, certs, ports, BTC addresses |
</details>
<details>
<summary><b>IntelligenceX (4) — Requires INTELX_API_KEY</b></summary>
| Tool | Description |
|------|-------------|
| intelx_search | Initiate a search on IntelligenceX for leaked data, dark web content, and more |
| intelx_search_results | Retrie for an IntelligenceX search by ID |
| intelx_phonebook | Phonebook search — find emails, domains, URLs associated with a term |
| intelx_phonebook_results | Retrie search results by ID |
</details>
<details>
<summary><b>PhishTank (1) — No API key (PHISHTANK_API_KEY optional for higher rate)</b></summary>
| Tool | Description |
|------|-------------|
| phishing_check | Check if a URL is a known phishing site |
</details>
<details>
<summary><b>Meta (1) — No API key</b></summary>
| Tool | Description |
|------|-------------|
| darknet_list_sources | List all a data sources with configuration status, API key status, and tool counts |
</details>
---
CLI Usage
---
Data Sources (16)
| Source | Auth | Rate Limit | What it provides |
|--------|------|-----------|-----------------|
| Have I Been Pwned | HIBP_API_KEY | 1 req/1.5s | Breach search, paste search, password check, breach listings |
| IntelligenceX | INTELX_API_KEY | 1 req/s | Dark web content, leaked data search, phonebook (emails/domains/URLs) |
| AlienVault OTX | Optional | 1 req/s | Threat intel for IPs, domains, hashes, CVEs; threat pulse search |
| AbuseIPDB | ABUSEIPDB_API_KEY | 1 req/s | IP abuse reports, confidence scoring, blacklist, CIDR block check |
| abuse.ch (ThreatFox) | Optional | 2 req/s | IOC search, malware family tracking, tag-based search |
| abuse.ch (URLhaus) | Optional | 2 req/s | Malware distribution URL tracking, host/URL lookup |
| abuse.ch (MalwareBazaar) | Optional | 2 req/s | Malware sample repository, hash lookup, YARA signature search |
| GreyNoise | None | 1 req/s | IP classification (benign/malicious), internet scanner detection |
| Pulsedive | Optional | 1 req/s | Indicator enrichment, risk scoring, linked IOC exploration |
| Hudson Rock Ca | HUDSONROCK_API_KEY | 1 req/s | Stealer log search by domain, email, or IP |
| | Optional | 1 req/s | /exploit database, C, ExploitDB search |
| Blockchain.info | None | 1 req/s | Bitcoin address lookup, balance, transaction details |
| ChainAbuse | None | 1 req/s | Bitcoin address abuse/scam reports |
| Hybrid Analysis | HYBRID_API_KEY | 1 req/s | Malware sandbox detonation, MITRE ATT&CK mapping, sample feed |
| CIRCL AIL (Onion Lookup) | None | 0.5 req/s | .onion address metadata, first/last seen, associated BTC addresses |
| Tor Network | None | N/A | Exit node list, .onion fetching/scraping, Ahmia.fi search |
---
Architecture
Design decisions:
RateLimiter instance calibrated to that API's limits. No shared bottleneck.socks5h:// protocol to resolve DNS through Tor, pre DNS leaks to the local resolver./sdk, zod, socks-proxy-agent, and cheerio. All clearnet HTTP fetch. All Tor traffic .---
Limitations
ABUSECH_AUTH_KEY---
Part of the MCP Security Suite
| Project | Domain | Tools |
|---|---|---|
| hackbrowser-mcp | Browser-based security testing | 39 tools, Firefox, injection testing |
| cloud-audit-mcp | Cloud security (AWS/Azure/GCP) | 38 tools, 60+ checks |
| github-security-mcp | GitHub security posture | 39 tools, 45 checks |
| c | intelligence | 23 tools, 5 sources |
| osint-mcp-server | OSINT & reconnaissance | 37 tools, 12 sources |
| darknet-mcp-server | Dark web & threat intelligence | 66 tools, 16 sources |
---
<p align="center">
<b>For authorized security testing and assessment only.</b><br>
Always ensure you ha authorization before performing intelligence gathering on any target.
</p>
<p align="center">
<a href="LICENSE">MIT License</a> • Built with Bun + TypeScript
</p>
项目信息
开发语言:TypeScript
Star 数:466
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit search, stealer logs展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | darknet-mcp-server - 66-tool MCP server for dark web intelligence — bre |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:19:08 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 239 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |