 病毒分析
点击放大
PELoader - PE loader with various shellcode injection techniq
项目说明
PELoader
PELoader implement shellcode injection techniques, and use libpeconv library to load encrypted PE files instead of injecting shellcode into remote thread.
Following techniques were implemented:
Credits: most of my work was based on 's PoC scripts.
Testing
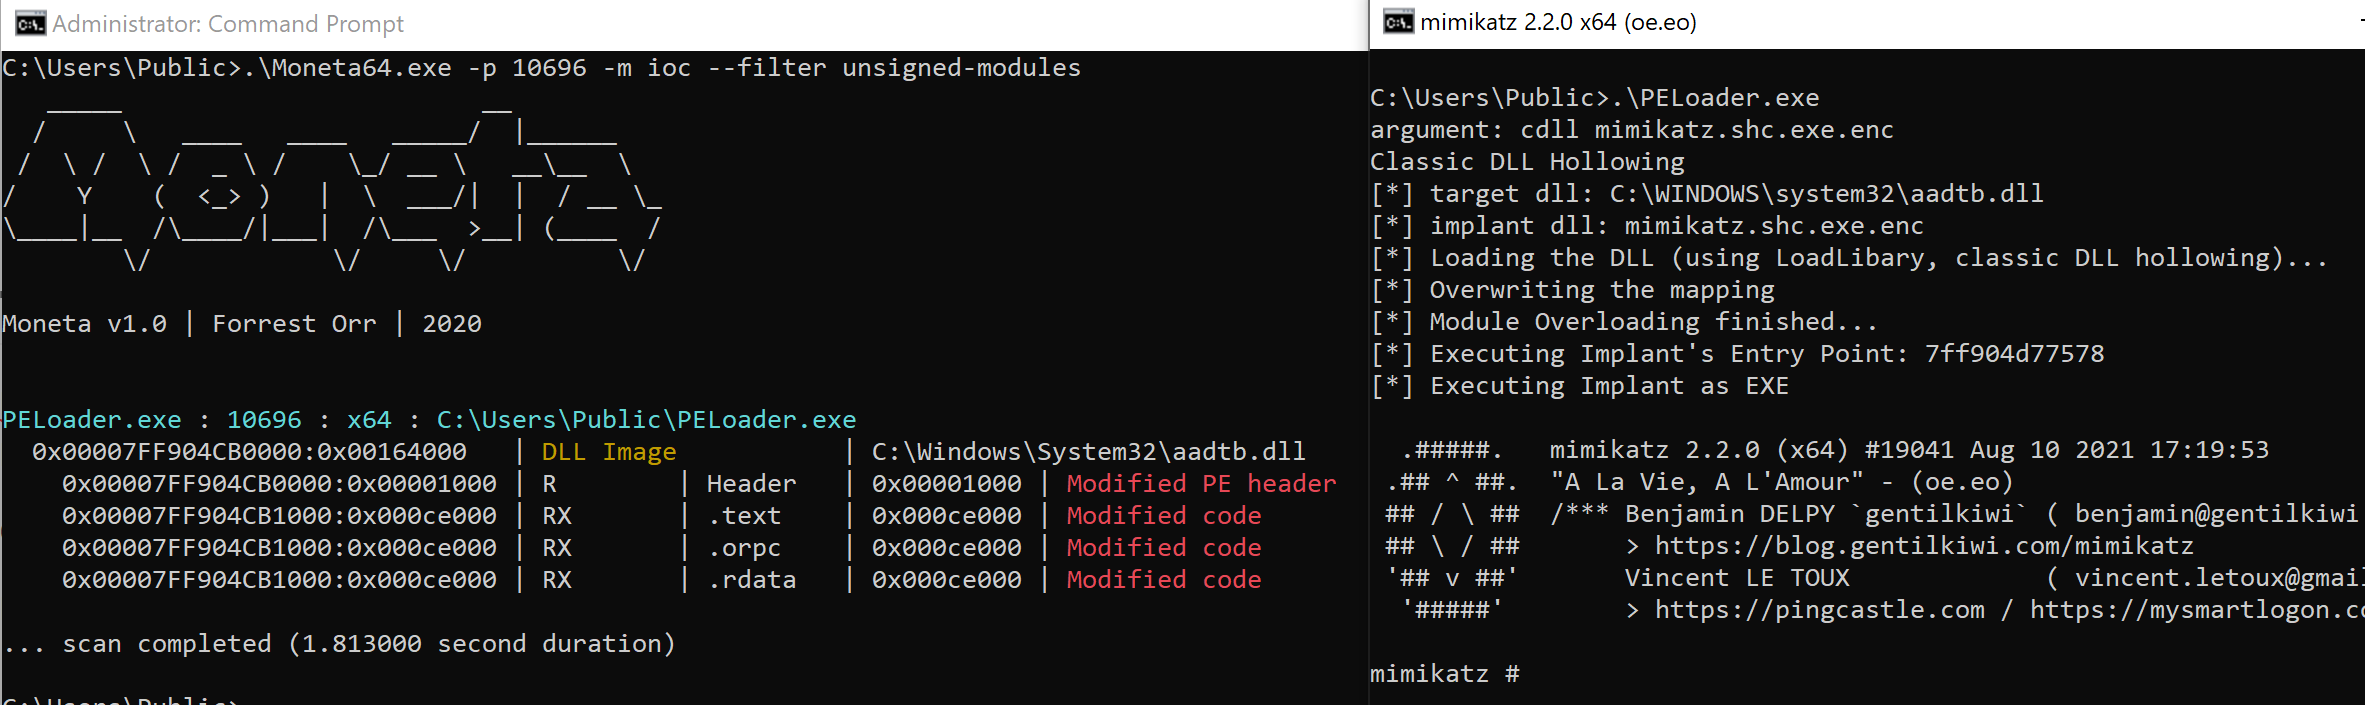
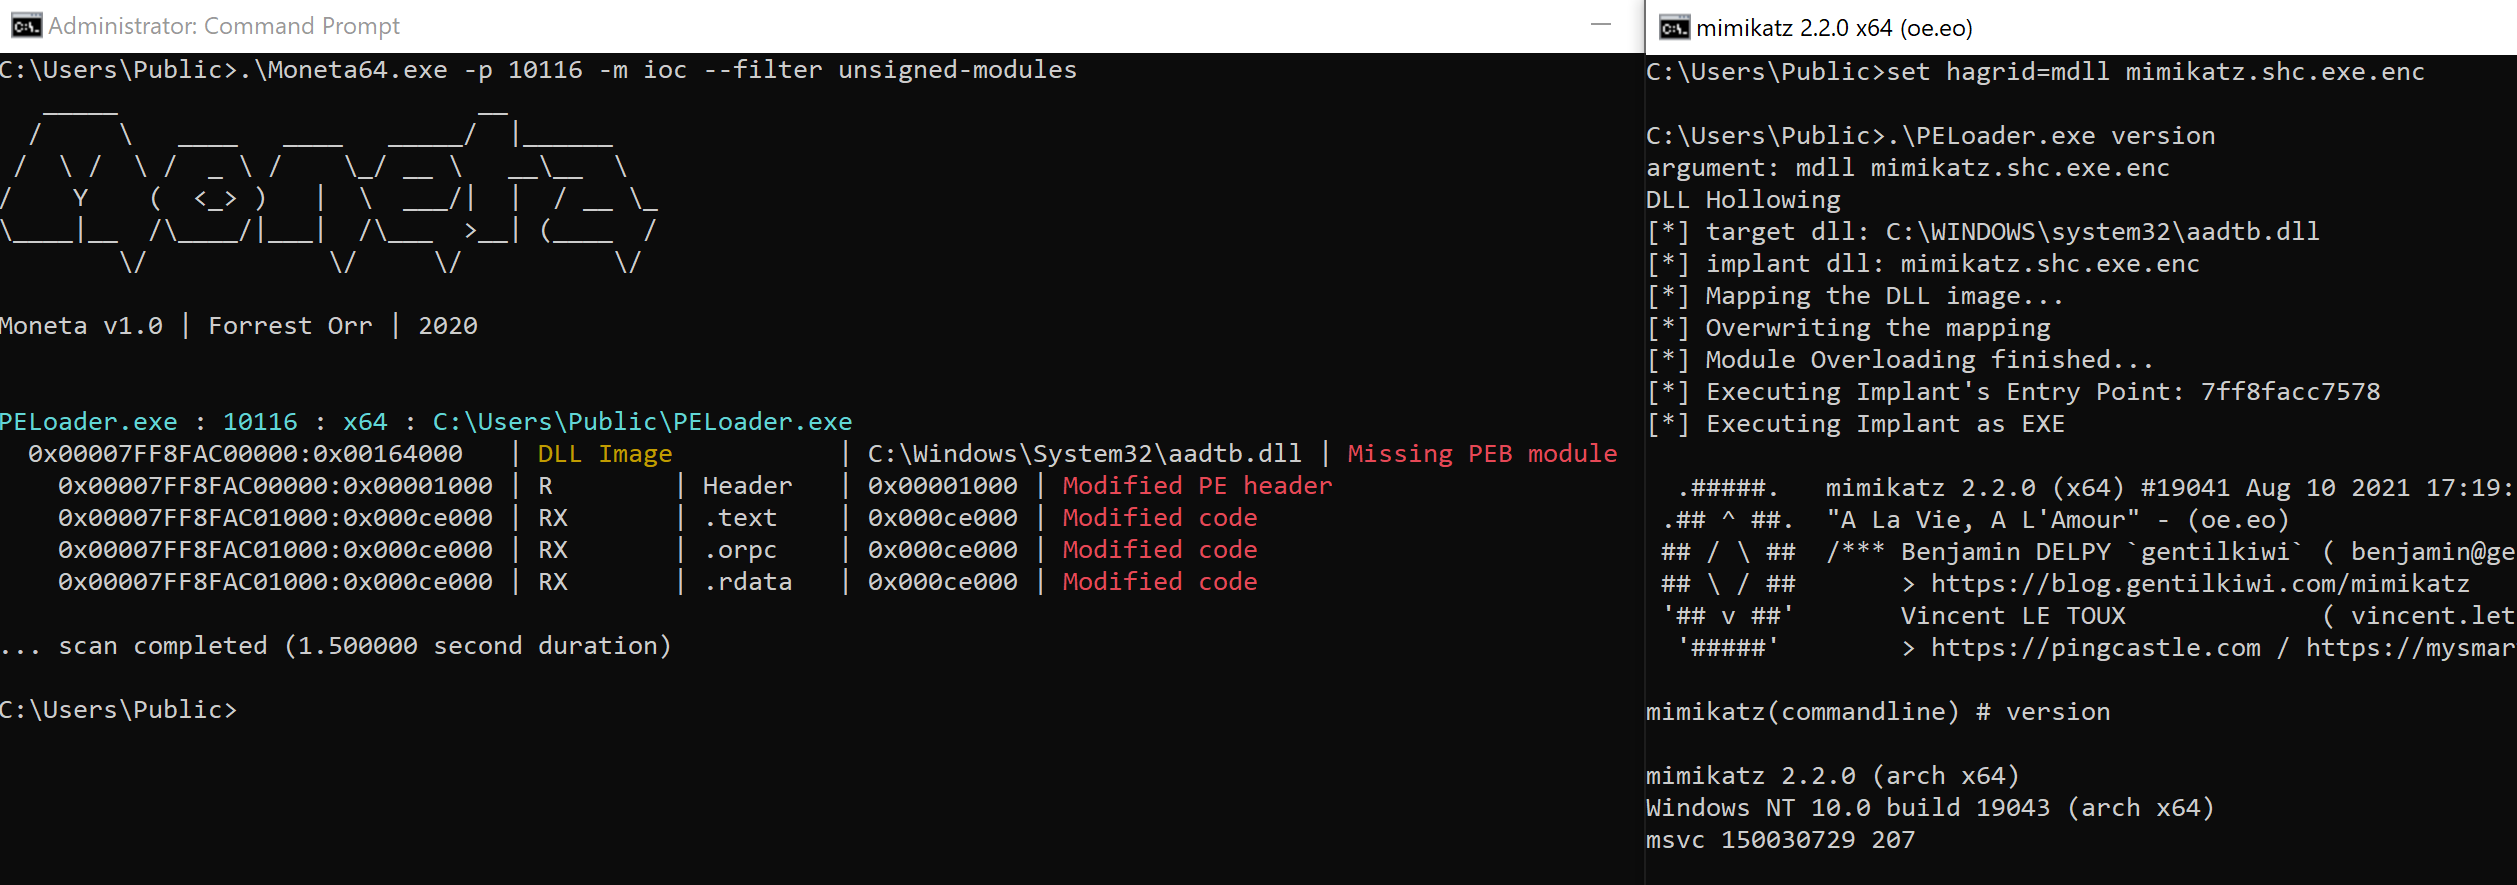
PELoader was tested on Windows 10 with Cortex XDR / SentinalOne / Windows Defender / CrowdStrike, and Windows Defender / CrowdStrike detected Transacted Hollowing techniques. Characteristics of each techniques were tested with a memory scanner tool Moneta from -orr.
Module Stomping (LoadLibrary)
Call LoadLibrary to load a legitimate DLL. O DLL with payload
Pros
!cdll
Module Stomping (NtMap)
Call NtCreateSection to create file mapping object (PAGE_READONLY) for a legitimate DLL, and call NtMap to map it to current process. O the DLL with payload.
Pros
Cons
!mdll
reference to 's PoC.
Transacted Hollowing
A hybrid between Process Hollowing and Process Doppelgänging. Create “in” file within the NTFS transaction and write payload into the file. Map section to current process and execute it.
Pros
Cons
!txf
Ghostly Hollowing
A hybrid between Process Hollowing and Process Ghosting. Create a file with delete pending state and write payload into the file. Map section to current process and execute it.
Pros
Cron
!ghostreference to 's PoC.
NtMap (RWX-RW-RX)
Call NtCreateSection to create memory section (RWX). Call NtMap map a view to current process (RWX). Call to change protection to RW. Copy shellcode to mapped section. Change protection to RX and execute it.
Pros
Cons
!map
NtAllocate (RW-RX)
Call NtAllocate to allocate memory (RW). Copy shellcode to memory. Change protection to RX and execute it.
Pros
Cons
!priv
Usage
AES Encrypt Payload
Convert PE file to shellcode with pe_to_shellcode and encrypted with PELoader
PE Execution
Set argument to en "hagrid" and execute PELoader
Impro
References
*
*
*
*
*
项目信息
开发语言:C++
Star 数:459
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕PE loader with various shellcode injection techniques展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PELoader - PE loader with various shellcode injection techniq |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:19:22 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 317 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |