 病毒分析
点击放大
imaginaryC2 - Imaginary C2 is a python tool which aims to help i
项目说明
Imaginary C2
_author:_ Felix Weyne (website) (Twitter)
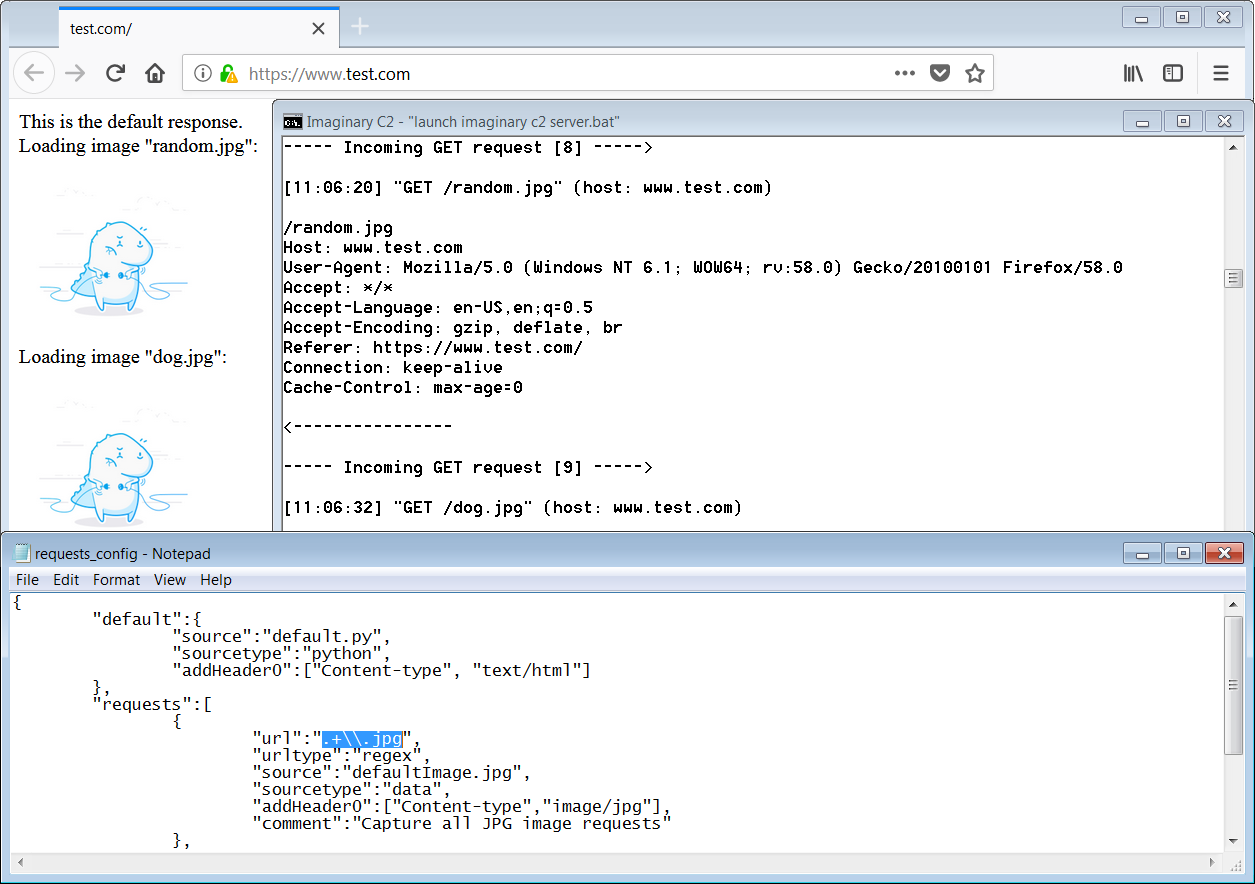
Imaginary C2 is a python tool which aims to help in the beha (network) analysis of malware.
Imaginary C2 hosts a HTTP ser captures HTTP requests towards selectively chosen domains/IPs. Additionally, the tool aims to make it easy to replay captured Command-and-Control responses/ser.
By using this tool, an analyst can feed the malware consistent network responses (e.g. C&C instructions for the malware to execute). Additionally, the analyst can capture and inspect HTTP requests towards a domain/IP which is off-line at the time of the analysis.
!Imaginary C2
Replay packet captures
Imaginary C2 provides two scripts to convert _packet captures (PCAPs)_ or _Fiddler Session Archives_ into __request definitions__ which can be parsed by imaginary C2.
scripts the user can extract HTTP request URLs and domains, as well as HTTP responses. This way, one can quickly replay HTTP responses for a given HTTP request.
Technical details
__requirements__: Imaginary C2 requires Python 2.7 and Windows.
__modules:__ Currently, Imaginary C2 contains three modules and two configuration files:
| Filename | Function
| ---------------------------------------------- | ------------------------------------------------------------------------------------------------------
| 1. imaginary_c2.py | Hosts python's simple HTTP server. Main module.
| 2. redirect_to_imaginary_c2.py | Alters Windows' host file and Windows' (IP) Routing Table.
| 3. unpack_fiddler_archive.py & unpack_pcap.py | Extracts HTTP responses from packet captures. Adds corresponding HTTP request domains and URLs to the configuration files.
| 4. redirect_config.txt | Contains domains and IPs which needs to be redirected to localhost (to the python HTTP server).
| 5. requests_config.txt | Contains URL path definitions with the corresponding data sources.
__request definitions__: Each (HTTP) request defined in the request configuration consists of two parameters:
Parameter 1: _HTTP request URL path_ (a.k.a. urlType)
| Value | Meaning
| ----- | -------
| fixed | Define the URL path as a literal string
| regex | Define a regex pattern to be matched on the URL path
Parameter 2: _HTTP response source_ (a.k.a. sourceType)
| Value | Meaning
| ----- | -------
| data | Imaginary C2 will respond with the contents of a file on disk
| python | Imaginary C2 will run a python script. The output of the python script defines the HTTP response.
Demo use case: Simulating TrickBot servers
Imaginary C2 can be used to simulate the hosting of TrickBot components and configuration files. Additionally, it can also be used to simulate TrickBot's web injection servers.
How it works:
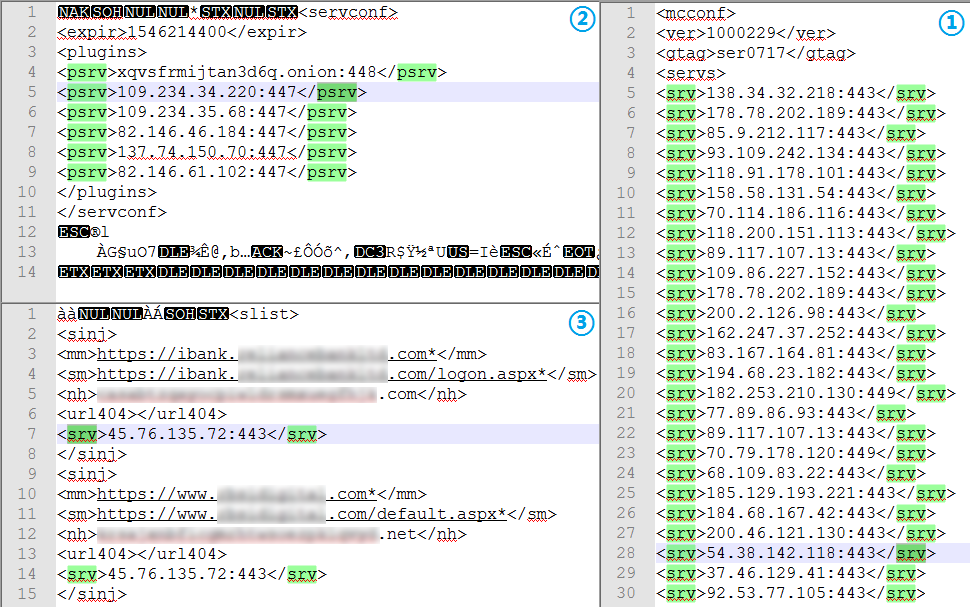
Upon execution, the TrickBot downloader connects to a set of hardcoded IPs to fetch a few configuration files. One of these configuration files contains the locations (IP addresses) of the TrickBot plugin servers. The Trickbot downloader downloads the plugins (modules) from these servers and decrypts them. The decrypted modules are then injected into a _s.exe_ instance.
!Example decoded TrickBot configuration files
One of TrickBot's plugins is called _injectdll_, a plugin which is responsible for TrickBot's webinjects. The _injectdll_ plugin regularly fetches an updated set of webinject configurations. For each targeted (banking) website in the configuration, the address of a _webfake server_ is defined. When a browses to a (banking) website which is targeted by TrickBot, his browser secretly gets redirected to the _webfake server_. The _webfake server_ hosts a replica of the targeted website. This replica website usually is used in a social-engineering attack to defraud the .
Imaginary C2 in action:
The below video shows the TrickBot downloader running inside _s.exe_ and connecting to imaginary C2 to download two modules. Each downloaded module gets injected into a newly spawned _s.exe_ instance. The webinject module tries to steal the browser's sa and exfiltrates the stolen passwords to the TrickBot server. Upon a targeted banking website, TrickBot redirects the browser to the _webfake server_. In the demo, the _webfake server_ hosts the message: "Default imaginary C2 ser" (full video).
!Imaginary C2 simulating TrickBot server
项目信息
开发语言:Python
Star 数:446
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures HTTP requests towards selectively chosen domains/IPs. Additionally, the tool aims to make it easy to replay captured Command-and-Control responses/served payloads.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | imaginaryC2 - Imaginary C2 is a python tool which aims to help i |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:19:46 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 234 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |