 病毒分析
点击放大
作者:admin
发布:2026-10-05
PeaceMaker - PeaceMaker Threat Detection is a Windows kernel-ba
项目说明PeaceMaker Threat DetectionPeaceMaker Threat Detection is a kernel-mode utility designed to detect a of methods commonly used in ad forms of malwa…
资源可下载
免费下载
0 条讨论
会员资源
开通会员后即可下载全部资源。
448浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-05
人工审核发布
评论区答疑
项目说明
PeaceMaker Threat Detection
PeaceMaker Threat Detection is a kernel-mode utility designed to detect a of methods commonly used in ad forms of malware. Compared to a stereotypical anti-virus that may detect or patterns, PeaceMaker targets the techniques malware commonly uses in order to catch them in the act. Furthermore, PeaceMaker is designed to provide an incredible amount of detail when a malicious technique is detected, allowing for effecti and response.
Moti
PeaceMaker was designed primarily as a weapon to detect custom malware in en. Specifically, this project was started in pursuit of preparing for the Information Security Talent Search blue/red team competition hosted by RIT's Security Club, RITSEC. The competition's red team is primarily industry security professionals, which is why I decided my own defense platform would be useful. In a project like this, I can make sacrifices to factors such as performance that widely-employed AV/EDR companies can't make, allowing me to make decisions I couldn't get away with in a real product.
Features
- Process Creation
- Image Load
- Thread Creation
- Logs the source process and stack of the operation.
Notable properties
Shortcomings
- Performs useful, but expensi that slow down common operations.
- Often allocates more memory than needed, doesn't utilize space optimization techniques such as compression.
- For example, filters that prevent deletion of a file or registry key can be bypassed.
- You can only filter on the target of an operation (i.e file/key name).
- Only protects against process termination of the GUI, nothing else.
Screenshots
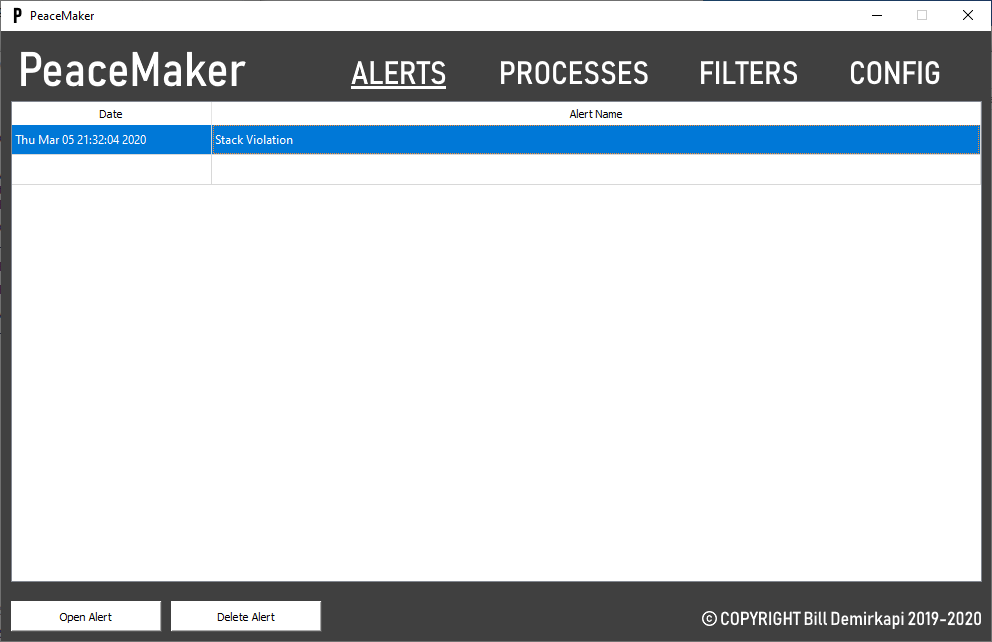
!Alerts Tab
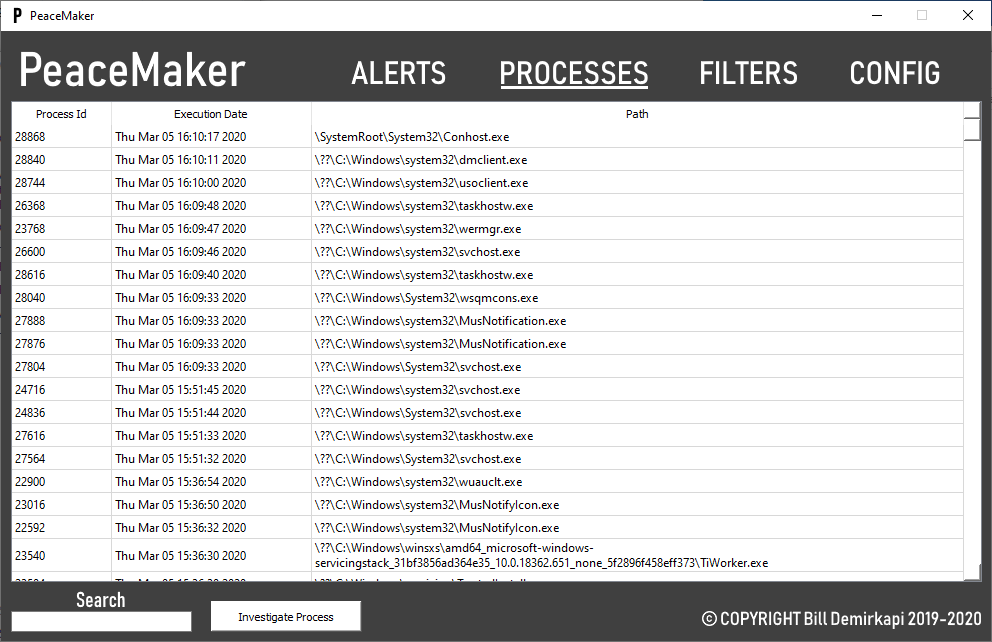
!Processes Tab
!Filters Tab
!Process Information
项目信息
开发语言:C++
Star 数:430
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕PeaceMaker Threat Detection is a Windows kernel-based application that detects advanced techniques used by malware.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PeaceMaker - PeaceMaker Threat Detection is a Windows kernel-ba |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:20:07 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 448 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |
本资源免费,登录后即可在本页「下载链接」区域获取全部附件。
请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。
请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
还没有讨论,快来抢沙发~
登录 后才能参与讨论