 病毒分析
点击放大
APT38-0day-窃取器 - APT38 Tactic PoC for Stealing 0days from security
项目说明
Lazarus-Tactic
<di="center">
<img src=" alt="Image Description" width="600">
</div>
* A program that automates the APT38 technique, which has been utilized to target cybersecurity researchers experts
* Lazarus is a state-sponsored group affiliated with North Korea, has a well-documented track record of targeting cybersecurity researchers. Among their notable techniques, one stands out for its effecti in tricking numerous cybersecurity experts.
* The attackers create multiple Twitter and other social media accounts to establish credibility. Through social engineering tactics, they manipulate security researchers into engaging in collaborati using a Microsoft Studio Project, the project contains a malicious code in the file. Consequently, when the researcher attempts to build the project, the malicious code embedded within it is executed.
Attack Scenario: De En Supply Chain Attack
An attacker sends a malicious Studio project to a de, the de opens the project, appearing to be a legitimate code sample, Upon first build, the program infects ALL Studio projects on the de's system
The infected de continues normal work, modifying and sharing projects with colleagues and each shared project carries the infection to new de machines and when colleagues open and build these projects, their en become infected the infection continues to spread across the de team
Impact
In a successful campaign, this will create a catastrophic compromise of the entire de ecosystem .
<di="center">
<img src=" alt="Image Description" width="600">
</div>
technical Details
This analysis is based on information shared by both Google Threat Analysis Group and a security researcher Joel Eriksson who documented their experience with this attack. Their tweet highlighted effecti measures:
Initial Approach
* Create believable security researcher personas on social platforms and Build trust through technical con
<di="center">
<img src=" alt="Image Description" width="600">
</div>
* Target actual security researchers through direct messages and Offer collaboration on "proof of concept" projects
<di="center">
<img src=" alt="Image Description" width="600">
</div>
Delivery Mechanism
* Send encrypted ZIP files containing Studio projects and claim the projects demonstrate interesting
Mention encryption to appear security-conscious
<di="center">
<img src=" alt="Image Description" width="600">
</div>
Use small file sizes (452.13KB) to seem like legitimate code projects
Execution Method
Hide malicious PowerShell commands within Studio project files the powerShell commands execute with bypassed execution policy and hidden windows
Include OS checks that :
* Windows 10 is running (os..major -eq 10)
* System is 64-bit (is64bitoperatingsystem)
* A specific path exists (Test-Path x64\Debug\Browse.VC.db)
Key technique: Use rundll32 to load malicious code from a file disguised as a Studio database file and call a specific exported function ENGINE_get_RAND with two parameters:
A 16-character string that appears to be a key/identifier: 6bt7cJNGEb3Bx9yK
A numeric value: 2907
<di="center">
<img src=" alt="Image Description" width="600">
</div>
APT38-0day-Stealer technical Details
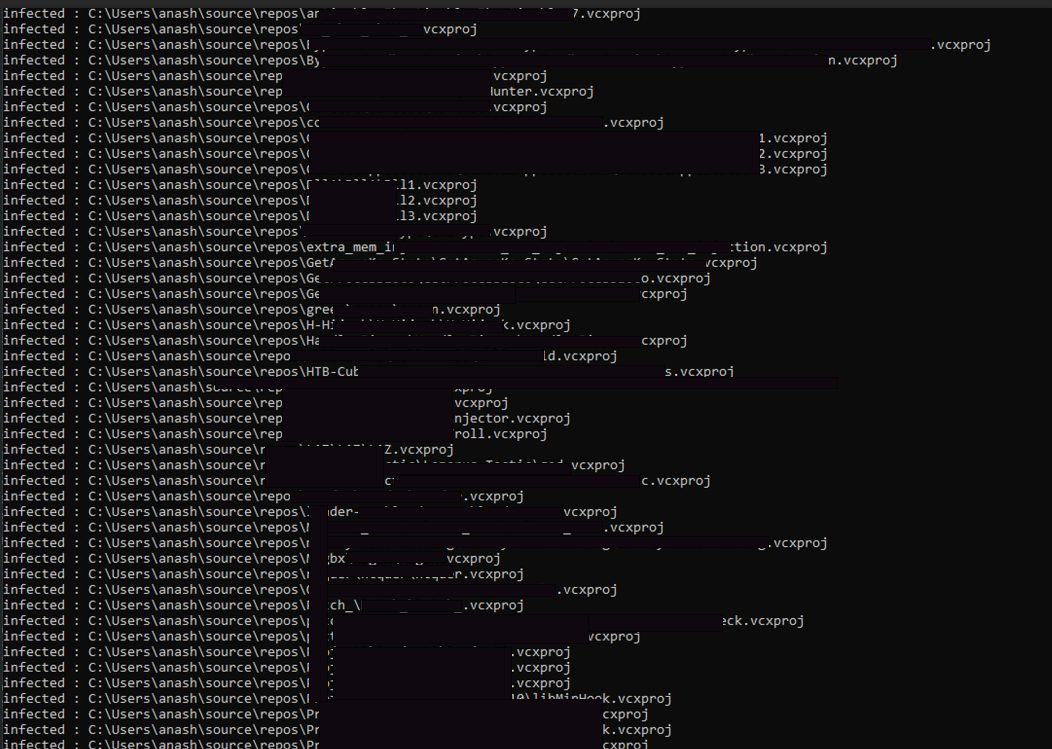
* Upon execution within the Studio projects directory, the program infects all files by injecting custom code. This code is designed to execute when the indi attempts to build the project .
<di="center">
<img src=" alt="Image Description" width="600">
</div>
DEMO
Credits
* Joel Eriksson
* Google Threat Analysis Group
项目信息
开发语言:C++
Star 数:335
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕APT38 Tactic PoC for Stealing 0days from security researchers展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | APT38-0day-窃取器 - APT38 Tactic PoC for Stealing 0days from security |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:22:41 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 446 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |