 病毒分析
点击放大
InflativeLoading - Dynamically convert an unmanaged EXE or DLL file t
项目说明
Inflati
Article: <
Major Update History
In this section, major updates are provided. Major updates do include added supports or features.
4/11/2024 Added PE Signature Obfuscation
Only a few bytes in the PE header, such as
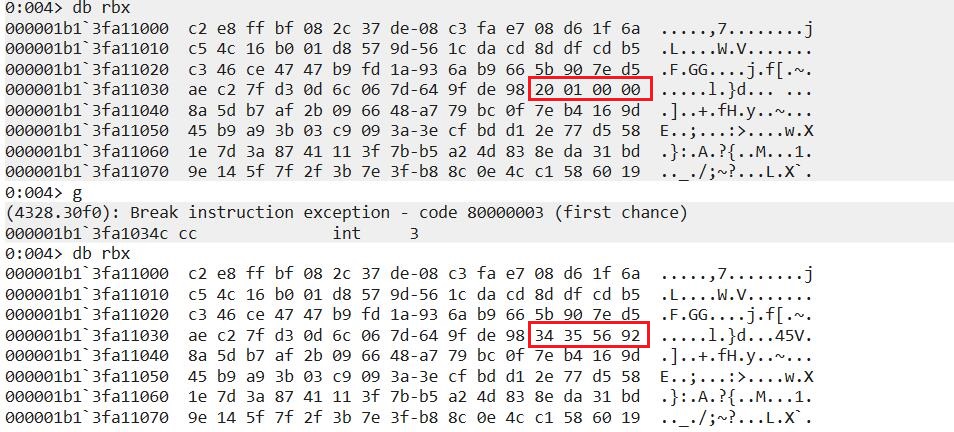
e_lfanew, RVA of Import Directory, are essential to complete the loading process. Therefore, other bytes can be o with random ones to hide PE header signatures.After all the processes are completed, e bytes will be o for complete obfuscation. For instance, from the screenshot below, we can notice that the PE header is mostly obfuscated, but e_lfanew remains unobfuscated for loading purposes. But after the loading process, e_lfanew is also obfuscated.
!image
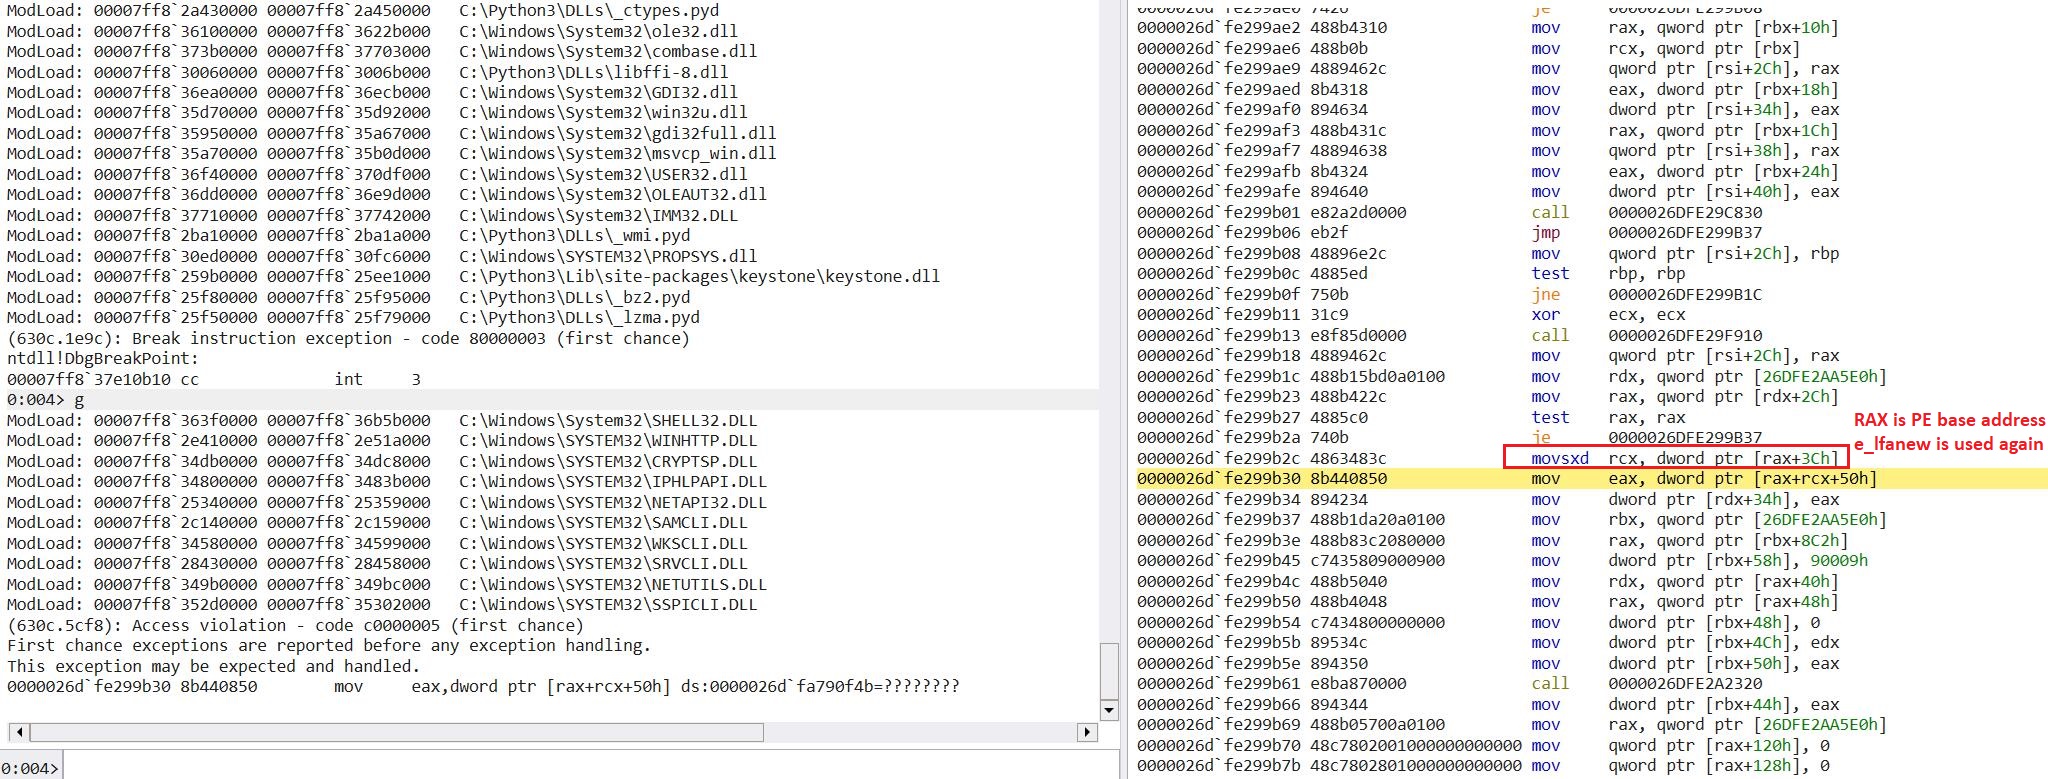
However, depending on the selected program, obfuscation may not be compatible with it. You should know how does the program work. For example, Ha DLL payload is not compatible with the obfuscation feature because the DLL also makes use of the PE header.
!image
Ha EXE payload works well with obfuscation:
4/11/2024 Replace padded NOP with NOP-Like instruction sequences
Before the update,
0x90/NOP instructions are padded after the actual shellcode stub to align a memory page. Many NOPs could be a detection, therefore, Inflati script dynamically selects preset NOP-Like instruction sequences. Users can also add new ones or replace existing ones to achie obfuscation.4/11/2024 Impro Logic
I added additional shellcode logic to handle some uncommon exceptions. For instance, in the CobaltStrike stateless DLL payload, some base relocation entries are invalid because the page RVA is larger than size of image.
The size of image is 0x58000.
!image
However, some RVAs are larger than 0x58000.
!image
Besides, the shellcode gracefully exits the program after executing the con shellcode.
4/11/2024 Improved PE Dumper
Now the dumper can display more information and provide suggestions for memory allocation:
The shellcode stub is fixed at 0x1000 bytes, the PE header is fixed at 0x1000 bytes, and the size of the text section and other sections .
4/11/2024 Added Support For Unmanaged DLL
After the update, unmanaged DLLs can also be con to PIC shellcode. Test cases for custom DLLs, Ha DLL payload, and CobaltStrike stageless DLL payload are passed.
!image
2/19/2024 Added Basic Support For UPX Packed EXE
I slightly modified the code that fixes IAT, because I found some lines of code are unnecessary. After this, Inflati can execute some UPX packed EXE programs, including calc.exe, PsExec. However, only some of packed programs. Firstly, I will not likely test all possible packing configurations for all tested programs. For the second reason, please continue to read:
For programs that do not have delayed import directory, Inflati can execute UPX-packed of them. However, unlike unpacked programs, packed programs have all ILT empty.
Take normal calc.exe as an example, ILT and IAT are identical for all modules.
!image
But for the UPX packed calc.exe, ILT is empty for all entries in Import Directory.
!image
But if the program has delayed import directory, like Mimikatz, it gets more complex.
For the normal mimikatz.exe, the delayed import directory is as follows:
!image
But for the UPX packed mimikatz.exe, PE Bear is unable to parse it, so do I.
!image
The below is a passed test case for UPX-packed calc.exe.
!image
Background
One of my goals is to convert an exe to shellcode. This way, some security tools like Mimikatz can be used with more flexibility. Though some tools like Donut ha achieved this, I still want to create such a tool with my approach, and hopefully, it can bring some impro.
Motivated and inspired by some classic and modern tools and techniques, Inflati is a tool that can dynamically convert an unmanaged EXE/DLL to PIC shellcode.
In short, Inflati generates and prepends a shellcode stub to a dumped PE main module.
The tool consists of DumpPEFromMemory.exe and Inflati.py.
Included Components
The following two components are required to convert an unmanaged PE file to shellcode.
DumpPEFromMemory Project
DumpPEFromMemory.exe is used to get the in-memory of the selected PE file.
For EXE programs, it works by creating a process in a suspended state and dumping the main module into a binary file (on your de). Why? A typical reflecti process maps each section of a PE file into a newly allocated memory region. Regarding this, I have two concerns: Firstly, although the data of each section is fundamentally consistent whether it resides on disk or in memory, there might still be certain differences for particular PE files or under specific circumstances.
For DLL files, DumPEFromMemory creates a file mapping and maps a view of the file without executing DllMain().
Secondly, the PE file's content already exists in the loader's memory(like a byte array), but the loader allocates memory space again. The execution of DumpPEFromMemory is completed on the operator's de. The operator gets a dump of the PE file when it is loaded in memory. Although some data still requires updates, allocating a memory region on the 's machine is unnecessary.
In this way, rather than manually map a file, we only need to patch specific data regions like Import Directory, Base Relocation Table Directory, Delayed Load Import Descriptors Directory, etc.
The dumped main module will be saved as a binary file to append to the shellcode stub.
For instance, DumpPEFromMemory executes a classic tool mimikatz, and dumps its main module into a binary file.
!image
And dump Havoc DLL payload from memory:
!image
Inflati Script
The script dynamically generates a shellcode stub and prepends it to the dump file.
The shellcode completes the following tasks:
1. Walk PEB and find kernel32.dll
2. Update the command line
3. Parse kernel32.dll to get the address of LoadLibraryA, GetProcAddress function.
4. Locate the appended dump file with an offset
5. Dynamically fix Import Directory, Base Relocation Table Directory, Delayed Load Import Descriptors Directory, etc.
6. Choose to obfuscate the PE header
7. Transfer the execution to the entry point of the PE file.
8. Exit gracefully
For instance, use the script to read pre dumped mimikatz and supply proper command line to dump credentials in LSASS:
!image
Though the shellcode stub should typically be less than 1000 bytes, the script still pads it to 4096 bytes for alignment with the memory page boundary. Then, the operator can easily set proper page permissions for different memory regions. The dumper provides memory allocation suggestion:
How To Use?
I believe you already went through both components of Inflati, in summary:
1. Use DumpPEFromMemory.exe to select an unmanaged PE file and dump the PE main module from memory into a bin file. Please refer to the Best Use Cases and Know Issues or Limitations sections for information on selecting PE files.
2. Use Inflati.py script to prepend a shellcode stub for the dump file. You can choose to provide a command line, obfuscate or not, and whether to execute the generated shellcode immediately. Currently, the user-supplied command line only works properly for a small set of programs.
Best Use Cases
Because Inflati is in its early stage, not every exe is supported well. Unmanaged DLL is supported well; execution of the export function is coming in the next update!
:white_check_mark: Nati program that does not rely on arguments, like stageless C2 implant, simple custom console program.
:white_check_mark: Nati program with an interacti/shell, like Mimikatz.
:white_check_mark: Unmanaged DLL
Impro O
:hea: No specific export functions are required, making it more friendly towards PE files for which the source code and compilation are not con accessible
:hea: Avoids unintended results due to differences between the PE file on disk and in memory in certain cases
:hea: Eliminates the need for con between the original file offset and RVA
:hea: Avoids additional memory space allocation
:hea: Avoids RWX memory regions.
:hea: Even for RX memory regions, it does not start with the MZ characteristic, increasing the difficulty of in.
Capabilities
:ballot_box_with_check: Support for normal native EXE
:ballot_box_with_check: Support for unmanaged DLL
:ballot_box_with_check: Support for EXE/DLL that has Delayed Import Directory
:ballot_box_with_check: Fix IAT
:ballot_box_with_check: Fix Base Relocation Directory
:ballot_box_with_check: Tests passed with classic programs like calc, mimikatz, PsExec, etc.
:ballot_box_with_check: Tests passed with classic C2 payload, such as CobaltStrike and Ha DLL/EXE payload.
:ballot_box_with_check: Partial support for packed programs.
Known Issues or Limitations
:warning: Some of the following issues may be fixed in the future, while some of them remain out of scope due to their nature.
+ Supplied command line does not always work properly. It is a major area that I will be focusing on.
+ Does not work well for GUI programs, like mspaint.exe. But calc.exe works well.
+ Does not work for all the packed programs. Some of the packed programs can be executed well, it is case by case.
+ Does not work for programs that require other dependencies, like custom DLLs.
+ Only support x64, and I do not plan to add support for x86 programs.
If you encounter any of the abo or limitations, the execution of shellcode may crash, the con program cannot properly identify the command line, or there may be no response.
For instance, PsExec.exe can be con to PIC shellcode, however, user-supplied command line cannot be identified properly.
Test Cases
| Program | FORMAT | Has GUI? | Supplied Arguments?| Successful Execution | Execute Properly w Arguments |
| ----------- | ----------- | ----------- |----------- | ----------- |----------- |
| Simple custom C/C++ programs | EXE |No | No |:hea: | N/A |
| Simple custom DLL | DLL |No | No |:hea: | N/A |
| Havoc and CobaltStrike EXE Payload | EXE |No | No |:hea: | N/A |
| Havoc and CobaltStrike DLL Payload | DLL |No | No |:hea: | N/A |
| calc.exe | EXE | Yes | No |:hea: |N/A |
| mimikatz.exe | EXE | No | Yes |:hea: |:hea: |
| PsExec | EXE | No |Yes |:hea: |:no_entry_sign:|
| mspaint.exe | EXE | Yes |No | :no_entry_sign: |N/A|
| Packed Programs | EXE | No |No | Partial|N/A |
Dumped of calc.exe and mimikatz.exe can be found in the bin/ folder of the repository.
Impro In The Future
:bell: The following features and impro are expected in the future.
+ A separate loader for .NET programs.
+ Add support for DLL export functions.
+ Add support for more packed programs.
+ Improve the shitty code : )
Acknowledgements and References
The following resources inspired me a lot during my research and de:
<
<
<
<
<
<
<
项目信息
开发语言:Python
Star 数:324
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | InflativeLoading - Dynamically convert an unmanaged EXE or DLL file t |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:23:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 471 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |