 病毒分析
点击放大
项目说明
MWEmu
![CI]()
![mwemu crates.io]()
![libmwemu crates.io]()
![Docs.rs]()
![PyPI]()

![MSRV]()
![Listed on mcpservers.org]()
Official documentation
mwemu.github.io
What is this?
It's a hardware emulator + OS process simulator implemented in pure rust.
This approach is very con to malware analysis and other stuff (PE, shellcode etc)
The OS is mainly windows, it emulates a windows process, some very basic support for linux.
The hardware is x86 32/64bits it's fast and reliable.
!MWEMU Logo
Three ways of using the software
note about scemu
The project was renamed from scemu to mwemu.
Some
r2con2025 using radare2 from mwemu for doing static analisys and inside an emulation moment.
some demos
Features
- All dependencies are in rust.
- benchmarks
- 25,767,432 instructions/second
- 680,000 instructions/second printing every instruction -vv.
- test yourself: time mwemu -f test/exe64win_enigma.bin -6 -v -c 20000000 --cmd q
- metasploit shellcodes.
- metasploit encoders.
- cobalt strike.
- shellgen.
- guloader (not totally for now, but arri than the debugger)
- mars stealer pe32.
- bumblebee.
- guloader
- xloader
- danabot
pymwemu
Capture an emulation moment
During the emulation you can see the nubmer of cpu instructions emulated, that's an unique ID for an emulation moment.
With -c flag you stop the emulation in a specific moment and inspect what is going on with the console.
Usage
Command line examples
64bits needs the -6 flag, -vv for ASM, and -c for spawning console at specific moment:
Testing
make tests
Some use cases
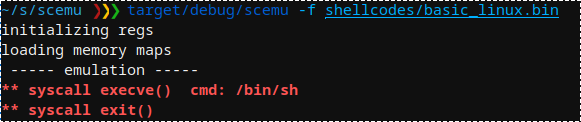
mwemu emulates a simple shellcode detecting the execve() interrupt.
note that I renamed this tool from scemu to mwemu (in italian scemu is a bad word)
!exploring basic shellcode
We select the line to stop and inspect the memory.
!inspecting basic shellcode
After emulating near 2 million instructions of GuLoader win32 in linux, faking cpuid's and other tricks in the way, arrives to a sigtrap to confuse debuggers.
!exception handlers
Example of memory dump on the api loader.
!exception handlers
There are several maps by default, and can be created more with apis like LoadLibraryA or manually from the console.
!exception handlers
Emulating basic windows shellcode based on LdrLoadDLl() that prints a message:
!msgbox
The console allow to view an edit the current state of the cpu:
The cobalt strike api loader is the same that metasploit, emulating it:
!api loader
Cobalt Strike API called:
!cobalt strike
Metasploit rshell API called:
!msf rshell
Metasploit SGN encoder using few fpu to hide the polymorfism:
!msf encoded
Metasploit shikata-ga-nai encoder that also starts with fpu:
!msf encoded
Displaying PEB structure:
Displaying PEB_LDR_DATA structure:
Displaying LDR_DATA_TABLE_ENTRY and first module name
A malware is hiding something in an exception
Let's inspect exception structures:
And here we have the error routine 0x4f96f4 and the filter 0x51068c
Star History
![Star History Chart]()
项目信息
开发语言:Rust
Star 数:316
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕x86 malware emulator展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | mwemu - x86 malware emulator |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:23:20 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 536 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |