 病毒分析
点击放大
Hells-Hollow - Hells Hollow Windows 11 Rootkit technique to Hook
项目说明
Hells Hollow
Hell's Hollow is a Windows 11 compatible rootkit technique that is equi to a modern (PatchGuard) resistant technique to effectively
perform SSDT Hooking (System Service Dispatch Table) - bypassing all previous defence mechanisms put in the kernel.
This technique works by abusing an undocumented Alternate Syscall handler mechanism in the kernel, within which we are able to directly
alter the KTRAP_FRAME, allowing us to effectively hook the SSDT in Windows 11. We are able to decide to either let the OS continue to dispatch the
system call (and giving us the ability to alter the arguments passed to it), or to alter it on behalf of the dispatcher, and return straight back to
userland - so the calling application thinks the system call was dispatched normally.
Shoutout to who made a key obser in my first implementation of this, that the KTRAP discovery can be simplified
by reading directly from the KTHREAD. The repo is now updated to reflect this, and it now works e with no stack modification required!
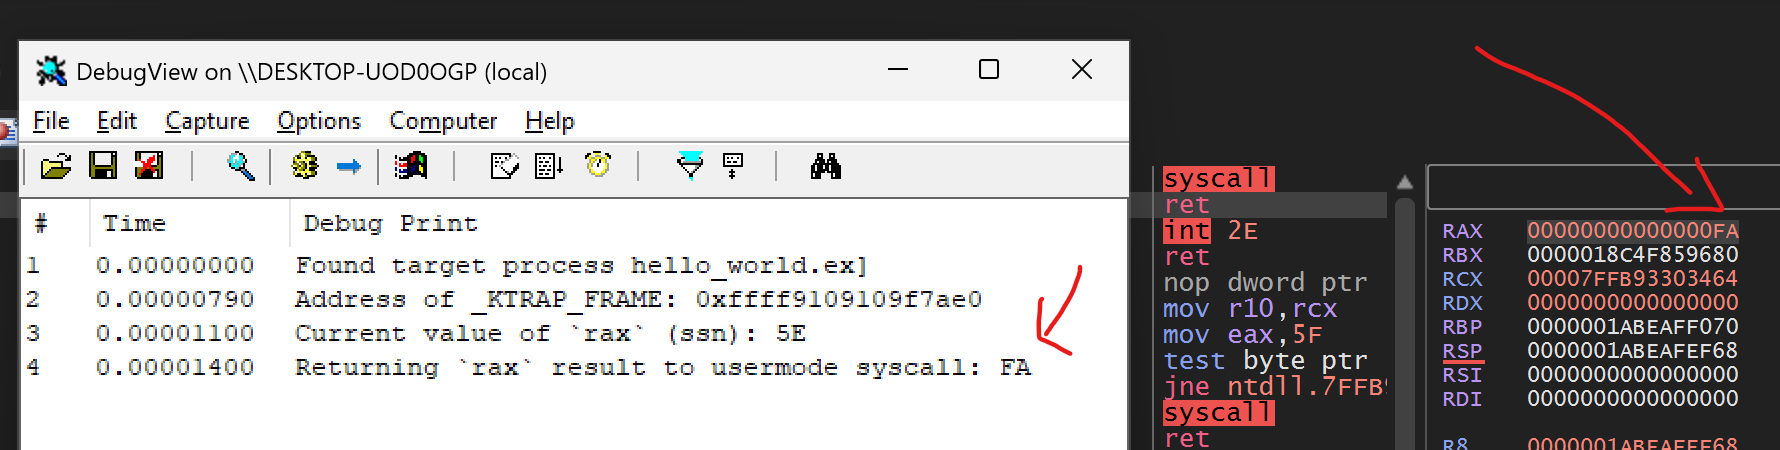
Altering the return value from a syscall via the hook:
!Hells Hollow SSDT hooking Windows 11 Rust
Limitations
Thanks to some testing by Xacone, we now know that HVCI prevents writing to the PspSer structure; so this technique is blocked by HVCI.
Setup
I ha this repo as a MVP for producing the technique (in RUst). If you are new to Rust, and simply want to get it up
and running, follow the en config steps at Windows Rust Drivers project and run cargo make.
It will spit our a driver that you can simply load with OSR or whatever tool you want. This POC is designed to hook NtTraceEvent in the kernel (via Alt Syscalls),
it will modify the return value to 0xff in rax to usermode.
If you want to test this out on a SSN of your choice that isn't NtTraceEvent, then make a program called hello_world.exe (this rootkit currently filters on that)
and in alt_syscalls.rs change which SSN you want to hook, which is currently defined as:
Then, a kernel debugger for the Alt Syscall callback / trap, or a usermode debugger on the syscall itself, you'll see what's going on under the hood.
Video POC coming soon with a bit more of an explanation on what is going on, until then, read my blog :).
References
项目信息
开发语言:Rust
Star 数:292
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Hells Hollow Windows 11 Rootkit technique to Hook the SSDT via Alt Syscalls展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Hells-Hollow - Hells Hollow Windows 11 Rootkit technique to Hook |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:24:18 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 191 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |