 病毒分析
点击放大
DrSemu - DrSemu - Sandboxed Malware Detection and Classific
项目说明
Dr.Semu
Dr.Semu runs executables in an isolated en, monitors the behavior of a process, and based on Dr.Semu rules created by you or the community, detects if the process is malicious or not.
!drsemu_lua
[The tool is in the early de stage]
#### whoami: @_qaz_qaz
With Dr.Semu you can create rules to detect malware based on dynamic behavior of a process.
Isolation through redirection
E happens from the user-mode. Windows Projected File System (ProjFS) is used to provide a file system. For Registry redirection, it clones all Registry hives to a new location and redirects all Registry accesses.
See the source code for more about other redirections (process/objects isolation, etc).
Monitoring
Dr.Semu uses DynamoRIO (Dynamic Instrumentation Tool Platform) to intercept a thread when it's about to cross the user-kernel line. It has the same effect as hooking SSDT but from the user-mode and without hooking anything.
At this phase, Dr.Semu produces a JSON file, which contains information from the interception.
Detection
After terminating the process, based on Dr.Semu rules we receive if the executable is detected as malware or not.
Dr.Semu Rules/Detections
Dr.Semu rules
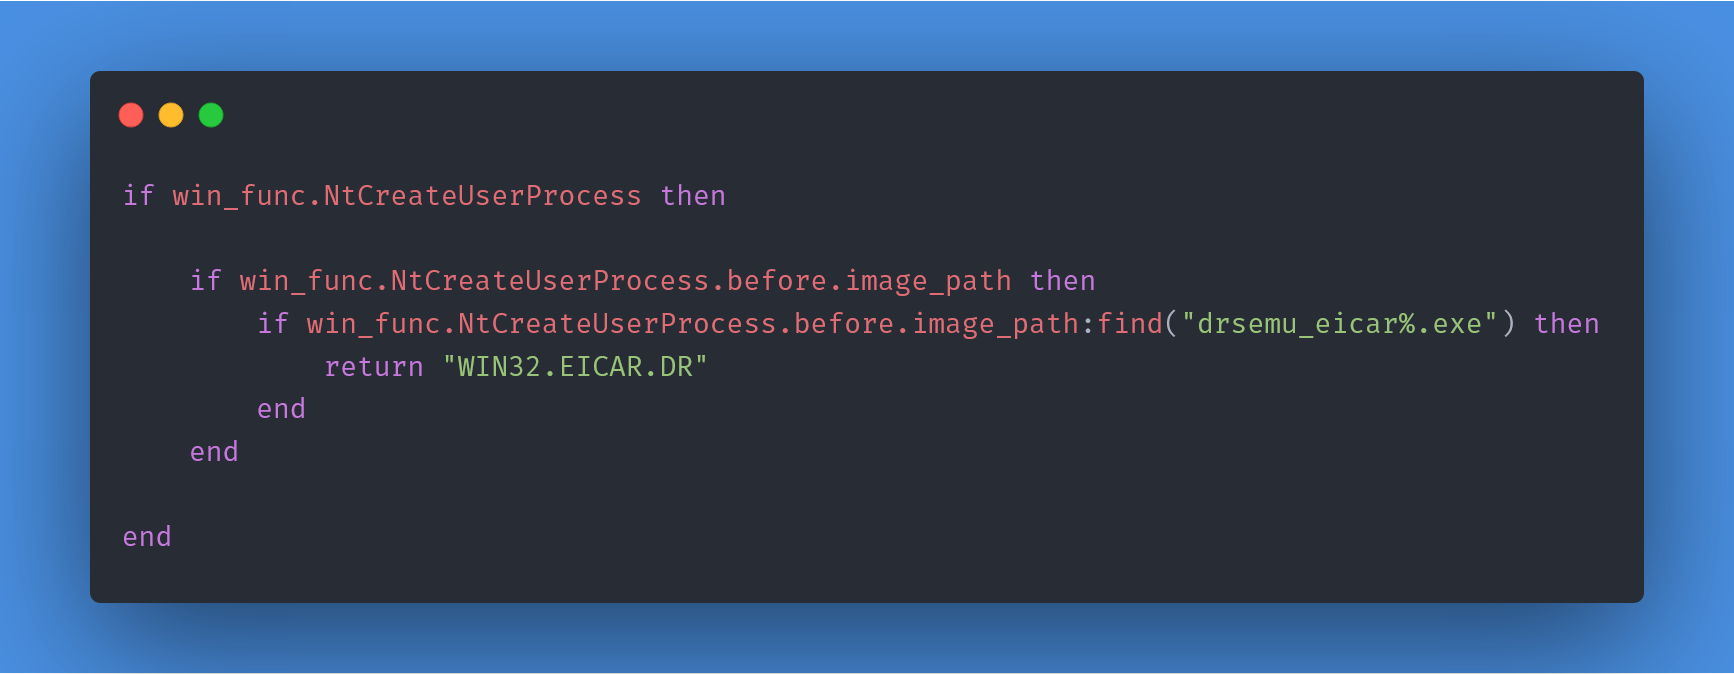
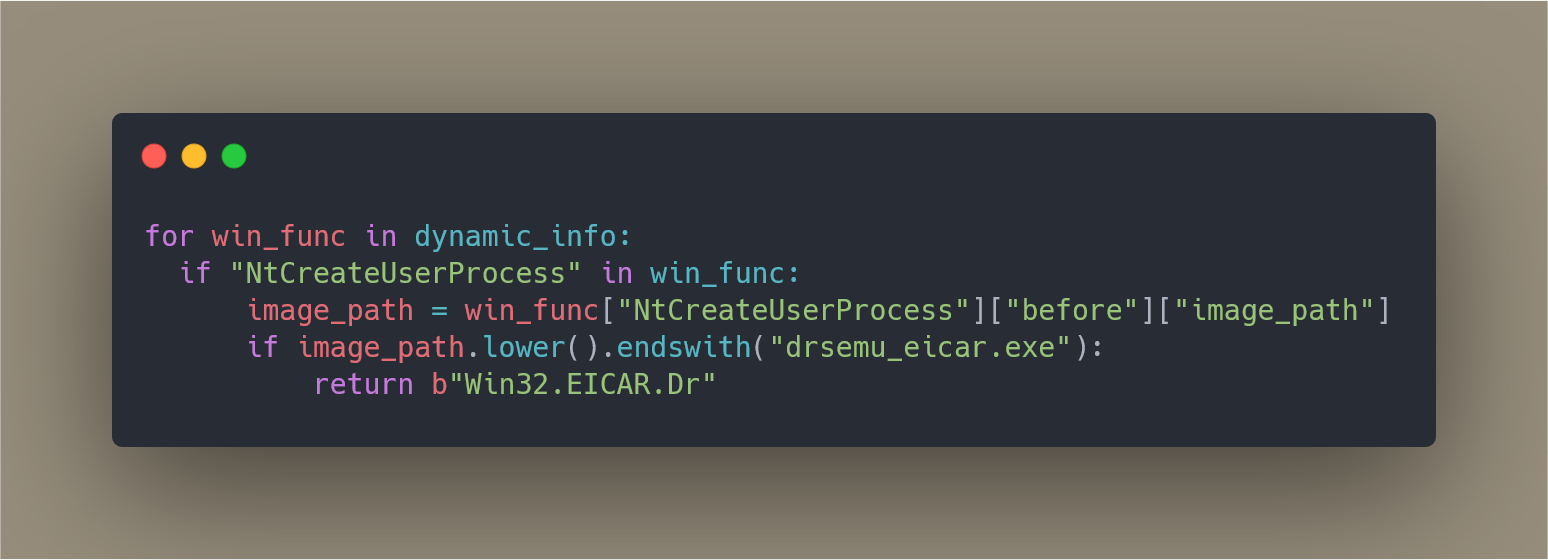
They are written in Python or LUA (located under dr_rules) and use dynamic information from the interception and static information about the sample. It's trivial to add support of other languages.
!drsemu_rule_python
Example (Python):
Example (Lua):
Usage
PowerShell to enable ProjFS in an elevated PowerShell window:Enable-WindowsOptionalFeature -Online -FeatureName Client-ProjFS -NoRestart
DynamoRIO and extract into DrSemu folder and rename to dynamorioDrSemu.exe --target file_path
DrSemu.exe --target files_directory
DEMO

BUILD
* Use
PowerShell to enable ProjFS in an elevated PowerShell window:Enable-WindowsOptionalFeature -Online -FeatureName Client-ProjFS -NoRestart
!powershell
* Install Python 3 x64
* Download DynamoRIO and extract into bin folder and rename to dynamorio
* Build pe-parser-library.lib library:
- Generate from DrSemu\shared_libs\pe_parse using cmake-gui
- Build 32-bit library under build (\shared_libs\pe_parse\build\pe-parser-library\Release\) and 64-bit one under build64
- Change run-time library option to Multi-threaded (/MT)
* Set LauncherCLI As StartUp Project
TODO
Limitations
Windows 10, 1809 (due to Windows Projected File System)Windows 10, 1809 (DynamoRIO supports Windows 10 until 1809)项目信息
开发语言:C++
Star 数:280
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | DrSemu - DrSemu - Sandboxed Malware Detection and Classific |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:24:33 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 537 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |