 病毒分析
点击放大
reveng_rtkit - Linux Loadable Kernel Module (LKM) based rootkit (
项目说明
re
<p align="center">
<img alt="Language" src=" />
<img alt="Compiled with" src=" />
<img alt="Tested on" src=")%20x86__64%20and%20Kernel%205.11.0--49--generic-yellow" />
</p>
<p align="center">
<!--
<img alt="Category" src=" />
-->
<img alt="Category" src=" />
<img alt="License" src=" />
</p>
*re* is a Linux Loadable Kernel module (aka LKM) based rootkit targeting Linux Kernel: 5.11.0-49-generic as it was only tested on it till now.
---
> :no_entry_sign: [Disclaimer]: Use of this project is for Educational/ Testing purposes only. Using it on unauthorised machines is strictly forbidden. If somebody is found to use it for illegal/ malicious intent, author of the repo will not be held responsible.
---
re mechanism:
![]()
<ins>Rootkit features</ins>:
| Sl. no. | Name | Features |
| ------- | ------- | -------- |
| 1. | Finding Syscall Table address | By creating custom kallsyms_lookup_name function to get <ins>address</ins> of sys_call_table symbol from kernel memory. |
| 2. | Function Hooking | Get the <ins>address</ins> of the syscall from sys_call_table to get them hooked, then modify CR0 register to <ins>remo protect bit</ins> and then modify/edit the sys_call_table and then again <ins>applying write protection to kernel memory</ins>. |
| 3. | Hide Rootkit | Hides itself by deleting itself(or entry) from responsible linked list. |
| 4. | Hide Processes/implants | Done in same way, as mentioned above in Sl. no. 2. |
| 5. | Unable to rmmod rootkit module | Using kernel function called try_module_get() makes impossible for admins to remove our rootkit. |
| 6. | Interacti | Implementing an IOCTL which manages the features of the rootkit and allows the user to send it commands. |
| 7. | Bypassing | Can bypass infamous rkhunter antirootkit |
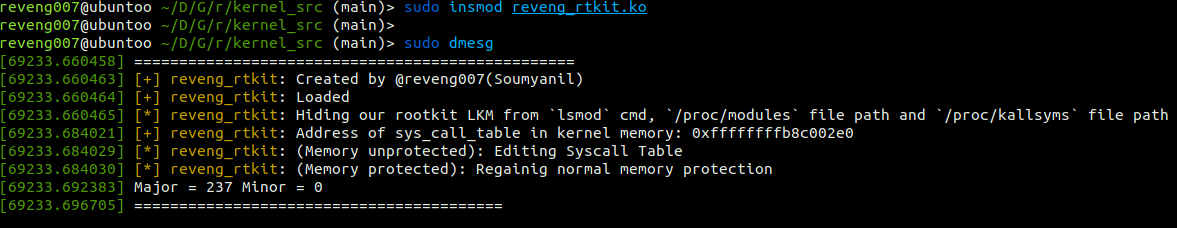
Let's see what functions will be called during loading the rootkit:
| Defined within Filename | Functions | function name in rootkit.c | Working | Effectivity of remo() | Mode of access |
| ----------------------- | --------- | -------------------------- | ------- | ----------------------------------------------------- | -- |
| hide_show_helper.h | proc_lsmod_hide_rootkit() | hide_rootkit() | Hides rootkit from _"/proc/modules"_ file, _"/proc/kallsyms"_ file and "lsmod" command. | No effectivity | ./client_usermode |
| hide_show_helper.h | sys_module_hide_rootkit() | hide_rootkit() | Hides rootkit from "/sys/module/<THIS_MODULE>/" directory. | No effectivity | ./client_usermode |
| hide_show_helper.h | proc_lsmod_show_rootkit() | show_rootkit() | Reveals our rootkit in _"/proc/modules"_ file, _"/proc/kallsyms"_ file and "lsmod" command. | Will work effectively | ./client_usermode |
| hide_show_helper.h | sys_module_show_rootkit() | show_rootkit() | Reveals our rootkit in "/sys/module/<THIS_MODULE>/" directory. | _ | ./client_usermode |
| rootkit.c | tidy() | tidy() | In this function we do some clean up. If we don't do this, there will be some errors during unloading the rootkit using rmmod. | _ | _ |
| rootkit.c | protect_rootkit() | protect_rootkit() | This is very simple function which just makes impossible to unload the rootkit by "rmmod rootkit" command even if it is . However it is still possible to unload by "rmmod -f rootkit" if kernel was compiled with support for forced unloading modules. link: sysprog21.github.io | _ | ./client_usermode |
| rootkit.c | remo() | remo() | Making rootkit removable from kernel using rmmod | _ | ./client_usermode |
| hook_syscall_helper.h | hacked_kill() | rootkit_init() and rootkit_exit(void) | Process/Implant Hiding | _ | cmd prompt: kill -31 \<pid> |
| hook_syscall_helper.h | hacked_kill() | rootkit_init() and rootkit_exit(void) | getting rootshell | _ | cmd prompt: kill -64 \<any pid> |
NOTE:
> Function tidy(), sys_module_hide_rootkit() and sys_module_show_rootkit() are not used in code. They were commented out. The reason behind that will be discussed in details in my blog post.
How to use it:
1. Clone the repo
2. Enter the directory
3. Now, we have 2 directories: kernel_src and user_src.
Contains
usermode client code to interact with our rootkit module (once it it loaded into the kernel) via the registered Character Device file.Contains
kernelmode rootkit: re which will be responsible for the whole mayhem :wink:.!kernel_rootkit
4. To interract with the kernel rootkit. Open another terminal
5. compile and run the code
#### NOTE: Be sure to run the code with root pri we are interracting with device driver, which is a part of the Linux kernel.
!client_mode
6. Another method to interract with it is via kill syscall interception:
!Screenshot from 2022-02-25 20-40-46
!Screenshot from 2022-02-25 20-45-45
#### NOTE:
> This rootkit is capable of pro rootshell to only bash and sh shell, not others. Although, it is possible for other shells as well but with some tricks. We can use system() C function alike function in Linux Kernel programming, so that we 1st trigger a bash/sh shell then offer rootshell to the attacker. I have'nt got that type of kernel function till now, but as soon as I get it, I will add it up. If anybody this know about this, or interested to contribute, are most welcome to make a pull request.
show command using client_usermode file as re while loading hides itself from being re (also change to remove mode, if you have made rootkit module to protect mode pre).Bypassing *rkhunter* antirootkit:
Here is the log file, that was generated:
![asciicast]()
1. /usr/bin/lwp-request : stackexchange
So, this is not a threat! cool!
Update:
Today, I found out this *Warning*.
!rootkit_warning
Then searched for other options of *rkhunter* to get more informations about this "warning", that which exact processes are actually causing this warning (suspicious (large) shared memory segments). Found out this:
!rootkit_warning_reasons
We can see it is telling us, configured size allowed: 1.0MB, i.e. those processes which takes more than 1MB gets flagged. But main point is our rootkit is not getting flagged :) (More like False-Positi).
There are several links related to this:
1. ser
2. linuxquestions
To-Do list :man_mechanic::
ls <filename>, they can easily open them./sys/module/ directory using sycall interception, in order to decie programs issue #6.kernel_src/re.c issue #8.bypass SELinux enabled Linux System issue #9.chkrootkit antirootkit issue #4.- Getting detected by
chkrootkit antirootkit till now, under chkproc section: chkproc.c
!Screenshot from 2022-02-26 09-33-19
Limitations:
1. Secure Boot
2. Adding a grub parameter to "
/etc/default/grub" file.This thing was pointed out to me by Artem Baranov and this link was shared to me, on my linkedin post, by Sergeev, for further research.
Detections:
#### 1. Blog by : diy-linux-kernel-rootkit-detection
#### 2. Unususal Kernel Taints kernel-taint.sh:
<img width="1926" height="746" alt="image" src=" />
> Can also be detected by : Osqueryi Sql Script: unusually-tainted-kernel-linux.sql
#### 3. Detecting unusual /dev entries (unexpected-device.sql, mode: .mode line):
<img width="831" height="465" alt="image" src=" />
> Another rootkit detection paper by SANS: Linux kernel rootkits: protecting the system’s “Ring-Zero”. Can be Explored, too!
#### Detailed Blog article on *re* LKM rootkit, is a now, where I ha how I created this LKM rootkit step by step.
> If you() ha anything erronious or something which should be made correct, haven't documented correctly or haven't credited someone's work properly, please don't hesitate to reach out to me social media handles listed at the end of this file.
Honourable Mentions:
Resources that helped me:
1. This project is heavily inspired by Heroin by Runar Jensen (didn't get any of his social media handle ;( ) and Diamorphine by open source LKM rootkit projects. Especially, the
Syscall interception mechanism section was totally taken from Diamorphine repo by .2.
3. Rootkit features:
4. Excellent resource for grabbing lkm rootkit concepts:
5. Simple LKM rootkit:
6. IOCTL:
7.
8. LKM HACKING:
9. Hide Files and Processes:\
i.
ii.
iii.
10. Get Rootshell:
11. kobject:
12.
13.
14. Editing cr0 register:
15.
Slides from my talk on BSides Singapore
1. PPT: PPT
2. PDF: pdf
Author: @re (Soumyanil Biswas)
---
![]()
![]()
![]()
项目信息
开发语言:C
Star 数:272
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Linux Loadable Kernel Module (LKM) based rootkit (ring-0), capable of hiding itself, processes/implants, rmmod proof, has ability to bypass infamous rkhunter antirootkit.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | reveng_rtkit - Linux Loadable Kernel Module (LKM) based rootkit ( |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:24:41 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 260 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |