 病毒分析
点击放大
malware_api_class - Malware dataset for security researchers, data sci
项目说明
!Total Downloads
Windows Malware Dataset with PE API Calls
Our public malware dataset generated by Cuckoo Sandbox based on Windows OS API calls analysis for cyber security researchers for malware analysis in csv file format for machine learning applications.
Cite The DataSet
If you find those results useful please cite them :
{10.7717/peerj-cs.346,
title = {Data augmentation based malware detection using con neural networks},
author = {Catak, Ferhat Ozgur and Ahmed, Javed and Sahinbas, Kevser and Khand, Zahid Hussain},
year = 2021,
month = jan,
keywords = {Con neural networks, Cybersecurity, Image augmentation, Malware analysis},
= 7,
pages = {e346},
journal = {PeerJ Computer Science},
issn = {2376-5992},
url = {
doi = {10.7717/peerj-cs.346}
}
Publications
The details of the Mal-API-2019 dataset are published in following the papers:
* [[Link]]() AF. Yazı, FÖ Çatak, E. Gül, *Classification of Metamorphic Malware with Deep Learning (LSTM)*, IEEE Signal Processing and Applications Conference, 2019.
* [[Link]]() Catak, FÖ., Yazi, AF., *A Benchmark API Call Dataset for Windows PE Malware Classification*, arXiv:1905.01999, 2019.
Introduction
This study seeks to obtain data which will help to address machine learning based malware research gaps. The specific objective of this study is to build a benchmark dataset for Windows operating system API calls of malware. This is the first study to undertake metamorphic malware to build sequential API calls. It is hoped that this research will contribute to a deeper understanding of how metamorphic malware change their behavior (i.e. API calls) by adding meaningless opcodes with their own dissembler/assembler parts.
Malware Types and System O
In our research, we ha the families produced by each of the software into 8 main malware families: *Trojan, Backdoor, Downloader, Worms, Spyware Adware, Dropper, Virus*. Table 1 shows the number of malware belonging to malware families in our data set. As you can see in the table, the number of samples of other malware families except *AdWare* is quite close to each other. There is such a difference because we don't find too much of malware from the adware malware family.
| Malware Family | Samples | Description |
| ------------- |:-------------:|:-----|
| Spyware | 832 | enables a user to obtain covert information about another's computer acti by transmitting data co from their hard drive. |
|Downloader | 1001 | share the primary functionality of downloading content. |
|Trojan | 1001 | misleads users of its true intent.|
|Worms | 1001 | spreads copies of itself from computer to computer.|
|Adware | 379 | hides on your device and serves you ad.|
|Dropper | 891 | surreptitiously carries , back doors and other malicious software so they can be executed on the compromised machine. |
|Virus | 1001 | designed to spread from host to host and has the ability to replicate itself.|
|Backdoor | 1001 | a technique in which a system security mechanism is bypassed undetectably to access a computer or its data. |
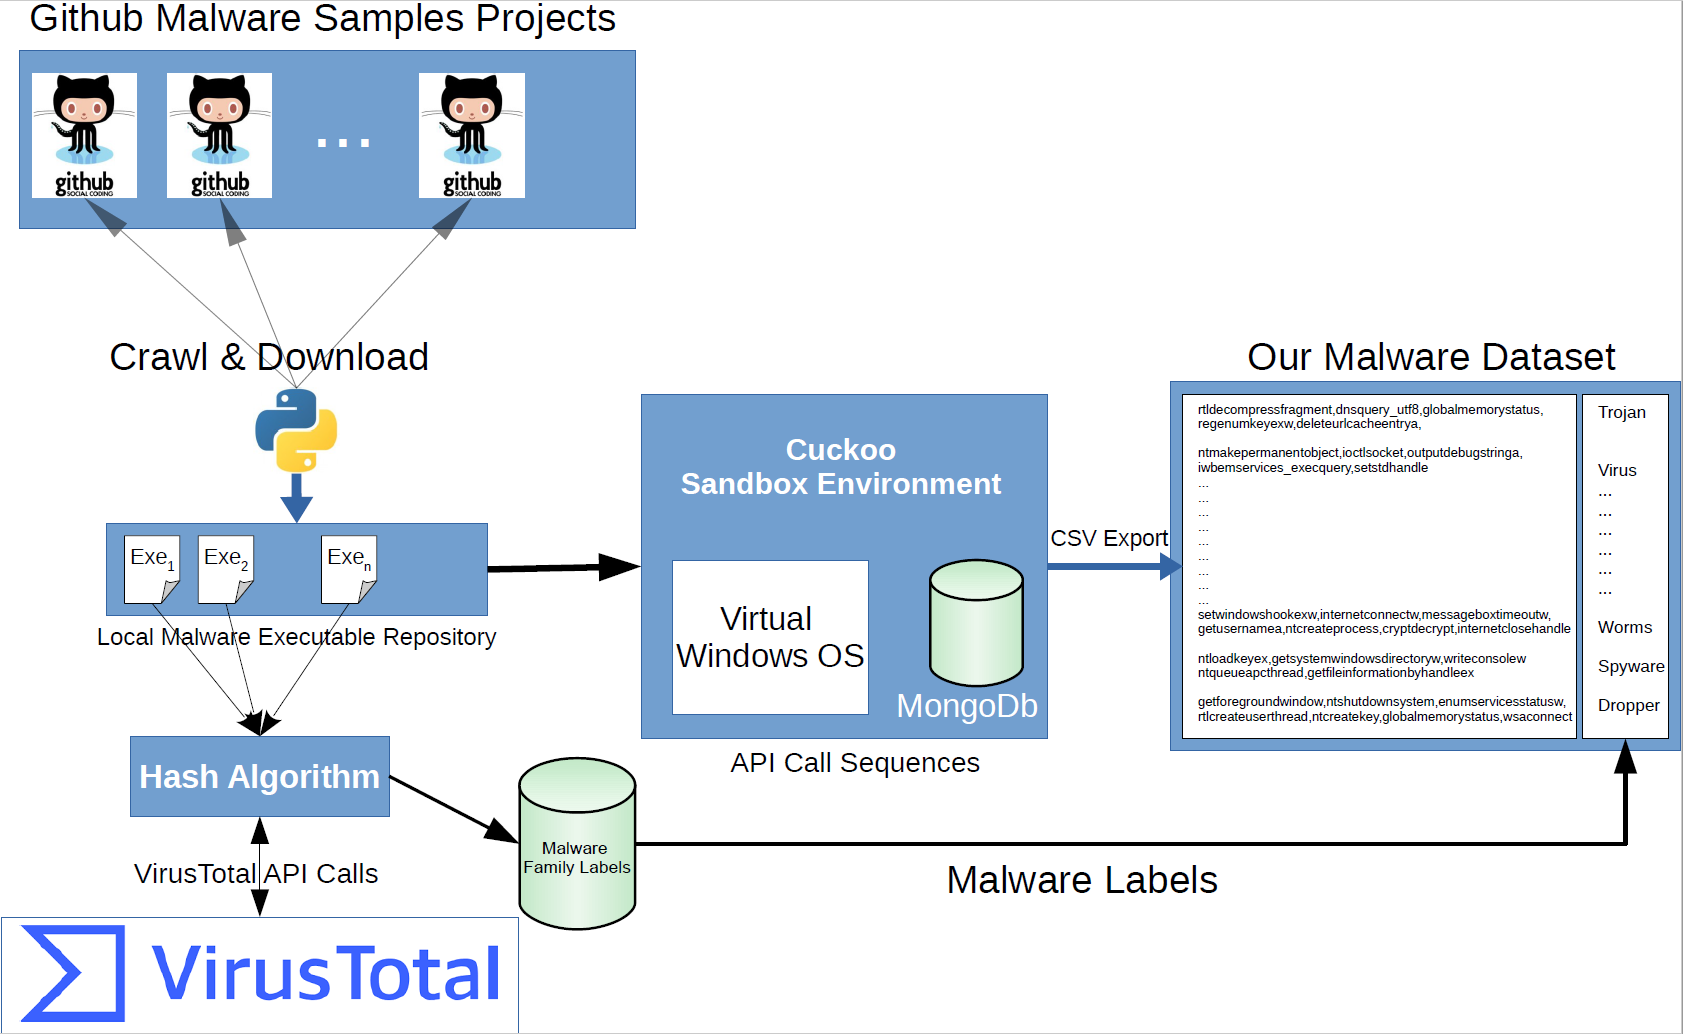
Figure shows the general flow of the generation of the malware data set. As shown in the figure, we ha the MD5 hash of the malware we collect from Github. We searched these hash using the API, and we ha the families of these malicious software from the reports of 67 different antivirus software in . We ha that the malicious software families found in the reports of these 67 different antivirus software in are different.
!Screenshot
Data Description
* Sample dataset
* labels
* all dataset
项目信息
开发语言:Python
Star 数:262
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Malware dataset for security researchers, data scientists. Public malware dataset generated by Cuckoo Sandbox based on Windows OS API calls analysis for cyber security researchers展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | malware_api_class - Malware dataset for security researchers, data sci |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:25:12 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 488 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |