 病毒分析
点击放大
Arkana - Arkana - Your entire malware analysis lab, behind
项目说明
Arkana - Your Entire Malware Analysis Lab, Behind One AI Prompt
!Arkana Logo

![CI]()
![Python 3.10+]()

![GitHub stars]()
![MCPVault: claimed]()
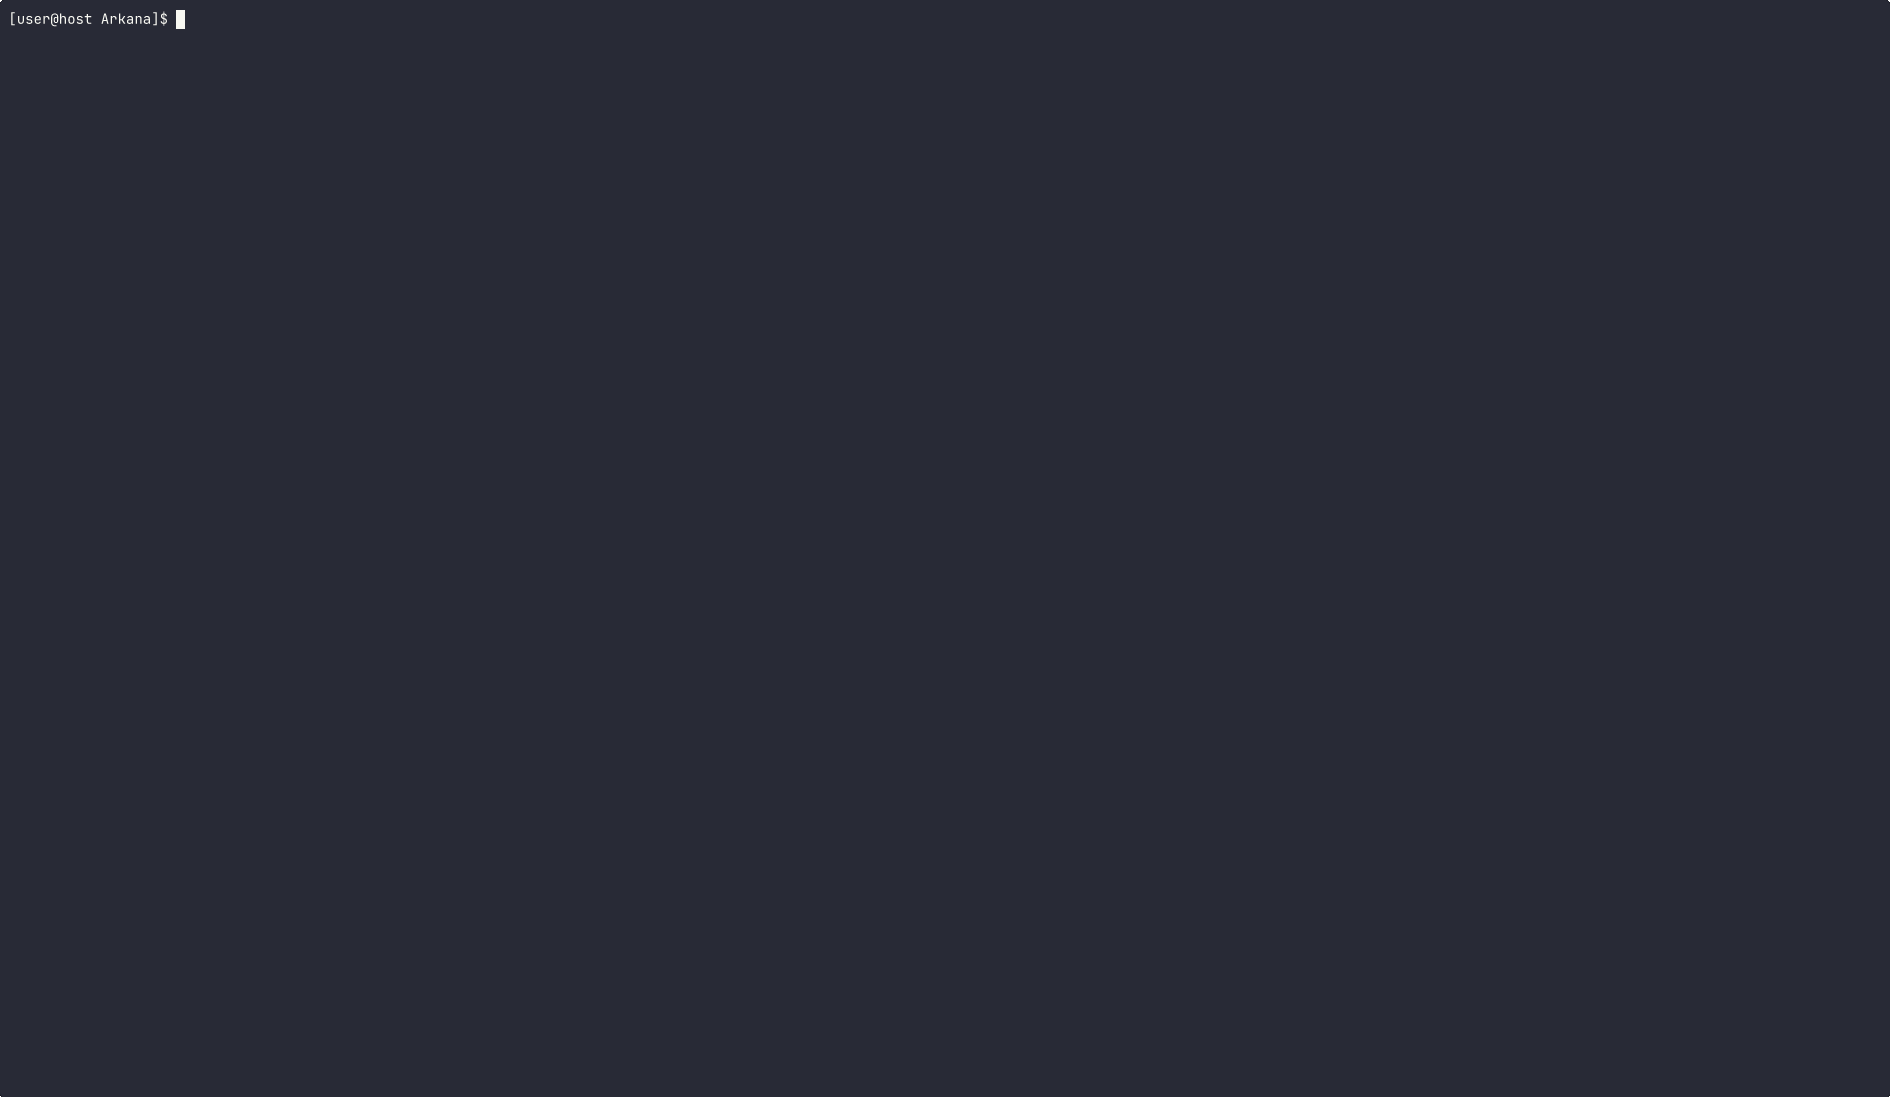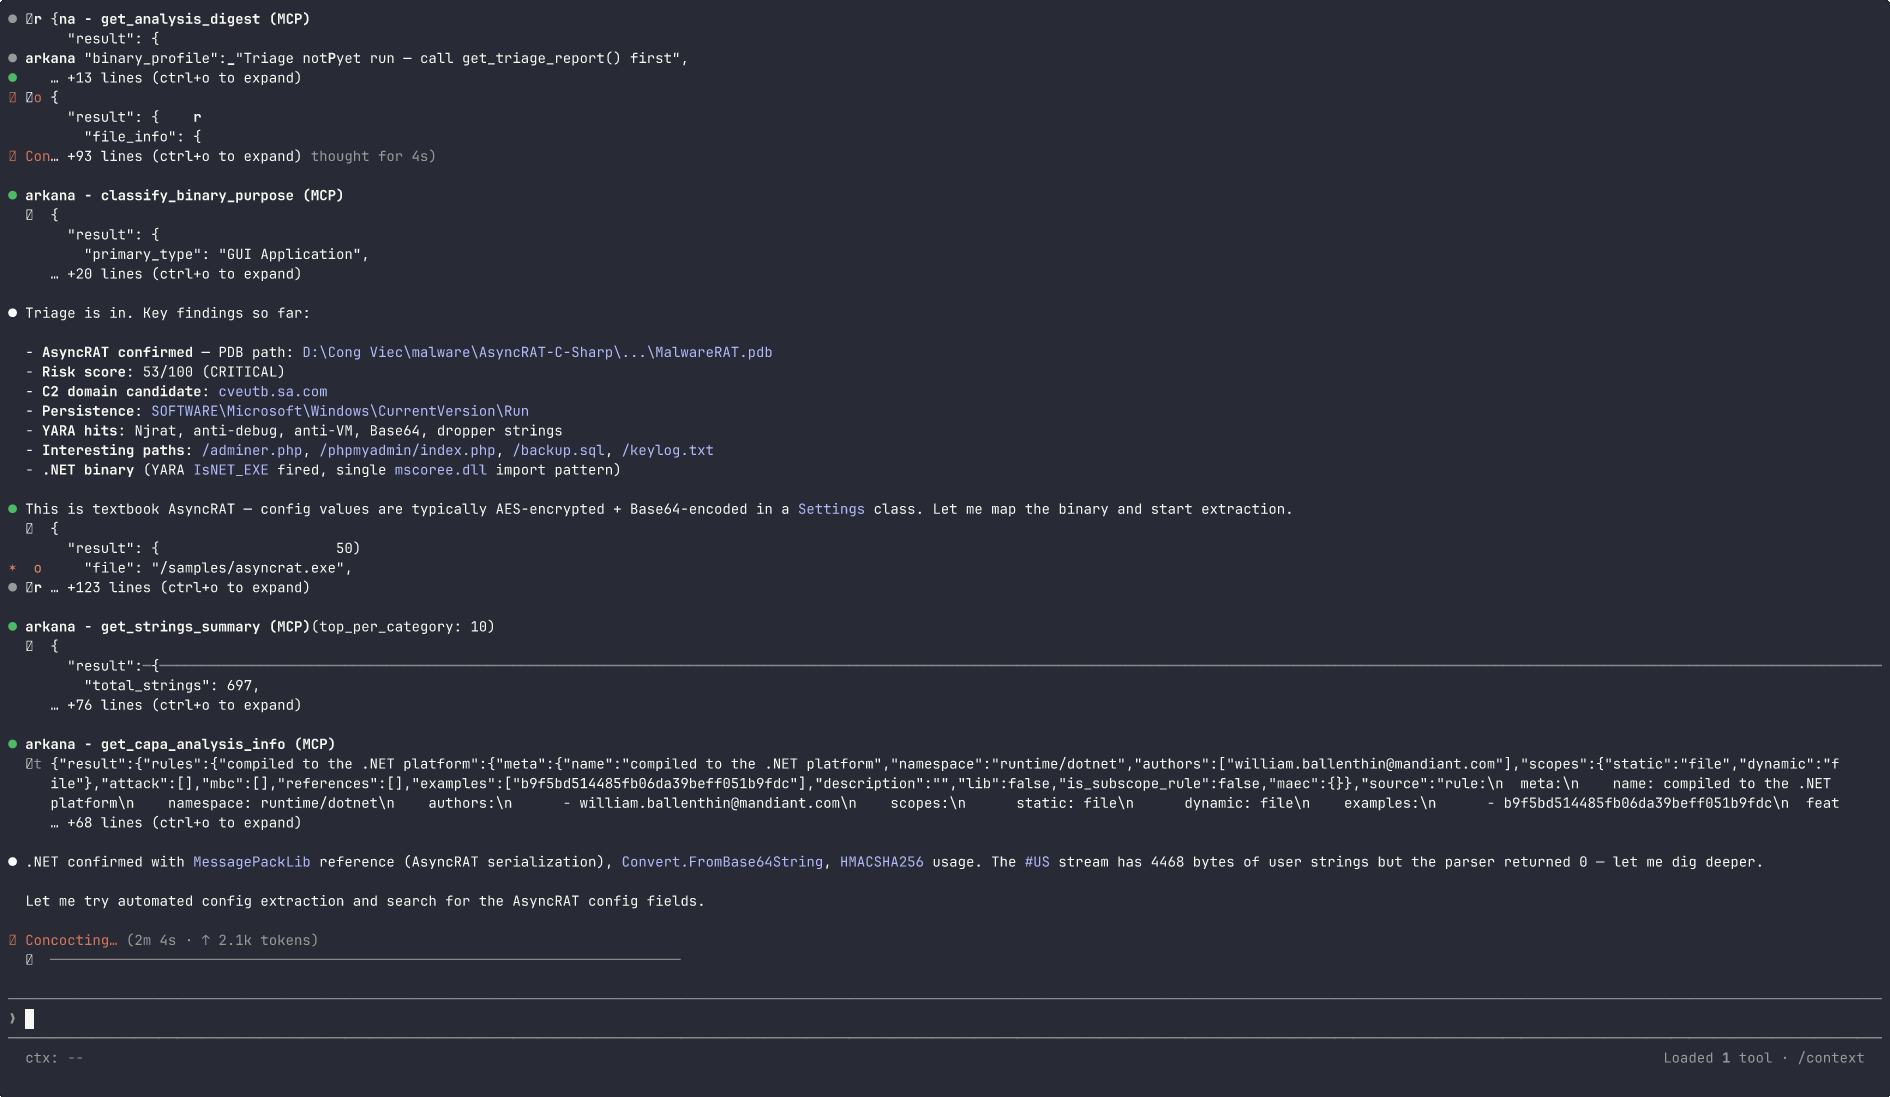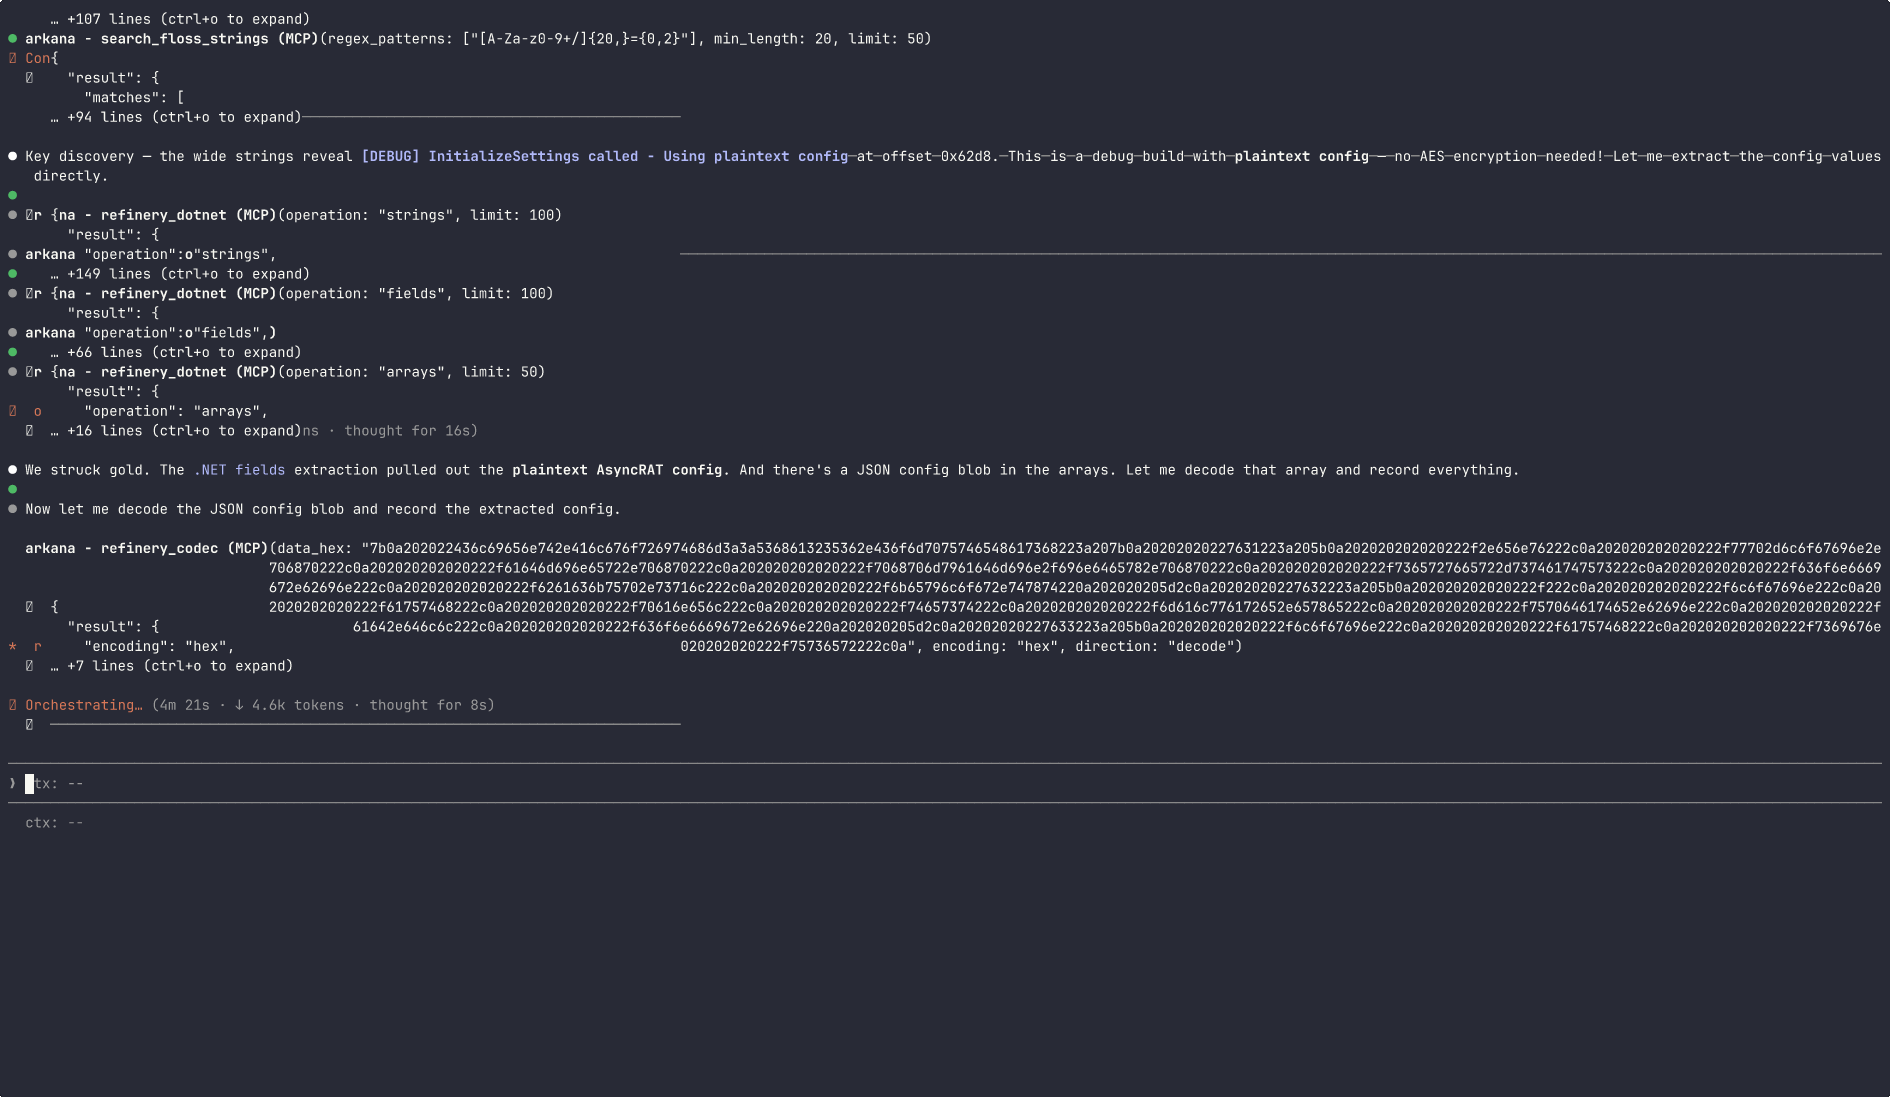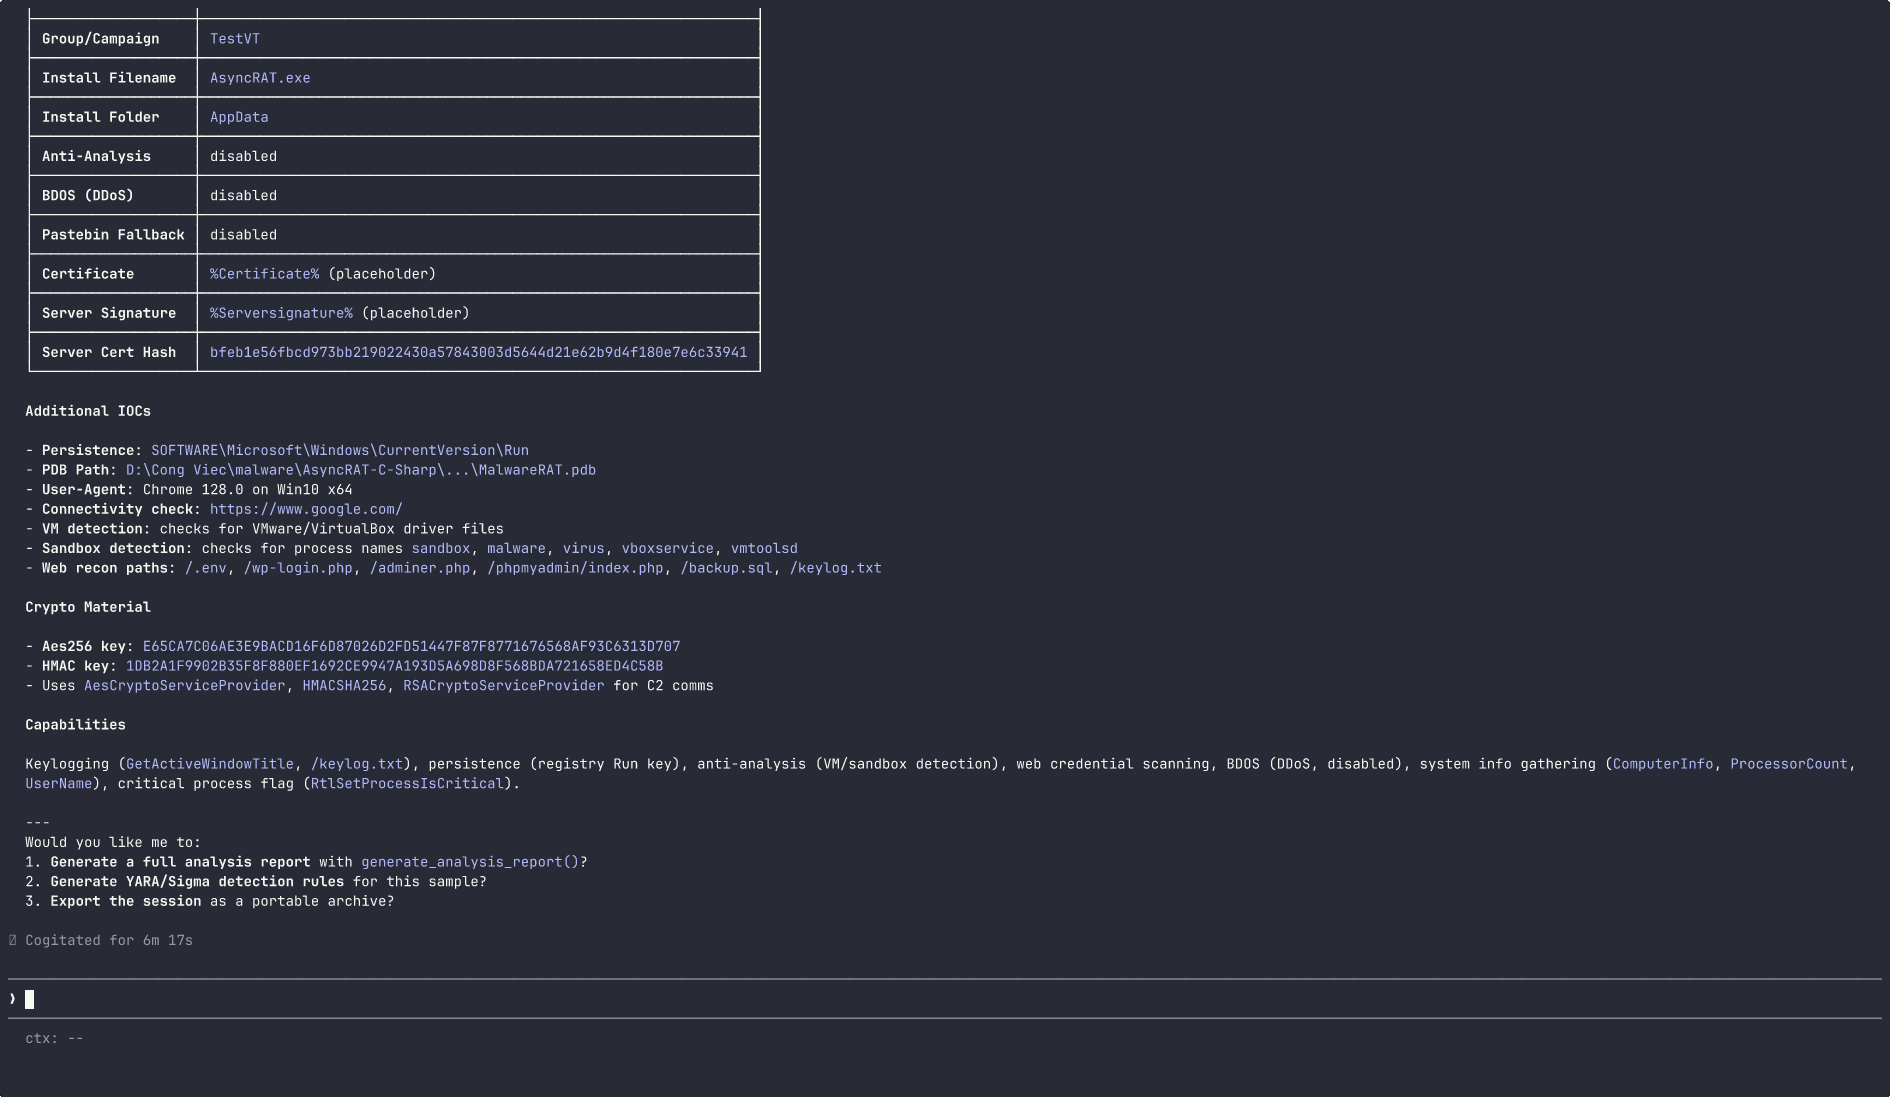
> *"Analyse asyncrat.exe and tell me what it does"*
From a single prompt, Arkana opens the binary, triages it (CRITICAL -- 43/72 ),
extracts the C2 server (cveutb.sa.com), identifies AES-256 encrypted communications via
MessagePack, maps 12 MITRE ATT&CK techniques, detects anti- for //
Sandboxie, finds the persistence mechanism (Registry Run key), and recovers the operator's
PDB path re a threat actor.
See the full report.
> *"Step through the unpacking stub and show me what it decrypts"*
Arkana starts an interacti session, sets breakpoints on and , steps through the decryption loop, snapshots state before and after, diffs the memory regions, and dumps the unpacked payload -- all driven by natural language.
!Arkana analysing AsyncRAT
Arkana is a Model Context Protocol (MCP) server that gives Claude Code (or any MCP client) 308 analysis tools -- decompilation, symbolic execution, interacti debugging, data-flow analysis, YARA/capa/FLOSS signatures, Binary Refinery data transforms, Qiling/Speakeasy emulation, .NET deobfuscation, function similarity matching, and a real-time web dashboard -- so you can in PE, ELF, Mach-O, .NET, Go, Rust, and shellcode samples by describing what you want to know. No Ghidra scripts, no CLI flags, no context-switching between a dozen tools. Just results.
---
Why Arkana
The problem: Malware analysis means juggling Ghidra, IDA, CyberChef, YARA, and a dozen other tools -- each with its own interface, scripting language, and learning cur a single sample might mean switching between 5-10 tools, manually correlating findings across disconnected workflows.
Arkana eliminates this by putting 308 specialised analysis tools behind a single AI-dri -- the equi of an entire malware lab in one MCP server. Describe what you want to know in natural language and the AI orchestrates the right tools automatically.
What makes it different:
memcpy and an indirect call, it recognises the shellcode injection pattern, renames the function to inject_shellcode, and suggests in the source buffer.Who benefits:
---
Key Features
transfer_annotations carries your analysis to . Includes whole-binary triage, confidence scoring, and false-positi--brief-descriptions trims tool descriptions to first-paragraph summaries, reducing tool listing size by ~60% for clients without tool searchHow It Compares
| | Arkana | Ghidra | IDA Pro | CyberChef |
|---|---|---|---|---|
| AI reasoning | Native | No | No | No |
| Decompilation | Angr (multi-arch, batch) | Ghidra Decompiler | Hex-Rays ($$$) | No |
| Function similarity | BSim-style cross-binary | BSim (Java) | BinDiff/Lumina | No |
| Data transforms | 200+ | Manual scripting | Manual scripting | 300+ (manual) |
| Emulation | Speakeasy + Qiling | Limited | No | No |
| Interacti | 29-tool step debugger | Manual | Manual | No |
| Auto-enrichment | Background triage on open | No | No | No |
| Web dashboard | Real-time, 14 pages | No | No | No |
| Learning curve | Natural language | Months | Months | Moderate |
| Cost | Free & open source | Free | $1,800+/yr | Free |
Arkana complements rather than replaces Ghidra/IDA -- see Scenarios & Comparisons for detailed analysis.
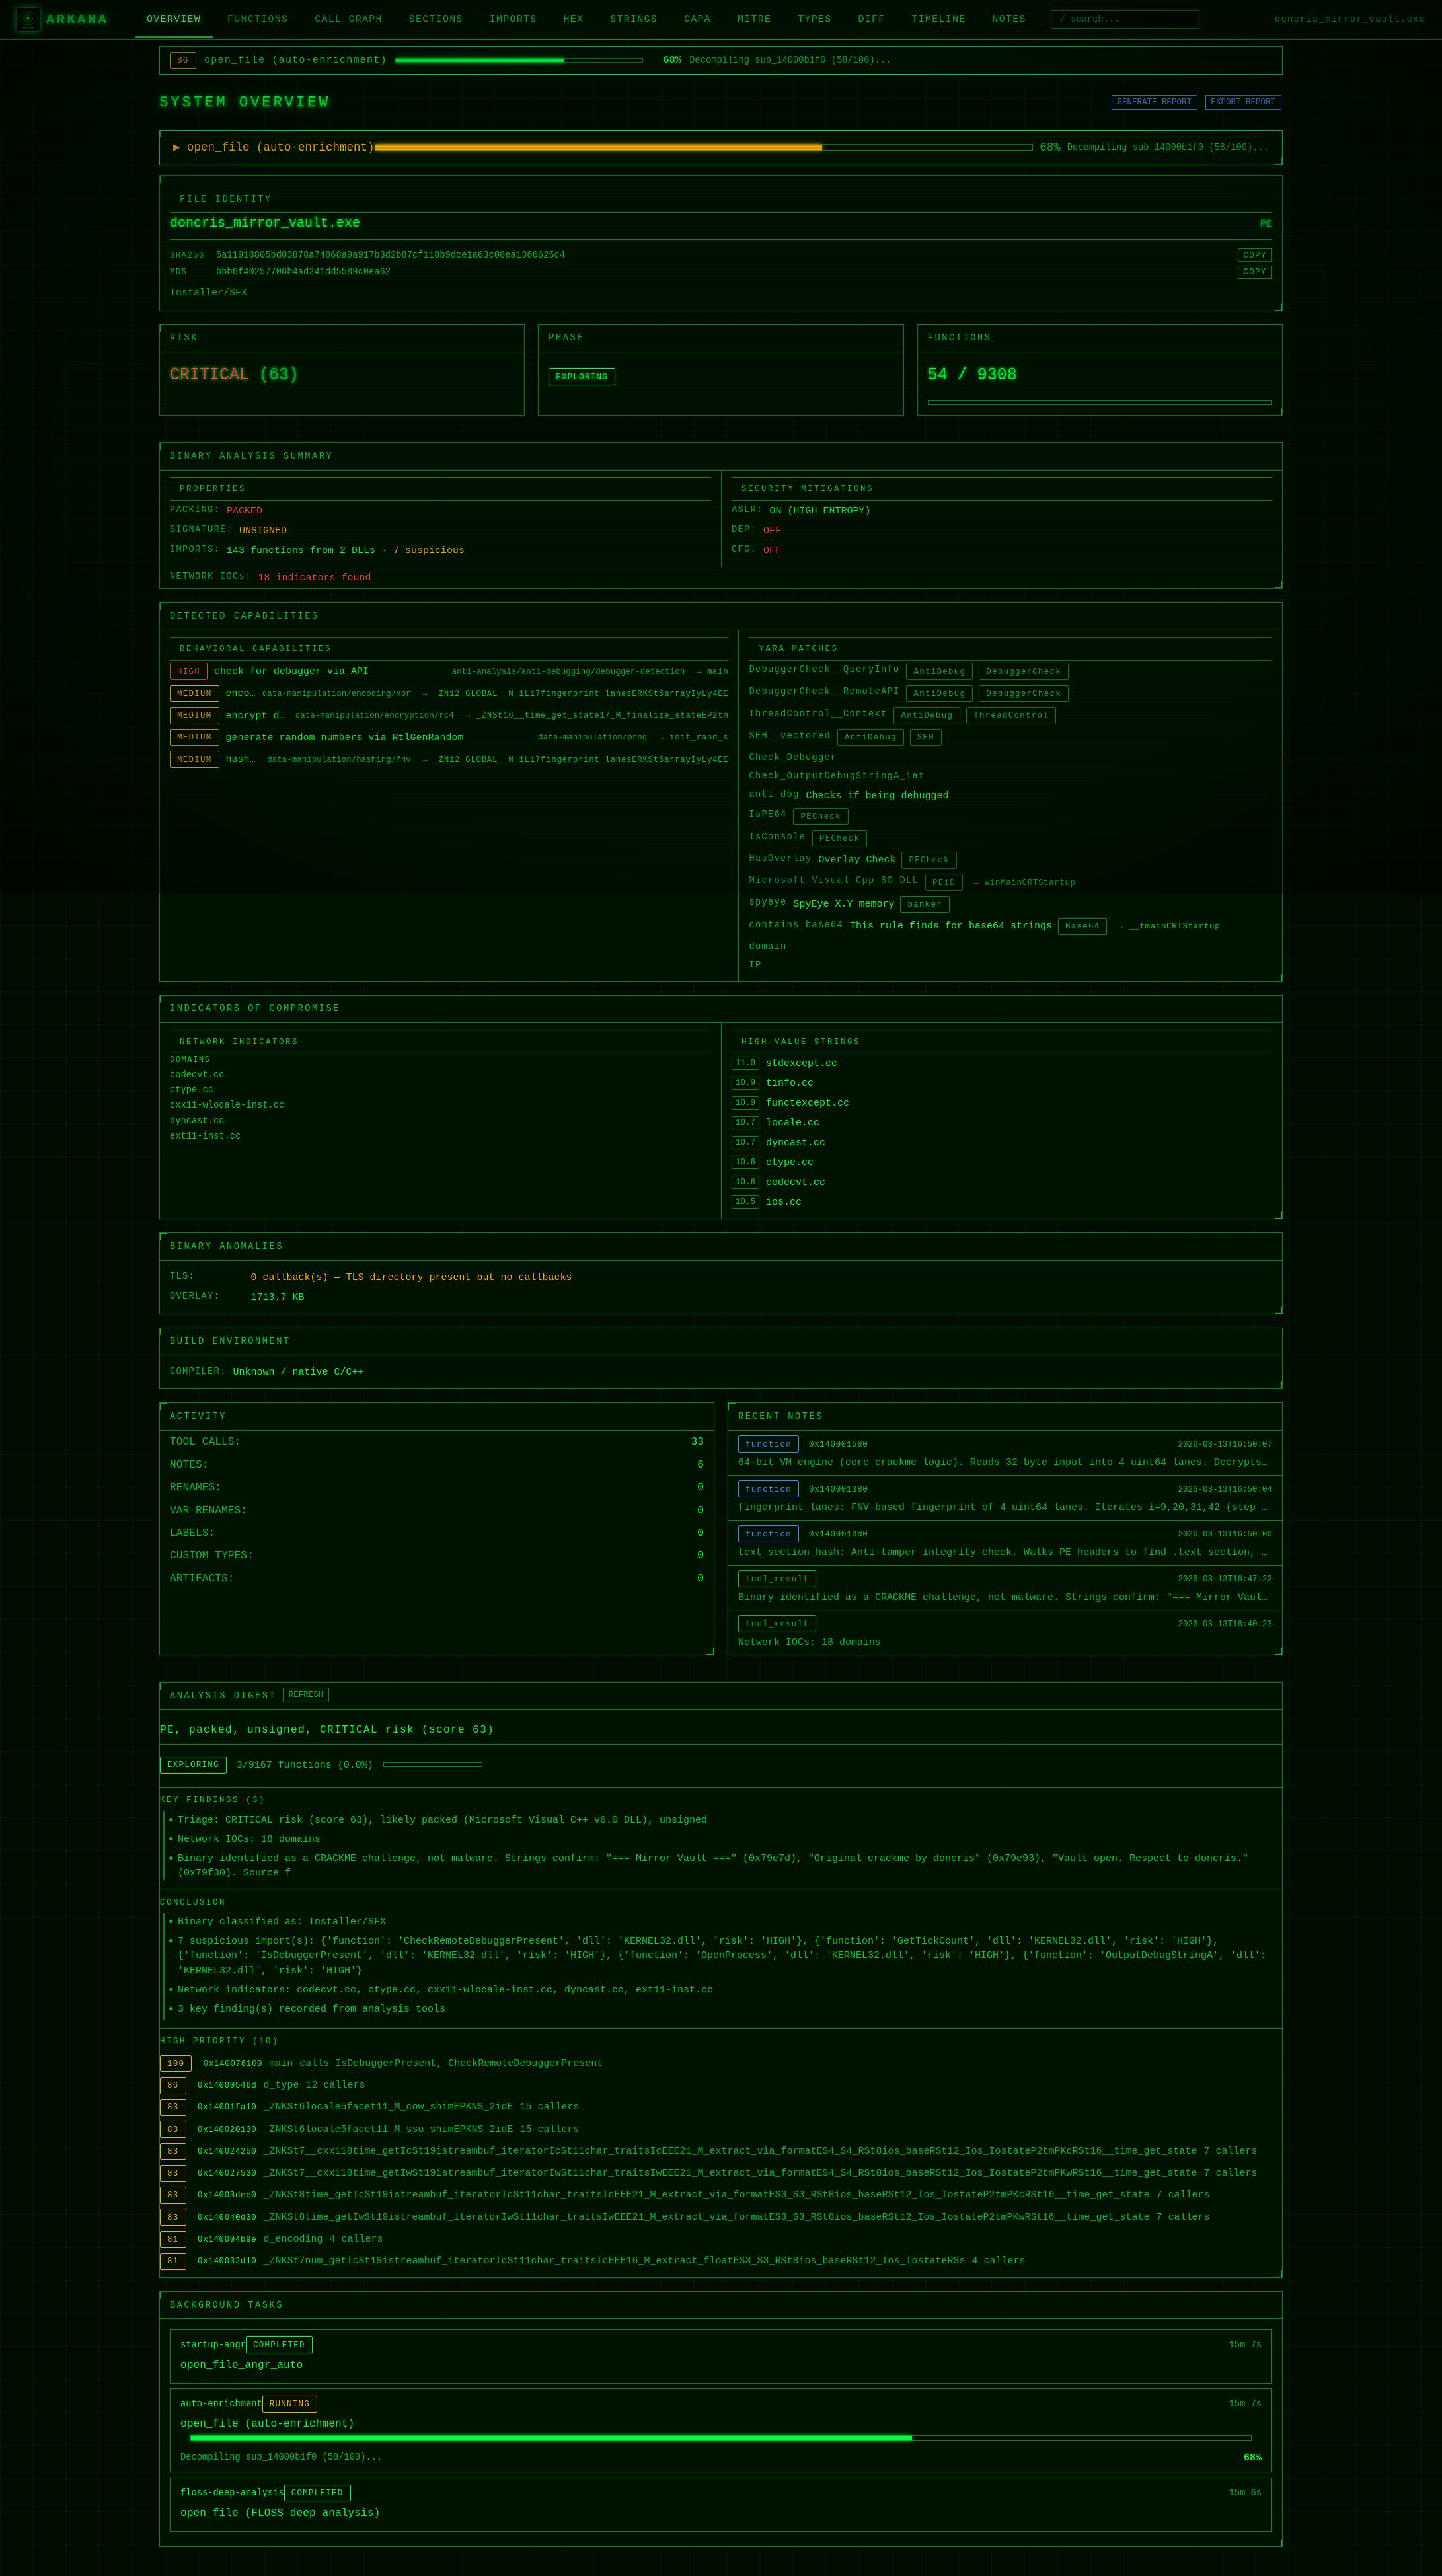
Web Dashboard
Arkana includes a real-time web dashboard that launches automatically on port 8082. It provides a companion to the AI-dri, letting you observe and interact with the in as it happens.
!Arkana Dashboard O
The dashboard uses token-based authentication (persisted to ~/.arkana/dashboard_token). Access URL with token is printed at ser. See the Dashboard Gallery for screenshots of all views.
---
Example Reports
Every report below was generated from a single prompt: *"Analyse this binary and tell me what it does."*
| Report | Sample | Highlights |
|--------|--------|-----------|
| Trojan.Delshad BYO | Multi-stage dropper | Payload carving, attack chain diagram, 12 ATT&CK techniques |
| LockBit 3.0 Ransomware | Packed ransomware | Entropy analysis, packing detection, stub extraction |
| AsyncRAT .NET RAT | .NET RAT | C2 config extraction despite obfuscated metadata |
| StealC Info Stealer | Credential stealer | 32 capa rules, browser/Steam targeting, crypto toolkit |
| Multi-Stage Loader | Chinese APT RAT | 5-stage unpacking, custom ARX cipher re, C2 config extraction |
| Brute Ratel C4 Badger | Commercial C2 implant | PIC shellcode tracing, RC4 unpacking, C2 config extraction, 17 ATT&CK techniques |
| CrackMeZ3S CTF Challenge | PELock 6-key crackme | Interacti with IAT patching, code-ca injection, encrypted blob decryption, manual XOR cipher re, MD5 hash cracking |
| Ternary Trap Neural Crackme | Neural network password lock | Custom NLI2 format re, ternary MLP reconstruction, SIMD assembly type discovery (c), autoregressi, DFS password search |
| ACRStealer Go Loader | Go-compiled info stealer | Same-day Malware Bazaar sample, Go pclntab parsing, custom 5-stage cipher re, PEB-walking API e, zero static IOCs, encrypted payload extraction |
| SalatStealer 3-Layer Stealer | 3-layer Go stealer | AES-256-CBC payload decryption, UPX 5.02 LZMA manual decompression, Go module mapping, 16 browsers + 23 wallets + LSASS dump, dual Defender e, DoH C2 |
| StealC v2 7-Layer AutoIt3 Loader | 7-layer process hollowing loader | IExpress SFX → batch deobfuscation → PE fragment reassembly → RanRot PRNG decryption → 41-API process hollowing → RC4 + LZNT1 payload extraction → StealC v2 PE with encrypted C2 config, builder path, and credential targets |
| Elysium RAT (SheetRAT) | .NET plugin-based RAT | Same-day MalwareBazaar sample, custom 2-alphabet substitution cipher, 313 C# files recovered, AMSI/ETW patch bytes extracted, plugin-framework architecture with registry DLL storage, dual C2 with Dead Drop Resolver |
| CrySome RAT | .NET modular RAT | 124 C# files decompiled, 5-layer persistence with factory reset survival, BSOD-on-kill self-protection, 5- A targeting 114+ products, HVNC for 6 browsers, DLL-injection credential theft, mutual watchdog processes |
| MBA-Obfuscated WinHTTP RAT | Same-day Malware Bazaar RAT | Full C2 protocol re (4 commands, protocol, Cloudflare bypass), Mixed Boolean-Arithmetic obfuscation hiding XOR crypto, Base64+XOR encrypted C2, download-and-execute (EXE/DLL/custom), 27 anti-analysis techniques, embedded Chromium form injection, system profiling with author misspelling fingerprint |
---
How Analysis Works
Arkana follows a structured, e methodology -- the same phased workflow a professional malware analyst uses, orchestrated automatically across 308 tools. Every claim cites specific tool output, indicators are treated as leads (not conclusions), and the AI cannot attempt decryption without first decompiling the function that performs it.
Read the full methodology with annotated AsyncRAT walkthrough →
---
Get Started in 4 Commands
Arkana works with Claude Code and any MCP-compatible client. The fastest way to get running with Claude Code and Docker:
Then in Claude Code, use the /arkana-analyse skill to get the best results:
Or just ask a question directly:
There's also an /arkana-learn skill -- an interacti engineering tutor that teaches you binary analysis hands-on using Arkana's tools.
For other MCP clients, local Python installation, and detailed configuration, see the Installation Guide.
---
Demos
AsyncRAT analysis -- single prompt to full triage, C2 extraction, and MITRE ATT&CK mapping:
!Arkana analysing AsyncRAT
<sub>Interacti: asciinema play docs/demos/demo-asyncrat.cast</sub>
Multi-phase in -- deep analysis with decompilation, emulation, and structured findings:
!Arkana deep analysis
<sub>Interacti: asciinema play docs/demos/demo-analysis.cast</sub>
---
Documentation
| Document | Description |
|----------|-------------|
| Installation Guide | Docker, local, and minimal installation; modes of operation; multi-format binary support |
| Analysis Methodology | Eight-phase analysis pipeline, tool-by-tool walkthrough, decision logic, built-in guardrails, annotated AsyncRAT example |
| Claude Code Integration | Setup via CLI and JSON config; analysis and learning skills; typical workflows and example queries |
| Configuration | API keys, analysis cache, and command-line options |
| Tools Reference | Complete catalog of all 308 MCP tools organised by category |
| Binaries | Analysing /Themida/Enigma binaries with Frida DBI scripts; four-stage pipeline |
| Scenarios & Comparisons | Se analysis walkthroughs; Arkana , IDA Pro, CyberChef |
| Architecture | Package structure, design principles, pagination and result limits |
| Security & Testing | Path sandboxing, security measures, testing and CI/CD |
| Web Dashboard | Real-time analysis dashboard on port 8082; function triage, call graph, timeline, notes |
| Qiling Rootfs Setup | Windows DLL setup for Qiling cross-platform emulation |
| Dependencies | Library dependencies and optional component details |
| Future Impro | Roadmap and planned enhancements |
| Contributing | Contribution guidelines and de workflow |
---
Contributing
Contributions are welcome! See the Contributing Guide for details.
1. Fork the repository
2. Create a feature branch (git checkout -b feature/your-enhancement)
3. Commit your changes
4. Open a Pull Request
---
Licence
Distributed under the MIT Licence. See LICENSE for more information.
---
Disclaimer
This toolkit is provided "as-is" for educational and research purposes only. It is capable of executing parts of analysed binaries (via angr emulation and symbolic execution) in a sandboxed en. Always exercise caution when analysing untrusted files. The authors accept no responsibility for misuse or damages arising from the use of this software.
---
If Arkana is useful to you, consider giving it a star -- it helps others discover the project.
Report a bug | Request a feature | Full tools reference
项目信息
开发语言:Python
Star 数:240
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Arkana - Your entire malware analysis lab, behind one AI prompt. 250+ MCP tools for binary analysis with Claude Code or other MCP展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Arkana - Arkana - Your entire malware analysis lab, behind |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:26:23 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 281 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |