 病毒分析
点击放大
PeiBackdoor - PEI stage backdoor for UEFI compatible firmware
项目说明
PEI stage backdoor for UEFI compatible firmware
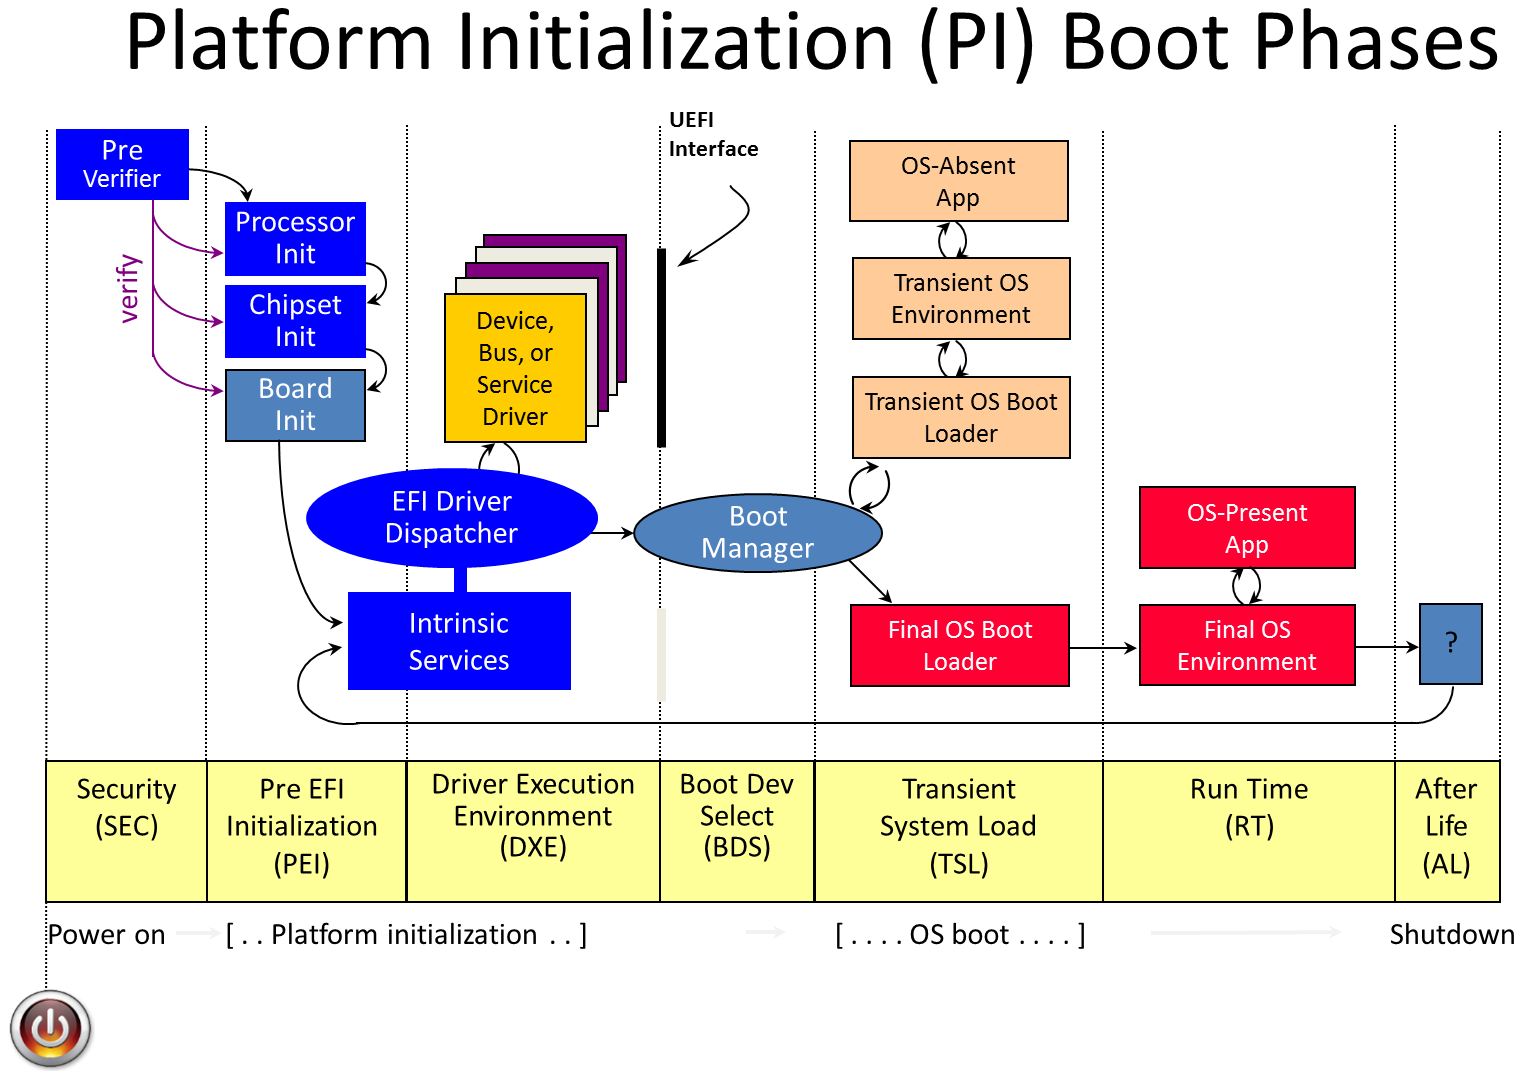
This project implements early stage firmware backdoor for UEFI based firmware. It allows to execute arbitrary code written in C during Pre EFI Init (PEI) phase of Platform Initialization (PI). This backdoor might be useful for low le with the target platform configuration when the most of the platform configuration registers are not locked yet.
<img src=" width="610">
Possible applied use cases:
* Edit of REMAPBASE, REMAPLIMIT and other host controller registers during RAM initialization to perform UMA remap attack on Intel Management Engine RAM.
* Lock TSEGMB host controller register with the junk value to make System Management Mode code to DMA attacks.
* Do other e that requires hijacking of early stage platform initialization code.
Contents <a id="_0"></a>
PEI backdoor project includes:
* PeiBackdoor.py - Python program that allows to infect raw flash images or indi UEFI PEI drivers with the backdoor code.
* PeiBackdoor_IA32.efi, PeiBackdoor_IA32.pdb - 32-bit PEI backdoor binary compiled with ACTI = IA32.
* PeiBackdoor_X64.efi, PeiBackdoor_X64.pdb - 64-bit PEI backdoor binary compiled with ACTI = X64.
* PeiBackdoor.inf - PEI backdoor project configuration for EDK2 build en.
* config.h - PEI backdoor build options.
* payload.c - Put your own PEI stage code into this source file and call it from Payload() function.
* src/ - Rest of the PEI backdoor code.
PeiBackdoor.py is using Capstone engine and pefile Python libraries, you need to install them with pip install capstone pefile command.
Building from the source code <a id="_1"></a>
payload.c file with the user supplied PEI stage payload code has the following look:
config.h file allows to change some of the backdoor settings:
To build PeiBackdoor project you need to have a Windows machine with Studio 2008 and EDK2 source code.
Step by step instruction:
1. Run Studio 2008 Command Prompt and cd to EDK2 directory.
2. Execute Edk2Setup.bat --pull command to configure build en and download required binaries.
3. Execute git clone git://github.com/Cr4sh/PeiBackdoor.git command.
4. Edit Conf/target.txt file and set ACTI property value to the O/O.dsc for 64-bit build or to the O/O.dsc for 32-bit build. Also you need to set TARGET_ARCH property value to the X64 for 64-bit build or to the IA32 for 32-bit build.
5. Edit O/O.dsc and add PeiBackdoor/PeiBackdoor.inf path at the end of the [components] section.
6. cd PeiBackdoor && build
7. After compilation resulting PE image file will be created at Build/O/DEBUG_/X64/PeiBackdoor/PeiBackdoor/OUTPUT/PeiBackdoor.efi for 64-bit build or at Build/O/DEBUG_/IA32/PeiBackdoor/PeiBackdoor/OUTPUT/PeiBackdoor.efi for 32-bit build.
Command line options <a id="_2"></a>
PeiBackdoor.py program is used to deploy PEI backdoor, it has the following command line options:
* -d <path>, --dri <path> - Infect existing PEI dri, both PE and TE formats are supported.
* -f <path>, --flash-image <path> - Infect existing UEFI flash image. Please note, this option works only for raw flash images (for example, dumped with hardware programer) but _not_ for UEFI capsules with firmware updates.
* -p <path>, --payload <path> - Path of the PEI backdoor binary for -d and -f options.
* -o <path>, --output <path> - Path of the output PEI binary or flash image for -d and -f options.
If -d option was specified - program is appending PEI backdoor binary code to the last section of PEI dri and hooks it's entry point to execute BackdoorEntryInfected() function located in src/PeiBackdoor.c file.
If -f option was specified - program is trying to find SiInitPreMem PEI driver from AMI by signature in the target flash image and hook it's entry point to execute BackdoorEntryInfected() function. This OEM specific driver runs on relatively early stage of platform initialization which allows us to execute arbitrary code from SPI flash e RAM initialization when the most of the physical memory space configuration registers like TOUUD, TOLUD, REMAPLIMIT and REMAPBASE are not configured and not locked yet. To infect other PEI dri point you also can edit SIGNATURE constant in PeiBackdoor.py to specify it's signature.
Instead of SiInitPreMem PEI dri point patch you also can use --patch-offs <offset> command line option to hook arbitrary function of some PEI driver that stored inside firmware image in uncompressed form (for example, AMI based firmware of my Intel NUC is not using any compression for all of it's PEI drivers).
Running on real hardware <a id="_3"></a>
To run PeiBackdoor.efi on your physical machine you need to obtain image of existing PEI driver:
1. Dump motherboard firmware using hardware SPI programmer.
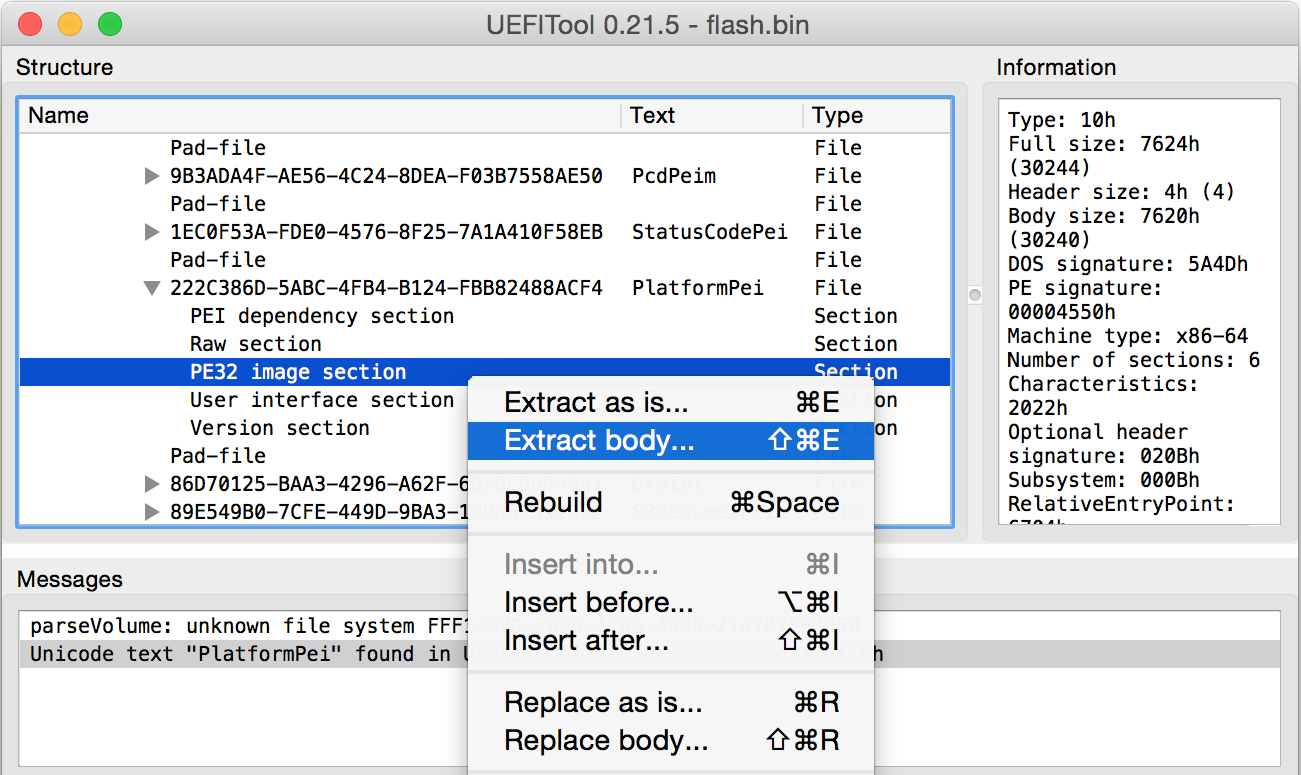
2. Open dumped flash image in UEFITool and extract PE/TE image of existing PEI driver that you want to infect with PEI backdoor:
<img src=" width="650">
... and itfect it using PeiBackdoor.py:
1. Infect extracted PE or TE image with SmmBackdoor_IA32.efi or SmmBackdoor_X64.efi depending on it's architecture: python PeiBackdoor.py -d image.efi -o image_patched.efi -p PeiBackdoor_X64.efi
2. Use UEFITool to replace original PE image with image_patched.efi, sa flash image into the file and write it to the motherboard ROM with programmer.
Unfortunately, on some machines (for example my Intel NUC) patched flash image is not working after it's modification with UEFITool, so, I implemented -f option for PeiBackdoor.py that allows to infect raw firmware image without PEI firmware volue rebuild needed. Here's example of it's usage to infect SYSKLi35.86A firmware of Skylake based Intel NUC:
Please note, that I used 32-bit PeiBackdoor_IA32.efi backdoor binary because Intel NUC, like lots of others machines with AMI based firmware, has 32-bit PEI phase code (I guess, mostly because it allows to have a bit smaller binaries than x86_64).
Running on QEMU <a id="_4"></a>
To run PEI backdoor on QEMU machine with O you have to perform the following steps:
1. Edit config.h and uncomment BACKDOOR_DEBUG_OVMF to see PEI backdoor debug messages generated with DbgMsg() function of src/debug.c in O output.
2. Execute build command from the root directory of EDK2 source code tree to build the whole O for TARGET_ARCH = X64, resulting firmware image file will be located at Build/O/DEBUG_/FV/OVMF.fd
3. Infect PlatformPei driver of EDK2 with the PEI backdoor: python PeiBackdoor/PeiBackdoor.py -d Build/O/DEBUG_/X64/O/PlatformPei/PlatformPei/OUTPUT/PlatformPei.efi -p PeiBackdoor_X64.efi
4. Rebuild O image: GenFds -f O\O.fdf -o Build\O\DEBUG_ -t -b DEBUG -p O\O.dsc -a X64 -D "EFI_SOURCE=EdkCompatibilityPkg" -D "EDK_SOURCE=EdkCompatibilityPkg" -D "TOOL_CHAIN_TAG=" -D "TOOLCHAIN=" -D "TARGET=DEBUG" -D "WORKSPACE=." -D "EDK_TOOLS_PATH=BaseTools" -D "ARCH=X64" -D "ECP_SOURCE=EdkCompatibilityPkg"
5. Run QEMU machine: qemu-system-x86_64 -bios Build/O/DEBUG_/FV/OVMF.fd -debugcon file:o.log -global isa-debugcon.iobase=0x402 -hda disk.qcow2 -net nic -m 1024 -gdb tcp:127.0.0.1:1234
6. Monitor PEI backdoor debug messages in the new terminal window: tail -f o.log | grep ') :'
Example of PEI backdoor debug output:
**
Written by Dmytro Oleksiuk (aka Cr4sh)
|
项目信息
开发语言:C
Star 数:231
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕PEI stage backdoor for UEFI compatible firmware展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PeiBackdoor - PEI stage backdoor for UEFI compatible firmware |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:27:01 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 459 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |