 病毒分析
点击放大
mobileAudit - Django application that performs SAST and Malware
项目说明
Mobile Audit
Security analysis for Android APKs, from upload to actionable findings.
Mobile Audit is a Django application for static application security testing and malware inspection. It extracts APK metadata, detects risky implementation patterns, organizes findings by se, and provides a focused workspace for review and reporting.
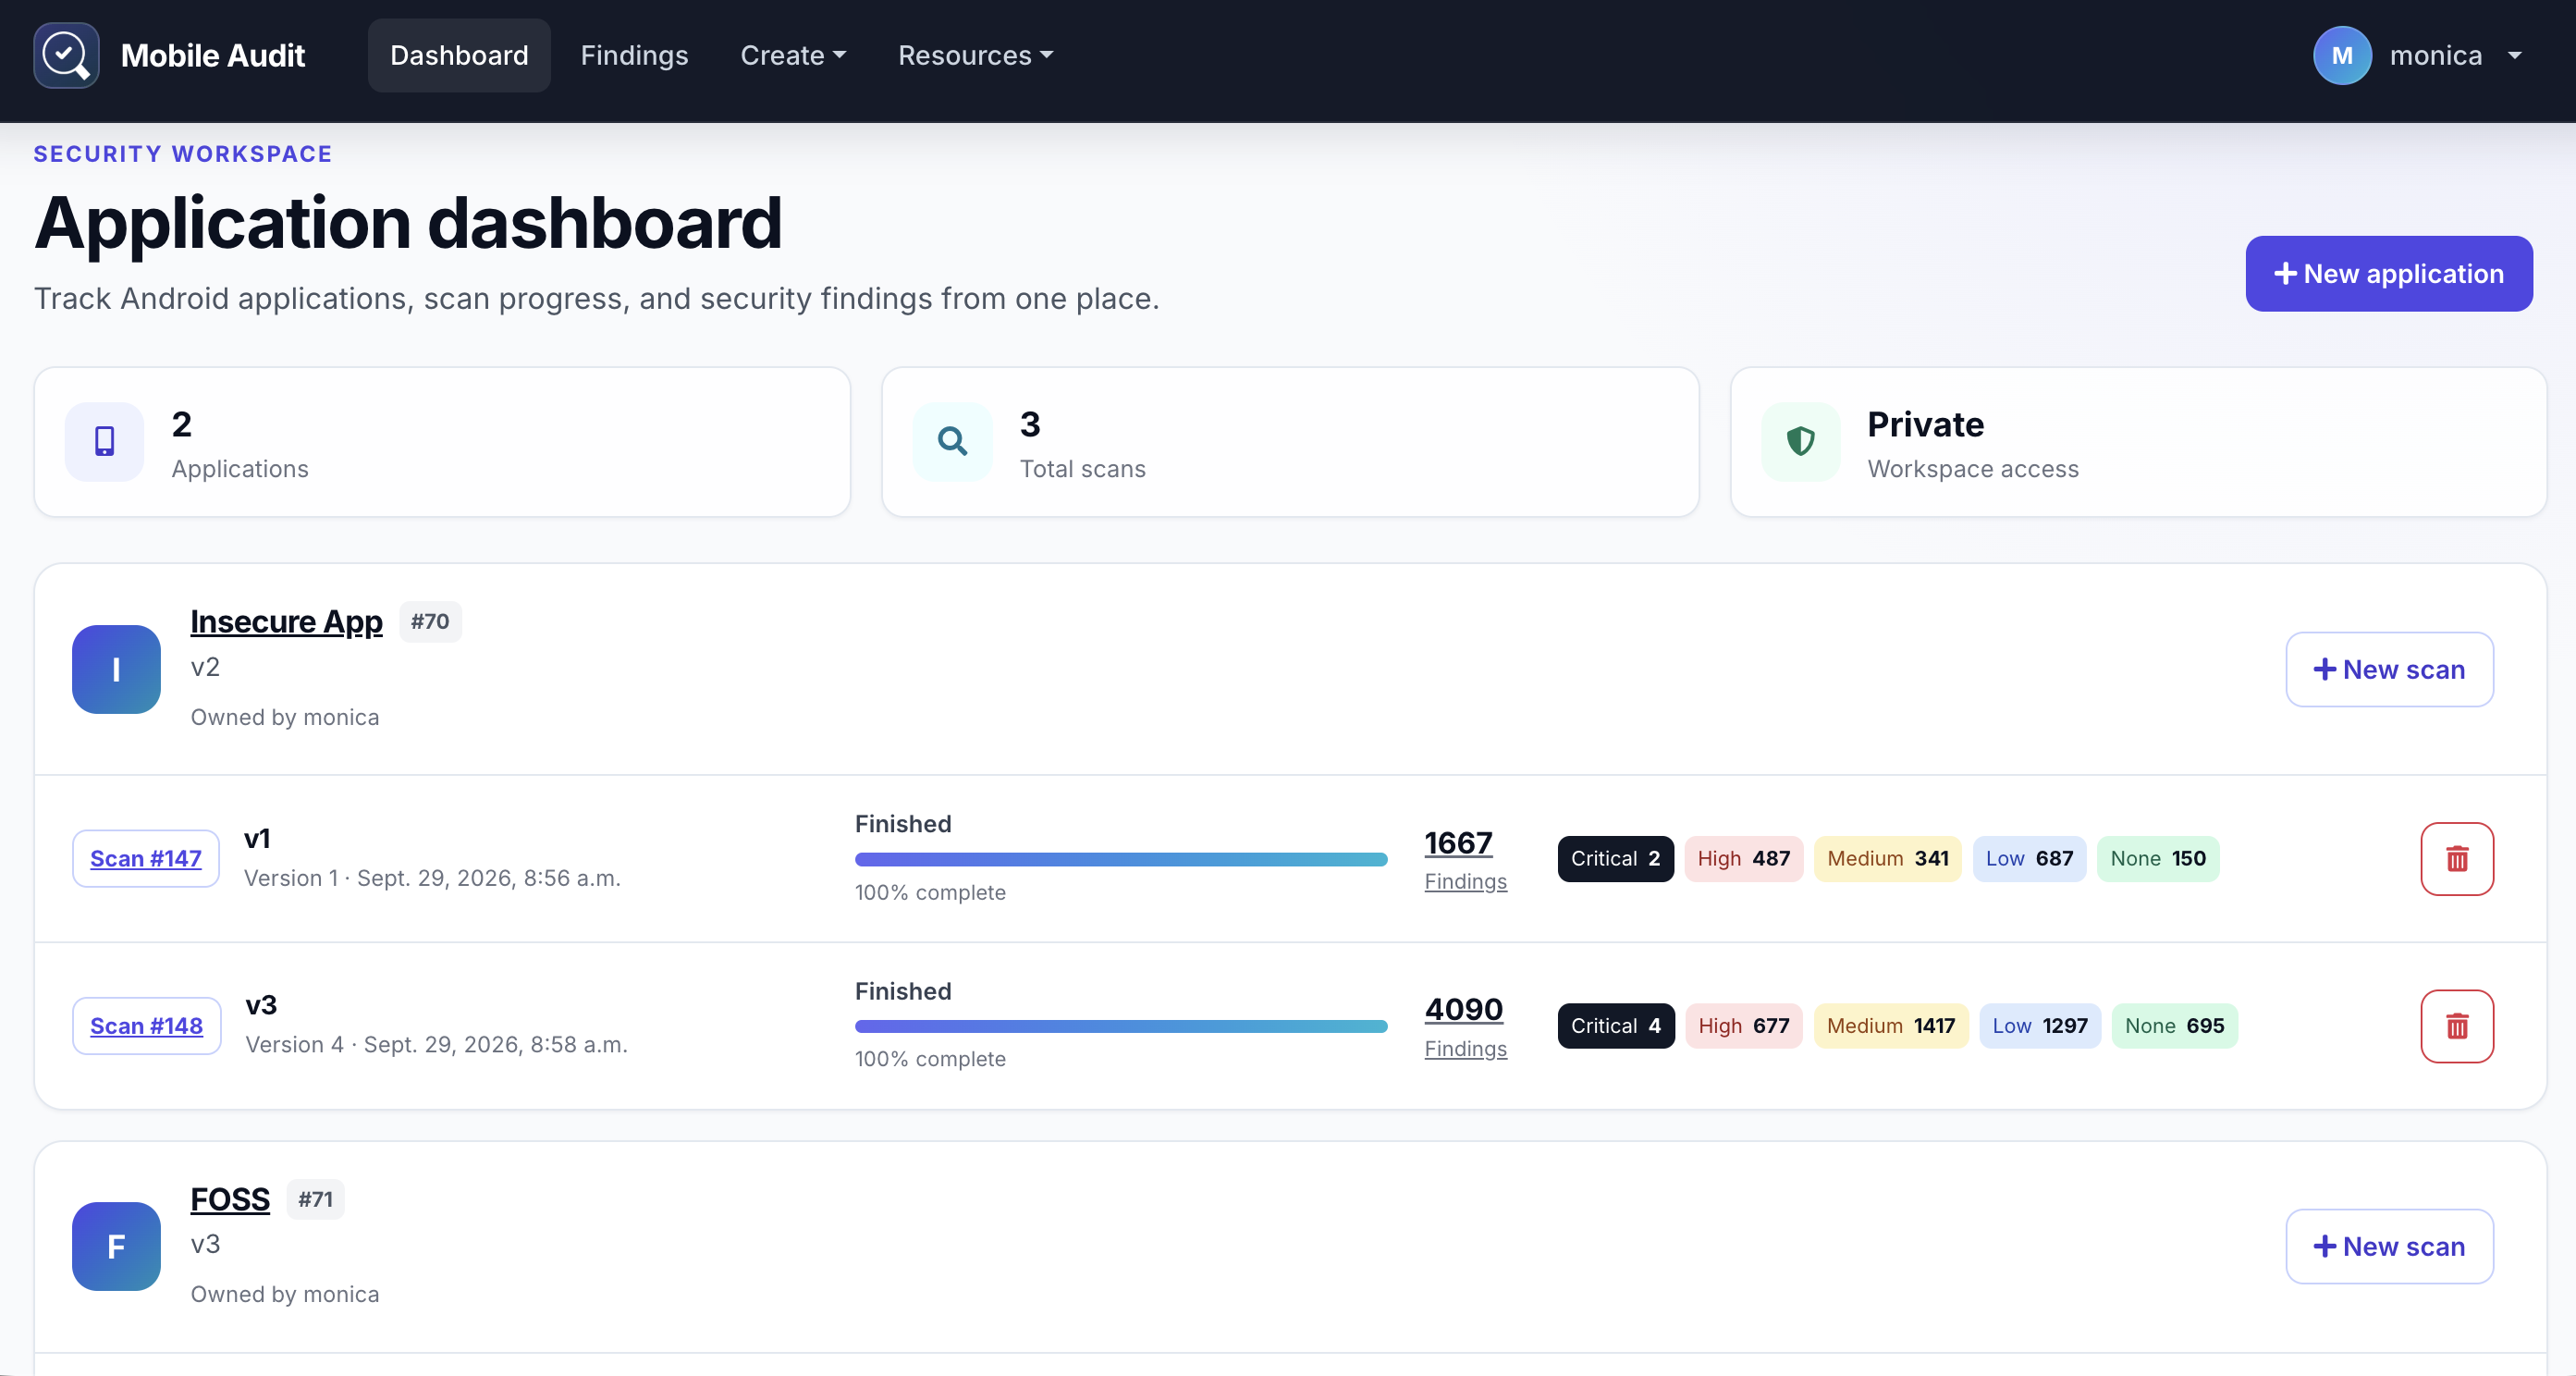
!Application dashboard with scan summaries
Get started
Docker Compose runs the complete local stack: Django, PostgreSQL, RabbitMQ, Celery, and Nginx.
~~~sh
docker compose build
docker compose up
~~~
Open when the services are ready.
To run in the background or stop the stack:
~~~sh
docker compose up -d
docker compose down
~~~
Before using Mobile Audit outside a local en, replace the example secret, database credentials, and administrator credentials in .en.
Core capabilities
| Area | What Mobile Audit provides |
| --- | --- |
| APK inspection | Application metadata, components, permissions, certificates, strings, databases, and files |
| Static analysis | Configurable SAST rules with CWE and Mobile Top 10 mappings |
| Malware checks | Domain checks against MalwareDB and Maltrail sources |
| Finding management | Se summaries, detailed e, editing, and false-positi |
| Integrations | Optional inspection and DefectDojo export |
| Reporting | PDF exports plus a token-authenticated REST API |
Interface tour
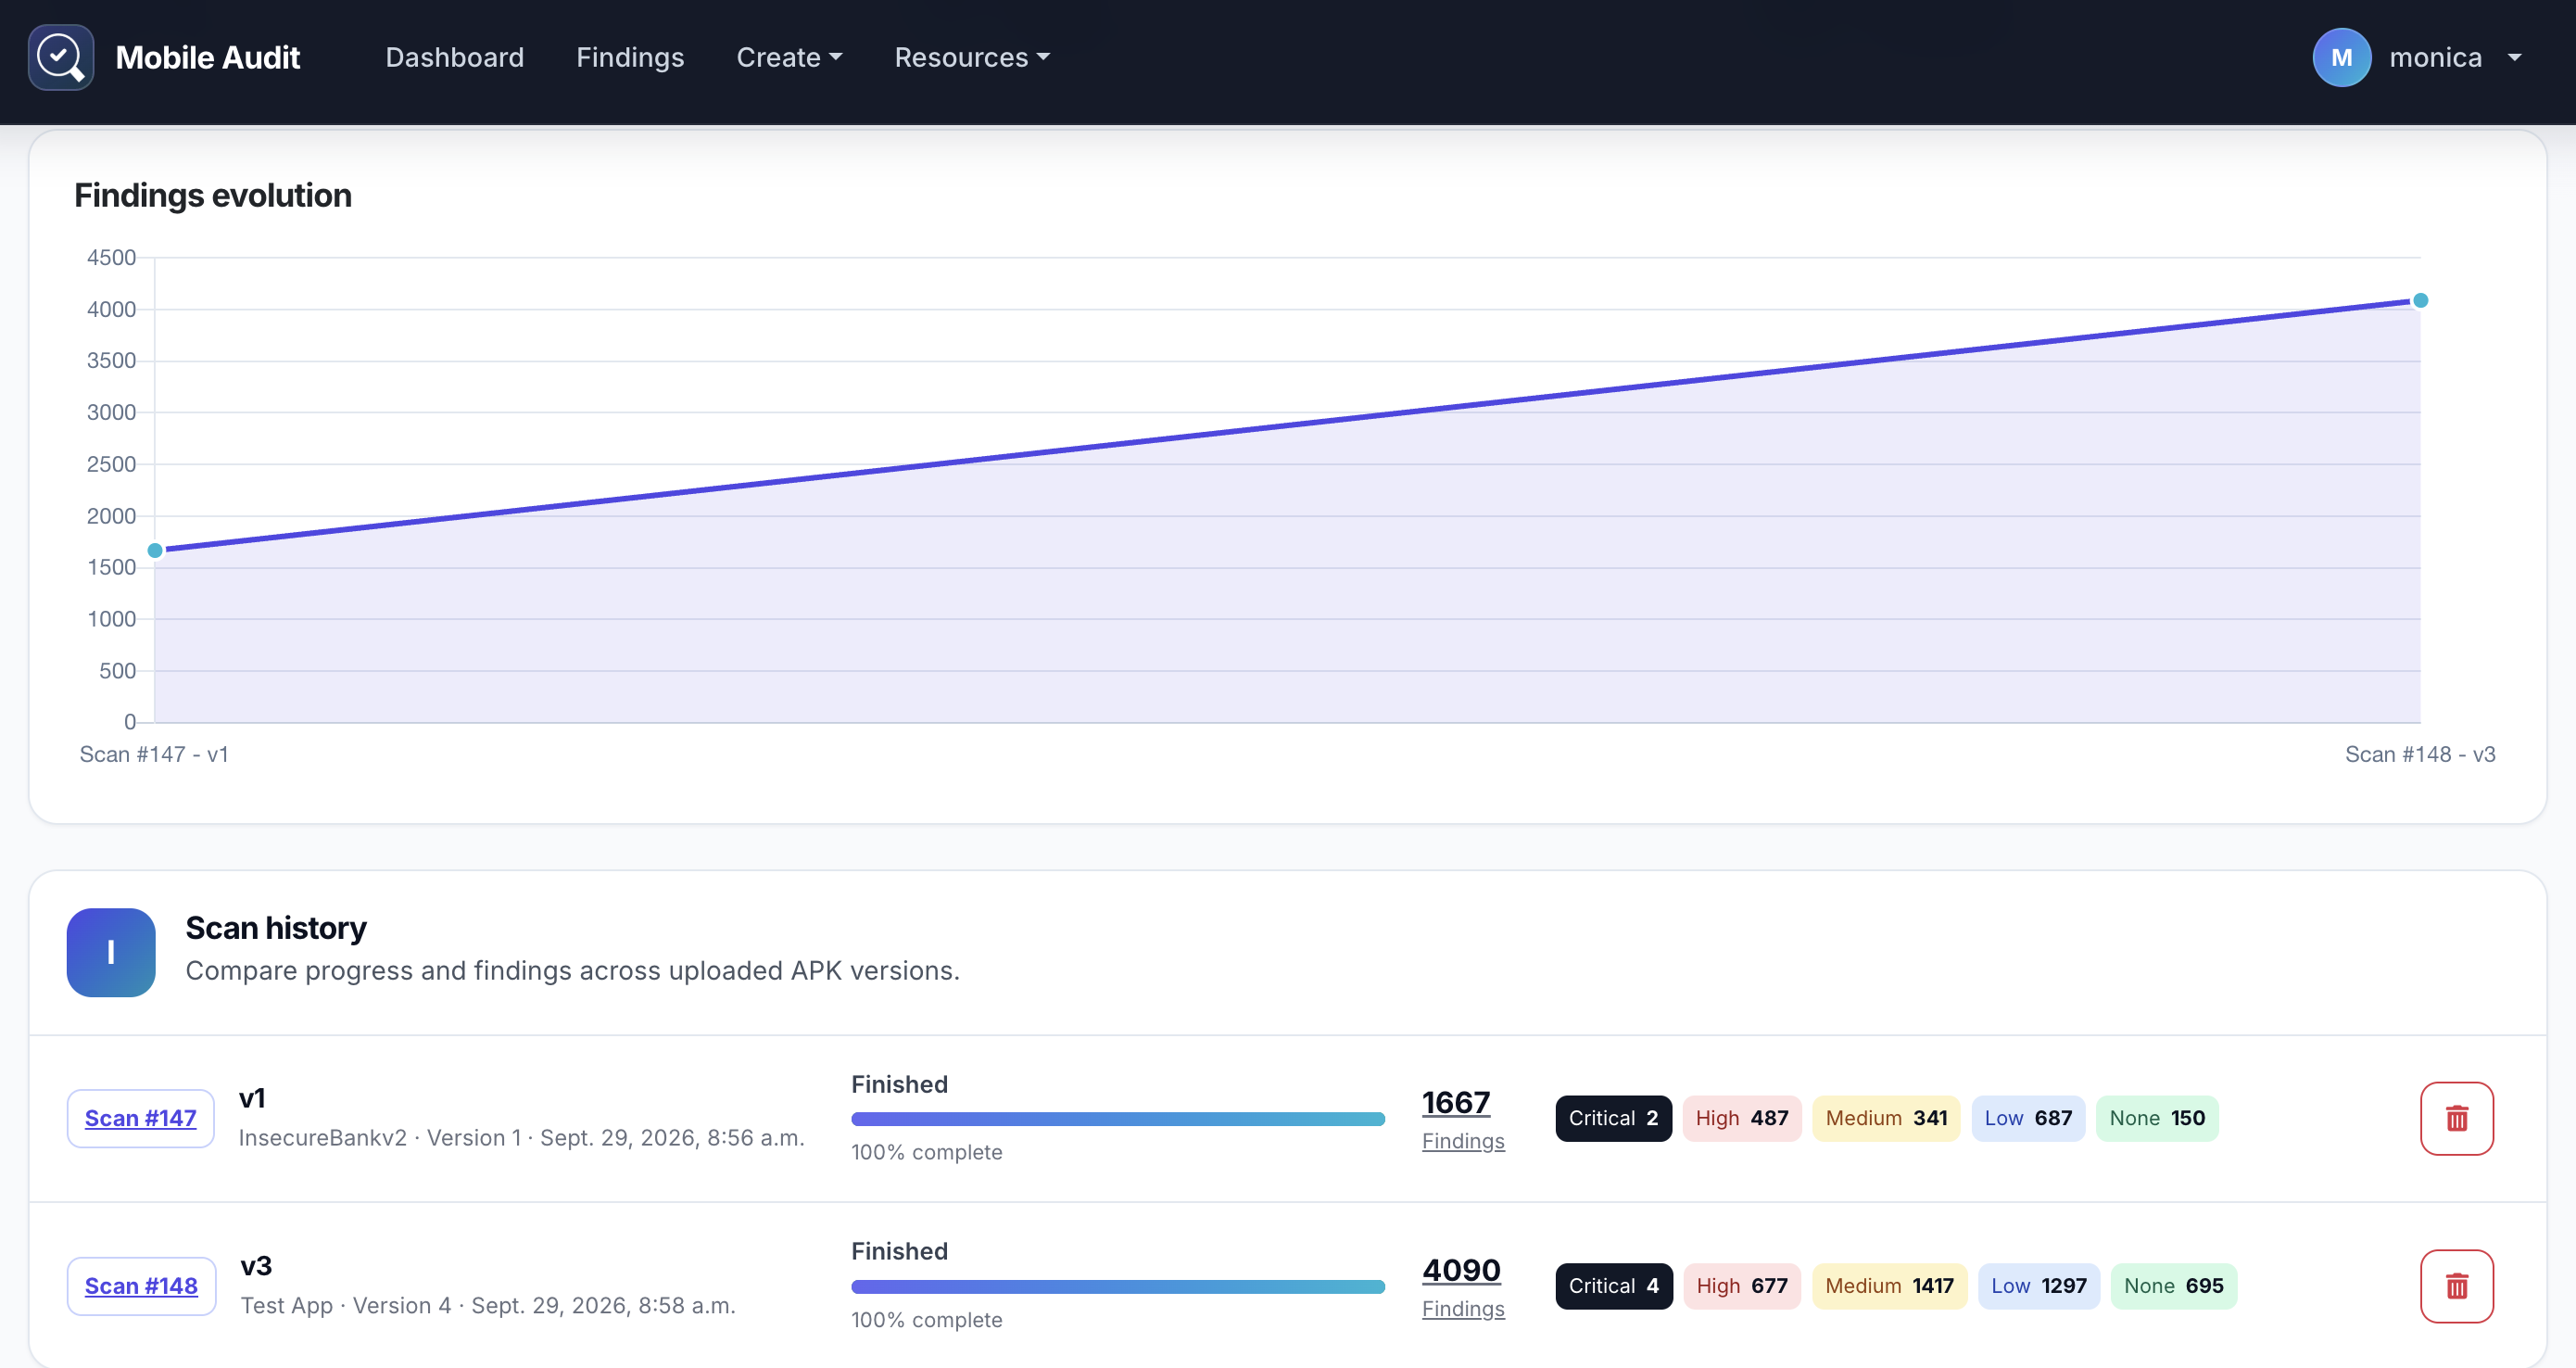
Application workspace
Review an application's scan history and compare how its finding count changes between APK .
!Application detail workspace with findings chart
Scan analysis
Move from the security summary into application metadata, permissions, components, findings, certificates, strings, files, and databases.
!Scan analysis o
The interface uses Bootstrap 5 and nati. Na, li filtering, sorting, pagination, confirmations, and scan status updates do not require jQuery.
Analysis workflow
1. Create an application workspace.
2. Upload an APK and start a scan.
3. Review se totals and inspect the supporting e.
4. Triage findings, export a PDF report, or use an integration.
Analysis rules can be enabled or disabled from the Patterns screen. Some hardcoded patterns are derived from apkleaks.
Architecture
!Mobile Audit architecture
| Service | Responsibility |
| --- | --- |
| Django 5.2 LTS | Web application and REST API |
| PostgreSQL 16 | Persistent application data |
| Celery | Background APK analysis |
| RabbitMQ 4.2 | Task broker |
| Nginx | HTTP or TLS entry point |
The application runtime uses Python 3.12. APK decompilation is provided by JADX.
API
Request a token:
~~~text
POST /api/v1/auth-token/
~~~
Authenticate subsequent requests:
~~~text
Authorization: Token <api-key>
~~~
| Documentation | Path |
| --- | --- |
| Swagger UI | /swagger/ |
| ReDoc | /redoc/ |
| OpenAPI JSON | /swagger.json |
| OpenAPI YAML | /swagger.yaml |
Optional integrations
The following features are disabled by default and configured through .en:
Enable only the services for which you ha endpoints and credentials.
TLS
Place the certificate and private key in nginx/ssl, then start the TLS configuration:
~~~sh
docker compose -f docker-compose.prod.yaml up -d
~~~
The application will be a at
For local testing, generate a one-day self-signed certificate:
~~~sh
openssl req -x509 -nodes -days 1 -newkey rsa:4096 \
-subj "/C=ES/ST=Madrid/L=Madrid/O=Example/OU=IT/CN=localhost" \
-keyout nginx/ssl/nginx.key \
-out nginx/ssl/nginx.crt
~~~
Project resources
项目信息
开发语言:Python
Star 数:228
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Django application that performs SAST and Malware Analysis for Android APKs展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | mobileAudit - Django application that performs SAST and Malware |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:27:12 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 228 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |