剑庭安
首页
黑客安全首页全部安全栏目 黑客技术黑客技术、渗透测试、漏洞利用工具与教程 安全软件安全工具、扫描器、检测与审计软件 病毒分析恶意软件分析、样本、逆向与沙箱 CTF思路CTF 题目、writeup、解题思路与工具 防护思路防御技术、加固、检测响应与蓝队 红蓝攻防红队攻击模拟、蓝队对抗、攻防演练 漏洞知识库漏洞、CVE、PoC、EXP 与安全研究
逆向|反编译
PHP源码PHP 网站源码、程序、系统 APP源码安卓/iOS APP 源码 ASP源码ASP 网站源码与程序 NET源码.NET 网站源码与系统 小程序源码微信/支付宝小程序源码 Dedecms风格模板Dedecms 织梦风格模板 Empirecms风格模板EmpireCMS 帝国风格模板 Discuz商业模板/插件Discuz 商业模板与插件 WordPress主题/插件WordPress 主题与插件 其它源码、模板其它各类源码与模板 游戏源码游戏源码与引擎项目 加密货币源码加密货币、区块链、钱包、USDT/比特币相关源码与工具 手游源码手机游戏源码、服务端、客户端与引擎项目 传奇源码热血传奇、传奇世界、复古传奇等客户端/服务端/引擎源码 页游源码网页游戏、H5 游戏、浏览器游戏源码 端游源码电脑单机游戏、PC 网游客户端/服务端源码
最新万能免驱动支持所有型号打印机下载程序 日历天气老黄历 · 每天同步真实日期与天气
站长工具站长工具 自助开通会员浏览该分类 其他资源qtziy SEO工具SEO工具 站群源码站群源码 泛程序泛程序 蜘蛛模板蜘蛛模板 蜘蛛池蜘蛛池 外链工具外链工具
搜索 自助开通会员🔓 破甲 API
登录 注册
首页 分类列表 病毒分析 hacksguard - A blazingly fas…
hacksguard - A blazingly fast, multi-threaded TUI malware analy 病毒分析 点击放大
作者:admin 发布:2026-10-05

hacksguard - A blazingly fast, multi-threaded TUI malware analy

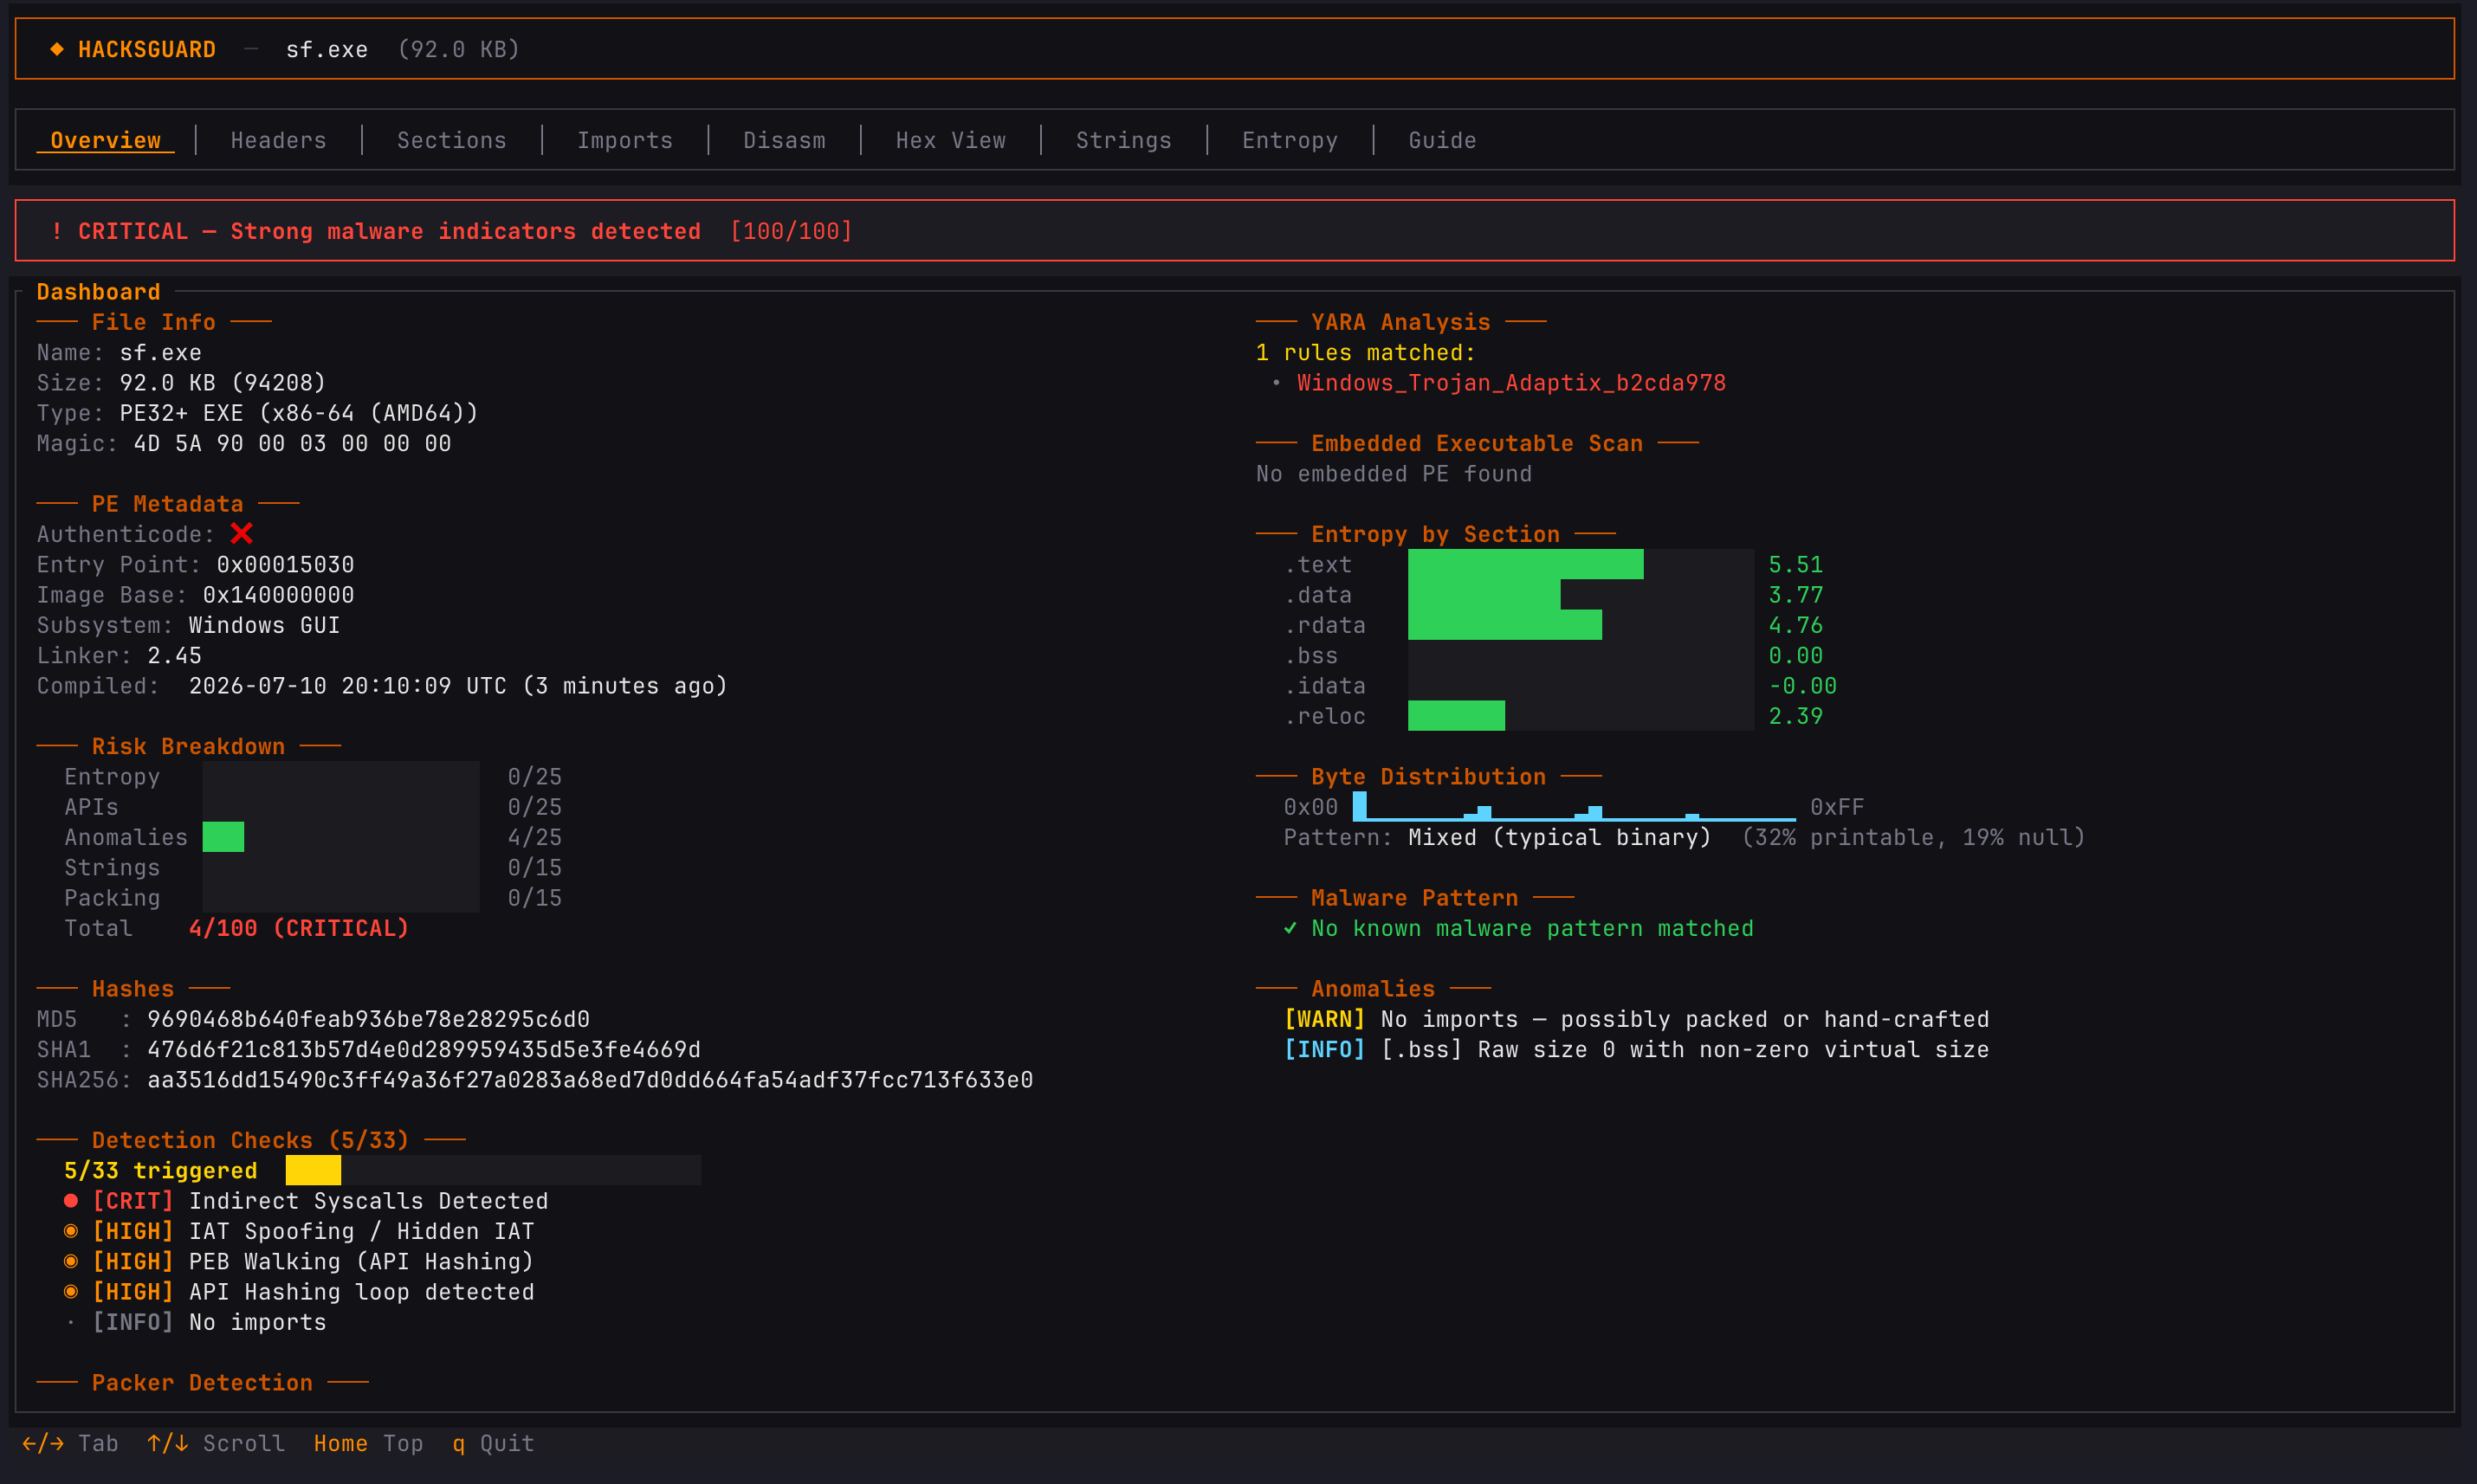
项目说明Hacksguard 0.4 - Blazing Fast TUI Malware Analysis Tool 🛡️!Rust!License!Platform!Hacksguard TUI Malware Analysis DashboardHacksguard is a blazingl…
资源可下载 免费下载 0 条讨论
会员资源
开通会员后即可下载全部资源。
登录后开通会员
会员方案
350浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-05
人工审核发布
评论区答疑

hacksguard - A blazingly fast, multi-threaded TUI malware analy

hacksguard - A blazingly fast, multi-threaded TUI malware analy

项目说明

Hacksguard 0.4 - Blazing Fast TUI Malware Analysis Tool 🛡️

!Rust
!License
!Platform

!Hacksguard TUI Malware Analysis Dashboard

Hacksguard is a blazingly fast, multi-threaded Terminal UI (TUI) static analysis tool designed for SOC analysts, threat hunters, and reverse engineers. Built entirely in Rust, it provides an intuiti for quick triage and deep inspection of Windows (PE), Linux (ELF), and macOS (Mach-O & Uni Fat) binaries right from your terminal.

🌟 Key Features

  • Blazing Fast & Multi-Threaded: The core analysis pipeline runs concurrently. This ensures zero UI latency, even when analyzing large executables.

  • Multi-Format Static Analysis: Native deep inspection of Portable Executable (PE), Linux (ELF), and macOS (Mach-O / Fat containers) formats.

  • Ad Risk Scoring: Hacksguard automatically compiles a 0-100% Risk Score based on 5 heuristic axes (Entropy, Suspicious APIs, Format Anomalies, Strings, and Packing), through an interacti chart.

  • Integrated YARA Engine: Powered by the boreal crate, Hacksguard dynamically loads local YARA rules (e.g., Elastic protections-artifacts and Neo23x0 signature-base) to detect known threats, packers, and e techniques.

  • Deep PE, ELF & Mach-O Inspection: Headers, Sections/Segments, Imports & Exports, Security Mitigations (ASLR/PIE, DEP/NX, RELRO, CodeSign, RPATHs), Mandiant Imphash, and Rich Header parsing (toolchain ID decoding & RichPE hash).

  • Authenticode Certificate Decoding: Zero-dependency ASN.1 DER and PKCS#7 parser extracting X.509 leaf certificate details (Subject, Issuer, window, Digest Algorithm, Serial Number) and flagging self-signed certificates.

  • 1-Byte XOR Payload Brute-Forcer: High-speed single-pass scanner detecting obfuscated PE binaries (MZ...PE), DOS stubs, and URLs hidden inside o or high-entropy sections.

  • Direct & Indirect Syscall Detection: Automated scanning for e techniques including x86/x64 direct/indirect syscalls (syscall, sysenter, int 0x80) and ARM64 supervisor calls (svc #0 on Linux AArch64, svc #0x80 on macOS ARM64).

  • Entropy Graph: A dedicated Entropy tab plots the Shannon entropy distribution of the file using sparklines, allowing analysts to spot encrypted or packed payloads instantly.

  • ASCII & UTF-16LE Strings: Automatically extracts and categorizes ASCII and UTF-16LE wide strings (IPs, URLs, Registry keys, commands) with li filtering (/) and category shortcuts (u/i/r/c/s/p/a).

  • Built-in Disassembler & Hex View: Inspect Entry Point instructions (x86/x64 decoded via iced-x86, ARM64 instruction word formatting with syscall highlighting) or dive into raw bytes with the Hex Dump .

  • O Detection: Automatically detects appended hidden data at the end of the binary, a technique commonly used by droppers and malicious installers.

  • Clipboard Integration (y): Instant zero-dependency copy of hashes and strings to system clipboard via ANSI OSC 52 sequences.

  • CLI Mode / CI-CD Ready: Run hacksguard --json <file> to bypass the terminal UI and export the full analysis report as a structured JSON object for SIEM/SOAR integrations.
  • 📦 Installation

    Building from source

    Make sure you have Rust and Cargo installed. Clone the repository with its submodules:

    If already cloned without submodules:

    The compiled binary will be a at target/release/hacksguard.

    Nixpkgs

    For Nix or NixOS users is a package
    a in Nixpkgs. Keep in mind that the lastest releases might only
    be present in the `unstable channel.

    🚀 Usage

    Run Hacksguard by pro the path to the executable you want to analyze:

    Keyboard Shortcuts

  • Tab / Right Arrow: Next Tab

  • Shift+Tab / Left Arrow: Previous Tab

  • Up / Down / k / j: Scroll

  • PageUp / PageDown: Fast Scroll

  • /: Interacti (li across Strings, Imports, Sections)

  • y: Copy to Clipboard (OSC 52 - copies active hash or string)

  • u / i / r / c / s / p / a: Quick category filter in Strings view (URLs, IPs, Reg, Cmd, Suspicious, Path, All)

  • Esc: Clear search / category filter (or Quit if clean)

  • q: Quit
  • Dependencies

  • ratatui & crossterm - TUI rendering

  • goblin - PE/ELF/Mach-O parsing

  • boreal - Pure Rust YARA engine

  • iced-x86` - Disassembler
  • 🔗 Related Projects

  • Elastic Protections Artifacts - YARA rules

  • Neo23x0 Signature Base - YARA rules
  • 📸 Screenshots

    O


    !O

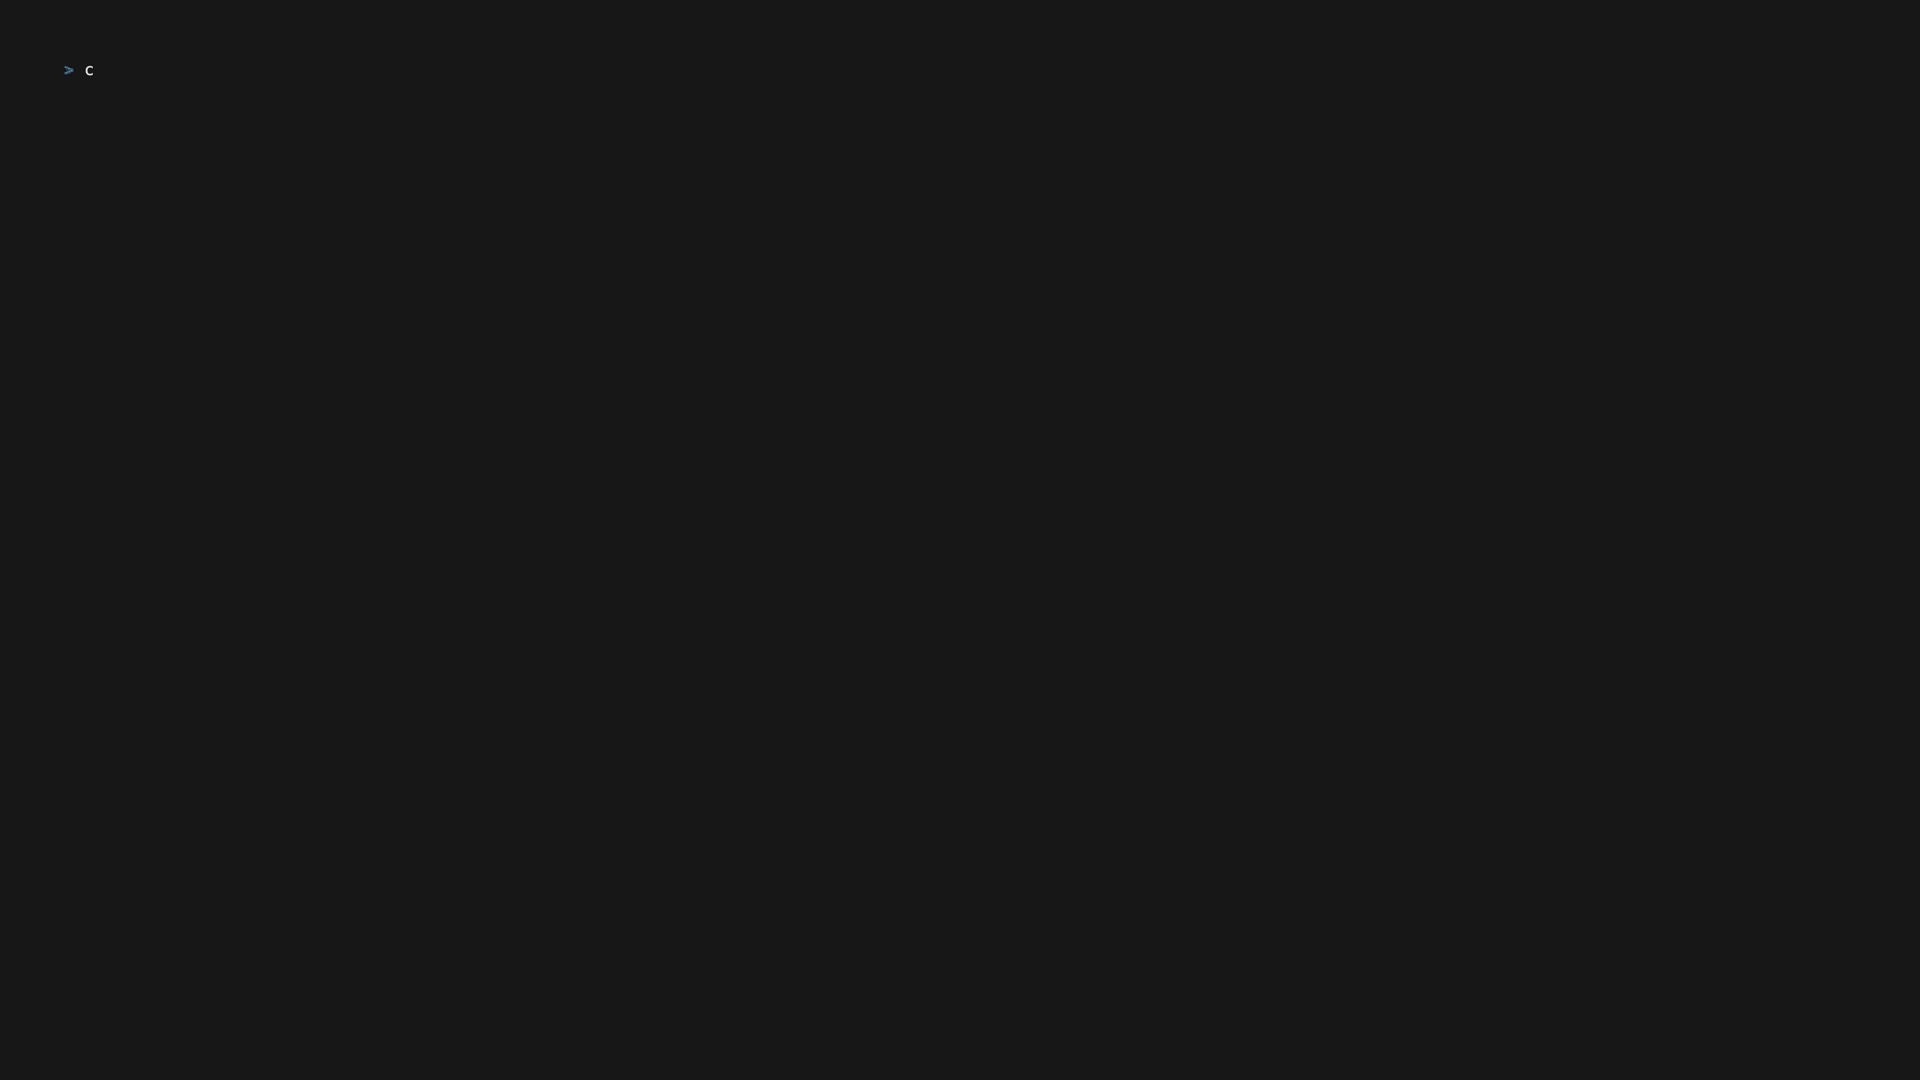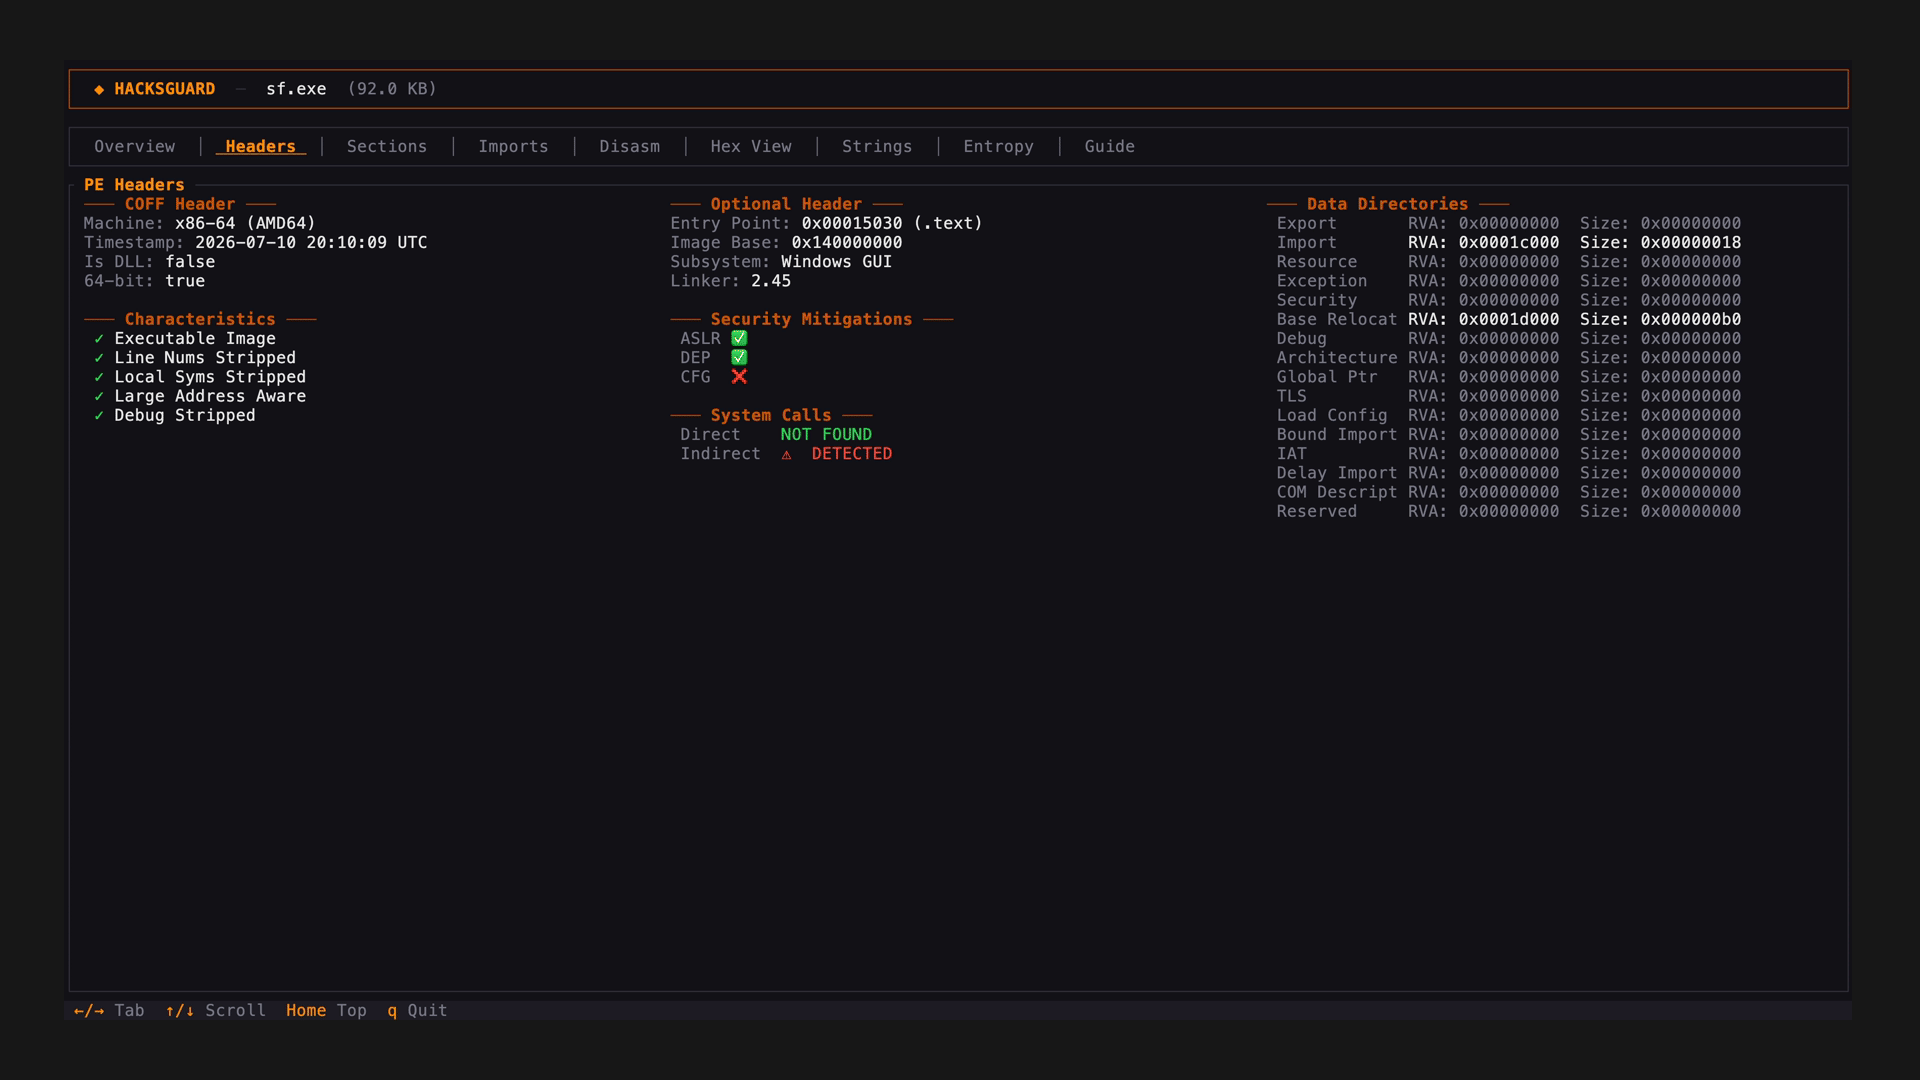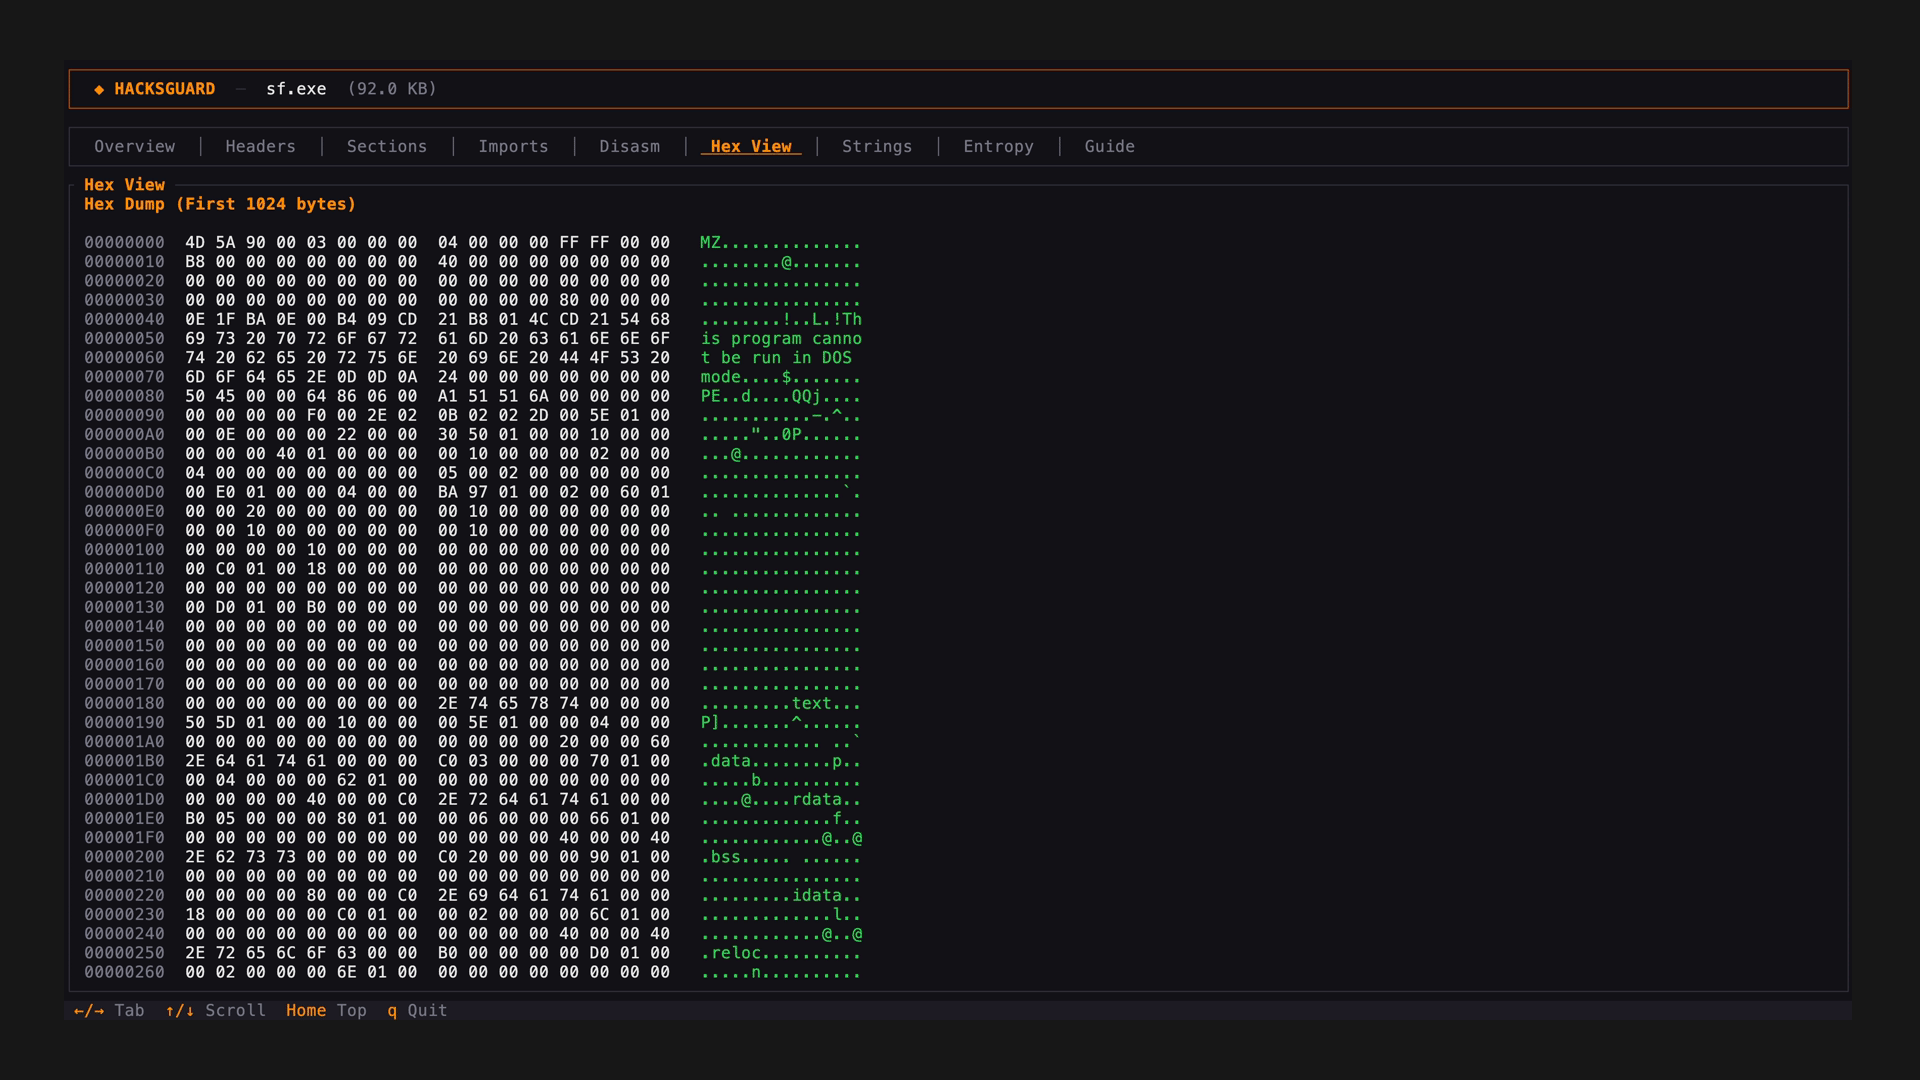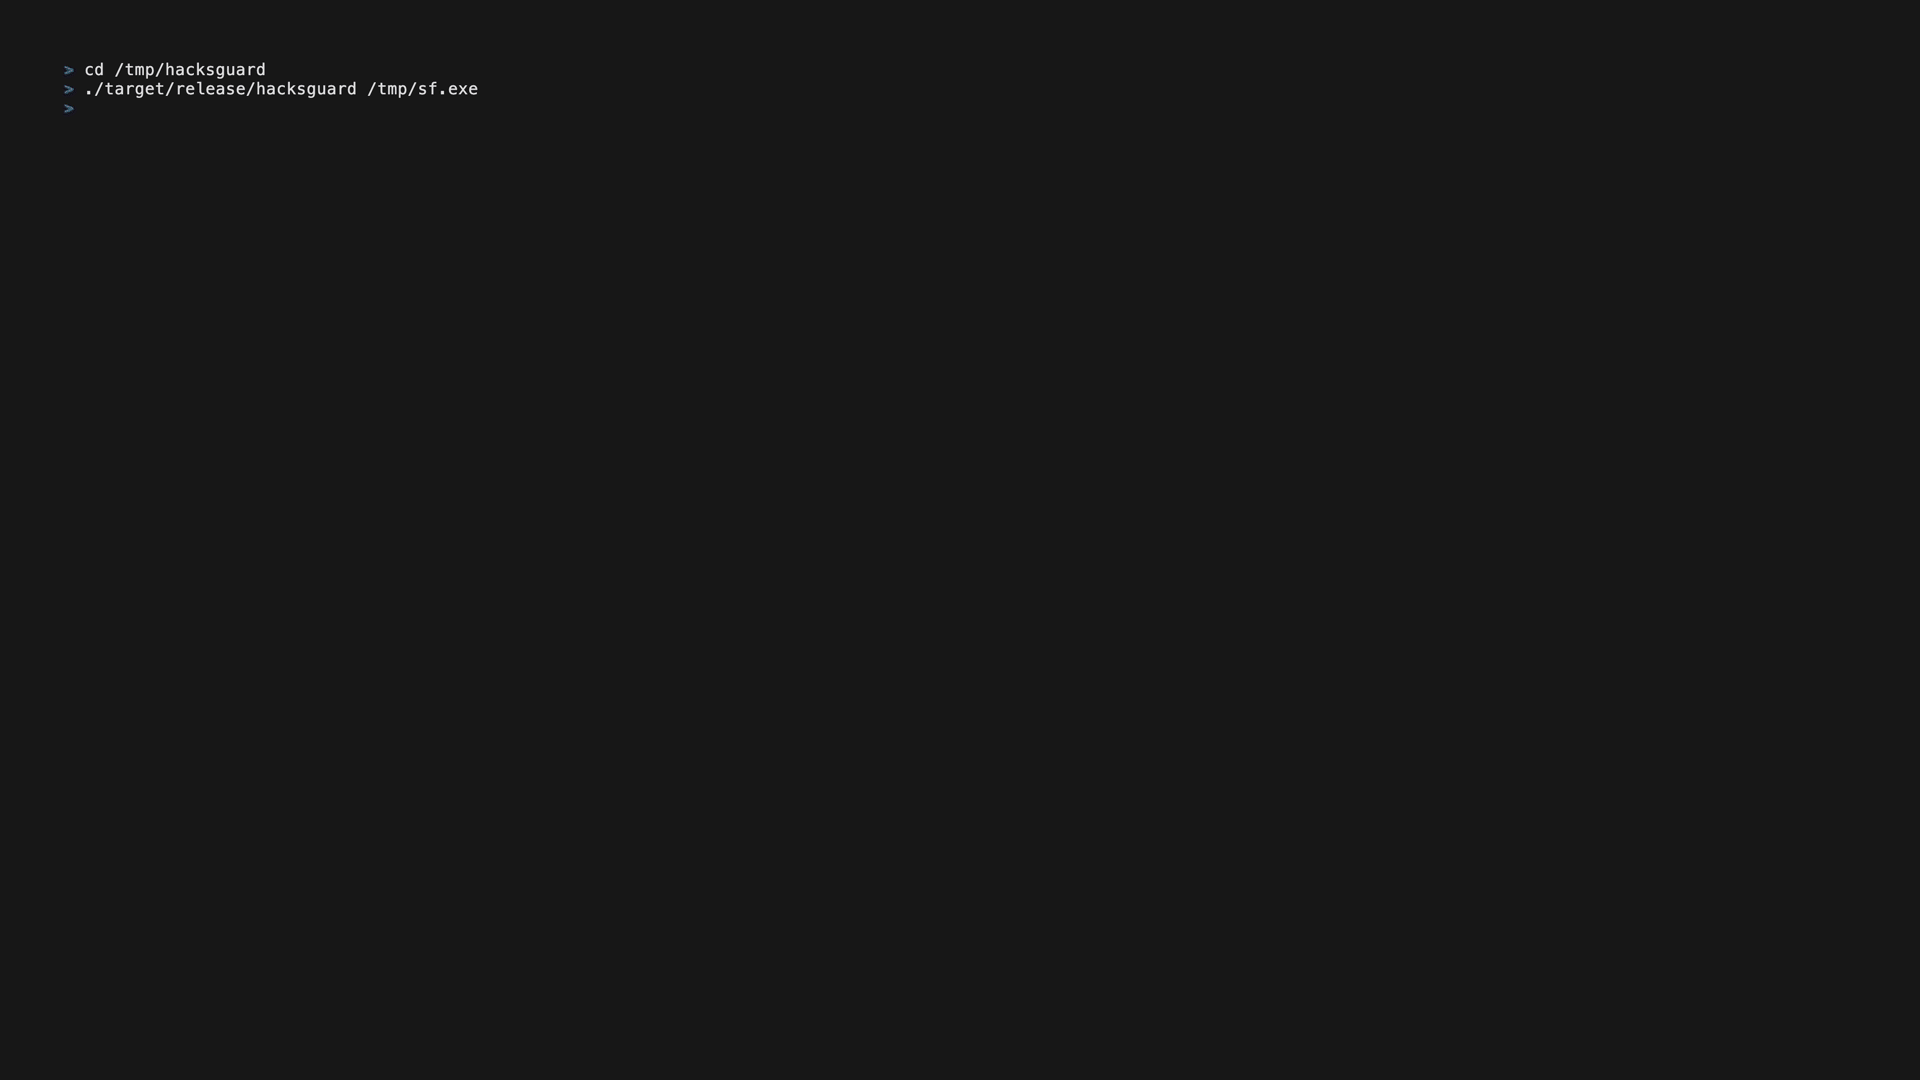
    PE Headers


    !PE Headers

    Sections


    !Sections

    Imports


    !Imports

    Disassembly


    !Disassembly

    Hex View


    !Hex View

    Strings


    !Strings

    Entropy


    !Entropy

    Analyst Guide


    !Analyst Guide

    项目信息

    开发语言:Rust

    Star 数:213

    技术要点

    该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。

    从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。

    使用与学习建议

    1. 下载源码压缩包,解压到本地环境。

    2. 根据项目类型准备对应的运行环境与依赖。

    3. 按照 README 中的步骤完成配置与部署。

    4. 在隔离的测试环境中运行验证,避免影响生产系统。

    免责声明

    本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。

    资源标题hacksguard - A blazingly fast, multi-threaded TUI malware analy
    所属分类病毒分析
    发布作者admin
    发布时间2026-10-05 23:28:02
    下载权限 免费下载
    附件数量2 个下载链接
    浏览次数350
    讨论数量0
    主题状态正常讨论中

    本资源免费,登录后即可在本页「下载链接」区域获取全部附件。

    请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。

    请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
    还没有讨论,快来抢沙发~
    登录 后才能参与讨论
    下载链接
    会员才能下载
    登录后开通会员
    同分类推荐
    暂无同类资源
    免费登录即可下载
    查看会员
    放大预览

    © 2026 剑庭安 - 网站开发定制 SEO 优化蜘蛛池代做 在线看手相算命. 保留所有权利。

    Powered by 酷像SEOv3.0

    网站地图 Sitemap.xml
    首页 全部分类 黑客安全 逆向|反编译 精品源码 站长工具自助开通会员其他资源SEO工具站群源码泛程序蜘蛛模板蜘蛛池外链工具创意乐园 搜索 会员服务 登录 注册