 病毒分析
点击放大
firedrill - firedrill is a malware simulation harness for eval
项目说明
🧯firedrill: A malware simulation harness
![goreleaser]()
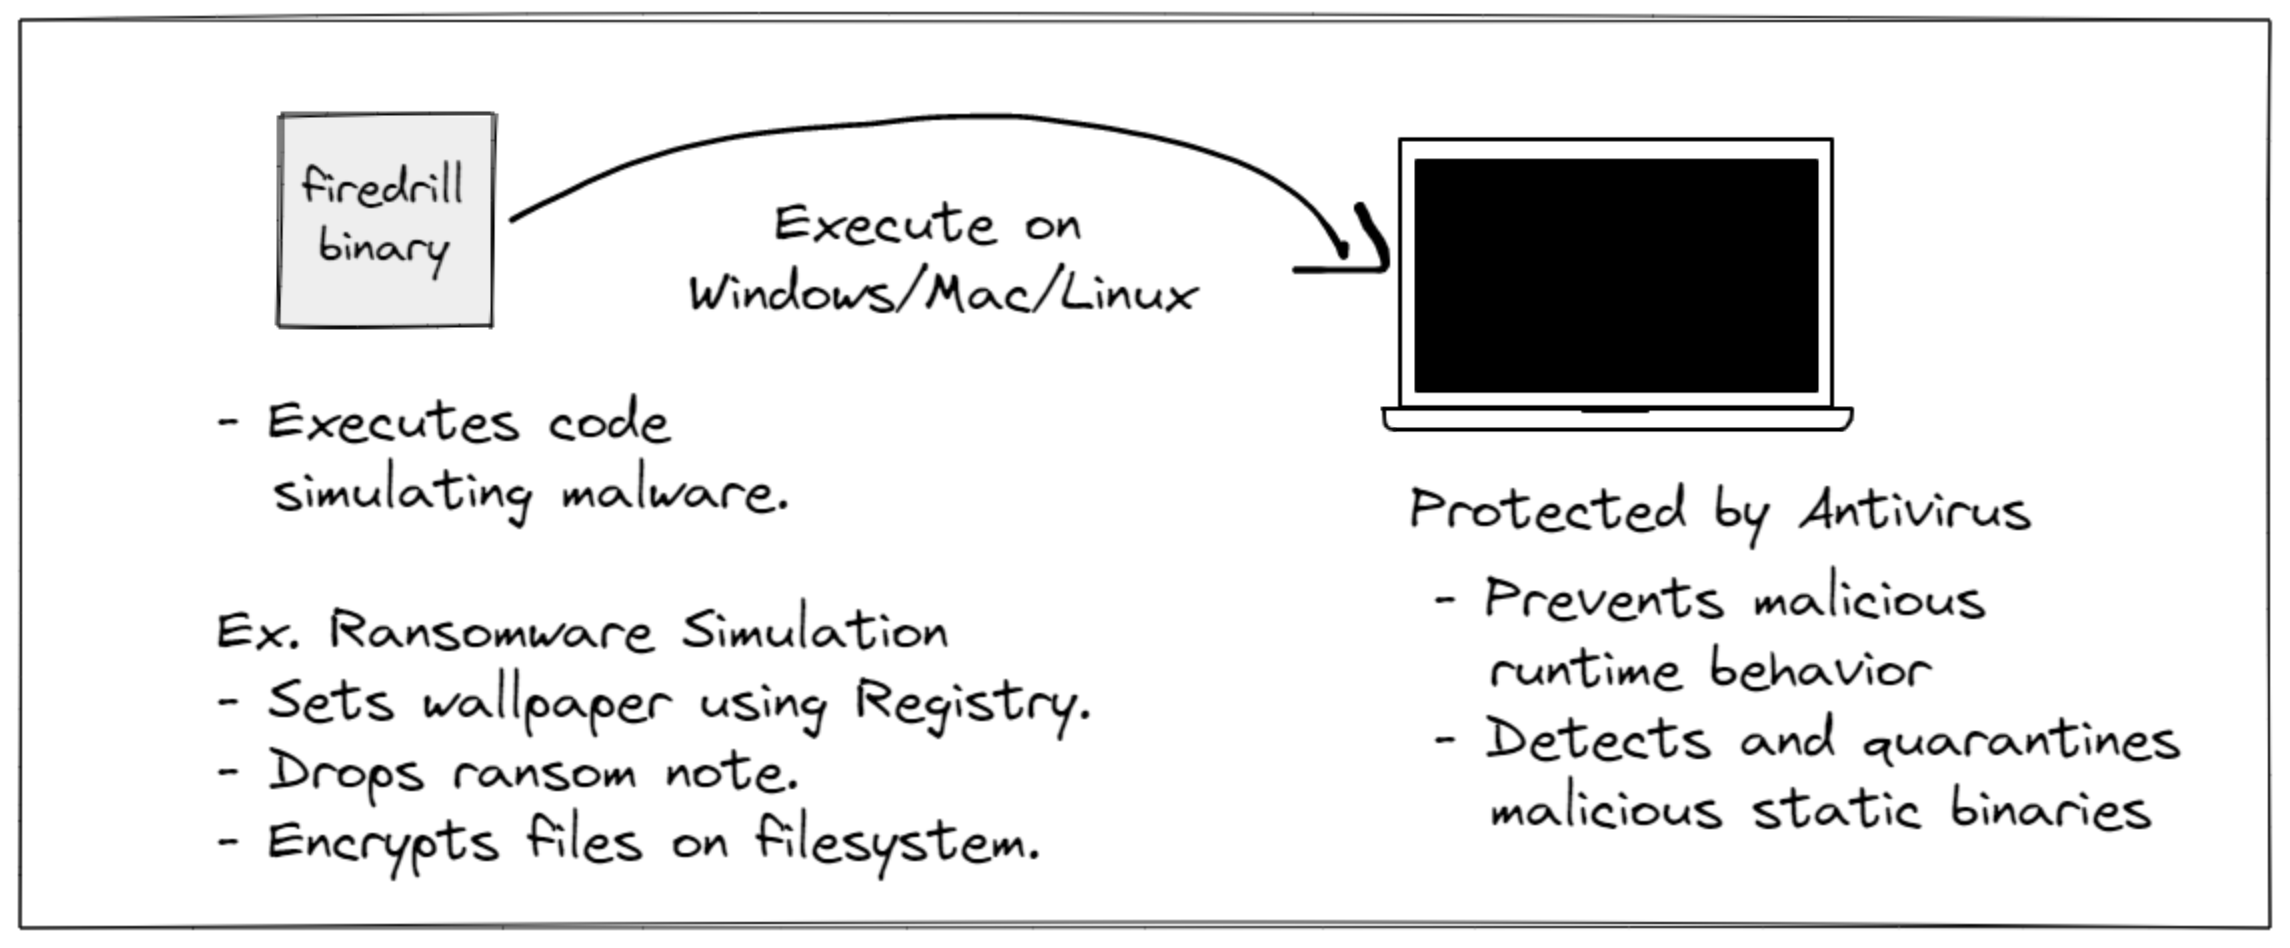
TL;DR: firedrill is an open-source library from FourCore Labs to build malware simulations easily. We ha a set of four different attack simulations for you to use and build on top of: Ransomware Simulation, Discovery Simulation, a UAC Bypass and a Persistence Simulation.
Organizations invest a whole lot in their security controls and tooling for the security teams to be efficient. They might put in 10s of man-hours tuning a single security control to their needs building out detection rules, identifying best practice configuration and setting up automation. However, the task shouldn't end right here, it is crucial to test the effecti of these security systems against attackers. Usually, this is done with pentesting and red teaming acti done either in-house or by external teams. This results in immense value for the organization as its build confidence in security controls against in the event of a real attack.
!firedrill
Read more about firedrill on our blog.
Ransomware Simulation
The ransomware simulations consists of typical behaviour of a ransomware.
Mock Ransomware
This includes, in this order:
Sandbox Analysis
| Sandbox |
| ------- |
| Hybrid-Analysis |
| Intezer Analyze |
System Ransomware
This includes, in this order:
Sandbox Analysis
| Sandbox |
| ------- |
| Hybrid-Analysis |
| Virus Total |
Discovery Simulation
The discovery simulation consists of simulation of a malware executing three techniques from the Discovery tactic in MITRE ATT&CK, performing reconnaisance of system information which is used for further exploiting the system:
This includes, in this order:
Sandbox Analysis
| Sandbox |
| ------- |
| Hybrid-Analysis |
| Intezer Analyze |
UAC Bypass Simulation
The UAC Bypass simulation consists of malware using the fodhelper.exe utility a from Windows 10 to achie pri escalation by creating a registry structure to execute arbitrary commands with adminstrator pri:
This includes, in this order:
HKCU:\Software\Classes\ms-settings\ and start notepad.exe with admin pri bypassing UAC.
Sandbox Analysis
| Sandbox |
| ------- |
| Hybrid-Analysis |
| Intezer Analyze |
Registry Run Key Persistence Simulation
This is a simulation of a persistence techniques which use registry Run keys to achie for arbitrary payloads. These keys include: HKEY_CURRENT_USER\Software\Microsoft\Windows\Current\Run, EY_CURRENT_USER\Software\Microsoft\Windows\Current\RunOnce, HKEY_CURRENT_USER\Software\Microsoft\Windows\Current\RunServices, HKEY_CURRENT_USER\Software\Microsoft\Windows\Current\RunSer.
This includes, in this order:
HKCU\SOFTWARE\Microsoft\Windows\Current\Run to execute a sample payload embedded in the binary.
HKCU\SOFTWARE\Microsoft\Windows\Current\Run to bring back it to it's original state for a safe simulation.
| Sandbox |
| ------- |
| Hybrid-Analysis |
| Intezer Analyze |
Usage
Windows
Mock Ransomware Simulation
System Ransomware Simulation
Discovery Simulation
UAC Bypass Simulation
Registry Run Key Simulation
Linux/bash
项目信息
开发语言:Go
Star 数:198
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕firedrill is a malware simulation harness for evaluating your security controls展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | firedrill - firedrill is a malware simulation harness for eval |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:28:50 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 220 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |