 病毒分析
点击放大
ReflectiveNtdll - A Dropper POC with a focus on aiding in EDR evasio
项目说明
:exclamation: A Small personal WeekEnd Project POC form my side. Completely Free and Open Source. Doesn't belong to my Company's Asset!
#### This POC will be useful if the Operator came to know about the _RealeaseID_ of the Windows Machine before the execution of this implant into the Machine. As for different release ID, the ntdll.dll are different. In case of wrong match, this implant will *NOT* work/ crash!
Another Project Related to this Concept done by : NTDLLReflection
Future Upgrades:
1. Applying ApiHashing to replace
GetModuleHandle & GetProcAddress by Reflecti
POC1:
1. A POC Dropper focusing EDR e (*Self-Injecting dropper*). Again thanks to Sektor7 by reenz0h
2. Followed by loading of ntdll in-memory (BYONtdll), which is present as shellcode (using pe2shc by ).
3. NTDLL Unhooking from implant Process.
4. E via *In-memory Payload encryption* via SystemFucntion033 NtApi. It performs RC4 encryption and decryption in-memory, which *erradicates* "_On Injection_" shellcode detection, as in case of normal shellcode injection, encrypted payload is decrypted just before mapping those raw shellcode in process memeory, at that particular moment, the A happens. But in this case, no chance of that as decryption occurs when it is already mapped in process memory :wink:
5. Shellcode Execution via No new thread technique via Fiber.
POC2:
1. A POC Dropper focusing EDR e (*Self-Injecting dropper*). Again thanks to Sektor7 by reenz0h
2. Loading of ntdll in-memory (BYONtdll), which is present as shellcode (using pe2shc by ).
3. [_
Different from Previous One_]\No need of Ntdll Unhooking.\
Mapping the new Ntdll in memory and then getting the *address of our target NtApi* from the EAT of the mapped Ntdll in process memory (Yup! Appended the technique of NTDLLReflection by ).
4. E via *In-memory Payload encryption* via SystemFucntion033 NtApi. It performs RC4 encryption and decryption in-memory, which *erradicates* "_On Injection_" shellcode detection, as in case of normal shellcode injection, encrypted payload is decrypted just before mapping those raw shellcode in process memeory, at that particular moment, the A happens. But in this case, no chance of that as decryption occurs when it is already mapped in process memory :wink:
5. Shellcode Execution via No new thread technique via Fiber.
DrawBack of this POC:
To make it work in a Windows Machine, Operator need to know the
ReleaseID of the Windows Machine prior to the Execution of this Implant, as based on the ReleaseID, ntdll.dll . After getting the ntdll , follow the below mentioned steps.Building the Executable (For POC1 as well as POC2):
Demo For POC1:
Video Link:
Internal Findings:
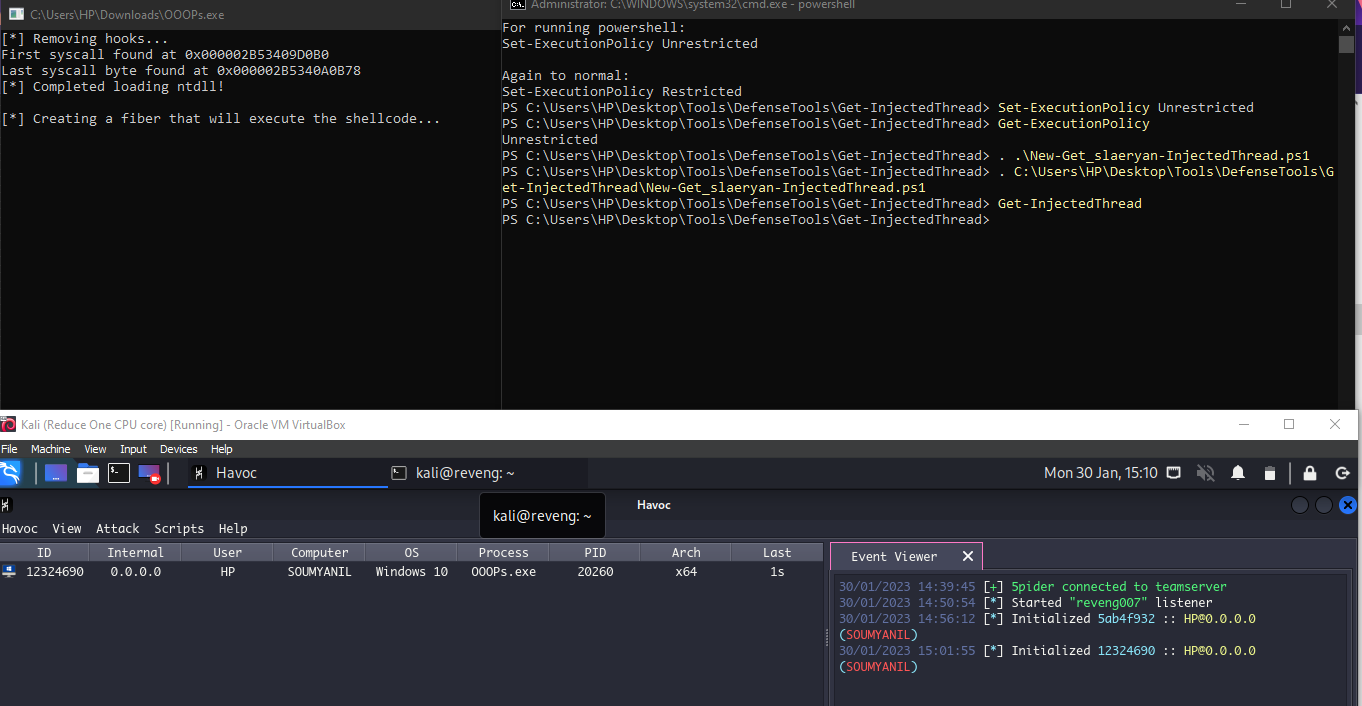
1. Bypassing Get-InjectedThread.ps1 by :
I used CreateThread not CreateRemoteThread, to run shellcode of ntdll in-memory!
According to Get-InjectedThread.ps1:
!image
No CreateThread is mentioned!
!image
2. Bypassing DefenderCheck: by
!image
3. AntiScan.me Scan:
!image
4. Capa Scan:
!image
5. Moneta Scan:
!image
As we ha ntdll.dll in-memory and also the implant is not signed!
6. Pe-sieve Scan:
7. PEBear View: IAT Table
!image
Suspicious usage of WinApi is removed from IAT
Demo For POC2:
Video Link:
Internal Findings:
1. Bypassing Get-InjectedThread.ps1 by :
I used CreateFiber not CreateRemoteThread, to run shellcode in-memory!
!image
2. Bypassing DefenderCheck: by
!image
3. AntiScan.me Scan:
!image
4. Capa Scan:
!image
5. Moneta Scan:
!image
As we ha ntdll.dll in-memory, but this time it was not detected by Moneta and also the implant is not signed!
6. Pe-sieve Scan:
7. PEBear View: IAT Table
!image
Suspicious usage of WinApi is removed from IAT
Also thanks to:
1. for enlightening me, regarding the internals of EDR and other suggestions.
2. for having a spontenious discussion on ImplantDev.
3. @_winterknife_ for his Wraith Project.
4. for enlightening me, regarding the internals of
ntdll.dll hooking by EDR.项目信息
开发语言:C
Star 数:177
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A Dropper POC with a focus on aiding in EDR evasion, NTDLL Unhooking followed by loading ntdll in-memory, which is present as shellcode (using pe2shc by @hasherezade). Payload encryption via SystemFucntion033 NtApi and No new thread via Fiber展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ReflectiveNtdll - A Dropper POC with a focus on aiding in EDR evasio |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:29:56 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 424 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |