 病毒分析
点击放大
项目说明
Reverse Engineer's Toolkit
What?
This is a collection of tools you may like if you are interested in reverse
engineering and/or malware analysis on x86 and x64 Windows systems. After
installing this program, you'll have two ways to access the tools:
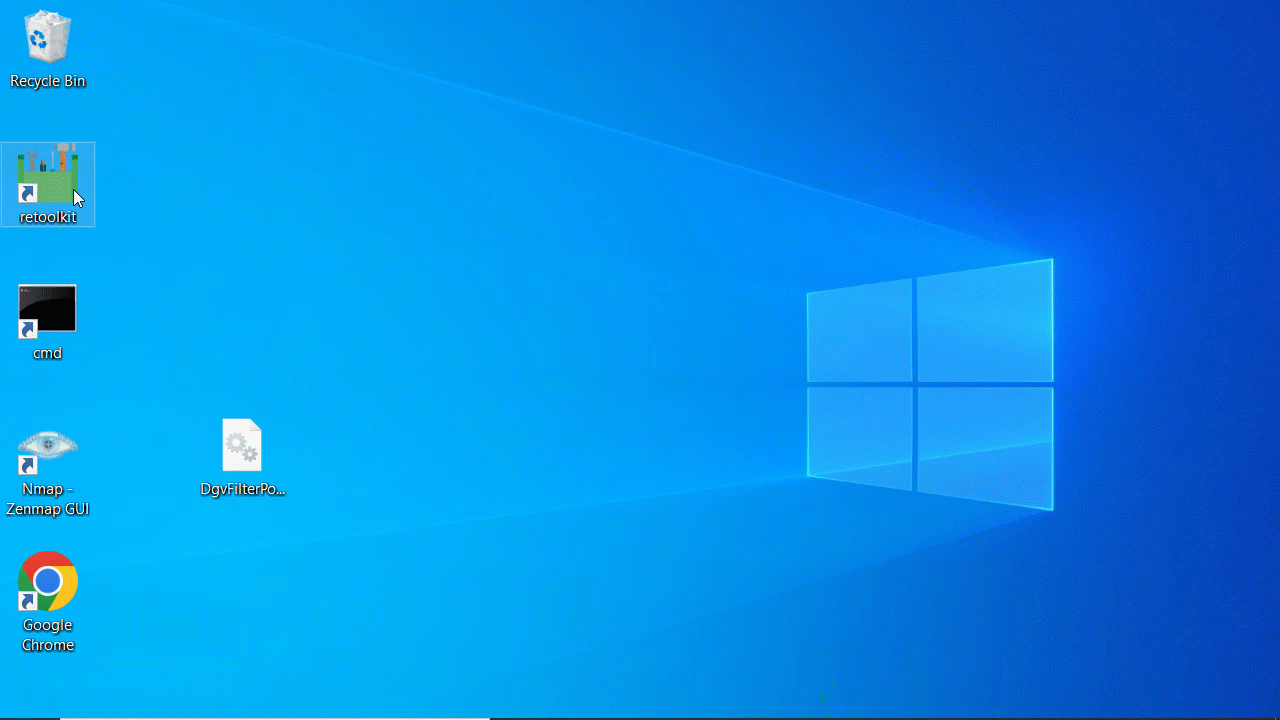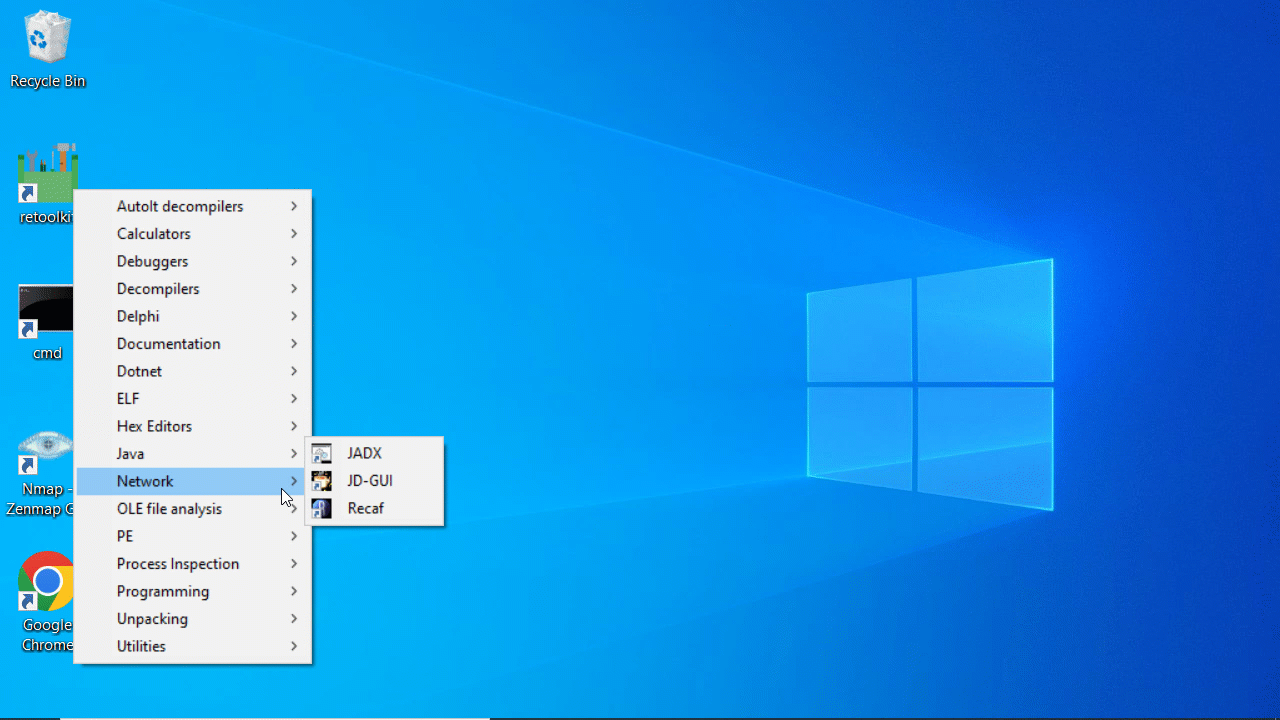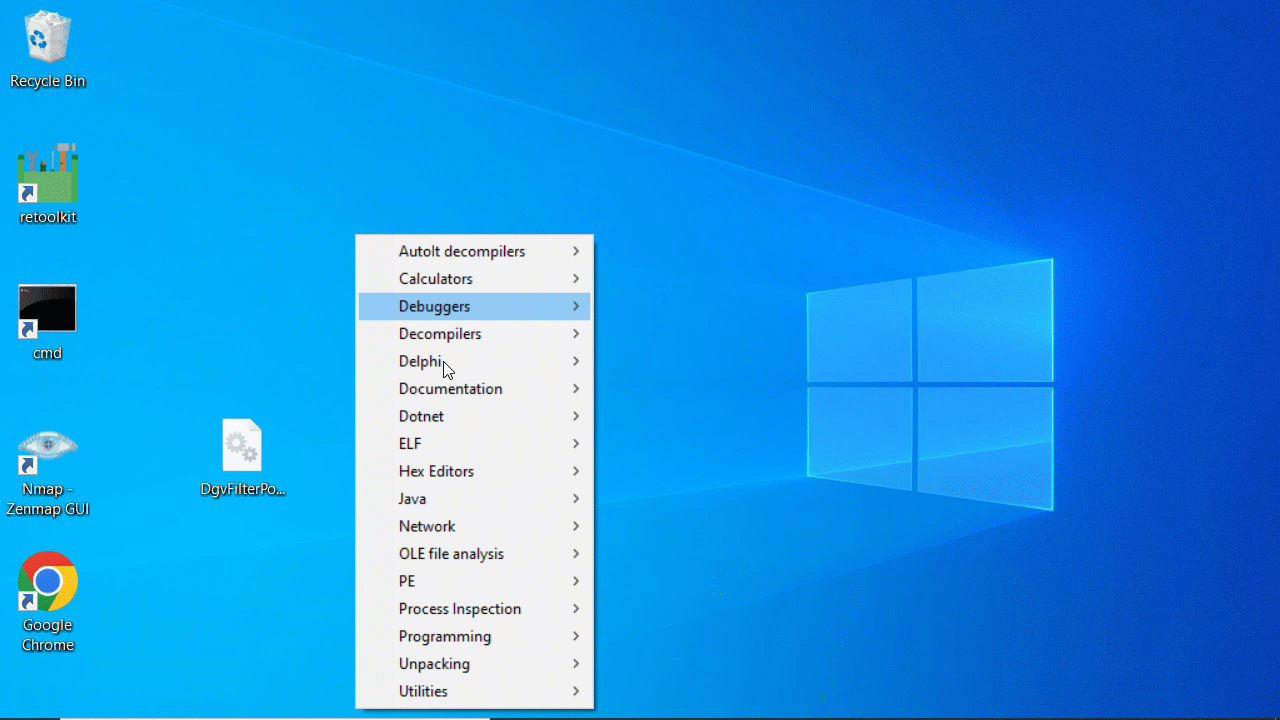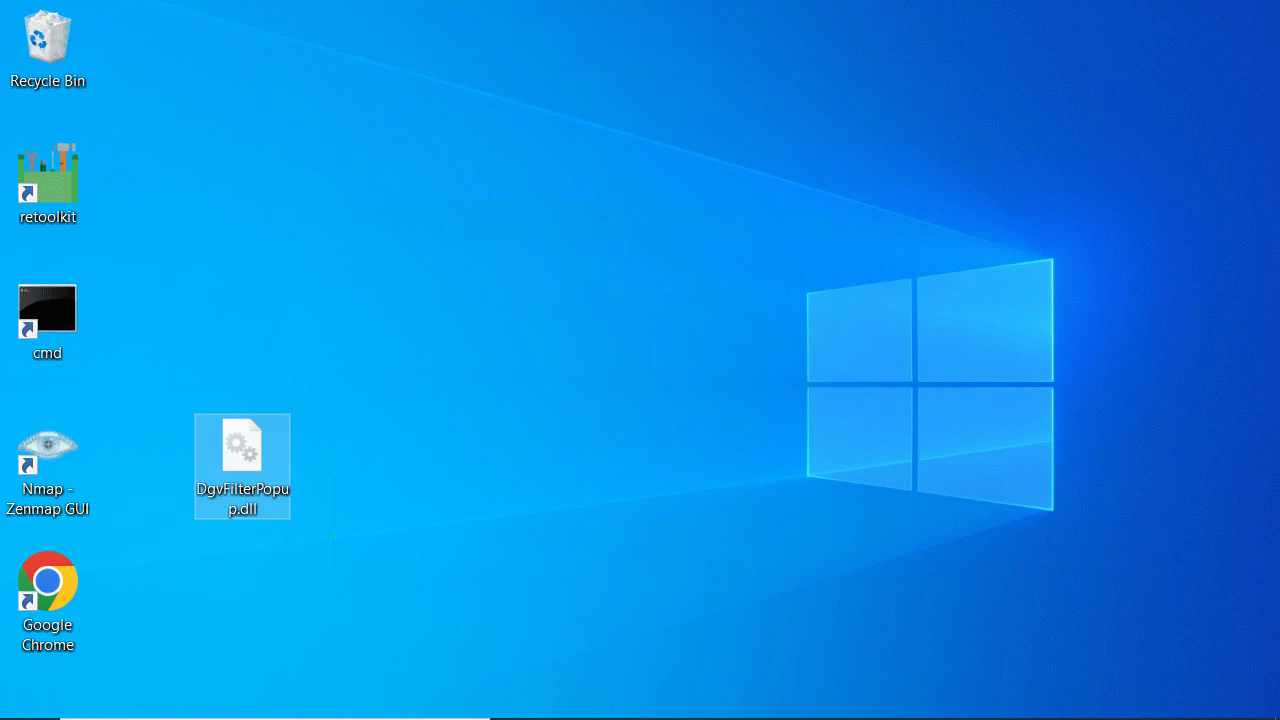
retoolkit icon in the Desktop.retoolkit. This way the selected file ispassed as argument to the desired program.

Why do I need it?
You don't. Ob, you can download such tools from their own website and
install them by yourself in a new VM. But if you download retoolkit, it will
probably save you some time. Additionally, the tools come pre-configured so
you'll find things like x64dbg with a few plugins, command-line tools working
from any directory, etc. You may like it if you're setting up a new analysis VM.
Download
The \*.iss files you see here are the source code for our setup program built
with Inno Setup. To download the real
thing, you have to go to the
Releases section and
download the setup program.
Included tools
Have a look at the wiki for a
detailed list. By the way, you won't find cracked software there.
Is it safe to install it in my en?
I don't know. Some included tools are not open source and come from shady
places. You should use it exclusively in machines and under your own
responsibility.
Windows Defender is complaining about malware during retoolkit installation!
Yeah, I prefer to analyze malware without antivirus software installed, but it's
up to you. If you want to disable Windows Defender, see this
page.
Can you add tool X?
It depends. The idea is to keep it simple. We won't add a tool just because it's
not here yet. But if you think there's a good reason to do so, _and the license
allows us to redistribute the software_, please open an issue
here
if it doesn't exist yet.
Changelog
See CHANGELOG.md.
Inspiration
This project is inspired by (but not copied from) a toolkit that has been distributed
in reverse engineering forums over the years called "Cracker Tools by yildo".
I couldn't find an official source for it, although a web search will reveal
copies and references.
The key differences are:
for redistribution by its license or by its authors.
your own installer based on this project. Attribution to the original project is expected.
项目信息
开发语言:Inno Setup
Star 数:5293
技术要点
该项目属于病毒分析方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Reverse Engineer's Toolkit展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | retoolkit - Reverse Engineer's Toolkit |
| 所属分类 | 病毒分析 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:32:18 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 127 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |