 CTF思路
点击放大
cicd-goat - A deliberately vulnerable CI/CD environment. Learn
项目说明
![cicd-goat]()
![maintained by]()
![top 10]()
![.github/workflows/release.yaml]()
![CircleCI]()
!Docker pulls
!
Deliberately CI/CD en.
Hack CI/CD pipelines, capture the flags. :triangular_flag_on_post:
Created by Cider Security (Acquired by Palo Alto Networks).
Table of Contents
* Description
* Download & Run
* Linux & Mac
* Windows (Powershell)
* Usage
* Instructions
* Take the challenge
* Troubleshooting
* Solutions
* Contributing
Description
The CI/CD Goat project allows engineers and security practitioners to learn and practice CI/CD security through a set of 11 challenges, enacted against a real, full blown CI/CD en. The scenarios are of difficulty levels, with each scenario focusing on one primary attack .
The challenges cover the Top 10 CI/CD Security Risks, including Insufficient Flow Control Mechanisms, PPE (Poisoned Pipeline Execution), Dependency Chain Abuse, PBAC (Pipeline-Based Access Controls), and more.\
The different challenges are inspired by Alice in Wonderland, each one is themed as a different character.
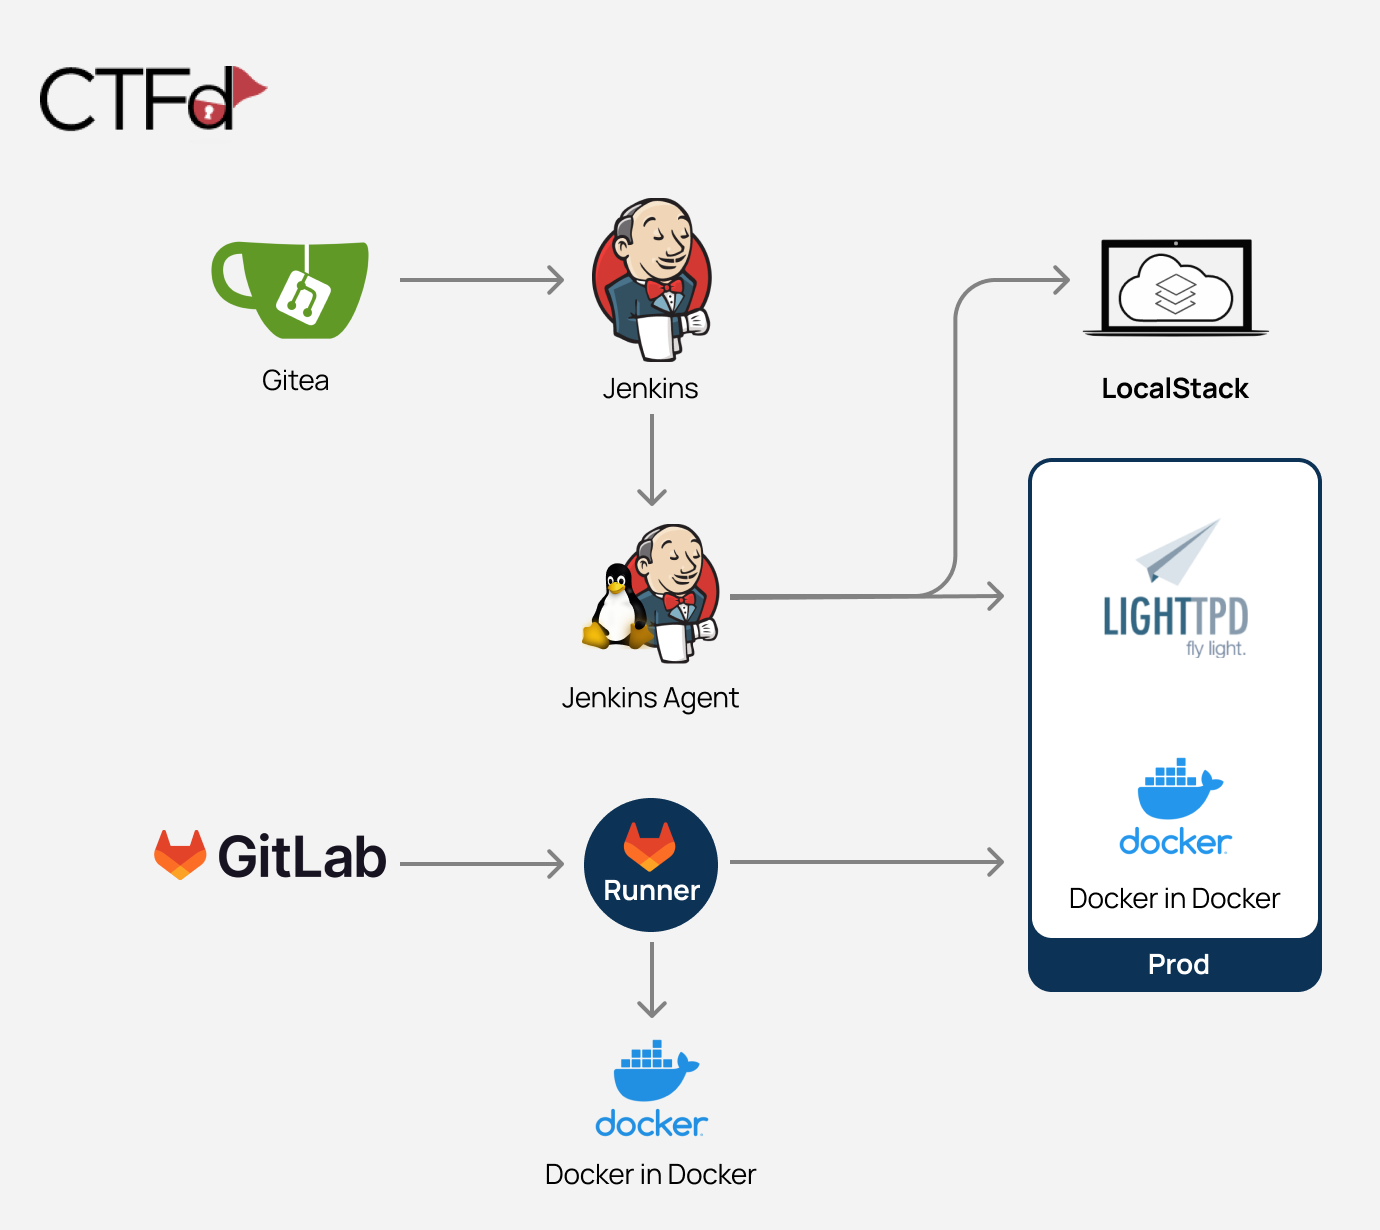
The project’s en is based on Docker containers and can be run locally. These containers are:
1. Gitea (minimal git server)
2. Jenkins
3. Jenkins agent
4. LocalStack (cloud service emulator that runs in a single container)
5. Prod - contains Docker in Docker and Lighttpd service
6. CTFd (Capture The Flag framework)
7. GitLab
8. GitLab runner
9. Docker in Docker
The images are configured to interconnect in a way that creates fully functional pipelines.

Download & Run
There's no need to clone the repository.
Linux & Mac
Windows (Powershell)
Usage
Instructions
* Spoiler alert! Avoid browsing the repository files as they contain spoilers.
* To configure your git client for accessing private repositories we suggest cloning using the http url.
* In each challenge, find the flag - in the format of _flag#_ (e.g _flag2_), or another format if mentioned specifically.
* Each challenge stands on its own. Do not use access gained in one challenge to sol challenge.
* If needed, use the hints on CTFd.
* There is no need to exploit CVEs.
* No need to hijack admin accounts of Gitea or Jenkins (named "admin" or "red-queen").
Take the challenge
1. After starting the containers, it might take up to 5 minutes until the containers configuration process is complete.
2. Login to CTFd at to view the challenges:
* Username:
alice* Password:
alice3. Hack:
* Jenkins
* Username: alice
* Password: alice
* Gitea
* Username: thealice
* Password: thealice
* GitLab
* Username: alice
* Password: ali12345
4. Insert the flags on CTFd and find out if you got it right.
Troubleshooting
* If Gitea shows a blank page, refresh the page.
* When forking a repository, don't change the name of the forked repository.
* If any of the services doesn't start or is not configured correctly try adding more cpu and memory to the docker engine and update it to the lateset .
Solutions
Warning: Spoilers! :see_no_evil:
* See Solutions.
* BSidesLV talk: Climbing the Production Mountain: Practical CI/CD Attacks Using CI/CD Goat - Featuring solutions of the Caterpillar, Mock Turtle and Dormouse challenges.
Contributing
See Contributing.
项目信息
开发语言:Python
Star 数:2314
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A deliberately vulnerable CI/CD environment. Learn CI/CD security through multiple challenges.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | cicd-goat - A deliberately vulnerable CI/CD environment. Learn |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:35:25 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 410 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |