 CTF思路
点击放大
MemLabs - Educational, CTF-styled labs for individuals inter
项目说明
<img src="./Images/MemLabs.png" alt="MemLabs" class="center">
---
Table of contents
1. About MemLabs
2. Moti
3. Structure of Repository
4. Tools and Frameworks
5. Flag Submission
- Email Format
6. Resources
7. Feedback & suggestions
8. Usage
9. Author
About MemLabs :mag:
MemLabs is an educational, introductory set of CTF-styled challenges which is aimed to encourage students, security researchers and also CTF players to get started with the field of Memory Forensics.
Moti :dart:
The main goal of creating this repository was to provide a reliable platform where indi can learn, practice and enhance their skills in the field of memory forensics. As of the CTF-style, well, what better & interesting way to learn security than by playing CTFs?
I also belie labs can be used by anyone to help others become good with the essentials and fundamentals of memory forensics.
Structure of repository
| Directory | Challenge Name | Level Of Difficulty |
|:----:|:----:|:----:|
|Lab 0 | Never Too Late Mister | Sample challenge |
|Lab 1 | Beginner's Luck | Easy |
|Lab 2 | A New World | Easy |
|Lab 3 | The Evil's Den | Easy - Medium |
|Lab 4 | Obsession | Medium |
|Lab 5 | Black Tuesday | Medium - Hard |
|Lab 6 | The Reckoning | Hard |
To aid first-timers to understand how to approach CTF challenges & usage of , please refer Lab 0 which comes with a elaborate walkthrough & I hope it will be a great way to start MemLabs!
All the memory dumps are that of a Windows system.
> Note: The level of difficulty specified may not be fully accurate as it depends on the indi. I' my best to categorize them after receiving feedback from beginners to the field.
Tools and frameworks :hammer_and_wrench:
I'd suggest e use The Framework for analysing the memory images.
Please execute the setup.sh file to install all the required dependencies in your system.
> Note: Windows users can download the executable file from here.
As these labs are quite introductory, there is no need for installing more tools. However, if the user wishes, they can install many other forensic tools.
The preferred OS would be Linux. However, you can also use Windows (WSL) or macOS.
Flag submission :triangular_flag_on_post:
Please mail the flags of each lab to <>
Please have a look at the following example to better understand how to submit the solution.
Suppose you find 3 flags in a particular lab,
+ flag{stage1_is_n0w_d0n3}
+ flag{stage2_is_n0w_d0n3}
+ flag{stage3_is_n0w_d0n3}
Concatenate all the flags like this: flag{stage1_is_n0w_d0n3} flag{stage2_is_n0w_d0n3} flag{stage3_is_n0w_d0n3}
Note: Place the flags in the right order. The content inside the flags indicates their place. The flags must be space-separated.
All the labs will follow the same flag format unless specified otherwise.
Email format
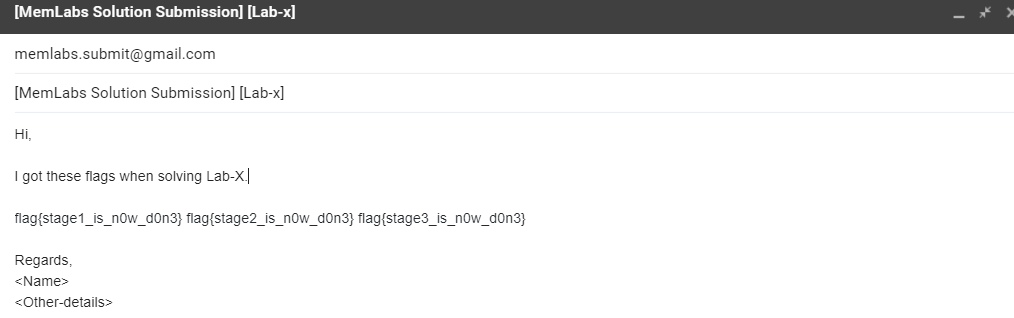
Please follow the following guidelines when sending the solution. Below is a sample:
Email Subject: [MemLabs Solution Submission] [Lab-x]
> x indicates the Lab number. Ex: 1,2,3 etc..
!Email-Picture
Email your solution to
If the solution is correct, then the participant will receive a confirmation mail.
Feedback & suggestions
I'd love the community's feedback regarding these labs. Any suggestions or impro are always welcome. Please email it to me or contact my : @_abhiramkumar.
Resources :rocket:
This section contains resources which I' myself and some others which I have used when I learnt memory forensics. I hope this resources will help e in not only solving these labs but also in exploring more areas in memory forensics.
+ Basics of Memory Forensics
+ Windows Command Reference
+ Sans DFIR Memory Forensics cheat sheet
If you're interested to play more CTFs or want to try more challenges,
+ AboutDFIR - Challenges & CTFs
+ CTFtime.org
If you are interested in knowing how to write plugins for framework,
+
+
Usage
MemLabs is completely free to anyone to use. If you wish to use MemLabs in your workshops, classes or use the labs anywhere else, it is my humble request to you to use the original links to the labs and please mention my name as well. For any other queries, please contact me.
Author :bust_in_silhouette:
P. Abhiram Kumar
Digital Forensics, Team bi0s
+ Mail:
+ Twitter: @_abhiramkumar
+ Personal Blog: stuxnet999.github.io
项目信息
开发语言:Shell
Star 数:1918
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Educational, CTF-styled labs for individuals interested in Memory Forensics展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | MemLabs - Educational, CTF-styled labs for individuals inter |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:35:55 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 234 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |