 CTF思路
点击放大
Crypton - Library consisting of explanation and implementati
项目说明
Crypton
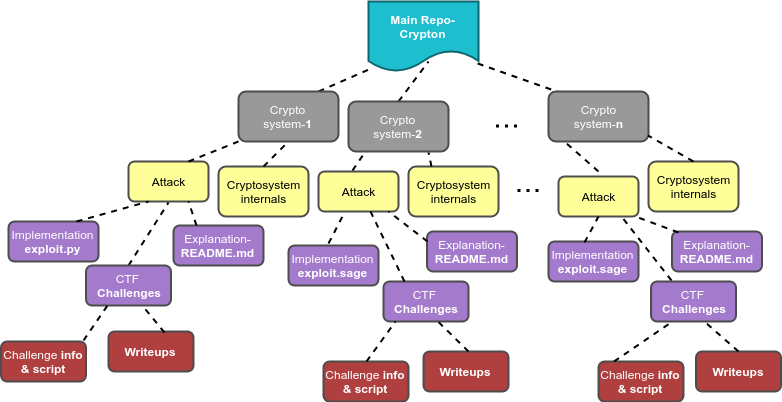
Crypton is an educational library to learn and practice Offensive and Defensi. It is basically a collection of explanation and implementation of all the existing and attacks on Encryption Systems (Symmetric and Asymmetric), Digital Signatures, Message Authentication Codes and Authenticated Encryption Systems. Each attack is also supplemented with example challenges from "Capture The Flag" contests and their respecti. Indi who are already acquainted (or are into CTFs) with this field can use Crypton as a tool to sol based on a particular existing .
The library will be continuously updated with attack explanations and CTF challenges! Feel free to email me regarding any suggestions!
I ha a blog post on the timeline of de of this library:
WARNING: The author in no way guarantees that the code is secure. The library is only meant for educational purposes and the code should not be used for implementing in real world. All the example scripts in the library are *trivial* implementations.
There are different sections in this README:
* _Moti What motivated me to create this library
* _Library Structure_- Directory structure of Crypton
* _Domain Co What all cryptosystems and attacks are covered in this library
* _Future Plans/TODO_- Attacks/concepts that are to be included soon
---
Moti
Help CTF players and indi interested in the field of Cryptography provide a platform for learning attacks in crypto and for experienced CTF players to practice challenges systematically divided into attacks associated with different sub-domains in crypto. Also, illustrate through attack explanations how proper implementation of protocols is crucial.
---
Library Structure
!picture
---
Domain Co
1. Block Ciphers
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | Block Cipher Basics- working of block ciphers, padding etc.| <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul> |
| 2 | Modes of Encryption- different modes of operation on block ciphers: ECB, CBC, CTR | <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul> |
| 3 | Block Size Detection- detect blocksize of a block cipher encrypting data on a remote service| <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul> |
| 4 | Mode Detection- detect type of mode of encryption: independent or dependent encryption of blocks| <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul> |
| 5 | ECB Byte at a Time- byte at a time decryption of a secret string running on a remote service encrypting input+secret in ECB mode| <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [x] [\[link\]]() </li></ul> |
| 6 | CBC I- detect the value of Initialisation on a remote service that is encrypting our input using a block cipher in CBC mode| <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> | <ul><li>- [ ] </li></ul> |
| 7 | CBC Bit Flipping Attack- exploiting cookie generation mechanism to login as admin when cookie is generated using a block cipher in CBC mode| <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [x] [\[link\]]() </li></ul> |
| 8 | CBC Byte at a Time- byte at a time decryption of a secret string running on a remote service encrypting input+secret in ECB mode| <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> | <ul><li>- [ ] </li></ul> |
| 9 | CBC Padding Oracle Attack- decryption of data encrypted by a service pro encryption/decryption | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [x] [\[link\]]() </li></ul> |
| 10 | CTR Bit Flipping- exploiting cookie generation mechanism to login as admin when cookie is generated using a block cipher in CBC mode| <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [ ] </li></ul> | <ul><li>- [x] [\[link\]]() </li></ul> |
2. RSA Encryption
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | Unpadded RSA Enc/Dec- key generation, distribution, encryption/decryption, of decryption formula and padding in RSA | <ul><li>- [x] [\[link\]]() </li></ul> | <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul> |
| 2 | Direct Root Attack- attack on unpadded RSA with low public key exponent | <ul><li>- [x] [\[link\]]() </li></ul> | <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul>|
| 3 | Fermat's Factorisation- technique used to factor modulus n when p and q are in proximity | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 4 | Pollard's p-1 Factorisation- technique to factorise n when both of it's factors p & q, p-1 and q-1 have very small prime di| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 5 | Common Modulus Attack- decrypt ciphertext when it's corresponding plaintext is encrypted two different times with the same modulus n | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 6 | Common Prime Attack- retrie of moduli n1 and n2 when they have a common factor | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 7 | Wiener's Attack- get value of decryption key exponent d when d < N<sup>0.25</sup> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 8 | Wiener's Attack - get value of decryption key exponent d when d is a few bits greater than N<sup>0.25</sup> or d < N<sup>0.25</sup>| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 9 | Coppersmith's Attack- coppersmith's theorem, attack on stereotyped messages and factoring n with high bits known | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 10 | Franklin Reiter Related Message Attack- attack to retrie messages encrypted using the same modulus| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 11 | Hastad's Broadcast Attack- with extension- attack to retrieve a message broadcasted among different people, encrypted using same exponent but different moduli| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 12 | PKCS1-v1.5-Padded-RSA-Encryption/Decryption- ASN1 encoding, padded RSA encryption (needs to be fixed)| <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 13 | Least Significant Bit Oracle Attack- attack on RSA oracle leaking least significant bit value on decryption | <ul><li>-[x] [\[link\]]()</li></ul>| <ul><li>-[x] [\[link\]](RSA-encryption/Attack-LSBit-Oracle/lsbitoracle.py) </li></ul>| <ul><li>- [ ] </li></ul> |
| 14 | Attack-Retrie- attack on RSA oracle to extract value of modulus in case it is not public | <ul><li>-[x] [\[link\]]() </li></ul>| <ul><li>-[x] [\[link\]]() </li></ul> | <ul><li>-[x] [\[link\]]() </li></ul> |
| 15 | Intro-RSA-Challenges- basic challenges in RSA related to Number Theory| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
3. Message Authentication Codes (MACs)
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | Message Authentication Code- internals and security analysis of MACs| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 2 | CBC MAC Forgery- generating two message M1 and M2 having the same CBC-MAC authentication tag| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 3 | Length Extension Attack on CBC-MAC- generate a valid authentication tag of message M1 \|\| M2 (concatenation) given MAC(M1) | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [ ] </li></ul> |
4. Discrete Logarithm Problem
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | DLP- Cyclic Groups, Discrete Logarithm Problem| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
| 2 | Pollard's Rho Algorithm to solve DLP | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> |
| 3 | Baby Step Giant Step Algorithm to solve DLP| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul> |
| 4 | Pohlig Hellman Algorithm to solve DLP| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul> |
| 5 | Elliptic Curve DLP- defining identity element, inverse of a point, cyclic groups o on an EC, Hasse's theorem, ECDLP | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 6 | Baby Step Giant Step Algorithm to sol Curve DLP | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul> |
| 7 | Pollard's Rho Algorithm to sol Curve DLP | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> |
5. ElGamal Encryption
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | ElGamal Cryptosystem- Encryption/Decryption- key generation, encryption, decryption in ElGamal Cryptosystem| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [x] [\[link\]]()</li></ul> |
6. Authenticated Encryption (AE)
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | AE basics & internals- working of authenticated encryption| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 2 | AE with MACs- different techniques of implementing AE with MACs: Encrypt and MAC, MAC then encrypt and encrypt then MAC| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 3 | Authenticated Ciphers| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 4 | AE with Associated Data| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 5 | AES-GCM- encryption in AES-GCM, Wegman-Carter MAC| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]() </li></ul>| <ul><li>- [ ] </li></ul> |
| 6 | Forbidden Attack on AES-GCM- attack on AES-GCM due to nonce-reuse| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [x] [\[link\]]() </li></ul> |
7. Elliptic Curves
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | Elliptic Cur- defining Elliptic Curves, point addition, point doubling and scalar multiplication | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[python\]](), [\[sage\]]()</li></ul> | <ul><li>- [ ] </li></ul> |
8. Digital Signatures
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | ElGamal Signatures- key generation, signature generation, signature and correctness of ElGamal Signature scheme| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [x] [\[link\]]()</li></ul> |
| 2 | Elliptic Curve DSA- signature generation, signature and correctness of signature algorithm| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 3 | Attack k-reuse ECDSA- forging of ECDSA signatures due to reuse of k | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul>| <ul><li>- [ ] </li></ul> |
| 4 | Unpadded RSA Digital Signatures- signature generation and in RSA digital signature scheme| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> |
| 5 | PKCS1-v1.5 padded RSA Digital Signatures| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [ ] </li></ul> |
| 6 | e=3 Bleichenbacher's Attack| <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul>| <ul><li>- [x] [\[link\]]()</li></ul> |
9. Identification
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | Identification Internals | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul> | <ul><li>- [ ] </li></ul> |
| 2 | Ephemeral Key Authentication | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [ ] </li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> |
10. Diffie Hellman Key Exchange
| S.No. | Topic | Explanation | Impl./Exploit | Challenge# |
|-------|:---------------------------:|:-----------------------------------------------------------------------------------------------:|:------------:|:----------:|
| 1 | Diffie Hellman Key Exchange Internals | <ul><li>- [x] [\[link\]](Diffie-Hellman-Key-Exchange/README.md)</li></ul> | <ul><li>- [x] [\[link\]](Diffie-Hellman-Key-Exchange/example.py)</li></ul> | <ul><li>- [ ] </li></ul> |
| 2 | Small Subgroup Confinement Attacks | <ul><li>- [x] [\[link\]](Diffie-Hellman-Key-Exchange/Attack-Small-Subgroup-Confinement/README.md)</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]](Diffie-Hellman-Key-Exchange/Attack-Small-Subgroup-Confinement/Challenges/)</li></ul> |
| 3 | Invalid Cur Attack | <ul><li>- [x] [\[link\]](Diffie-Hellman-Key-Exchange/Attack-In/README.md)</li></ul> | <ul><li>- [x] [\[link\]]()</li></ul> | <ul><li>- [x] [\[link\]](Diffie-Hellman-Key-Exchange/Attack-In/Challenges/)</li></ul> |
TODO
1. RSA Encryption
+ PKCS1-v1.5 Padded RSA encryption
+ ~~Chosen Ciphertext Attack on RSA Cryptosystem- LSB Decryption Oracle~~ [\[Done\]]()
+ Padding Oracle Attack on PKCS1 padded RSA encryption system
+ Fermat's Factorisation
+ Sie
+ Coppersmith's Attack
+ Boneh Durfee Attack
+ Hastad's Broadcast Attack
+ Implementation of HBA on padded messages
2. Pseudo-Random-Number-Generators
+ Linear Congruential Generator
+ Mersenne Twister PRNG
+ Linear Feedback Shift Register
3. Digital Signatures
+ Blinding Attack on RSA Digital Signatures
4. ~~Diffie Hellman Key Exchange~~[\[Done\]]()
+ Elliptic Cur Hellman
5. [More to be added]
Author
Ashutosh Ahelleya
+ Twitter:
+ Blog:
+ EmailID:
项目信息
开发语言:Python
Star 数:1626
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Library consisting of explanation and implementation of all the existing attacks on various Encryption Systems, Digital Signatures, Key Exchange, Authentication methods along with example challenges from CTFs展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Crypton - Library consisting of explanation and implementati |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:36:44 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 380 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |