 CTF思路
点击放大
JavaSecLab - JavaSecLab is a comprehensive Java vulnerability p
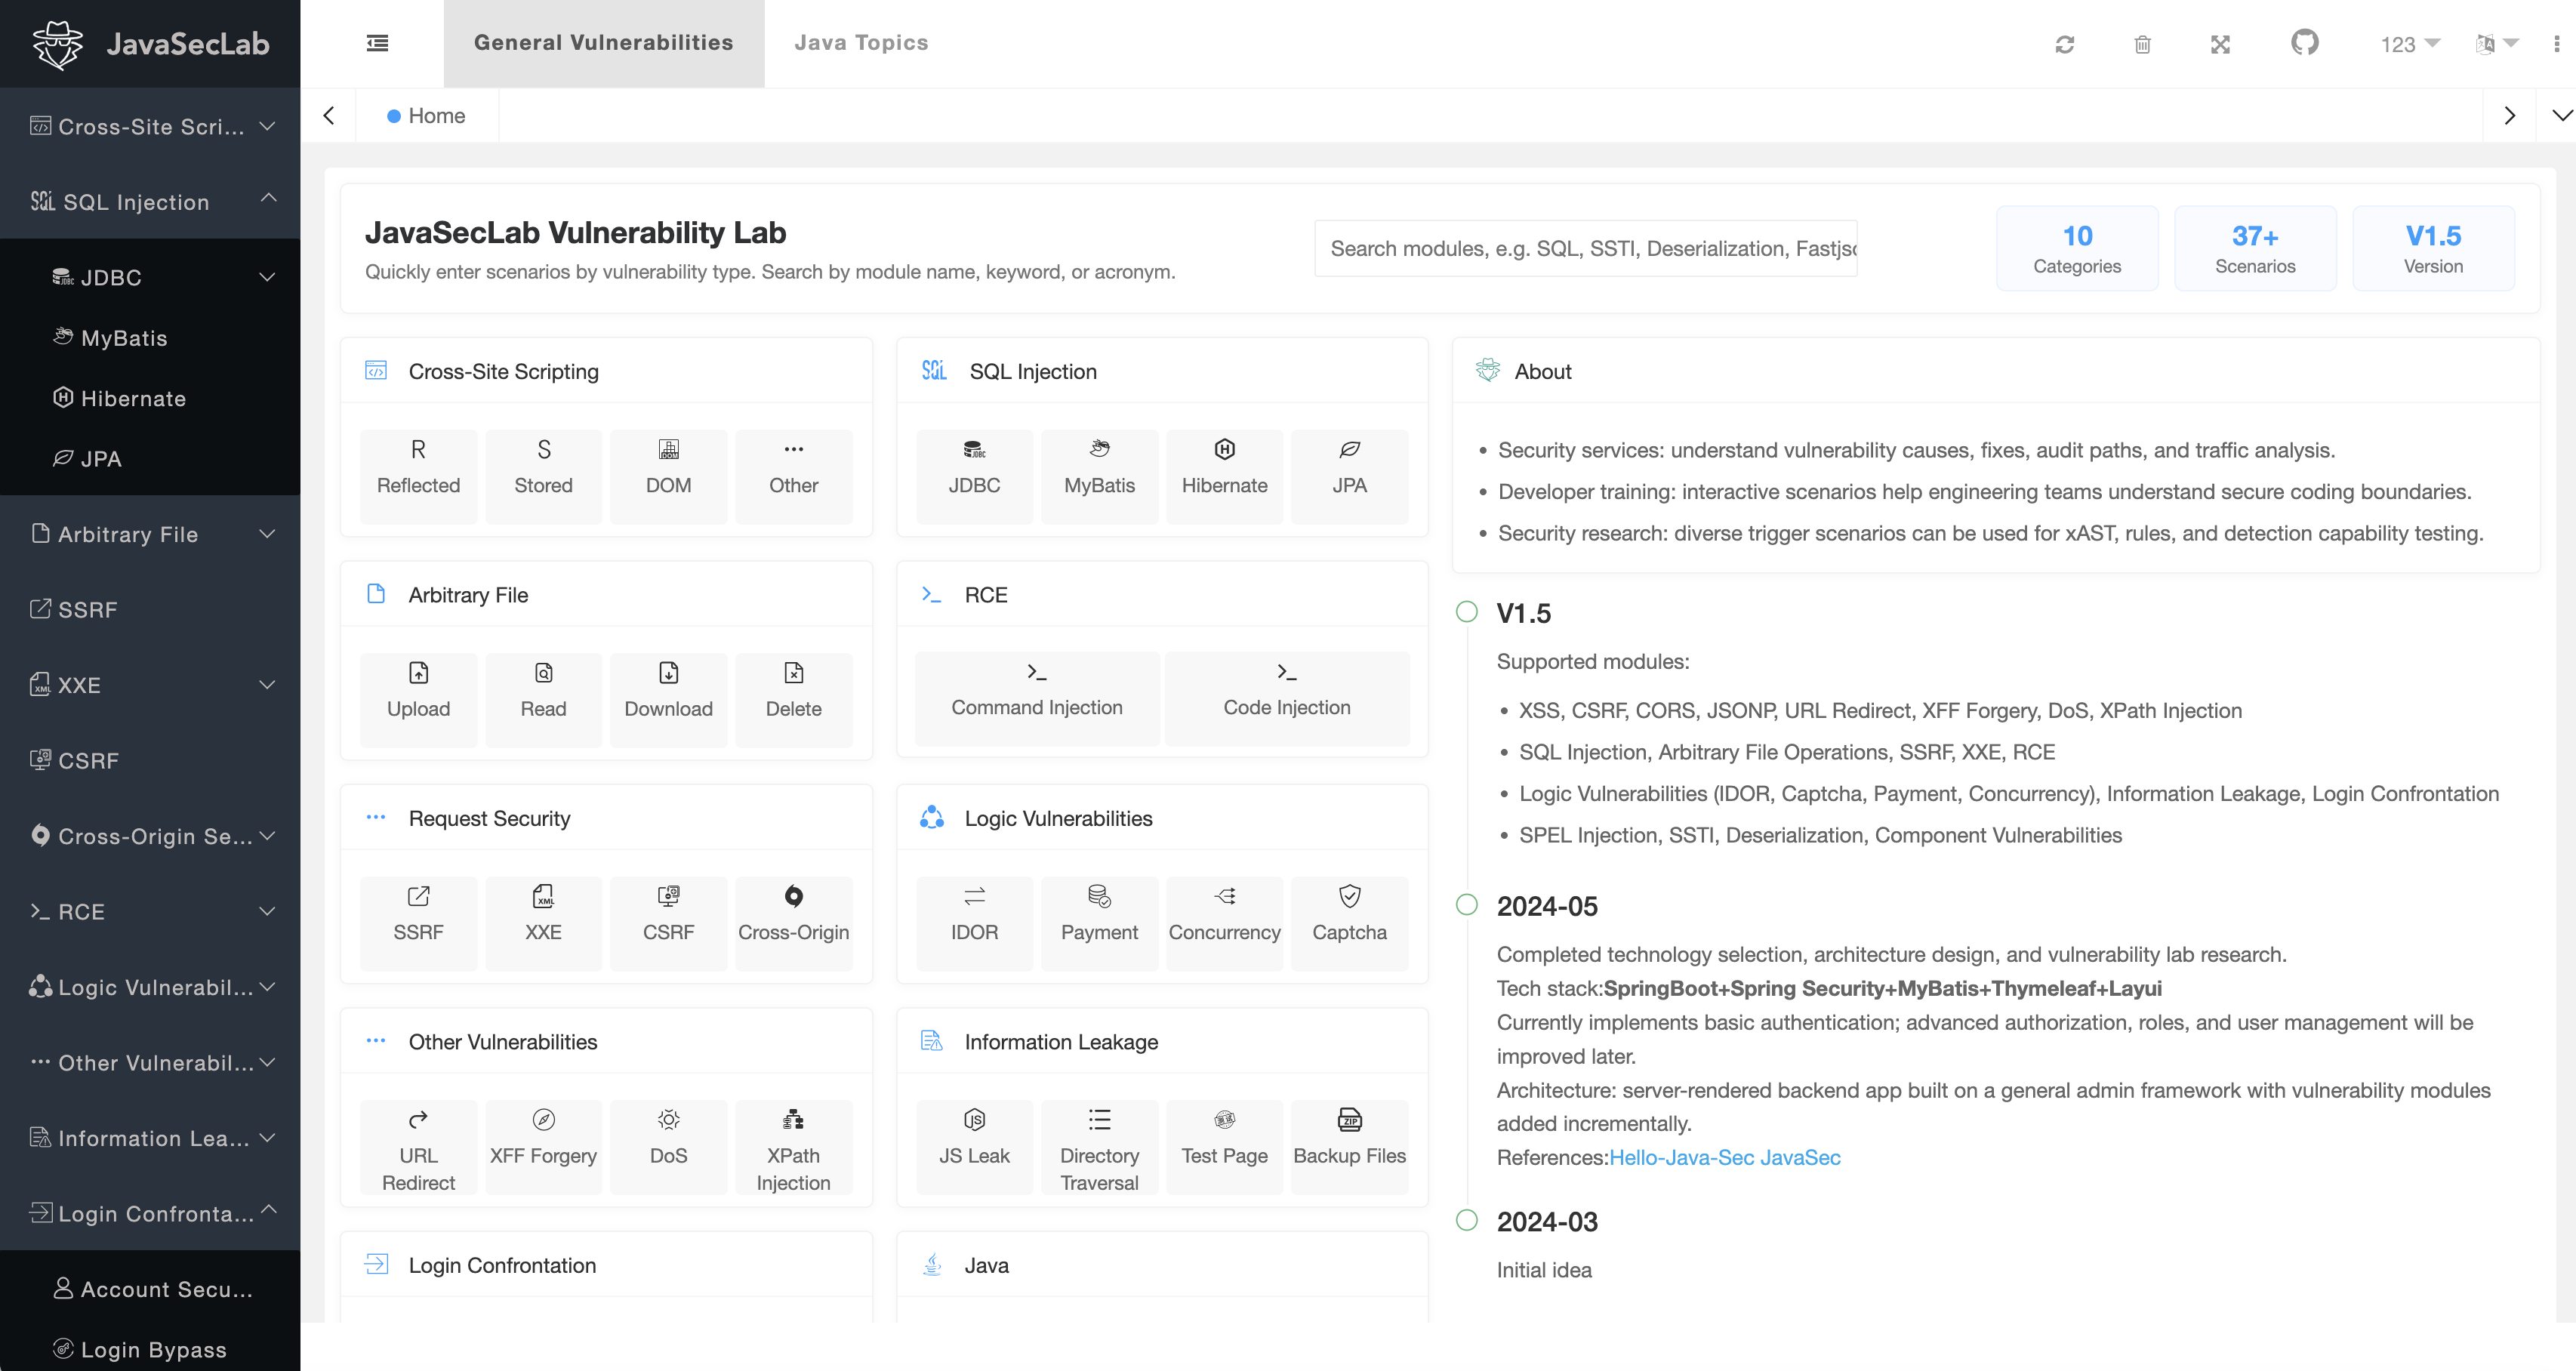
项目说明
 Ja - A Comprehensive Ja Lab
<di="center">
<a href=" src=" alt="License"></a>
<a href=" alt="Java" src="
<a href=" src=" alt=""></a>
<a href=" src=" alt="De by whgojp"></a>
<img src=" alt="GitHub Repo stars">
<img src=" alt="GitHub forks">
</div>
中文文档
----------------------------------------
O
Ja is a comprehensive Ja lab for application security learning, code audit practice, secure de training, and security tool e. Built on Spring Boot, it provides code, fixed implementations, realistic attack scenarios, audit-oriented source and sink notes, remediation guidance, secure coding explanations, and traffic-analysis examples.
The goal is practical: help users understand not only how a is exploited, but also why it exists in code and how it should be fixed.
!home
!show
Who Is It For?
Modules
Ja covers a wide range of Java web security scenarios, including:
Online Demo
Demo site: <
Default account: admin/admin
> Ja is intentionally and contains dangerous endpoints, dependencies, and insecure configurations. Run your own deployment only in an isolated en. Do not expose it directly to the public internet.
Why This Project Exists
The author has worked in enterprise security roles and experienced the full lifecycle. After penetration tests or security assessments, are often assigned to de teams through systems such as TAPD or Jira. In practice, two questions come up repeatedly:
1. Why is this behavior a ?
2. How should this be fixed?
Ja was created to connect behavior, code, remediation approaches, and audit thinking. Compared with a text-only report or a PoC, the project emphasizes understanding from the code perspective.
In code auditing, a common workflow is to locate a sink first, such as command execution, SQL execution, file access, template rendering, deserialization, or response output. The auditor then traces backward to identify the corresponding source, such as request parameters, headers, cookies, uploaded files, serialized data, or database content. Many Ja scenarios are designed around this source-to-sink path, making them useful for both learning and tool .
The same type often appears through multiple trigger paths in real systems. Ja therefore provides multiple scenarios for core classes where possible, so users can compare how different coding patterns, framework features, and business flows affect risk.
Traffic Analysis
Ja includes traffic-analysis examples to help learners connect request/response behavior with code execution. Contributions with clearer packets, better reproduction notes, or additional analysis examples are welcome.
!flow1
For example, in a time-based SQL injection scenario, the traffic pattern can be obser response latency: the ser after roughly fi.
!flow2
Tech Stack
Deployment
Clone the repository:
!git clone
Local Deployment with IDEA
Requirements:
1. Create the database and import sql/Ja.sql.
2. Set the acti to dev in src/main/resources/application.yml:
3. Update the database connection in src/main/resources/application-dev.yml:
4. Start the application from IDEA or with Maven.
Default account: admin/admin
!login
Docker Deployment
Requirements:
Option 1: start with the published image:
Option 2: build the image locally and start the lab:
If the database is empty after startup, manually import sql/Ja.sql.
!docker deployment
!docker deployment
For more deployment options and troubleshooting notes, see the Deployment Guide.
Security Notice
Ja is a lab project. It intentionally keeps dangerous endpoints, dependencies, and insecure configurations for reproduction and teaching. Run it only locally or in an isolated network.
Recommended precautions:
The secure code examples in this project are for teaching and demonstration. Real business systems usually require authentication, auditing, rate limiting, data , dependency go, monitoring, alerting, and defense in depth.
Contributing
Issues and pull requests are welcome. Good contributions include:
License
When we speak of free software, we are referring to freedom, not price.
Ja is released under the Apache License 2.0. See LICENSE for details.
Star History
<picture>
<source
media="(prefers-color-scheme: dark)"
srcset="
/>
<source
media="(prefers-color-scheme: light)"
srcset="
/>
<img
alt="Star History Chart"
src="
/>
</picture>
Changelog
See the Update Log for release notes and project history.
Author
Author's blog: 今天是几号
If you are interested in application security, secure de, SDL, De, or labs, feel free to join the community group.
<di="text-align: center;">
<img src="./pic/wechat.png" alt="WeChat" width="271" height="366" />
<img src="./pic/group.png" alt="Community group" width="271" height="366" />
</div>
Sponsorship
If Ja helps you, sponsorship is appreciated. Support will be used for maintaining the online en and continuously improving the project.
<di="text-align: center;">
<img src="./pic/donate.jpg" alt="Sponsor Ja" style="width: 40%; height: auto;"/>
</div>
项目信息
开发语言:Java
Star 数:883
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕JavaSecLab is a comprehensive Java vulnerability platform| JavaSecLab是一款综合型Java漏洞平台,提供相关漏洞缺陷代码、修复代码、漏洞场景、审计SINK点、安全编码规范,覆盖多种漏洞场景,友好用户交互UI……展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | JavaSecLab - JavaSecLab is a comprehensive Java vulnerability p |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:38:52 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 260 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |