 CTF思路
点击放大
项目说明
Aperi'Solve
![Website]()
!CI
!Lint
!Docker
!Python
!Ruff
!uv
!ty
!License
!GitHub Issues
!GitHub Pull Requests
!Last Commit
!Contributors
![Rawsec's CyberSecurity In]()
<p align="center">
<a href="
<img src=" alt="Aperi'Sol" />
</a>
</p>
Try it now:
Support Aperi'Solve:
<a href="
<img src=" alt="Sponsor Aperi'Solve on GitHub" />
</a>
---
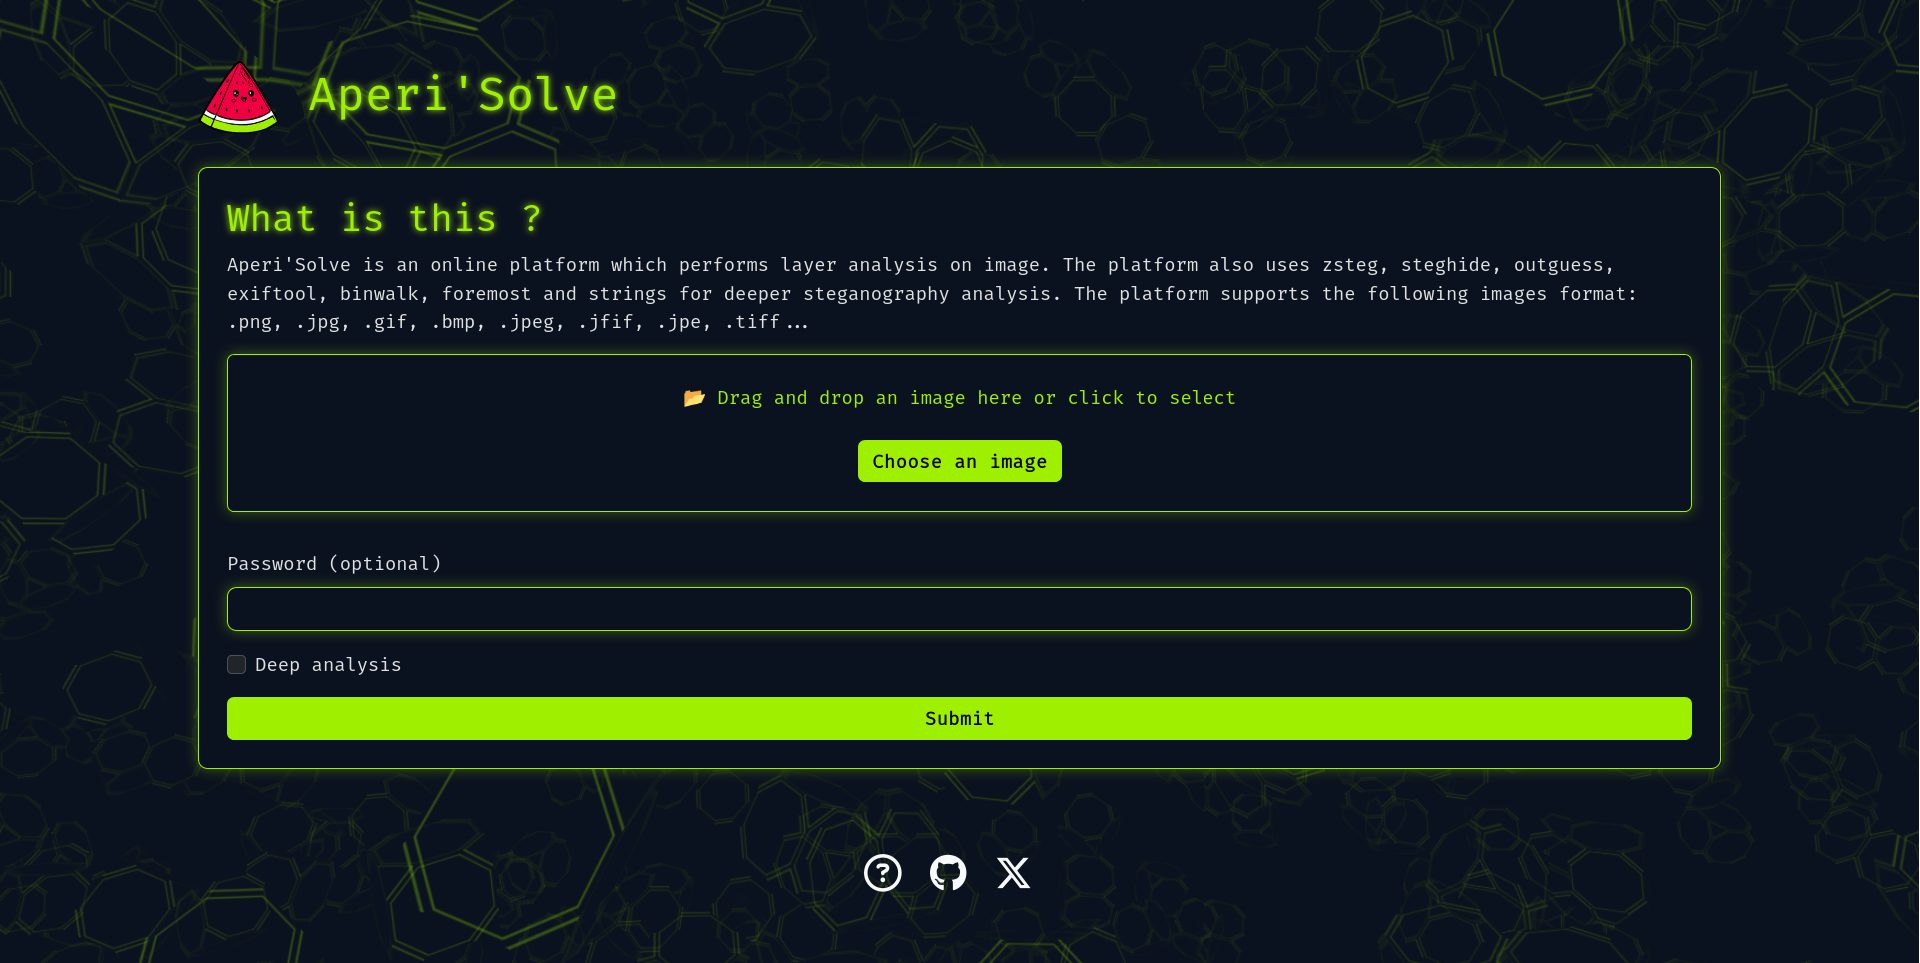
Aperi'Solve is an open-source steganalysis web platform that performs automated analysis on images to detect and extract hidden data using common steganography tools and techniques.
Key features
success/no-result badges and one-click download of extracted files:
- binwalk (embedded archives)
- exiftool (metadata and geolocation)
- file (MIME type and format detection)
- GraphicsMagick identify (image info & properties)
- foremost (car)
- jsteg (JPEG LSB extraction)
- jpseek / jphide (JPEG steganography extraction, with password)
- openstego (extraction with password)
- outguess (extraction with password, deep analysis)
- pcrt (PNG check & repair)
- pngcheck
- steghide (extraction with password)
- strings
- zsteg (LSB text/data extraction)
/wiki): a HackTricks-stylesteganography handbook — a triage methodology, a decision-tree cheatsheet,
technique pages per medium (image, audio, text, files), and a guide per
analyzer, all authored as Markdown.
Russian, Chinese and Portuguese under language-prefixed URLs (
/fr/, /es/, …).automatically by a scheduled job.
Adding an analyzer
Adding an analyzer is a single file: subclass SubprocessAnalyzer, set a few
class attributes (name, has_archive, needs_password, deep_only,display_order), and install the tool in the Dockerfile. The worker run
list, download allow-list, and frontend order are all deri.
See docs/adding-analyzer.md.
Quick start (Docker)
In case you want to host your own of
> Required: Docker + Docker Compose.
Then browse url:
Ads and analytics are disabled by default; every integration
(CUSTOM_EXTERNAL_SCRIPT, GOOGLE_ADS_TXT, SITE_BASE_URL, Sentry) is
opt-in documented in .en.
The app ne ad markup itself: CUSTOM_EXTERNAL_SCRIPT loads the
AdSense script and placement is left to Auto ads.
Architecture
The stack runs as Docker Compose services:
fanning out to one thread per tool.
request path.
IHDR CRC recovery database.
This separation keeps hea (binwalk, foremost, zsteg, etc.) isolated
and avoids blocking the web worker. Identical submissions are deduplicated by
a content hash, and deri are cached with long-li HTTP
headers, so repeat traffic is cheap.
Documentation
Testing
Roadmap
See Issues.
Contributing
See CONTRIBUTING.md.
Security
> [!WARNING]
> If you discover a security issue, please report it pri to the repository owner instead of opening a public issue.
Credits
Thanks to donors:
Thanks to contributors:
Thanks to the open-source community:
binwalk, exiftool, GraphicsMagick identify, foremost, jsteg, jphide/jpseek, openstego, outguess, pcrt, pngcheck, steghide, strings, zsteg, ...
项目信息
开发语言:Python
Star 数:848
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Steganalysis web platform展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | AperiSolve - Steganalysis web platform |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:38:55 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 494 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |