 CTF思路
点击放大
adscan - Free Active Directory pentesting tool for Linux, m
项目说明
<di="center">
<img width="740" height="198" alt="ADscan - Acti Pentesting Tool for Linux, macOS and Windows" src=" />
ADscan - Acti Pentesting Tool for Linux, macOS and Windows
![PyPI ]()
![downloads]()
![GitHub stars]()
![GitHub forks]()
![License: BSL 1.1]()
![Platform]()
![Discord]()
Free Acti pentesting tool. Replace your AD pentest toolchain with one CLI.
ADscan is a free CLI for pentesters, red teamers, and security consultants. It covers 105 Acti attack techniques in a single workflow: enumeration, Kerberoasting, AS-REP roasting, ADCS/ESC exploitation, DCSync, credential har, and nati analysis. It runs on Linux and macOS through Docker, and natively on Windows as a self-contained bundle with no Docker and no Python install.
Docs | Discord | Website
</div>
---
Table of Contents
---
Demo
![asciicast]()
_Real run, no cuts: ADscan takes HTB Forest from zero access to Domain Admin in ~3 minutes, unattended._
---
Quick Start
On Linux or macOS, ADscan runs inside Docker, so you need Docker Engine installed and running, and about 12 GB of free disk for the runtime image (the installer requires 15 GB free before it will pull).
On Windows, there is no Docker and no Python to install: download the self-contained ADscan bundle and run adscan.exe directly. The bundle carries its own runtime and tools, so it works on a hardened, locked-down host — the common assumed-breach scope where you only have a domain-joined Windows box.
> Docker install steps per distribution, the Windows bundle download, and e else: adscanpro.com/docs
Once inside the shell, start an unauthenticated recon:
This discovers domain controllers, SMB exposure, null sessions, and roastable accounts without credentials. From there, run start_auth with a domain user to enumerate LDAP, collect BloodHound data, and build the attack graph.
One command instead of the shell (PRO)
adscan ci runs the whole pipeline non-interactively: preflight, recon, enumeration, exploitation, reporting, no prompts. Same engine, no shell. It is a PRO capability — automation and unattended runs are what you're paying for; the free LITE tier gives you the full interactive adscan start shell on every platform.
--type, --interface and the auth/unauth positional are required. adscan ci --help lists the rest.
adscan ci makes every decision the interacti would ask you about, so it's built for pipelines, lab automation, and unattended engagement runs. For client work where you want to review each decision, the interactive adscan start shell (free on LITE) is the supported path.
---
ADscan
Most AD pentesters use 5-8 separate tools. ADscan replaces the chain:
| | ADscan | NetExec/CrackMapExec | Certipy | Impacket | BloodHound CE |
|---|---|---|---|---|---|
| Platform | Linux/Win | Linux/Win | Linux | Linux | Linux/Win |
| AD enumeration | Full | Partial | No | Partial | No |
| Kerberoasting | Yes | Yes | No | Yes | No |
| ADCS ESC1-16 | Yes (auto) | No | Yes (manual) | No | No |
| Attack paths | Nati | No | No | No | Yes |
| DCSync | Yes | Yes | No | Yes | No |
| Single workflow | Yes | No | No | No | No |
| Compliance reports | PRO tier | No | No | No | No |
ADscan is not a replacement for every tool in every scenario. It is the fastest path from credentials to a documented attack chain in a single terminal session.
---
Kerberoasting, ADCS and AD Attack Co
ADscan covers 105 Acti attack techniques across the kill chain — see the full technique co table, generated from the product catalog and mapped to MITRE ATT&CK:
<table>
<tr>
<td width="50%">
LITE (Free, Source A)
E a pentester could do manually, without the toolchain:
</td>
<td width="50%">
PRO
What takes days manually, automated:
Full comparison | Get PRO beta free
</td>
</tr>
</table>
---
Common Pentest Workflows
---
Usage Examples
Unauthenticated recon:
Discovers domain controllers, DNS, SMB null sessions, and roastable accounts without credentials.
Authenticated scan with BloodHound collection:
Collects LDAP data, builds the attack graph, and identifies Kerberoasting targets, ADCS misconfigurations, and pri escalation paths.
More walkthroughs:
---
Want the Full Client Report?
<a href="
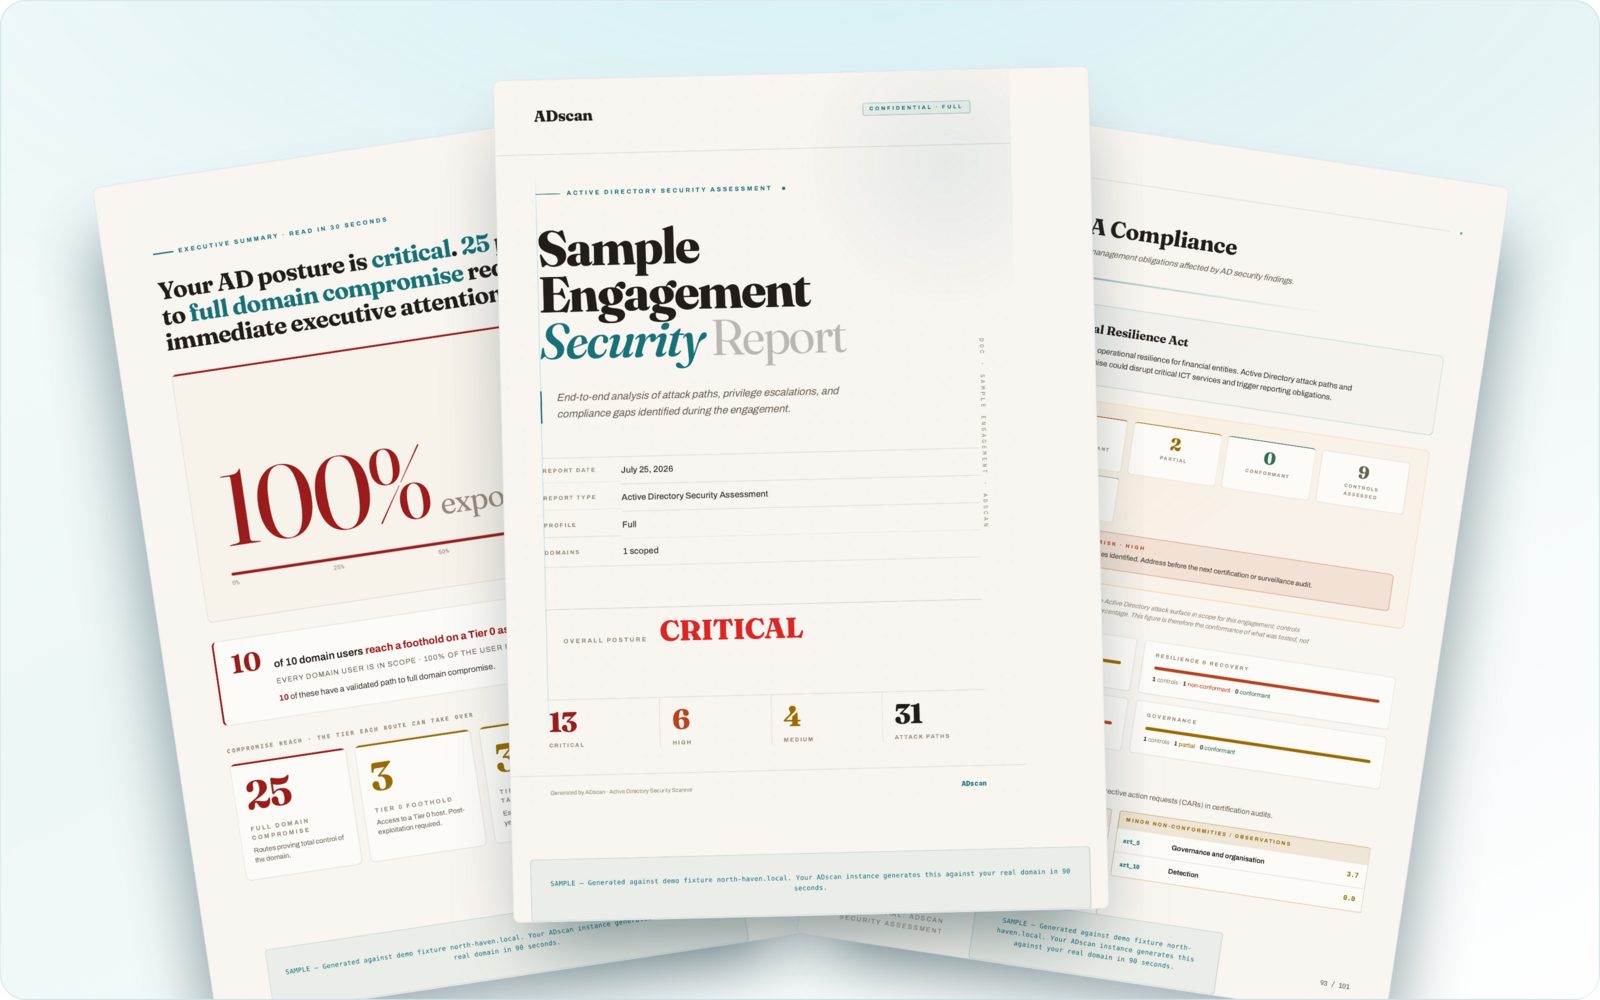
<img src="assets/report-hero.png" alt="ADscan PRO client report: cover, AD exposure score with se breakdown, and per-framework compliance mapping, generated as an audit-ready PDF" width="880">
</a>
The PRO deli is an audit-ready PDF an executive and a sysadmin can both act on: a posture score, attack-path analysis, and per-framework compliance mapping. The pages above come from a sample engagement against a lab domain.
ADscan LITE gives you enumeration, attack paths, and findings in the terminal. ADscan PRO turns them into three client-ready PDFs in 90 seconds:
Beta access is free for security consultants. adscanpro.com/pro
---
Requirements
| | |
|---|---|
| OS | Linux (Debian/Ubuntu/Kali/Parrot) or macOS with Docker Desktop; or Windows via the nati bundle (no Docker, no Python) |
| Docker | Required on Linux/macOS (Docker Engine; Compose is no longer needed). Not used by the Windows bundle |
| Disk | Linux/macOS: 15 GB free before install, runtime image roughly 12 GB unpacked. Windows bundle: a few hundred MB |
| Pri | Linux/macOS: docker group or sudo. Windows: runs as a normal domain user, no local admin required |
| Network | Internet to pull the image or download the bundle, plus the target network |
---
FAQ
Does ADscan work without a Windows machine?
Yes. On Linux (or macOS) ADscan runs entirely inside Docker. No Windows VM, no RDP, no agent installation required. It connects to your target AD en over the network using standard protocols (LDAP, SMB, Kerberos).
Does ADscan run natively on Windows?
Yes. There is a self-contained Windows bundle that runs adscan.exe directly — no Docker, no Python install, no local admin. It carries its own runtime and tools, so it works on a hardened, locked-down host, which is the usual assumed-breach scope where your only foothold is a domain-joined Windows box. The same engine runs on both platforms; only the packaging differs. On Windows without a GPU, password cracking falls back to CPU automatically, and the port scan runs in-process (no Npcap dri).
Is ADscan safe to run in production Acti en?
ADscan LITE is read-only by default for enumeration. Exploitation steps (Kerberoasting, credential dumping, DCSync) require explicit operator confirmation. Run it in a test window with your client's written authorization. See the security policy for responsible use guidelines.
How is ADscan different from BloodHound?
BloodHound is a graph analysis tool that requires separate data collection (SharpHound or AzureHound). ADscan collects data, builds the attack graph, and executes the attack chain from one terminal. LITE includes nati collection compatible with BloodHound CE. PRO adds algorithmic attack path auto-exploitation.
---
De Setup
Quality checks:
---
Contributing
Bug reports, lab reproductions, command-output samples, and focused pull requests are welcome. See CONTRIBUTING.md for the PR workflow and required checks.
Enterprise support:
---
Author
Built by Yeray Martin Dominguez, a working AD pentester. I share a new Acti attack technique most weeks — follow along on LinkedIn or X.
---
License
Source a under the Business Source License 1.1.
---
<di="center">
(c) 2024-2026 Yeray Martin Dominguez | adscanpro.com
</div>
项目信息
开发语言:Python
Star 数:733
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Free Active Directory pentesting tool for Linux, macOS and Windows. Automates AD and LDAP enumeration, Kerberoasting, ASREPRoast, password spraying, ADCS/ESC1, DCSync, RBCD, gMSA, shadow credentials, NTLM relay and credential dumping across 104 techniques, mapping BloodHound-compatible attack paths to Domain Admin. NIS2 / ISO 27001 reports.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | adscan - Free Active Directory pentesting tool for Linux, m |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:39:29 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 201 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |