 CTF思路
点击放大
h5i - An agent-native web security workspace. Find vulne
项目说明
<p align="center">
<a href=" target="_blank">
<img src="./docs/_static/logo.png" alt="h5i logo" height="126">
</a>
</p>
<p align="center">
<a href=" alt="tests" src="
<a href=" alt="Apache-2.0" src="
<a href=" alt="GitHub stars" src="
<a href=" alt="release" src="
</p>
<h1 align="center">The Agent-Native Web Security Workspace</h1>
h5i (pronounced *high-five*) is a unified workspace for building secure web applications through two complementary approaches: finding bugs and proving correctness.
* Find Bugs (Red-Teaming): Equip your AI agents with headless browser automation and deep HTTP traffic control to explore apps, intercept requests, and unco inside a configurable sandbox. Perfect for bug bounties, penetration testing, and CI regressions.
* Pro (Formal ): Build your backend on h5i-app (our Axum-based Rust framework) and use Lean 4 to formally your application logic, proving e from tenant isolation and authorization to core business state in.
Build with agents. Red-team for bugs. Formally properties.
<table align="center">
<tr>
<td align="center">
<strong>Red-teaming</strong><br>
<sub>Browser + direct HTTP control</sub>
</td>
<td align="center">
<strong>Formal </strong><br>
<sub><a href="#3-proh5i-app">Rust + Lean 4</a></sub>
</td>
<td align="center">
<strong>CI/CD</strong><br>
<sub>Continuous security checks</sub>
</td>
<td align="center">
<strong>Sandboxed workflows</strong><br>
<sub>Configurable limits + auditable sessions</sub>
</td>
</tr>
</table>
---
1. Install
The agent-facing interface is a skill, and the binary carries it:
<a href=" target="_blank" rel="noopener noreferrer"><img src=" alt="h5i on Trendshift" width="250" height="55"/></a>
---
2. Find bugs: red-team with agents
2.1. Drive the browser
A session combines one page state, cookie jar, network policy, and request
record. Agents read pages, interact with elements, and extract structured data
through one CLI:
2.2. Capture, replay, and compare traffic
The nati owns its network layer, so agents capture, inspect, edit,
replay, and compare HTTP traffic directly. Sites that need
full Chromium go through the same workbench via h5i browser proxy.
2.3. Replay confirmed flows in CI
We can replay confirmed attack flows in CI. Seeexamples/security-regression-ci for the
GitHub Actions template:
2.4. Sandbox and audit the agent
Since AI agnets might run out of control and perform dangerous actions,
h5i offers an auditable sandbox, where h5i browser requests andh5i browser audit show the full logs. For stronger isolation, a profile
in .h5i/env.toml picks a tier (workspace, process, supervised,container, or microvm) and limits network egress and filesystem access.
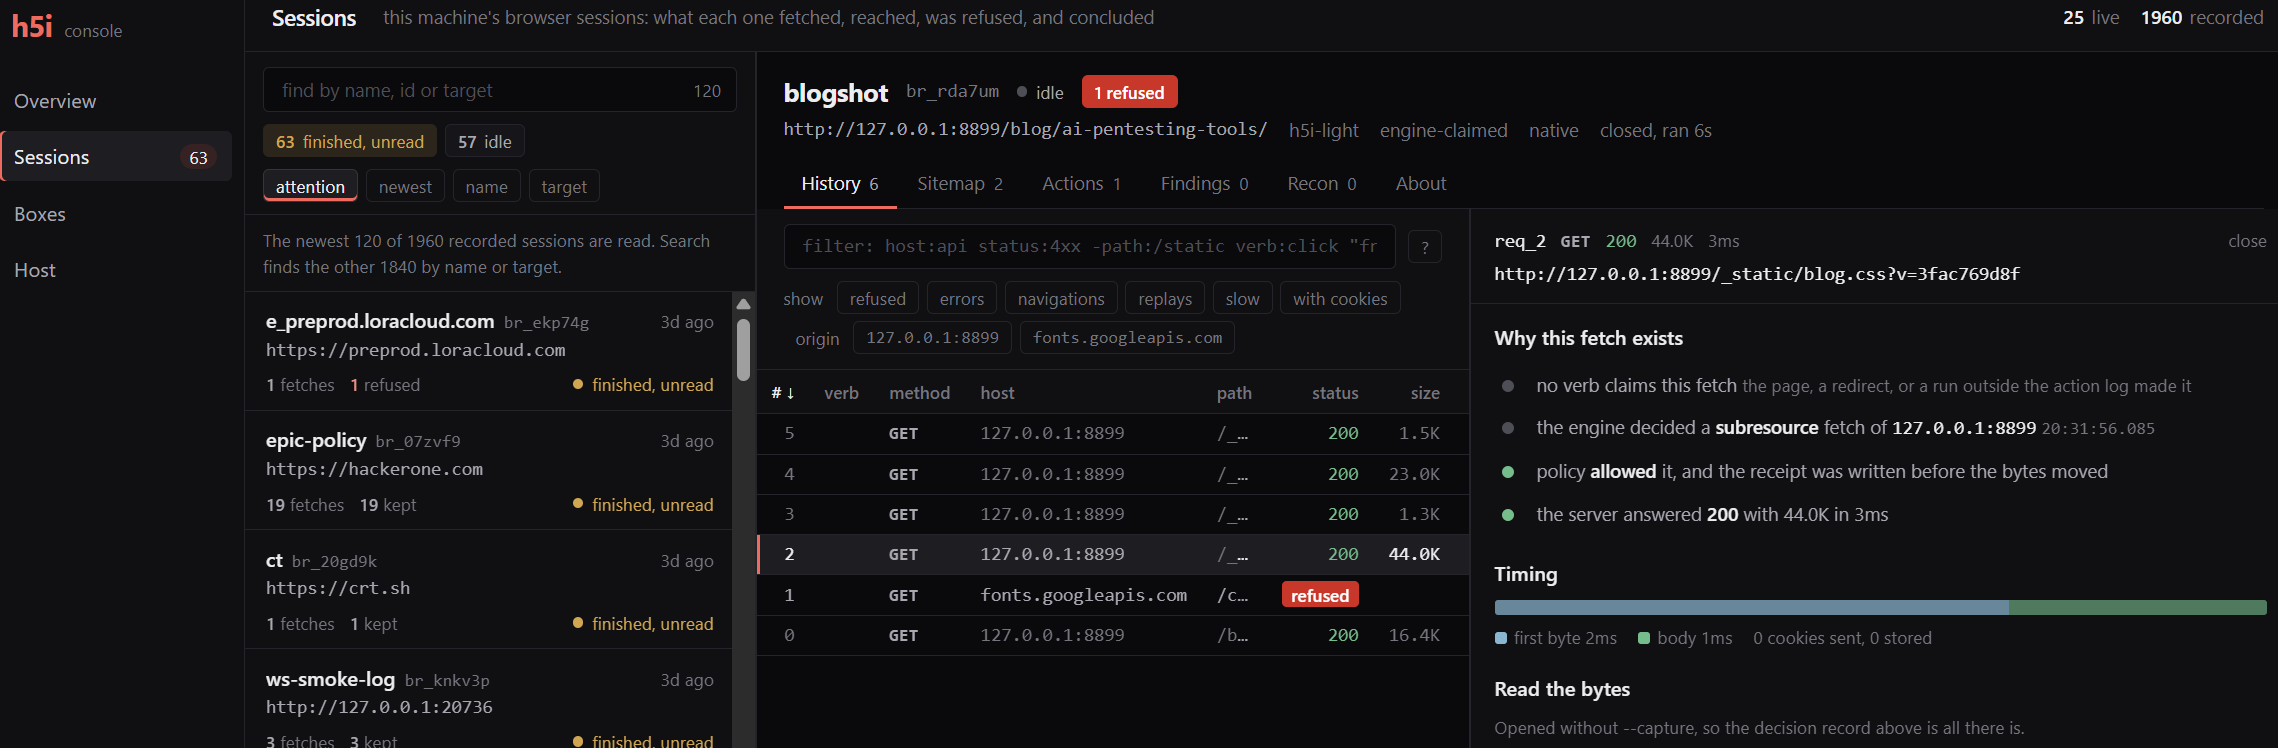
Watch it all from the host with h5i ui:
<p align="center">
<img src="./docs/_static/sandbox-ui-demo.png" alt="Watching a sandboxed browser session from the host" width="99%" />
</p>
---
3. Pro: build on h5i-app
Red-teaming finds the bugs you did not anticipate. h5i-app is a Rust web
framework for proving, in Lean 4, the properties you can state.
The kernel is one function that decides what a command does. This one, from the
calculator tutorial, keeps one
number per user:
Aeneas translates it to Lean, where theorems about it are ordinary Lean:
See crates/h5i-app for the full kernel, the axum
ser it, and the proof workflow, and TRUST.md
for exactly what is proven and what is assumed.
---
4. Tutorial
---
5. Documentation
man h5i: full command referencecurl -fsSL -o ~/.local/share/man/man1/h5i.1: install the man page---
6. FAQ
<details>
<summary>What is h5i?</summary>
h5i is an open-source workspace for building secure web applications. Theh5i CLI is a red-teaming tool for AI agents. It drives a target through its
own lightweight Rust browser, or through a capture proxy in front of Chromium,
and lets the agent capture, inspect, replay, and compare the HTTP traffic from
policy-controlled, auditable, sandboxed sessions. h5i-app is a Rust web
framework whose application logic is proven in Lean 4.
</details>
<details>
<summary>Do I need h5i-app to red-team, or the h5i CLI to use h5i-app?</summary>
No. The CLI tests any running web application, whatever it is built on.h5i-app is a crate you add to a Rust project and needs no h5i binary. They
meet when an agent builds an application on h5i-app inside an h5i sandbox and
red-teams it from the same box.
</details>
<details>
<summary>What does h5i-app actually prove?</summary>
Charon and Aeneas translate the kernel, the SQL planner and compiler, the JSON
writer, and the token codec to Lean, and every theorem is about that extracted
code. Proven: properties of transition, that compiled statements touch only
the tenant's rows, and that an in kept by accepted writes holds in every
database state and every snapshot loaded back, for every order in which
requests commit. Trusted, not proven: axum, PostgreSQL's statement semantics,
the HMAC key, the clock, and the translation tools. TRUST.md
has the full list.
</details>
<details>
<summary>Why use h5i instead of Playwright or Puppeteer?</summary>
Use Playwright or Puppeteer when maximum compatibility with complex websites is
the priority. Use h5i when you want lower resource use, direct network controls,
a complete session record, built-in HTTP testing tools, or a sandbox for the
browser and agent.
</details>
<details>
<summary>Is h5i a replacement for Burp Suite?</summary>
Not for every use case. h5i is useful when an AI agent needs to browse an
application and capture, edit, replay, and compare its HTTP traffic through one
interface. Its nati needs no proxy; the optional agent-browser lane
creates and configures a per-session proxy and CA. Burp Suite remains better
suited to mature manual workflows, automated scanning, extensions, and
low-le testing.
</details>
<details>
<summary>Does h5i work on every website?</summary>
No. h5i works best for content-hea and common browser interactions.
For sites that need Chromium, run h5i browser proxy <url> and open the
printed command with agent-browser, or run Chromium inside an h5i sandbox.
Linux trusts the session CA. macOS passes --ignore-https-errors.
</details>
<details>
<summary>Is h5i sandboxed by default?</summary>
The browser uses lightweight process isolation when a. For stronger
isolation, place the browser or the agent's entire workflow inside a supervised
network sandbox, container, or microVM.
</details>
<details>
<summary>Can h5i prevent prompt injection?</summary>
No browser can reliably detect or prevent every prompt injection. h5i reduces
the potential impact by treating page content as untrusted, restricting network
and filesystem access, isolating credentials, and recording the resulting
actions for review.
</details>
<details>
<summary>Can the agent see my passwords or cookies?</summary>
The agent can reference a named credential without reading its value, or a
human can take control to log in. The authenticated session continues without
returning the password or cookie to the model.
</details>
<details>
<summary>Does h5i keep my data local?</summary>
h5i has no hosted service and stores its sessions locally. Browser traffic still
goes to websites you allow, and model traffic goes to your configured model
provider.
</details>
---
7. License
Apache-2.0. See LICENSE.
---
8. Contributors
<a href="
<img src=" alt="h5i contributors" />
</a>
项目信息
开发语言:Rust
Star 数:674
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An agent-native web security workspace. Find vulnerabilities through red-teaming. Formally verify properties of Rust codes in Lean 4.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | h5i - An agent-native web security workspace. Find vulne |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:39:55 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 212 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |