 CTF思路
点击放大
StegCracker - Steganography brute-force utility to uncover hidde
项目说明
StegCracker
![Build Status]()
![PyPI ]()
![codecov]()
![pulls]()
Steganography brute-force utility to unco data inside files. <br>
Looking for the Docker repository? You can find it here
Deprecation
Stop wasting time and CPU, use stegseek instead! Not con? Look at these benchmarks (stolen with love):
| password | Line | Stegseek v0.4 | Stegcracker 2.0.9 | Stegbrute v0.1.1 (-t 8) |
|-------------|-------------|---------------|-------------------|-------------------------|
| "cassandra" | 1 000 | 0.9s | 3.1s | 0.7s |
| "kupal" | 10 000 | 0.9s | 14.4s | 7.1s |
| "sagar" | 100 000 | 0.9s | 2m23.0s | 1m21.9s |
| "budakid1" | 1 000 000 | 0.9s | [p] 23m50.0s | 13m45.7s |
| "␣␣␣␣␣␣␣1" | 14 344 383 | 1.9s | [p] 5h41m52.5s | [p] 3h17m38.0s |
While I' building this tool it is and always will built on bad foundations. StegCracker
started out as a dirty hack for a problem which didn't have any good or easy to use solutions, it's
biggest limiting factor however is that it relies on just spamming thousand of subprocess calls per second
which (despite being optimized slightly with multiple threads) is just horrible for performance.
So, as a result, after three years of managing the project I' to
pass on the torch and officially
retire the project. Thanks for the support and thank you for building a better :tada:
Usage
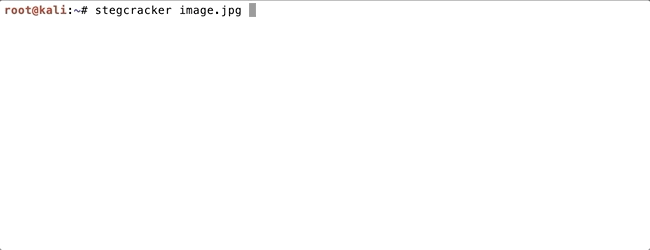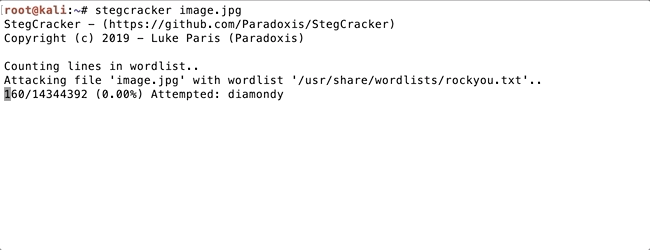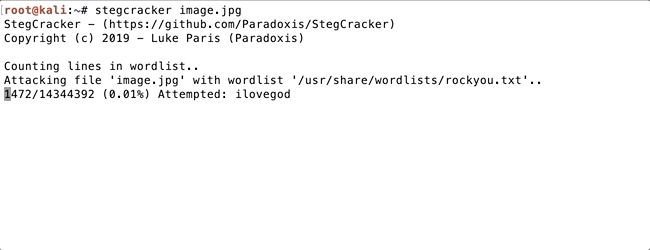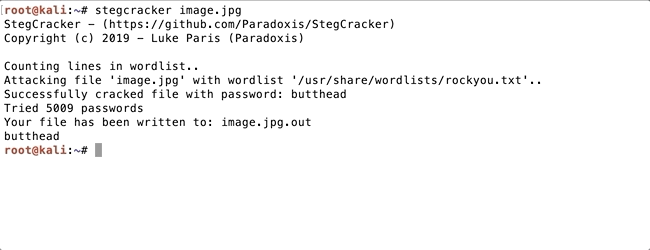
Using stegcracker is simple, pass a file to it as it's first parameter and
optionally pass the path to a wordlist of passwords to try as it's second
parameter. If you don't specify the wordlist, the tool will try to use the
built-in rockyou.txt wordlist which ships with Kali Linux. If you are running a
different distribution, you can download the rockyou wordlist
here.
Or using Docker:
Requirements
The program requires the steghide binary, and Python 3.6 or higher to be installed. If
python 3.6 is not installed, check out this
guide on how to do so. Steghide can be installed by using the following command (Kali Linux):
Installation
To install StegCracker, run the following command:
Or pull the latest docker image:
Updating
To update StegCracker, simply pass
-U to the installation command:Example
!demo
FAQ / Troubleshooting
* I can't install the tool with pip3, but python 3.6+ is installed
* Your pip binary might be using a different of Python. Try installing it
directly through Python like so (replace "X" with your minor , eg: python3.6):
python3.X -m pip install -U stegcracker
* I installed the tool, but when I run stegcracker it just returns 'command not found'
* Chances are your Python's bin directory is not in your PATH en .
As a dirty fix you could add the following to your ~/.bashrc file: alias stegcracker='python3 -m stegcracker'
* I'm using StegCracker 1.X, how do I upgrade?
* If you're upgrading StegCracker from the original 1.X release, please
remove the existing first using: sudo rm --force $(which stegcracker)
* I want to run an older of StegCracker, how do I obtain a copy?
* While I recommended using the latest and greatest , you might want
to install an older of StegCracker. You can do this
by checking out the releases
page. _(Note: all issues or pull requests regarding this will be be ignored)_.
* Can I run this tool on other Linux distro's?
* As long as you have a valid of Python 3.6 and steghide in your path
it *should* work. Please note that the tool has officially been tested on
Kali Linux, all other platforms might be unstable. If you find a bug on
another distro, please submit an issue and I'll see what I can do
_(but do fill in the template as well)_.
* Can I run StegCracker on Windows?
* As far as I know there aren't any official steghide releases for Windows,
so as far as I'm aware: no
License
Copyright 2020 - Luke Paris (Paradoxis)
Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction,
including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to
do so, subject to the following conditions:
The abo notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND
NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF
OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
项目信息
开发语言:Python
Star 数:604
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Steganography brute-force utility to uncover hidden data inside files展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | StegCracker - Steganography brute-force utility to uncover hidde |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:40:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 341 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |