 CTF思路
点击放大
PinCTF - Using Intel's PIN tool to solve CTF problems
项目说明
PinCTF
This tool is designed to use Intel's Pin Tool to instrument reverse engineering binaries and count instructions.
This tool is designed to use instruction counting as an avenue for Side Channel Analysis. By counting the number of instruction exeuted in a gi engineering program we can guess (Sometimes) that the more instructions that are executed per input, the closer we are to the flag.
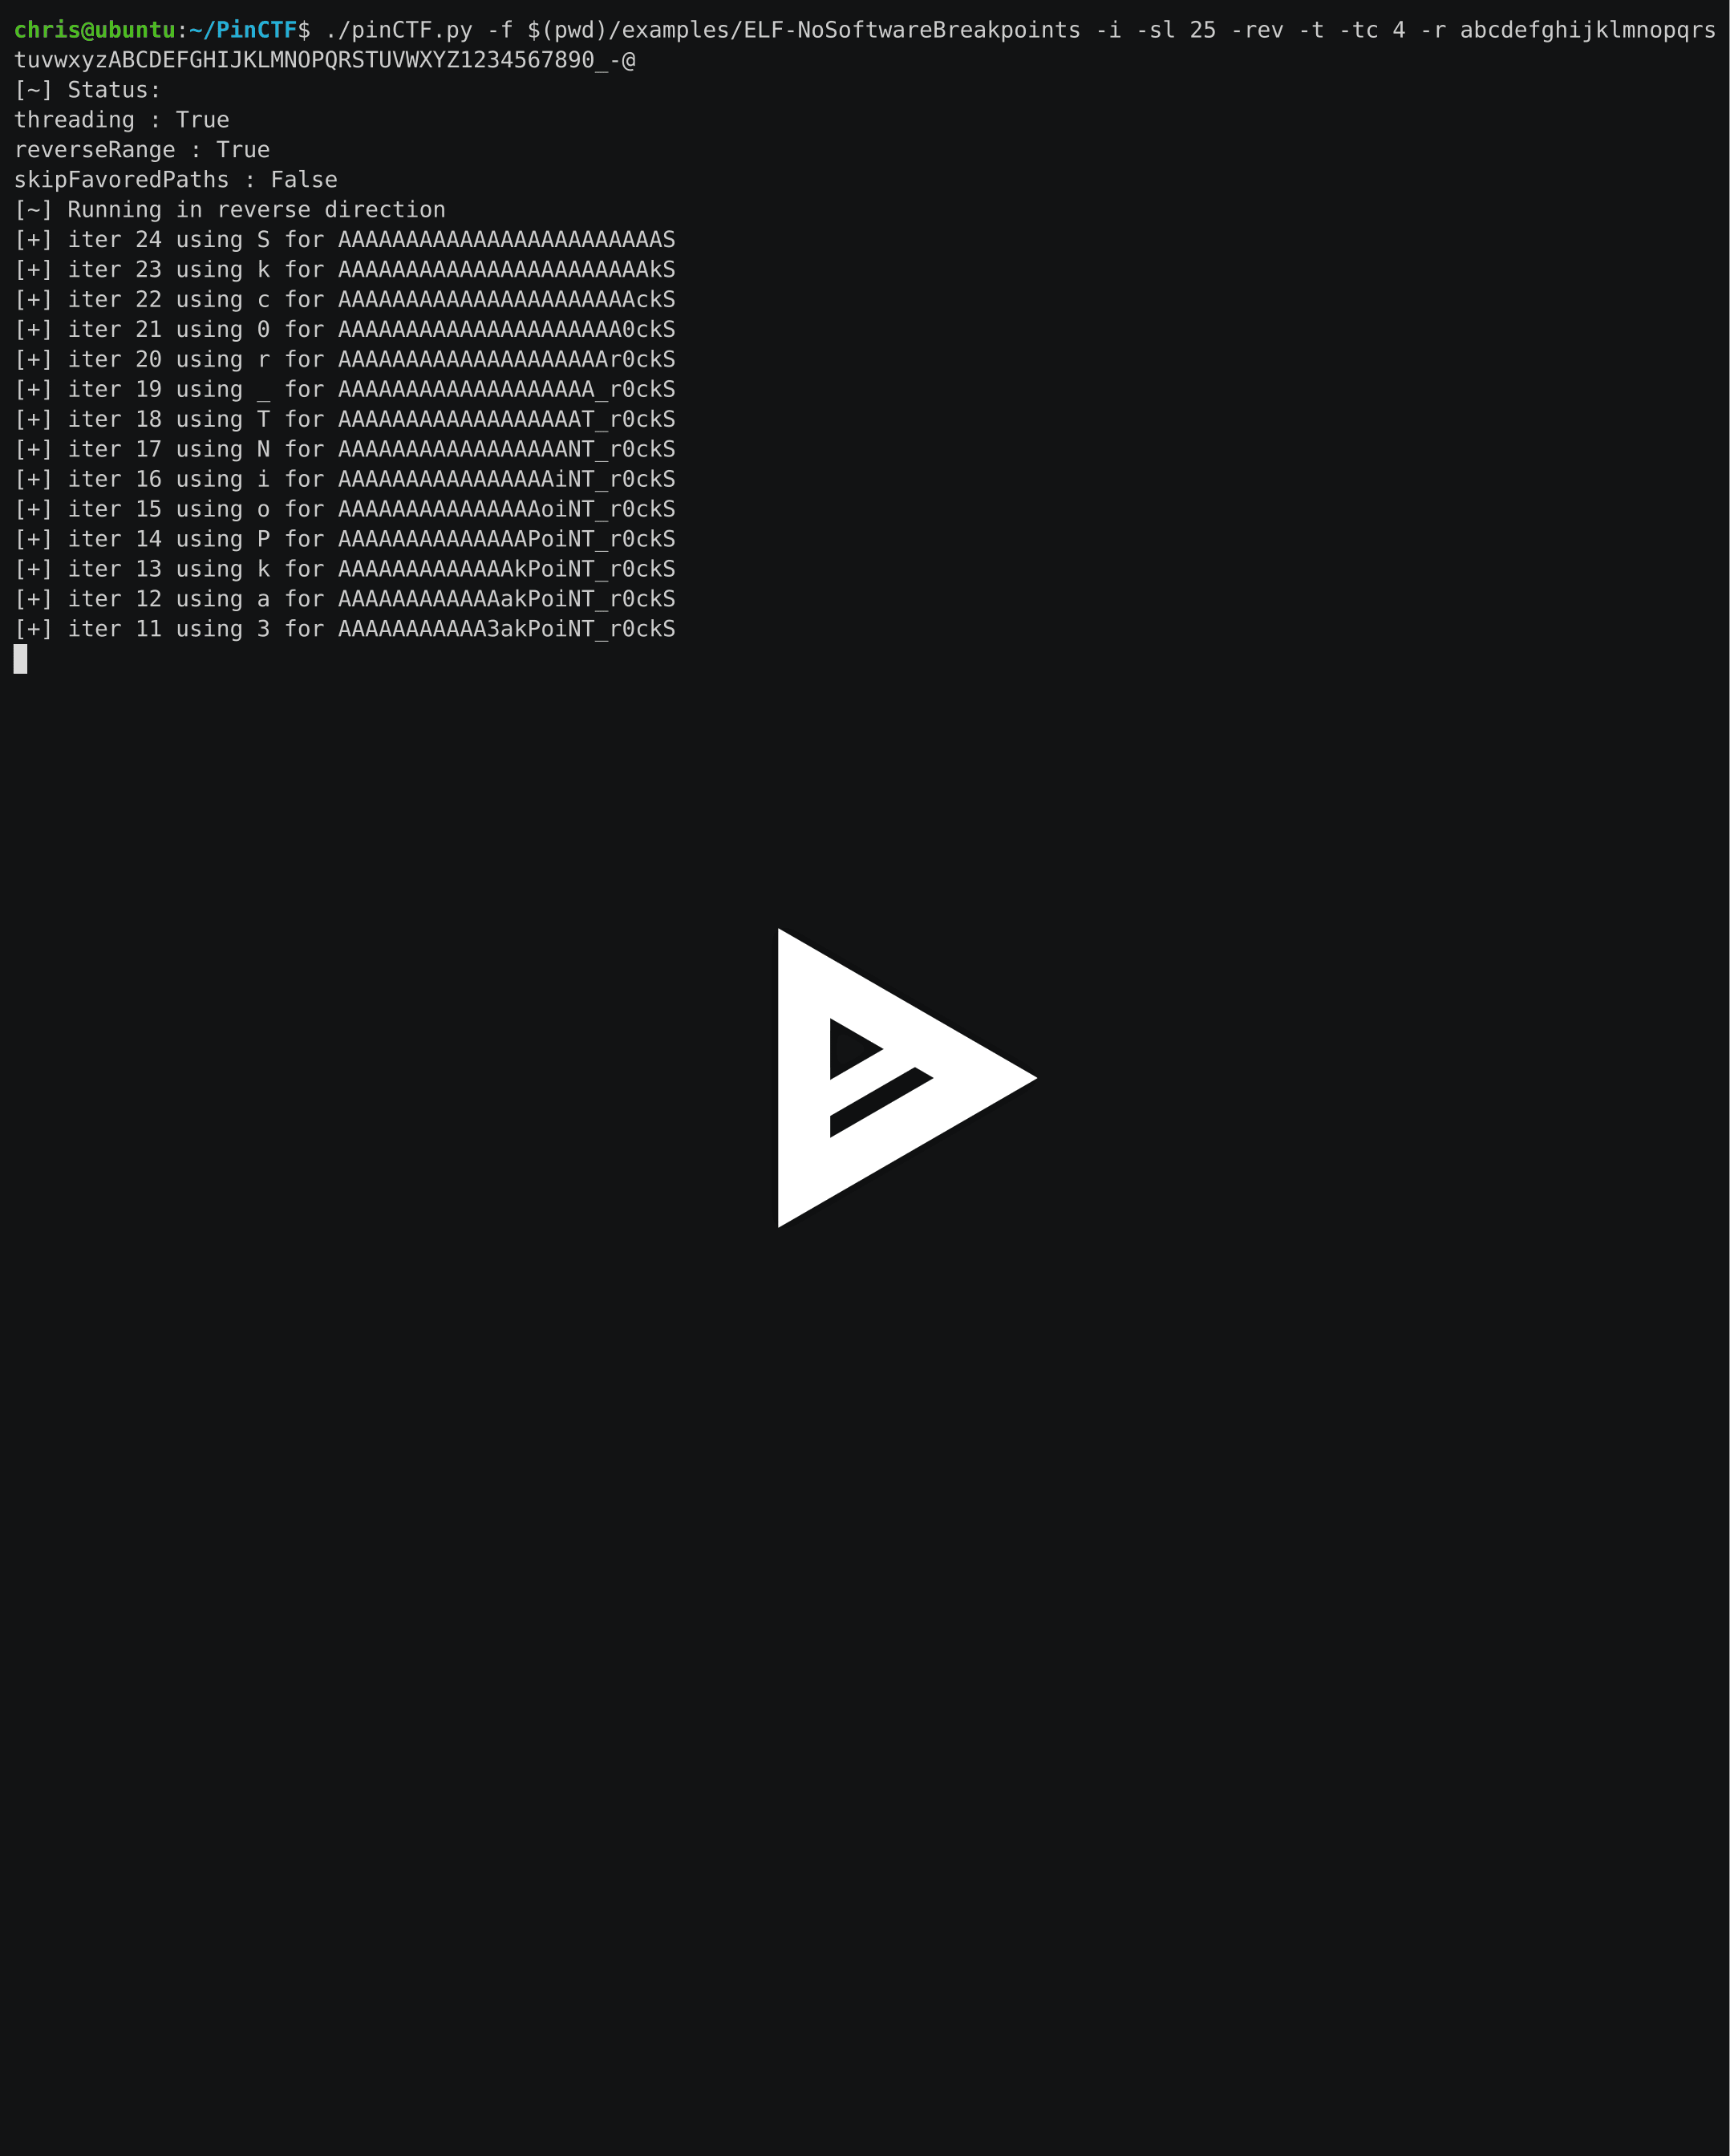
![asciicast]()
Install Pin
Included in this repo is a script for pulling down Intel's PIN and instructions for building it on Ubuntu 16.04.
Running PinCTF
PinCTF is implemented as a python script wrapping PIN. It will execute a pin command then read from PIN's produced *inscount.out* file
To compare instruction counts to length use the -il or -al commands
The -c command is used to specifyhow many A's to test
Now we know we that the flag is 28 characters long and we can start looking for a flag of 28 characters.
Once you' a length that seems to work you can use pin to change each value testing for instruction changes
The -sl flag can be used to determine the length of the initial seed, and the -r flag can be used to choose what range to iterate over
Script tricks for PIN
This process is pretty slow and can be sped up with threading. The -t (--threading) flag will enable threading and -tc represents the thread count
Some ctf binaries will input backwards to throw off fuzzers. using the -rev flag PinCTF is able to alter the input backwards
项目信息
开发语言:Python
Star 数:506
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Using Intel's PIN tool to solve CTF problems展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | PinCTF - Using Intel's PIN tool to solve CTF problems |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:41:14 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 143 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |