 CTF思路
点击放大
tulip - Network analysis tool for Attack Defence CTF
项目说明
🌷 Tulip
Tulip is a flow analyzer meant for use during Attack / Defence CTF competitions. It allows players to easily find some traffic related to their service and automatically generates python snippets to replicate attacks.
Origins
Tulip was de by Team Europe for use in the first International Cyber Security Challenge. The project is a fork of flower, but it contains quite some changes:
* New front-end (typescript / react / tailwind)
* New ingestor code, based on gopacket
* IPv6 support
* impro and tagging system.
* Deep links for easy collaboration
* Added an http decoding pass for compressed data
* Synchronized with Suricata.
* Flow diffing
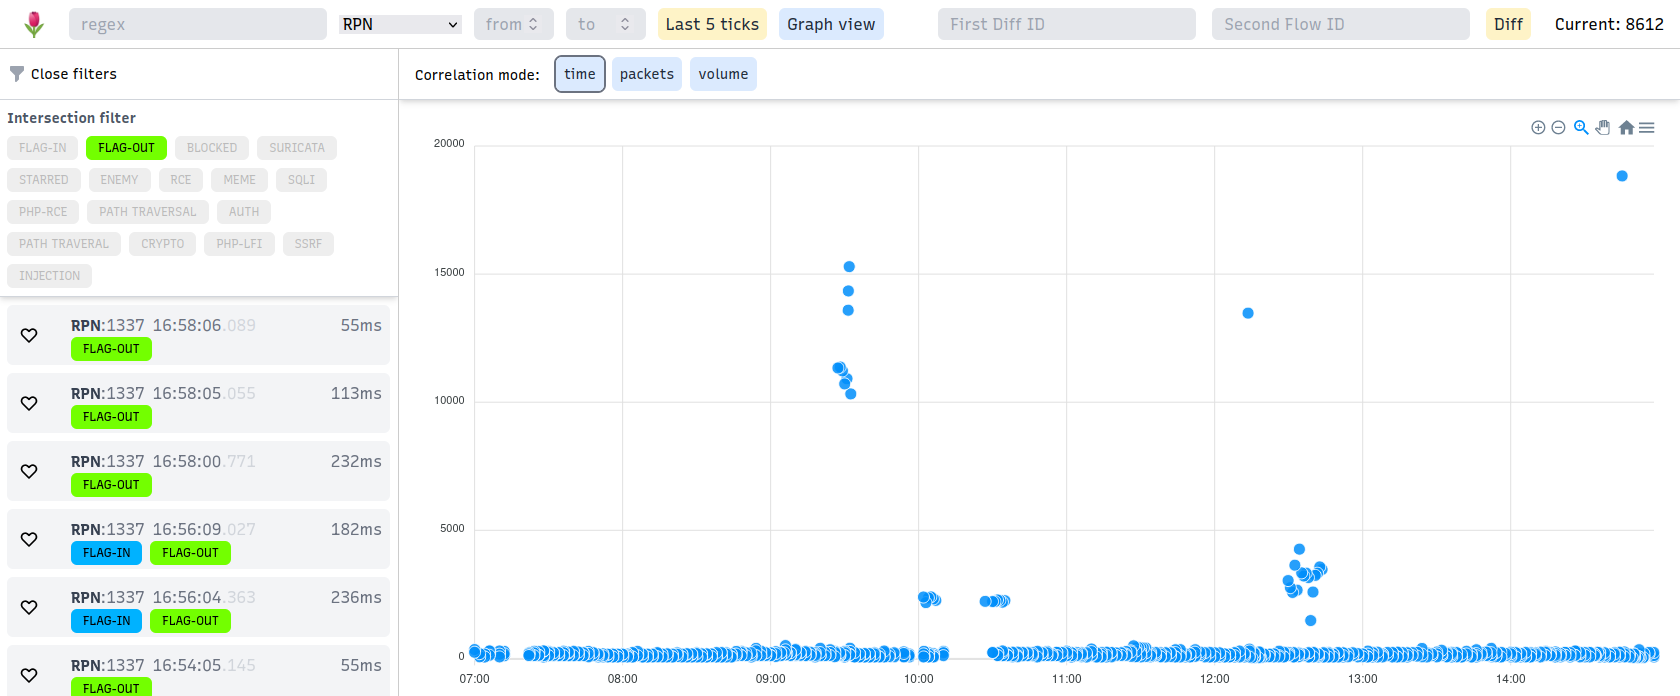
* Time and size-based plots for correlation.
* Linking HTTP sessions together based on cookies (Experimental*, disabled by default)
* PCAP-o with BPF filtering support**
\* - to enable, add -experimental after ./assembler in docker-compose.yml
\*\* - to enable, configure PCAP-o server (e.g. pcap-broker as suggested in PR 24) and set PCAP_O (and BPF if necessary) in .env
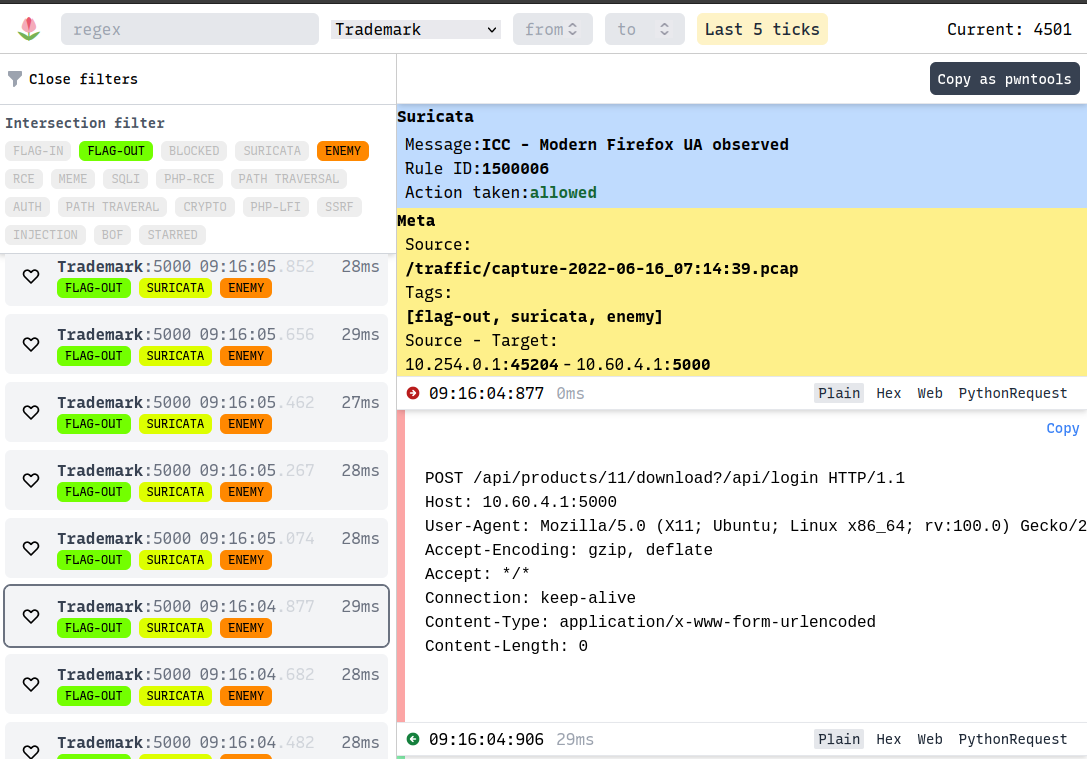
Screenshots


Configuration
Before starting the stack, edit
services/api/configurations.py:You can also edit this during the CTF, just rebuild the api service:
Usage
The stack can be started with docker-compose, after creating an .env file. See .en as an example of how to configure your en.
To ingest traffic, it is recommended to create a shared bind mount with the docker-compose. One con way to set this up is as follows:
1. On the , start a rotating packet sniffer (e.g. tcpdump, suricata, ...)
2. Using rsync, copy complete captures to the machine running tulip (e.g. to /traffic)
3. Add a bind to the assembler service so it can read /traffic
> (Just change TRAFFIC_DIR_HOST in .env)
The ingestor will use inotify to watch for new pcap's and suricata logs. No need to set a chron job.
Suricata synchronization
Run in Docker
Configure SURICATA_DIR_HOST in .env.
Create some rules (404 for testing):
After that run (default config for eve.json logging was good enough):
Metadata
Tags are read from the metadata field of a rule. For example, here's a simple rule to detect a path tra:
Once this rule is seen in traffic, the path_tra tag will automatically be added to the filters in Tulip.
> [!NOTE]
>
> After editing Suricata rules (renaming or id change) please:
>
> Remove old logs: rm ${SURICATA_DIR_HOST}/log/* (otherwise old signatures will be repopulated).
>
> Restart Docker containers.
>
> If database was only restarted (not dropped), try cleaning tags/signatures manually.
eve.json
Suricata alerts are read directly from the
eve.json file. Because this file can get quite when all extensions are enabled, it is recommended to strip the config down a fair bit. For example:Sessions with matched alerts will be highlighted in the front-end and include which rule was matched.
Security
Your Tulip instance will probably contain sensitive CTF information, like flags stolen from your machines. If you expose it to the internet and other people find it, you risk losing additional flags. It is recommended to host it on an internal network (for instance behind a VPN) or to put Tulip behind some form of authentication.
Contributing
If you have an idea for a new feature, bug fixes, UX impro, or other contributions, feel free to open a pull request or create an issue!
Credits
Tulip was written by and , with additional help from . Thanks to our fellow Team Europe players and coaches for testing, feedback and suggestions. Finally, thanks to the team behind flower for opensourcing their tooling.
项目信息
开发语言:Python
Star 数:495
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Network analysis tool for Attack Defence CTF展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | tulip - Network analysis tool for Attack Defence CTF |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:41:17 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 344 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |