 CTF思路
点击放大
writeups - Writeups for vulnerable machines.
项目说明
📖 ReadMe
![License: CC BY-SA 4.0]()
<a name="contents"></a>
🔖 Contents
* ⚙️ Phase 0: Recon
* ⚙️ Phase 1: Enumerate
* ⚙️ Phase 2: Exploit
* ⚙️ Phase 3: PrivEsc
* 📊 Counts
* 📊 Top Categories
* 📊 Top Ports/Protocols/Services
* 📊 Top TTPs
* ⚙️ Enumerate
* ⚙️ Exploit
* ⚙️ PrivEsc
* 🔑 Credentials
* 🔑 Hashes
<a name="methodology"></a>
☀️ Methodology ↟
<a name="mrecon"></a>
⚙️ Phase #0: Recon 🡑
Goal: to scan all ports on <targetip>
Process:
* enumerate_nmap_initial
* enumerate_nmap_tcp
* enumerate_nmap_udp
<a name="menumerate"></a>
⚙️ Phase #1: Enumerate 🡑
Goal: to find service and details
Process:
* find ttps for open ports
* start with weird services
* identify installed software and
* find critical c
* enumerate more common services - smb/ftp
* enumerate services with large attack like http at the end
<a name="mexploit"></a>
⚙️ Phase #2: Exploit 🡑
Goal: gain interacti on <targetip>
Process:
* debug a exploits for open ports
<a name="mprivesc"></a>
⚙️ Phase #3: PrivEsc 🡑
Goal: gain elevated pri on <targetip>
Process:
* debug a exploits or misconfigurations
* for nix, use linux smart enum
* for windows, use winpeas
<a name="stats"></a>
☀️ Stats ↟
📊 Counts 🡑
| # | TryHackMe | HackTheBox | | OSCPlike | Owned |
|:--------:|:---------------:|:----------------:|:-----------------:|:-----------------:|:-----------------:|
| Total |
1/591 (0.17%) | 25/303 (8.25%) | 24/725 (3.31%) | 46/254 (18.11%) | 50/1619 (3.09%) || Windows |
0/0 (0.00%) | 12/82 (14.63%) | 0/2 (0.00%) | 12/39 (30.77%) | 12/84 (14.29%) || *nix |
0/0 (0.00%) | 13/221 (5.88%) | 24/723 (3.32%) | 34/177 (19.21%) | 37/944 (3.92%) || OSCPlike |
0/38 (0.00%) | 25/94 (26.60%) | 21/122 (17.21%) | | 46/254 (18.11%) |<a name="topcategories"></a>
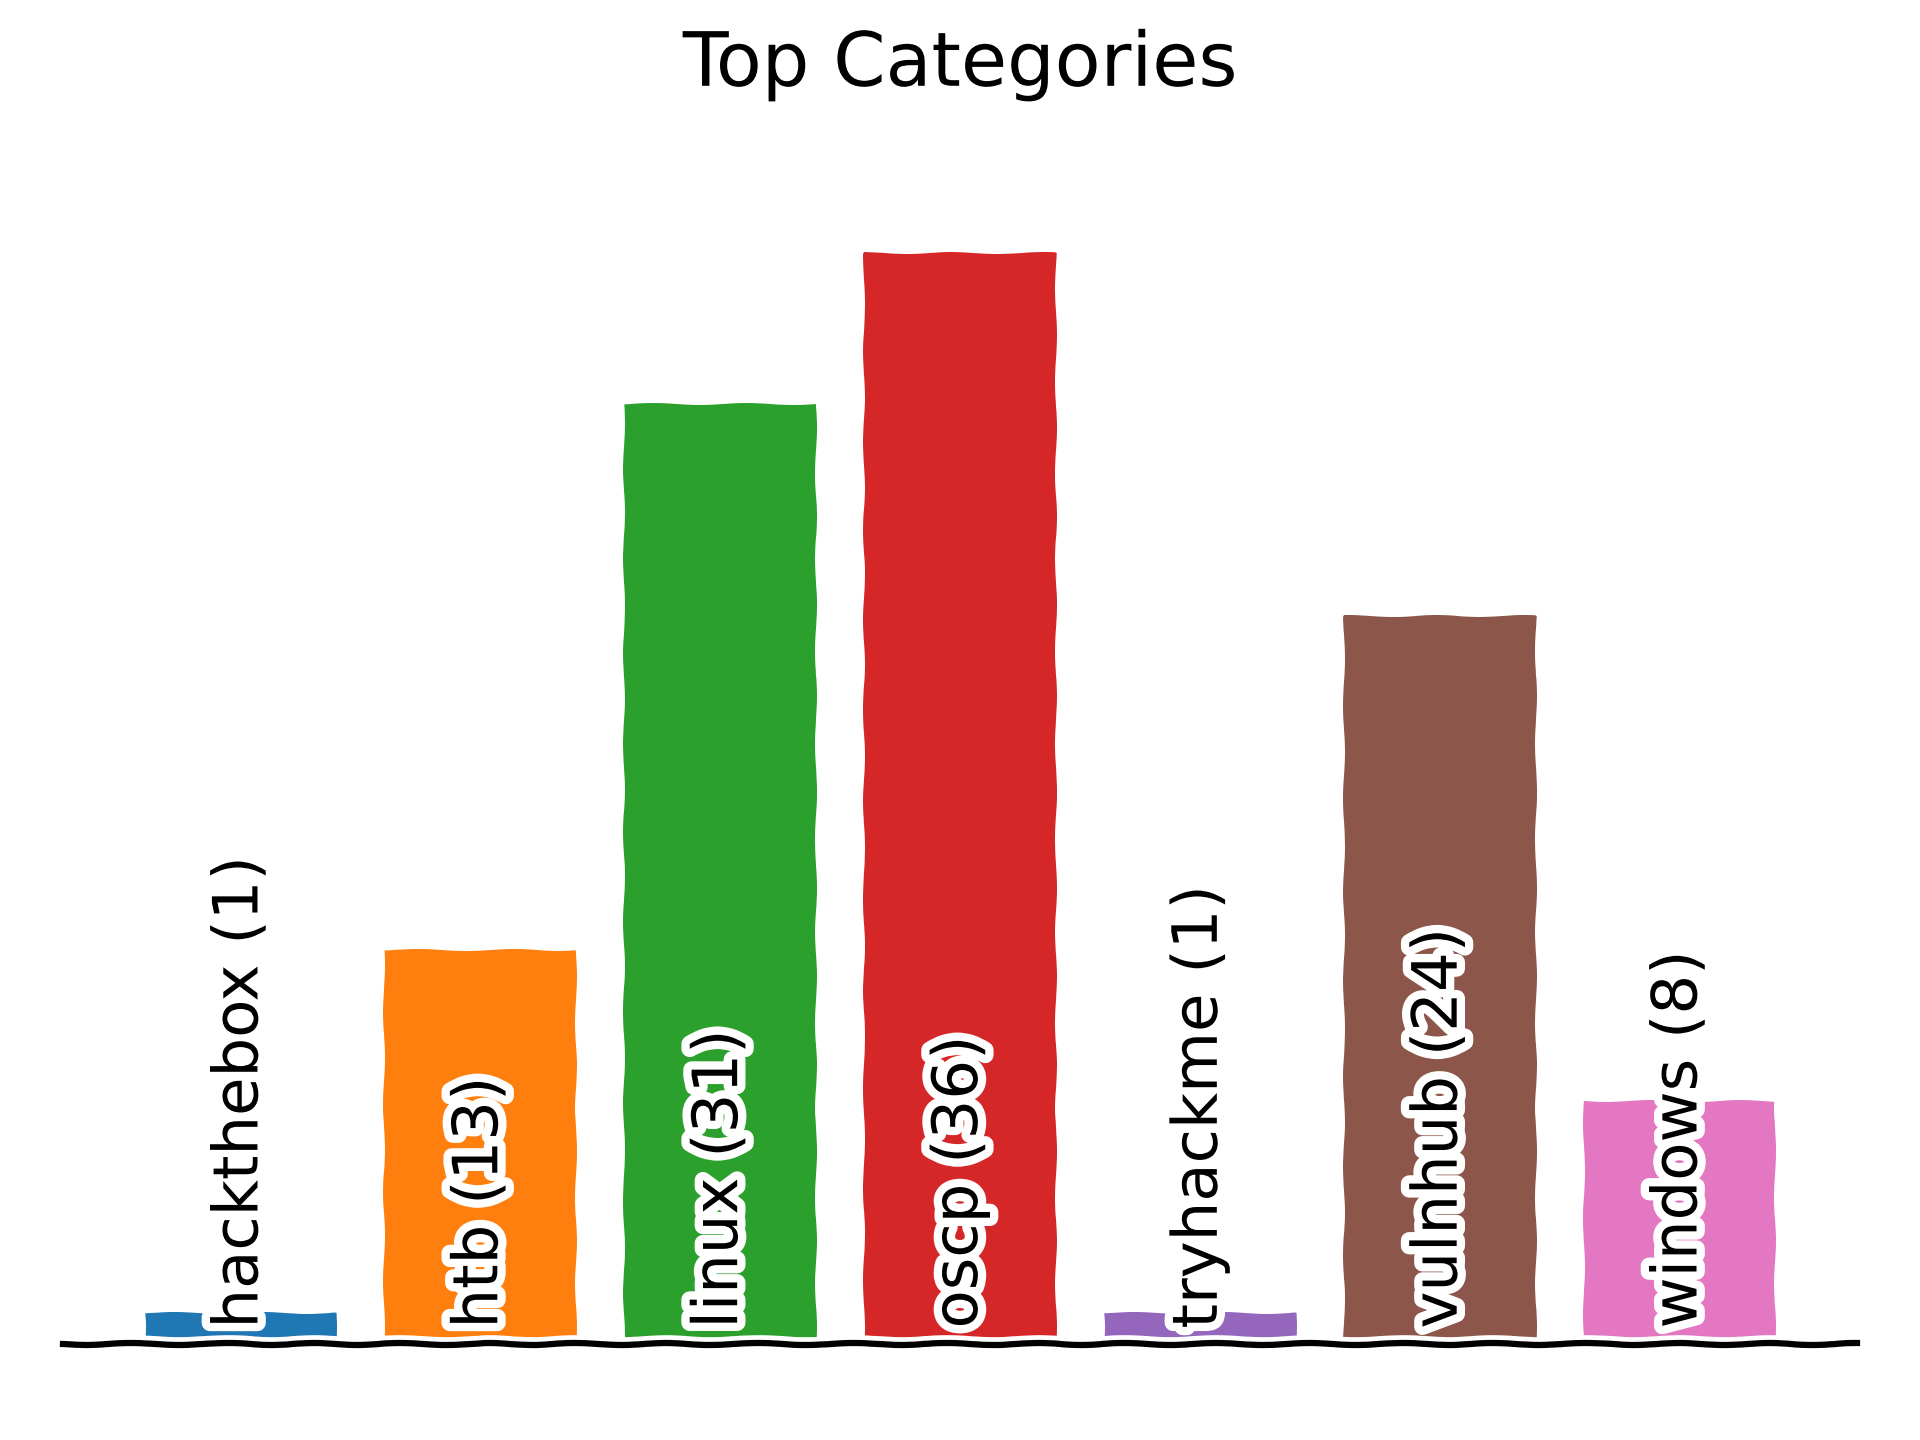
📊 Top Categories 🡑
<img src="./top_categories.png" height="320" />
<a name="topportsprotocolsservices"></a>
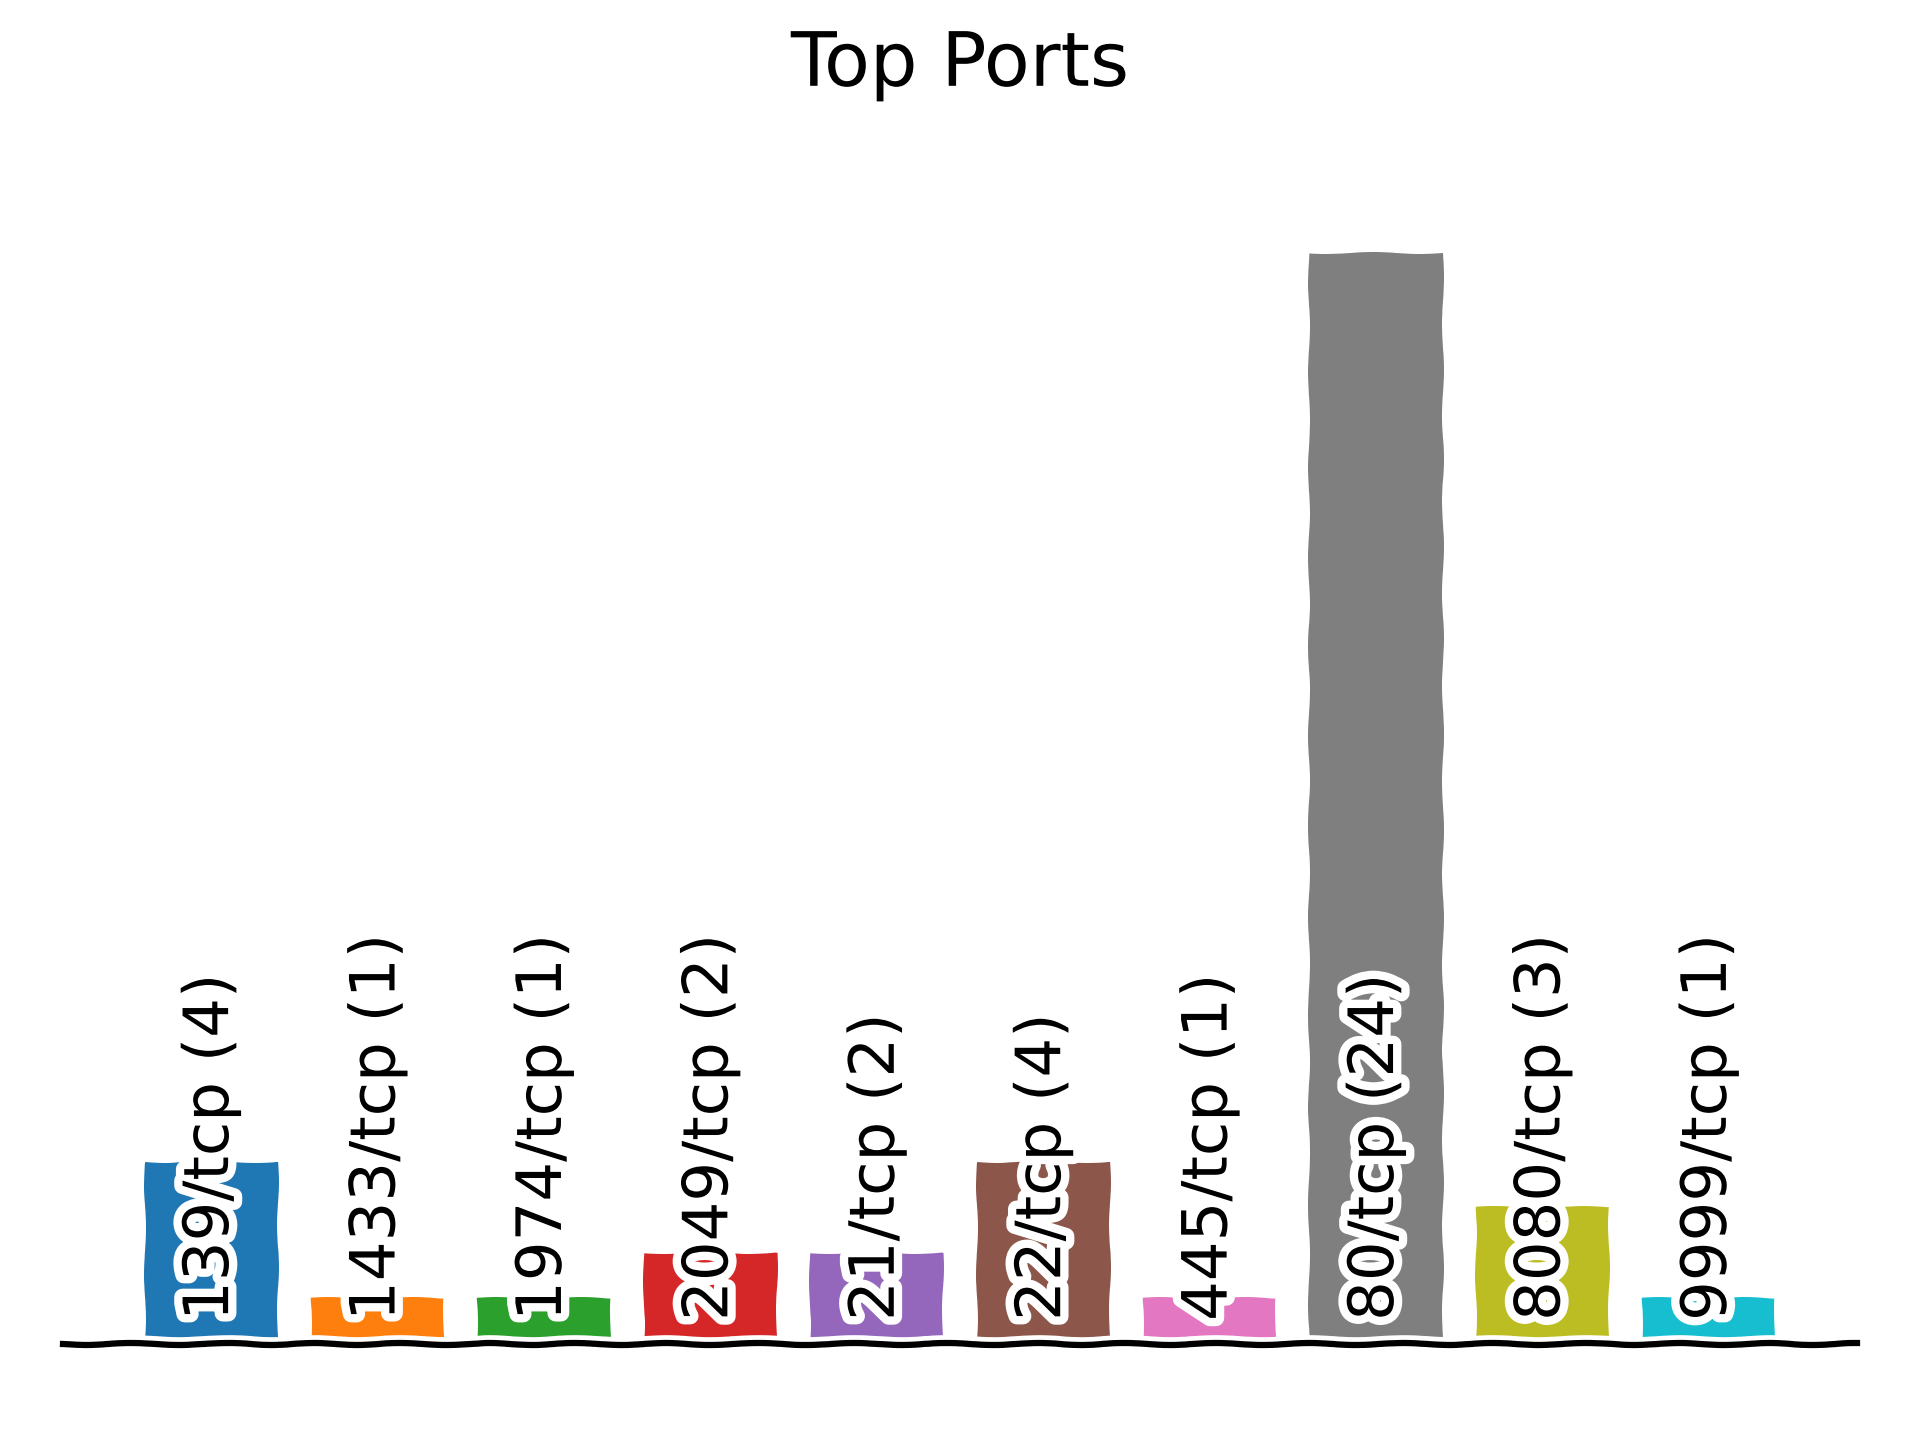
📊 Top Ports/Protocols/Services 🡑
<img src="./top_ports.png" height="320" />
---
<img src="./top_protocols.png" height="320" />
---
<img src="./top_services.png" height="320" />
<a name="topttps"></a>
📊 Top TTPs 🡑
<img src="./top_ttps_enumerate.png" height="320" />
---
<img src="./top_ttps_exploit.png" height="320" />
---
<img src="./top_ttps_privesc.png" height="320" />
<a name="mapping"></a>
⚡ Mapping ↟
| # | Port | Service | TTPs | TTPs - ITW |
|---|------|-----------|------|------------|
| 1. |
21/tcp | ftp/Microsoft ftpd<br /><br />ftp/ 2.3.5 | enumerate_proto_ftp | enumerate_proto_ftp, exploit_ftp_anonymous, exploit_ftp_web_root || 2. |
22/tcp | ssh/OpenSSH 5.9p1 Debian 5ubuntu1 (Ubuntu Linux; protocol 2.0)<br /><br />ssh/OpenSSH 5.9p1 Debian 5ubuntu1.10 (Ubuntu Linux; protocol 2.0)<br /><br />ssh/OpenSSH 6.6.1p1 Ubuntu 2ubuntu2.8 (Ubuntu Linux; protocol 2.0)<br /><br />ssh/OpenSSH 6.7p1 Debian 5+deb8u3 (protocol 2.0) | enumerate_proto_ssh | enumerate_proto_ssh, exploit_defaultcreds, exploit_ssh_authorizedkeys, exploit_ssh_bruteforce, pri, pri, pri || 3. |
23/tcp | | enumerate_proto_telnet | || 4. |
25/tcp | | enumerate_proto_smtp | || 5. |
53/tcp | | enumerate_proto_dns | || 6. |
79/tcp | | enumerate_proto_finger | || 7. |
80/tcp | http/2.4.18 ((Ubuntu))<br /><br />http/Apache httpd<br /><br />http/Apache httpd 2.0.52 ((CentOS))<br /><br />http/Apache httpd 2.2.15 ((CentOS) DAV/2 PHP/5.3.3)<br /><br />http/Apache httpd 2.2.21 ((FreeBSD) mod_ssl/2.2.21 OpenSSL/0.9.8q DAV/2 PHP/5.3.8)<br /><br />http/Apache httpd 2.2.22 ((Ubuntu))<br /><br />http/Apache httpd 2.2.8 ((Ubuntu) PHP/5.2.4-2ubuntu5.6 with Suhosin-Patch)<br /><br />http/Apache httpd 2.4.18 ((Ubuntu))<br /><br />http/Apache httpd 2.4.25 ((Debian))<br /><br />http/Apache httpd 2.4.29<br /><br />http/Apache httpd 2.4.29 ((Ubuntu))<br /><br />http/Apache httpd 2.4.34 ((Ubuntu))<br /><br />http/Apache httpd 2.4.41 ((Ubuntu))<br /><br />http/Apache httpd 2.4.7 ((Ubuntu))<br /><br />http/HttpFileSer 2.3<br /><br />http/Microsoft IIS httpd 6.0<br /><br />http/Microsoft IIS httpd 7.5 | enumerate_app_apache, enumerate_app_apache_tomcat, enumerate_app_coldfusion_files, enumerate_app_coldfusion_, enumerate_app_drupal, enumerate_app_joomla, enumerate_app_phpmyadmin, enumerate_app_prtg, enumerate_app_webmin, enumerate_app_wordpress, enumerate_proto_http, enumerate_proto_webdav | enumerate_app_wordpress, enumerate_proto_http, exploit_cmdexec, exploit_command_injection, exploit_credsreuse, exploit_hfs_cmd_exec, exploit_iis_asp_re, exploit_iis_webdav, exploit_lotuscms, exploit_pchart, exploit_php_fileupload, exploit_php_fileupload_bypass, exploit_php_re, exploit_python_re, exploit_shellshock, exploit_sqli, exploit_ssh_pri, exploit_wordpress_defaultcreds, exploit_wordpress_plugin, exploit_wordpress_plugin_acti, exploit_wordpress_plugin_hellodolly, exploit_wordpress_template, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri, pri || 8. |
111/tcp | | enumerate_proto_nfs, enumerate_proto_rpc | || 9. |
135/tcp | | enumerate_proto_rpc | || 10. |
139/tcp | netbios-ssn/Microsoft Windows netbios-ssn<br /><br />netbios-ssn/Samba smbd 3.X - 4.X (workgroup: WORKGROUP) | enumerate_app_powershell_history, enumerate_proto_smb, enumerate_proto_smb_anonymous_access, exploit_smb_ms08_067, exploit_smb_ms17_010 | exploit_smb_ms08_067, exploit_smb_ms17_010, exploit_smb_nullsession, exploit_smb_usermap, exploit_smb_web_root || 11. |
161/tcp | | enumerate_proto_snmp | || 12. |
389/tcp | | enumerate_proto_ldap | || 13. |
443/tcp | ssl/https/Apache/1.3.20 (Unix) (Red-Hat/Linux) mod_ssl/2.8.4 OpenSSL/0.9.6b | enumerate_app_apache, enumerate_app_apache_tomcat, enumerate_app_coldfusion_files, enumerate_app_coldfusion_, enumerate_app_drupal, enumerate_app_joomla, enumerate_app_phpmyadmin, enumerate_app_prtg, enumerate_app_webmin, enumerate_app_wordpress, enumerate_proto_http, enumerate_proto_webdav | exploit_modssl, pri || 14. |
445/tcp | microsoft-ds/Windows Server 2019 Standard 17763 microsoft-ds | enumerate_app_powershell_history, enumerate_proto_smb, enumerate_proto_smb_anonymous_access, exploit_smb_ms08_067, exploit_smb_ms17_010 | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, pri || 15. |
636/tcp | | enumerate_proto_ldap | || 16. |
1337/tcp | http/Apache httpd 2.4.7 ((Ubuntu)) | | exploit_credsreuse, exploit_sqli, pri, pri, pri || 17. |
1433/tcp | ms-sql-s/Microsoft SQL Server 14.00.1000.00 | enumerate_proto_mssql, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig | enumerate_app_powershell_history, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell || 18. |
1521/tcp | | enumerate_proto_oracle, enumerate_proto_postgres | || 19. |
1974/tcp | | | pri, pri, pri || 20. |
2049/tcp | nfs_acl/2-3 (RPC #100227)<br /><br />nfs_acl/3 (RPC #100227) | enumerate_proto_nfs | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri, pri || 21. |
3000/tcp | http/Node.js Express framework | | exploit_credsreuse, exploit_mongodb, exploit_nodejs, pri || 22. |
3232/tcp | | enumerate_proto_distcc | || 23. |
3306/tcp | | enumerate_proto_mysql | || 24. |
6660/tcp | | enumerate_app_unrealirc | || 25. |
6661/tcp | | enumerate_app_unrealirc | || 26. |
6662/tcp | | enumerate_app_unrealirc | || 27. |
6663/tcp | | enumerate_app_unrealirc | || 28. |
6664/tcp | | enumerate_app_unrealirc | || 29. |
6665/tcp | | enumerate_app_unrealirc | || 30. |
6666/tcp | | enumerate_app_unrealirc | || 31. |
6667/tcp | | enumerate_app_unrealirc | || 32. |
6668/tcp | | enumerate_app_unrealirc | || 33. |
6669/tcp | | enumerate_app_unrealirc | || 34. |
7000/tcp | | enumerate_app_unrealirc | || 35. |
8080/tcp | http/Apache httpd 2.2.21 ((FreeBSD) mod_ssl/2.2.21 OpenSSL/0.9.8q DAV/2 PHP/5.3.8)<br /><br />http/Apache httpd 2.4.29 ((Ubuntu))<br /><br />http/Apache httpd 2.4.43 ((Win64) OpenSSL/1.1.1g PHP/7.4.6) | enumerate_app_apache, enumerate_app_apache_tomcat, enumerate_app_coldfusion_files, enumerate_app_coldfusion_, enumerate_app_drupal, enumerate_app_joomla, enumerate_app_phpmyadmin, enumerate_app_prtg, enumerate_app_webmin, enumerate_app_wordpress, enumerate_proto_http, enumerate_proto_rdp, enumerate_proto_webdav | enumerate_proto_http, exploit_bash_re, exploit_cloudme_bof, exploit_gymsystem_rce, exploit_php_webshell, exploit_phptax, pri, pri, pri || 36. |
9999/tcp | abyss? | | pri, pri || 37. |
10000/tcp | http/SimpleHTTPServer 0.6 (Python 2.7.3) | | exploit_bof || 38. |
27017/tcp | | enumerate_app_mongo | || 39. |
28017/tcp | | enumerate_app_mongo | |<a name="machines"></a>
💥 Machines ↟
| # | Name | Infra | Killchain | TTPs |
|:---:|:--------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------:|:---------------------------------------------------------------------------:|:--------------------------------------------------------------------------------------------------------------------------------------:|:-------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------:|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100"/> |
enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri || 2. | Bashed<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#118 | <img src=" width="100" height="100"/> |
enumerate_proto_http, exploit_python_re, pri, pri || 3. | Billy Madison: 1.1 | vh#161 | <img src=" width="100" height="100"/> |
pri, pri, pri || 4. | Blocky<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#48 | <img src=" width="100" height="100"/> |
enumerate_app_wordpress, exploit_wordpress_plugin, exploit_credsreuse, pri || 5. | Blue<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#51 | <img src=" width="100" height="100"/> |
exploit_smb_ms17_010 || 6. | Brainpan: 1 | vh#51 | <img src=" width="100" height="100"/> |
exploit_bof, pri, pri || 7. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100"/> |
enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri || 8. | Buff<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#263 | <img src=" width="100" height="100"/> |
enumerate_proto_http, exploit_gymsystem_rce, exploit_cloudme_bof || 9. | Cronos<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#11 | <img src=" width="100" height="100"/> |
exploit_sqli, pri || 10. | DC: 6 | vh#315 | <img src=" width="100" height="100"/> |
enumerate_app_wordpress, exploit_wordpress_plugin_acti, pri, pri, pri || 11. | Devel<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#3 | <img src=" width="100" height="100"/> |
exploit_ftp_anonymous, exploit_ftp_web_root, exploit_iis_asp_re, pri || 12. | Escalate_Linux: 1 | vh#323 | <img src=" width="100" height="100"/> |
exploit_python_re, pri, pri || 13. | FristiLeaks: 1.3 | vh#133 | <img src=" width="100" height="100"/> |
exploit_php_fileupload, exploit_php_fileupload_bypass, pri, pri || 14. | Grandpa<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#13 | <img src=" width="100" height="100"/> |
exploit_iis_webdav, pri || 15. | Granny<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#14 | <img src=" width="100" height="100"/> |
exploit_iis_webdav, pri || 16. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100"/> |
enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri || 17. | hackfest2016: Sedna | vh#181 | <img src=" width="100" height="100"/> |
exploit_php_fileupload, exploit_php_re, pri, pri, pri || 18. | HackLAB: | vh#48 | <img src=" width="100" height="100"/> |
exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri || 19. | hackme: 1 | vh#330 | <img src=" width="100" height="100"/> |
exploit_php_fileupload, exploit_php_re, pri || 20. | IMF: 1 | vh#162 | <img src=" width="100" height="100"/> |
exploit_php_fileupload_bypass, pri || 21. | InfoSec Prep: OSCP | vh#508 | <img src=" width="100" height="100"/> |
enumerate_proto_http, exploit_ssh_pri, pri || 22. | Kioptrix: 2014 (#5) | vh#62 | <img src=" width="100" height="100"/> |
exploit_pchart, exploit_phptax, pri || 23. | Kioptrix: Level 1 (#1) | vh#22 | <img src=" width="100" height="100"/> |
exploit_modssl, pri || 24. | Kioptrix: Level 1.1 (#2) | vh#23 | <img src=" width="100" height="100"/> |
exploit_sqli, exploit_cmdexec, pri || 25. | Kioptrix: Level 1.2 (#3) | vh#24 | <img src=" width="100" height="100"/> |
exploit_lotuscms, pri, pri || 26. | Kioptrix: Level 1.3 (#4) | vh#25 | <img src=" width="100" height="100"/> |
exploit_sqli, exploit_credsreuse, pri, pri, pri || 27. | Lame<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#1 | <img src=" width="100" height="100"/> |
exploit_smb_usermap || 28. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100"/> |
enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri || 29. | Legacy<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#2 | <img src=" width="100" height="100"/> |
exploit_smb_ms08_067 || 30. | Lin.Security: 1 | vh#244 | <img src=" width="100" height="100"/> |
exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri || 31. | Lord Of The Root: 1.0.1 | vh#129 | <img src=" width="100" height="100"/> |
exploit_sqli, exploit_credsreuse, pri, pri, pri || 32. | Mirai<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#64 | <img src=" width="100" height="100"/> |
exploit_defaultcreds, pri || 33. | Misdirection: 1 | vh#371 | <img src=" width="100" height="100"/> |
exploit_php_webshell, exploit_bash_re, pri, pri || 34. | Moria: 1.1 | vh#187 | <img src=" width="100" height="100"/> |
pri || 35. | Mr-Robot: 1 | vh#151 | <img src=" width="100" height="100"/> |
exploit_php_re, pri, pri || 36. | Node: 1 | vh#252 | <img src=" width="100" height="100"/> |
exploit_nodejs, exploit_credsreuse, exploit_mongodb, pri || 37. | Optimum<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#6 | <img src=" width="100" height="100"/> |
exploit_hfs_cmd_exec, pri || 38. | Shocker<br/><img src=" width="59" height="59"/><br/><img src=" width="59" height="20"/> | htb#108 | <img src=" width="100" height="100"/> |
exploit_shellshock, pri || 39. | Year of the Fox | tryhackme#yotf | <img src=" width="100" height="100"/> |
enumerate_proto_http, exploit_command_injection, pri |<a name="ttps"></a>
☢️ TTPs ↟
<a name="enumerate"></a>
⚙️ Enumerate 🡑
<a name="enumerate_app_apache"></a>
#### enumerate_app_apache ⇡
---
<a name="enumerate_app_apache_tomcat"></a>
#### enumerate_app_apache_tomcat ⇡
[+]
---
<a name="enumerate_app_coldfusion_files"></a>
#### enumerate_app_coldfusion_files ⇡
look for a sub directories and files on a coldfusion install
[+]
---
<a name="enumerate_app_coldfusion_"></a>
#### enumerate_app_coldfusion_ ⇡
find out the coldfusion install
[+] (pg42)
---
<a name="enumerate_app_drupal"></a>
#### enumerate_app_drupal ⇡
[+]
---
<a name="enumerate_app_joomla"></a>
#### enumerate_app_joomla ⇡
[+]
---
<a name="enumerate_app_mongo"></a>
#### enumerate_app_mongo ⇡
---
<a name="enumerate_app_nodejs"></a>
#### enumerate_app_nodejs ⇡
---
<a name="enumerate_app_pfsense"></a>
#### enumerate_app_pfsense ⇡
---
<a name="enumerate_app_phpmyadmin"></a>
#### enumerate_app_phpmyadmin ⇡
---
<a name="enumerate_app_powershell_history"></a>
#### enumerate_app_powershell_history ⇡
For certain accounts (like sql_svc) that are both user and service accounts, we can look at the user's PowerShell history and find interesting information.
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="enumerate_app_prtg"></a>
#### enumerate_app_prtg ⇡
---
<a name="enumerate_app_unrealirc"></a>
#### enumerate_app_unrealirc ⇡
[+]
---
<a name="enumerate_app_webmin"></a>
#### enumerate_app_webmin ⇡
---
<a name="enumerate_app_wordpress"></a>
#### enumerate_app_wordpress ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Blocky | htb#48 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin, exploit_credsreuse, pri |
| 2. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
| 3. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
| 4. | DC: 6 | vh#315 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin_acti, pri, pri, pri |
| 5. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="enumerate_file_modified_time_window"></a>
#### enumerate_file_modified_time_window ⇡
find files modified within a time window
[+]
---
<a name="enumerate_nmap_initial"></a>
#### enumerate_nmap_initial ⇡
run nmap initial scans
[+]
[+]
[+]
[+]
---
<a name="enumerate_nmap_tcp"></a>
#### enumerate_nmap_tcp ⇡
run nmap full tcp scans
[+]
[+]
[+]
[+]
---
<a name="enumerate_nmap_udp"></a>
#### enumerate_nmap_udp ⇡
run nmap full udp scans
[+]
[+]
[+]
[+]
---
<a name="enumerate_proto_distcc"></a>
#### enumerate_proto_distcc ⇡
---
<a name="enumerate_proto_dns"></a>
#### enumerate_proto_dns ⇡
---
<a name="enumerate_proto_finger"></a>
#### enumerate_proto_finger ⇡
---
<a name="enumerate_proto_ftp"></a>
#### enumerate_proto_ftp ⇡
check if is and exploit is a. check if anonymous access is enabled. check if read permission for sensiti. check if write permission within webroot/uploads or other critical directories. check if ftp root directory is also http root directory and upload php reverse shell. remember - binary and ascii transfer mode switch
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
[+]
---
<a name="enumerate_proto_http"></a>
#### enumerate_proto_http ⇡
identify web server, technology, application. identify . run nikto, dirb/dirbuster, gobuster scans. look at robots.txt. look at source code. check for default creds, lfi/rfi, sqli, wordpress
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | InfoSec Prep: OSCP | vh#508 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_ssh_pri, pri |
| 2. | Year of the Fox | tryhackme#yotf | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_command_injection, pri |
| 3. | Buff | htb#263 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_gymsystem_rce, exploit_cloudme_bof |
| 4. | Bashed | htb#118 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_python_re, pri, pri |
| 5. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="enumerate_proto_ldap"></a>
#### enumerate_proto_ldap ⇡
---
<a name="enumerate_proto_mssql"></a>
#### enumerate_proto_mssql ⇡
---
<a name="enumerate_proto_mysql"></a>
#### enumerate_proto_mysql ⇡
---
<a name="enumerate_proto_nfs"></a>
#### enumerate_proto_nfs ⇡
---
<a name="enumerate_proto_oracle"></a>
#### enumerate_proto_oracle ⇡
---
<a name="enumerate_proto_postgres"></a>
#### enumerate_proto_postgres ⇡
---
<a name="enumerate_proto_rdp"></a>
#### enumerate_proto_rdp ⇡
---
<a name="enumerate_proto_rpc"></a>
#### enumerate_proto_rpc ⇡
---
<a name="enumerate_proto_smb"></a>
#### enumerate_proto_smb ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="enumerate_proto_smb_anonymous_access"></a>
#### enumerate_proto_smb_anonymous_access ⇡
open shares, anonymous logins
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="enumerate_proto_smtp"></a>
#### enumerate_proto_smtp ⇡
---
<a name="enumerate_proto_snmp"></a>
#### enumerate_proto_snmp ⇡
---
<a name="enumerate_proto_sql"></a>
#### enumerate_proto_sql ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="enumerate_proto_sql_ssis_dtsconfig"></a>
#### enumerate_proto_sql_ssis_dtsconfig ⇡
The .dtsConfig files are used by SQL Ser Services (SSIS) and can contain plaintext credentials for SQL users.
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="enumerate_proto_ssh"></a>
#### enumerate_proto_ssh ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="enumerate_proto_telnet"></a>
#### enumerate_proto_telnet ⇡
---
<a name="enumerate_proto_webdav"></a>
#### enumerate_proto_webdav ⇡
---
<a name="exploit"></a>
⚙️ Exploit 🡑
<a name="exploit_apache_tomcat"></a>
#### exploit_apache_tomcat ⇡
le Tomcat Web Application Manager to deploy a malicious .war file that spawns a reverse shell
[+]
---
<a name="exploit_bash_re"></a>
#### exploit_bash_re ⇡
spawn a bash reverse shell to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Misdirection: 1 | vh#371 | <img src=" width="100" height="100" /> | exploit_php_webshell, exploit_bash_re, pri, pri |
[+]
[+]
---
<a name="exploit_bof"></a>
#### exploit_bof ⇡
create a bof exploit to execute arbitrary code and gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Brainpan: 1 | vh#51 | <img src=" width="100" height="100" /> | exploit_bof, pri, pri |
---
<a name="exploit_cloudme_bof"></a>
#### exploit_cloudme_bof ⇡
the CloudMe 1.11.12 is to a buffer o that could be used to gain interacti on the target system, possibly with elevated pri
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Buff | htb#263 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_gymsystem_rce, exploit_cloudme_bof |
[+]
---
<a name="exploit_cmdexec"></a>
#### exploit_cmdexec ⇡
execute arbitrary commands via a command execution and gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: Level 1.1 (#2) | vh#23 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_cmdexec, pri |
---
<a name="exploit_coldfusion_dirtra"></a>
#### exploit_coldfusion_dirtra ⇡
coldfusion 8 is to a directory tra and exposes SHA1 hash of the user password
[+]
[+]
---
<a name="exploit_coldfusion_scheduledtasks"></a>
#### exploit_coldfusion_scheduledtasks ⇡
coldfusion 8 allows to obtain remote shell by creating and executing a new scheduled task. this is a post-authentication
[+]
---
<a name="exploit_command_injection"></a>
#### exploit_command_injection ⇡
certain webapps couldbe to command injection text fields
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Year of the Fox | tryhackme#yotf | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_command_injection, pri |
[+]
---
<a name="exploit_credsreuse"></a>
#### exploit_credsreuse ⇡
Reuse credentials already found for a service to interact with another service
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Blocky | htb#48 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin, exploit_credsreuse, pri |
| 2. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
| 3. | Node: 1 | vh#252 | <img src=" width="100" height="100" /> | exploit_nodejs, exploit_credsreuse, exploit_mongodb, pri |
| 4. | Lord Of The Root: 1.0.1 | vh#129 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
| 5. | Kioptrix: Level 1.3 (#4) | vh#25 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
---
<a name="exploit_defaultcreds"></a>
#### exploit_defaultcreds ⇡
Use default credentials to interact with a service
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Mirai | htb#64 | <img src=" width="100" height="100" /> | exploit_defaultcreds, pri |
---
<a name="exploit_drupal_passwordcrack"></a>
#### exploit_drupal_passwordcrack ⇡
Crack a drupal password hash
[+]
---
<a name="exploit_ftp_anonymous"></a>
#### exploit_ftp_anonymous ⇡
Interact with the ftp service using anonymous/any credentials
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Devel | htb#3 | <img src=" width="100" height="100" /> | exploit_ftp_anonymous, exploit_ftp_web_root, exploit_iis_asp_re, pri |
---
<a name="exploit_ftp_web_root"></a>
#### exploit_ftp_web_root ⇡
FTP server's root directory is mapped to the web server's root directory. Upload a reverse shell file native to the web ser ftp server (anonymous login or default creds or creds reuse or some exploit) and trigger it's execution to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Devel | htb#3 | <img src=" width="100" height="100" /> | exploit_ftp_anonymous, exploit_ftp_web_root, exploit_iis_asp_re, pri |
---
<a name="exploit_gpp_groupsxml"></a>
#### exploit_gpp_groupsxml ⇡
the Groups.xml file lists username and encrypted password that can be useful to gain initial access on the target system. access this file via an open ftp/smb share or some other method
[+]
[+]
---
<a name="exploit_gymsystem_rce"></a>
#### exploit_gymsystem_rce ⇡
use /contacts.php to confirm the is 1.0 and fire this exploit to get a pseudo-interacti on the target machine. you can
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Buff | htb#263 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_gymsystem_rce, exploit_cloudme_bof |
[+]
---
<a name="exploit_hfs_cmd_exec"></a>
#### exploit_hfs_cmd_exec ⇡
HFS (HttpFileServer 2.3.x) is to remote command execution
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Optimum | htb#6 | <img src=" width="100" height="100" /> | exploit_hfs_cmd_exec, pri |
[+]
[+]
---
<a name="exploit_iis_asp_re"></a>
#### exploit_iis_asp_re ⇡
use an asp|aspx reverse shell to gain interacti on the target system. useful when Microsoft IIS server is found during enumeration. might need a separate to upload the reverse shell file on target system (use burp to bypass filename filter - re.aspx%00.jpg)
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Devel | htb#3 | <img src=" width="100" height="100" /> | exploit_ftp_anonymous, exploit_ftp_web_root, exploit_iis_asp_re, pri |
[+]
---
<a name="exploit_iis_webdav"></a>
#### exploit_iis_webdav ⇡
multiple iis webda. can use msf exploits windows/iis/iis_webda or windows/iis/iis_webda to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Grandpa | htb#13 | <img src=" width="100" height="100" /> | exploit_iis_webdav, pri |
| 2. | Granny | htb#14 | <img src=" width="100" height="100" /> | exploit_iis_webdav, pri |
[+]
[+]
---
<a name="exploit_lotuscms"></a>
#### exploit_lotuscms ⇡
LotusCMS is to remote code execution
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: Level 1.2 (#3) | vh#24 | <img src=" width="100" height="100" /> | exploit_lotuscms, pri, pri |
[+]
---
<a name="exploit_modssl"></a>
#### exploit_modssl ⇡
Apache mod_ssl < 2.8.7 is to remote code execution
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: Level 1 (#1) | vh#22 | <img src=" width="100" height="100" /> | exploit_modssl, pri |
[+]
[+]
---
<a name="exploit_mongodb"></a>
#### exploit_mongodb ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Node: 1 | vh#252 | <img src=" width="100" height="100" /> | exploit_nodejs, exploit_credsreuse, exploit_mongodb, pri |
---
<a name="exploit_nfs_rw"></a>
#### exploit_nfs_rw ⇡
when an open nfs share is found, look for a mountpoints, mount using nfsv3 so that we can see the real remote uid and gid, create a new user with expected uid, switch user, create the .ssh directory, copy id_rsa.pub to this directory and ssh to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lin.Security: 1 | vh#244 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
| 2. | HackLAB: | vh#48 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
[+]
---
<a name="exploit_nodejs"></a>
#### exploit_nodejs ⇡
inspect source for assets/js/app/controllers/*.js files and look for rest api calls that could leak sensiti
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Node: 1 | vh#252 | <img src=" width="100" height="100" /> | exploit_nodejs, exploit_credsreuse, exploit_mongodb, pri |
---
<a name="exploit_nodejs_deserialize"></a>
#### exploit_nodejs_deserialize ⇡
user input is passed to unserialize() method that could allow remote code execution
[+]
[+]
[+]
[+]
---
<a name="exploit_pchart"></a>
#### exploit_pchart ⇡
the pChart 2.1.3 web application is to directory tra
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: 2014 (#5) | vh#62 | <img src=" width="100" height="100" /> | exploit_pchart, exploit_phptax, pri |
[+]
[+]
---
<a name="exploit_pfsense"></a>
#### exploit_pfsense ⇡
pfsense 2.1.3 is to command injection
[+]
[+]
---
<a name="exploit_php_acs_rfi"></a>
#### exploit_php_acs_rfi ⇡
Ad Comment System 1.0 is to remote file inclusion and command execution attacks
[+]
---
<a name="exploit_php_fileupload"></a>
#### exploit_php_fileupload ⇡
certain poorly de php web applications allow unrestricted file uploads that can be abused to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackme: 1 | vh#330 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri |
| 2. | hackfest2016: Sedna | vh#181 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri, pri, pri |
| 3. | FristiLeaks: 1.3 | vh#133 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_fileupload_bypass, pri, pri |
---
<a name="exploit_php_fileupload_bypass"></a>
#### exploit_php_fileupload_bypass ⇡
add gif file magicbytes GIF891 to a php reverse shell file, rename it to rs.php.gif and upload to bypass upload filter. sometimes, a restrictve waf might still stop file upload. in that case, use a minimal command execution php file with gif magicbytes instead of a full php reverse shell
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | IMF: 1 | vh#162 | <img src=" width="100" height="100" /> | exploit_php_fileupload_bypass, pri |
| 2. | FristiLeaks: 1.3 | vh#133 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_fileupload_bypass, pri, pri |
---
<a name="exploit_php_re"></a>
#### exploit_php_re ⇡
use php reverse shell code with an exploit to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
| 2. | Mr-Robot: 1 | vh#151 | <img src=" width="100" height="100" /> | exploit_php_re, pri, pri |
| 3. | hackme: 1 | vh#330 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri |
| 4. | hackfest2016: Sedna | vh#181 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri, pri, pri |
| 5. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
| 6. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="exploit_php_webshell"></a>
#### exploit_php_webshell ⇡
use the php web shell to execute arbitrary commands and gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Misdirection: 1 | vh#371 | <img src=" width="100" height="100" /> | exploit_php_webshell, exploit_bash_re, pri, pri |
---
<a name="exploit_phptax"></a>
#### exploit_phptax ⇡
the Phptax 0.8 web application is to remote code execution
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: 2014 (#5) | vh#62 | <img src=" width="100" height="100" /> | exploit_pchart, exploit_phptax, pri |
[+]
---
<a name="exploit_prtg_sensors"></a>
#### exploit_prtg_sensors ⇡
execute a reverse shell command through prtg sensor creation dialog and play it to get interacti on the target system
[+]
[+]
[+]
[+]
---
<a name="exploit_psexec_login"></a>
#### exploit_psexec_login ⇡
If credentials for a non-administrative user are a, we can use psexec.py to connect and gain interacti to the target system.
---
<a name="exploit_python_re"></a>
#### exploit_python_re ⇡
use a python reverse shell to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Bashed | htb#118 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_python_re, pri, pri |
| 2. | Escalate_Linux: 1 | vh#323 | <img src=" width="100" height="100" /> | exploit_python_re, pri, pri |
[+]
[+]
---
<a name="exploit_shellshock"></a>
#### exploit_shellshock ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Shocker | htb#108 | <img src=" width="100" height="100" /> | exploit_shellshock, pri |
[+]
[+]
[+]
---
<a name="exploit_smb_ms08_067"></a>
#### exploit_smb_ms08_067 ⇡
(netapi exploit) for microsoft windows xp systems with open smb ports, use the ms08-067 metasploit module [windows/smb/ms08_067_netapi]()
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Legacy | htb#2 | <img src=" width="100" height="100" /> | exploit_smb_ms08_067 |
[+]
[+]
[+]
[+]
[+]
---
<a name="exploit_smb_ms17_010"></a>
#### exploit_smb_ms17_010 ⇡
(eternalblue exploit) for microsoft windows system with smb v1 enbaled, use the metasploit exploit windows/smb/ms17_010_eternalblue
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Blue | htb#51 | <img src=" width="100" height="100" /> | exploit_smb_ms17_010 |
[+]
[+]
[+]
[+]
---
<a name="exploit_smb_nullsession"></a>
#### exploit_smb_nullsession ⇡
smb null sessions leak a lot of sensiti about the target system. it could be useful to access open shares or to get sensiti
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
---
<a name="exploit_smb_usermap"></a>
#### exploit_smb_usermap ⇡
samba 3.0.0 - 3.0.25rc3 is to remote command execution
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lame | htb#1 | <img src=" width="100" height="100" /> | exploit_smb_usermap |
[+]
[+]
---
<a name="exploit_smb_web_root"></a>
#### exploit_smb_web_root ⇡
smb shared directory is mapped to the web server's root directory. read files to obtain sensiti or upload a reverse shell file native to the web server and trigger it's execution to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
---
<a name="exploit_sql_login"></a>
#### exploit_sql_login ⇡
login to the target system using a sql service account
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="exploit_sql_xpcmdshell"></a>
#### exploit_sql_xpcmdshell ⇡
use the SQL xp_cmdshell method to gain command execution on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="exploit_sqli"></a>
#### exploit_sqli ⇡
target system is running a webapp that's to sql injection
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | CronOS | htb#11 | <img src=" width="100" height="100" /> | exploit_sqli, pri |
| 2. | Lord Of The Root: 1.0.1 | vh#129 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
| 3. | Kioptrix: Level 1.3 (#4) | vh#25 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
| 4. | Kioptrix: Level 1.1 (#2) | vh#23 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_cmdexec, pri |
---
<a name="exploit_ssh_authorizedkeys"></a>
#### exploit_ssh_authorizedkeys ⇡
if we ha to a user's .ssh directory, copy our id_rsa.pub file to .ssh/authorized_keys to obtain passwordless ssh access
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lin.Security: 1 | vh#244 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
| 2. | HackLAB: | vh#48 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
---
<a name="exploit_ssh_bruteforce"></a>
#### exploit_ssh_bruteforce ⇡
use hydra to bruteforce ssh password for a know user
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="exploit_ssh_pri"></a>
#### exploit_ssh_pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | InfoSec Prep: OSCP | vh#508 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_ssh_pri, pri |
---
<a name="exploit_ssl_heartbleed"></a>
#### exploit_ssl_heartbleed ⇡
use nmap nse script to confirm heartbleed and then sensepost exploit to dump memory from target system
[+]
---
<a name="exploit_wordpress_defaultcreds"></a>
#### exploit_wordpress_defaultcreds ⇡
target system has wordpress configured with default credentials admin/admin
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="exploit_wordpress_plugin"></a>
#### exploit_wordpress_plugin ⇡
certain wordpress installations might have a /plugins/ directory that could provide source files or leak sensiti
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Blocky | htb#48 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin, exploit_credsreuse, pri |
---
<a name="exploit_wordpress_plugin_acti"></a>
#### exploit_wordpress_plugin_acti ⇡
wordpress plugin Plainview Activity Monitor is to remote command injection
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | DC: 6 | vh#315 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin_acti, pri, pri, pri |
[+]
---
<a name="exploit_wordpress_plugin_hellodolly"></a>
#### exploit_wordpress_plugin_hellodolly ⇡
wordpress plugin Hello Dolly (default on stock wp installs) file hello.php is modified with php reverse shell code to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
| 2. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="exploit_wordpress_template"></a>
#### exploit_wordpress_template ⇡
edit a wordpress template file, like 404.php and add php reverse shell code within it to gain interacti on the target system
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
---
<a name="privesc"></a>
⚙️ PrivEsc 🡑
<a name="pri"></a>
#### pri ⇡
the
anansi_util application has sudo pri. use it to run manual commands and upon error run !/bin/bash to execute root shell | # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Brainpan: 1 | vh#51 | <img src=" width="100" height="100" /> | exploit_bof, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
bash reverse shell command
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackfest2016: Sedna | vh#181 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri, pri, pri |
[+]
[+]
---
<a name="pri"></a>
#### pri ⇡
craft exploit for the buffer o to gain elevated pri
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | IMF: 1 | vh#162 | <img src=" width="100" height="100" /> | exploit_php_fileupload_bypass, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackfest2016: Sedna | vh#181 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
le cronjobs to modify and execute root owned files
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | CronOS | htb#11 | <img src=" width="100" height="100" /> | exploit_sqli, pri |
| 2. | hackfest2016: Sedna | vh#181 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri, pri, pri |
| 3. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
| 4. | Billy Madison: 1.1 | vh#161 | <img src=" width="100" height="100" /> | pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
it would be useful to find root owned cronjob processes
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Bashed | htb#118 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_python_re, pri, pri |
[+]
---
<a name="primp"></a>
#### primp ⇡
a neat trick for ctf boxes is to use user.txt file time as a reference to search for recently modified files
[+]
---
<a name="pri"></a>
#### pri ⇡
race condition that allows breakage of private read-only memory mappings
[+]
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lin.Security: 1 | vh#244 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
certain files when referenced without their complete path, can be misused to gain elevated pri. this can be done by modifying the en path to find the referenced file within a directory under attacker's control and placing a malicious binary within that directory with the same name as the referenced file
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Year of the Fox | tryhackme#yotf | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_command_injection, pri |
[+]
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: 2014 (#5) | vh#62 | <img src=" width="100" height="100" /> | exploit_pchart, exploit_phptax, pri |
---
<a name="pri"></a>
#### pri ⇡
on iis servers, the web.config file stores configuration data for web applications (similar to .htaccess on apacher server). it can contain asp code which will be executed by the web server. use the powershell reverse shell from nishang framework to get a call back from uploaded web.config file
[+]
---
<a name="pring"></a>
#### pring ⇡
allows us to extract administrator tickets and crack those to obtain administrator password
[+]
[+]
[+]
[+]
---
<a name="pri"></a>
#### pri ⇡
Linux Kernel 2.6 < 2.6.19 (White Box 4 / CentOS 4.4/4.5/4.8 / Fedora Core 4/5/6 x86)
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: Level 1.1 (#2) | vh#23 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_cmdexec, pri |
[+]
[+]
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lord Of The Root: 1.0.1 | vh#129 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | InfoSec Prep: OSCP | vh#508 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_ssh_pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: Level 1 (#1) | vh#22 | <img src=" width="100" height="100" /> | exploit_modssl, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | hackfest2016: Quaoar | vh#180 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_defaultcreds, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
| 2. | Escalate_Linux: 1 | vh#323 | <img src=" width="100" height="100" /> | exploit_python_re, pri, pri |
| 3. | DC: 6 | vh#315 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin_acti, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lord Of The Root: 1.0.1 | vh#129 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
| 2. | Kioptrix: Level 1.3 (#4) | vh#25 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lord Of The Root: 1.0.1 | vh#129 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
| 2. | Kioptrix: Level 1.3 (#4) | vh#25 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | HackLAB: | vh#48 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Mr-Robot: 1 | vh#151 | <img src=" width="100" height="100" /> | exploit_php_re, pri, pri |
| 2. | DC: 6 | vh#315 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin_acti, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Misdirection: 1 | vh#371 | <img src=" width="100" height="100" /> | exploit_php_webshell, exploit_bash_re, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
If credentials for an administrative user are a, we can use psexec.py to connect and gain elevated access to the target system.
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Archetype | htb#287 | <img src=" width="100" height="100" /> | enumerate_proto_smb, enumerate_proto_smb_anonymous_access, enumerate_proto_sql, enumerate_proto_sql_ssis_dtsconfig, exploit_sql_login, exploit_sql_xpcmdshell, enumerate_app_powershell_history, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Node: 1 | vh#252 | <img src=" width="100" height="100" /> | exploit_nodejs, exploit_credsreuse, exploit_mongodb, pri |
| 2. | Mr-Robot: 1 | vh#151 | <img src=" width="100" height="100" /> | exploit_php_re, pri, pri |
| 3. | hackme: 1 | vh#330 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_re, pri |
| 4. | Escalate_Linux: 1 | vh#323 | <img src=" width="100" height="100" /> | exploit_python_re, pri, pri |
| 5. | FristiLeaks: 1.3 | vh#133 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_fileupload_bypass, pri, pri |
| 6. | Billy Madison: 1.1 | vh#161 | <img src=" width="100" height="100" /> | pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Kioptrix: Level 1.3 (#4) | vh#25 | <img src=" width="100" height="100" /> | exploit_sqli, exploit_credsreuse, pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | HackLAB: | vh#48 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Moria: 1.1 | vh#187 | <img src=" width="100" height="100" /> | pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Lin.Security: 1 | vh#244 | <img src=" width="100" height="100" /> | exploit_nfs_rw, exploit_ssh_authorizedkeys, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
using sudo to execute programs that run with elevated pri
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Bashed | htb#118 | <img src=" width="100" height="100" /> | enumerate_proto_http, exploit_python_re, pri, pri |
| 2. | LazySysAdmin: 1 | vh#205 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_smb_nullsession, exploit_smb_web_root, exploit_php_re, exploit_credsreuse, exploit_wordpress_template, pri |
| 3. | Kioptrix: Level 1.2 (#3) | vh#24 | <img src=" width="100" height="100" /> | exploit_lotuscms, pri, pri |
| 4. | FristiLeaks: 1.3 | vh#133 | <img src=" width="100" height="100" /> | exploit_php_fileupload, exploit_php_fileupload_bypass, pri, pri |
| 5. | DC: 6 | vh#315 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin_acti, pri, pri, pri |
| 6. | Brainpan: 1 | vh#51 | <img src=" width="100" height="100" /> | exploit_bof, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
being able to edit the /etc/sudoers file to give a user elevated pri
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Blocky | htb#48 | <img src=" width="100" height="100" /> | enumerate_app_wordpress, exploit_wordpress_plugin, exploit_credsreuse, pri |
| 2. | Shocker | htb#108 | <img src=" width="100" height="100" /> | exploit_shellshock, pri |
| 3. | Mirai | htb#64 | <img src=" width="100" height="100" /> | exploit_defaultcreds, pri |
| 4. | Misdirection: 1 | vh#371 | <img src=" width="100" height="100" /> | exploit_php_webshell, exploit_bash_re, pri, pri |
| 5. | Kioptrix: Level 1.2 (#3) | vh#24 | <img src=" width="100" height="100" /> | exploit_lotuscms, pri, pri |
| 6. | BSides : 2018 (Workshop) | vh#231 | <img src=" width="100" height="100" /> | enumerate_proto_ftp, enumerate_proto_ssh, exploit_ssh_bruteforce, enumerate_proto_http, enumerate_app_wordpress, exploit_wordpress_plugin_hellodolly, exploit_php_re, pri, pri |
| 7. | Billy Madison: 1.1 | vh#161 | <img src=" width="100" height="100" /> | pri, pri, pri |
---
<a name="pri"></a>
#### pri ⇡
---
<a name="pri"></a>
#### pri ⇡
[+]
[+]
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Devel | htb#3 | <img src=" width="100" height="100" /> | exploit_ftp_anonymous, exploit_ftp_web_root, exploit_iis_asp_re, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Grandpa | htb#13 | <img src=" width="100" height="100" /> | exploit_iis_webdav, pri |
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Granny | htb#14 | <img src=" width="100" height="100" /> | exploit_iis_webdav, pri |
---
<a name="pri"></a>
#### pri ⇡
---
<a name="pri"></a>
#### pri ⇡
| # | Name | Infra | Killchain | TTPs |
|---|------|-------|-----------|------|
| 1. | Optimum | htb#6 | <img src=" width="100" height="100" /> | exploit_hfs_cmd_exec, pri |
---
<a name="pri"></a>
#### pri ⇡
On a Windows XP system, we can modify the insecurely configured upnphost service to gain elevated pri. This can be done by creating a reverse shell binary and getting it executed by restarting the service.
[+]
---
<a name="tips"></a>
⚡ Tips ↟
bind shell 🡑
buffer o 🡑
file transfers 🡑
heartbleed 🡑
iptables 🡑
lfi/rfi/image upload 🡑
passthehash 🡑
passwords 🡑
persistence 🡑
port forward 🡑
portknock 🡑
restricted shells 🡑
reverse shell 🡑
shellcode 🡑
shellshock 🡑
sql injection 🡑
startup scripts 🡑
stegnography 🡑
tmux shortcuts 🡑
tunneling 🡑
windows useful commands 🡑
<a name="tools"></a>
💥 Tools ↟
burp 🡑
cewl 🡑
fcrackzip 🡑
gobuster 🡑
hashcat 🡑
hydra 🡑
john 🡑
kernel module 🡑
merlin c2 framework 🡑
metasploit 🡑
msfvenom 🡑
netcat 🡑
ncrack 🡑
netdiscover 🡑
nikto 🡑
nmap 🡑
openssl 🡑
searchsploit 🡑
socat 🡑
sqlmap 🡑
steghide 🡑
unicornscan 🡑
wfuzz 🡑
<a name="loot"></a>
🔥 Loot ↟
<a name="credentials"></a>
🔑 Credentials 🡑
| # | Username | Password | Type |
|---|----------|----------|------|
| 1. |
notch | 8YsqfCTn..... | ftp || 2. |
babygirl_@yah...... | ftp || 3. |
eric | ericdoesntdrinkhiso..... | ftp || 4. |
Balrog | Mell.. | ftp || 5. |
eezeepz | keKkeKKeKKeKkE.... | http || 6. |
john | MyNameIsJ... | liggoat || 7. |
robert | ADGAdsafdfwt4gadf.... | liggoat || 8. |
dreg | Mast.. | lotuscms || 9. |
loneferret | starwa.. | lotuscms || 10. |
admin | kEjdbRigfBHUREi.... | mysql || 11. |
john | thiscannotb... | mysql || 12. |
wpdbuser | meErKa.. | mysql || 13. |
mysql | mysql@12... | mysql || 14. |
admin | 3298fj8323j80d.... | mysql || 15. |
wordpress | Oscp1234.. | mysql || 16. |
john | hiroshi.. | mysql || 17. |
root | fuckey.. | mysql || 18. |
Admin | TogieMYSQL123.... | mysql || 19. |
root | darkshad.. | mysql || 20. |
sql_svc | M3g4c0rp... | sql || 21. |
administrator | MEGACORP_4dm.... | ssh || 22. |
notch | 8YsqfCTn..... | ssh || 23. |
pi | raspber.. | ssh || 24. |
fox | 12345.. | ssh || 25. |
eric | triscui.. | ssh || 26. |
anne | prince.. | ssh || 27. |
graham | GSo7isUM... | ssh || 28. |
root | 1234. | ssh || 29. |
admin | thisisalsopw... | ssh || 30. |
fristigod | LetThereBeFri.... | ssh || 31. |
dreg | Mast.. | ssh || 32. |
loneferret | starwa.. | ssh || 33. |
john | MyNameIsJ... | ssh || 34. |
robert | ADGAdsafdfwt4gadf.... | ssh || 35. |
togie | 1234. | ssh || 36. |
bob | secr.. | ssh || 37. |
susan | MySuperS3cretVa.... | ssh || 38. |
insecurity | P.. | ssh || 39. |
smeagol | MyPreciousR... | ssh || 40. |
Ori | span.. | ssh || 41. |
robot | abcdefghijklmnopqrstu..... | ssh || 42. |
mark | 5AYRft73VtFp.... | ssh || 43. |
wpadmin | wpadm.. | ssh || 44. |
root | rootpasswo... | ssh || 45. |
user | letme.. | ssh || 46. |
tomcat | submitthisforpo.... | tomcat || 47. | |
execrab.. | truecrypt || 48. |
rascal | lov. | webapp || 49. |
user1 | hell. | webapp || 50. |
user2 | comman.. | webapp || 51. |
user3 | p.. | webapp || 52. |
test | testte.. | webapp || 53. |
superadmin | Uncracka... | webapp || 54. |
test1 | testte.. | webapp || 55. |
admin | 5afac8d8.. | webapp || 56. |
john | 66lajGGb.. | webapp || 57. |
frodo | iwilltakethe.... | webapp || 58. |
smeagol | MyPreciousR... | webapp || 59. |
aragorn | AndMySwo.. | webapp || 60. |
legolas | AndMyB.. | webapp || 61. |
gimli | AndMyA.. | webapp || 62. |
myP14ceAdm1nAcc0uNT | manchest.. | webapp || 63. |
tom | spongeb.. | webapp || 64. |
mark | snowfla.. | webapp || 65. |
john | enig.. | wordpress || 66. |
mark | helpdesk.. | wordpress || 67. | |
admin:$P$Bx9ohXoC........ | wordpress || 68. |
admin | TogieMYSQL123.... | wordpress || 69. |
elliot | ER28-06.. | wordpress || 70. |
admin | admi. | wordpress |<a name="hashes"></a>
🔑 Hashes 🡑
| # | Hash |
|---|------|
| 1. |
abatchy:$6$xEq/159Q$ScuKnynbwTBdFA4B9w6OqKxQpWPGpofi59McwZQkx72XriPSIrc2ubr16OEBBn0:17238:0:99999:7::: || 2. |
admin:$6$NPXhvENr$yG4a5RpaLpL5UDRRZ3Ts0eZadZfFFbYpI1kyNJp9rND0AySx2FhYSmAuLAli2J/:16757:0:99999:7::: || 3. |
Administrator:500:0a70918d669baeb3148ab:34dec8a1db14cdde2a21967c3c997548::: || 4. |
Administrator:500:c74761604a24f0dfd0a9ba2c30e462cf:d6908f022af0373e9e21b8a241c86dca::: || 5. |
anansi:$6$hblZftkLUb18x/kHupYqQ2qz5O.ek.QcB1lyDGIPE1:15768:0:99999:7::: || 6. |
anne:$6$ChsjoKyY$1uHlk7QUSOmdp4ZdRx/pZp8C8gJAQGu2.8J94U7:0:99999:7::: || 7. |
arrexel:$1$mDpVXKQ/e.S.b.:17504:0:99999:7::: || 8. |
ASPNET:1007:3f71d62ec68a06a39721cb3f54f04a3b:edc0d5506804653f58964a2376bbd769::: || 9. |
Balrog:$6$J6kuCfxq$L5ALsHRYfOu0b.tpeIznf0d44qoFAMn3.:17284:0:99999:7::: || 10. |
billy:$6$eqJNxIDh$oO.ynkHZmLxfr0k8YXHHdbyB4boe2two4HnEiJzzu71QcLqhqnV/iknE/pXdS1:17035:0:99999:7::: || 11. |
bitnamiftp:$6$saPiFTAH$7K09sg5oIfkIs5kuMx1R/Um4HNd8O65wtzdPdP3JeuKbZ4RYBml0THNQ/:16751:0:99999:7::: || 12. |
bob:$6$Kk0DA.6Xha4nL2p5$jq7qoit2l4ckULg1ZxcbL5wUz2Ld2ZUa.RYaIMs.Lma0EFGheX9yCXfKy37K0GsHz50FYIqIESo4QXWL.DYTI0:17721:0:99999:7::: || 13. |
brexit:$6$51s7qYO35OLK9EGZJzDGF9nYaukD3eppHsn2P1ESMr.9rRn/YYO70uiUskfkWP0LyRtTiT1:18048:0:99999:7::: || 14. |
crackmeforpoints:$6$p22wX4fD$RRAamkeGIA56pj4MpM7CbrKPhSh/1upG.54kSph/HSP1LFcn4.2C11cF0R7QmojBqNy5/:17104:0:99999:7::: || 15. |
doomguy:$6$DWqgg./.y1u/xiFBPC0K/essEGOfxSF7ouoqo26wQkA4B2znR:17594:0:99999:7::: || 16. |
dreg:$1$qAc2saWZ$Y567sEs.ql3GMttI6pvoe0:15080:0:99999:7::: || 17. |
eezeepz:$6$djF4bN.s$JWhT7wJo37fgtuJ.be2Q62PnM/AogXuqGa.PgRzrMGv9/Th0aixBXl8Usy9.RkO1ZRAQ/UM3xP7oGWu9zgEIl.:16756:0:99999:7::: || 18. |
eric:$6$b15/PaMU$n.7.u6bJLM/lhb1xF0RcX906O6aIMbP7Xo.:17033:0:99999:7::: || 19. |
fristigod:$6$0WqnZlI/$gIzMByP7rH21W3neA.uHYZZg5aM7gI1xtOj8WwgoK1QgQh2LWL0nQBJau/mGcOSxLbaGJhJjM.6HNJTWsaetf0:16758:0:99999:7::: || 20. |
graham:$6$WF7GkVxM$MOL.cXLpG6UTO0M4exCUFwOEiUhW6bwQa.Frg9CerQbTp.EW4QTzEAuio26Ayl:18010:0:99999:7::: || 21. |
Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0::: || 22. |
hackme:$6$.L285.sE7ZCFoZPJnQ1kUXLje/bY2BIUQFbYu.8M6B:17981:0:99999:7::: || 23. |
harold:$1$7d.s/LP.mjL9lp/1:14529:0:99999:7::: || 24. |
harold:$1$Xx6dZdOd$IMOGACl3r757d:14513:0:99999:7::: || 25. |
Harry:1008:93cd1441208923e8628e6:031f5563e0ac4ba538e8ea325479740d::: || 26. |
IUSR_GRANPA:1003:a274b4532c9ca5cdf684351fab962e86:6a981cb5e038b2d8b713743a50d89c88::: || 27. |
IWAM_GRANPA:1004:95d112c4da2348b599183ac6b1d67840:a97f39734c21b3f6155ded7821d04d16::: || 28. |
jens:$6$JWiFWXb8$cGQi07IUqln/uLLCGjLenxfAaI2sg/Wk1OFoAh/:18011:0:99999:7::: || 29. |
john:$1$H.GRhlY6$sKlytDrwFEhu5dULXItWw/:15374:0:99999:7::: || 30. |
john:$1$wk7kHI5I$2kNTw6ncQQCecJ.5b8xTL1:14525:0:99999:7::: || 31. |
john:$1$zL4.MR4t$26N4YpTGceBO0gTX6TAky1:14513:0:99999:7::: || 32. |
john:$6$aoN7zaDl$e6RsRZndFekSS4bgqz0y5dgzO1dTQsMAWck6dFGogkxrrZf1ZyGbjy/oCpqJniIkasXP05iFZHs.XZ:17594:0:99999:7::: || 33. |
klog:$1$f2ZVMS4K$R9XkI.CmLdHhdUE3X9jqP0:14742:0:99999:7::: || 34. |
Lakis:1009:f927b0679b3cc0e192410d9b0b40873c:3064b6fc432033870c6730228af7867c::: || 35. |
loneferret:$1$/x6RLO82$43aCgYCrK7p2KFwgYw9iU1:15375:0:99999:7::: || 36. |
loneferret:$1$qbkHf53U$r.kK/JgDLDcXGRC6xUfB11:15079:0:99999:7::: || 37. |
mai:$6$Mp.mBBi7$BCAKb75xSAy8PM6IhjdSOIlcmHGiwZtwGPXalF15xT097Q6zaXrY6nD/7RsdSiE0:17594:0:99999:7::: || 38. |
makis:$1$Yp7BAV10$7yHWur1KMMwK5b8KRZ2yK.:17239:0:99999:7::: || 39. |
mark:$6$//1vISW6$9pl2caepnDyYE4lIPJDdX7ipnxm/muPD7DraEm3z0jqDe5iH/Em2i6YXJpQD.5pl0:18010:0:99999:7::: || 40. |
mark:$6$J3gYK/cQ$au1WmOCtq.X1DTKt1CEmKA9qr4PfwZuAGUdCfA/Xk1/oWJtQF0:17408:0:99999:7::: || 41. |
mysql:$6$O2ymBAYF$NZDtY392guzYrKkEUq/IonKdnYEec0S0ZBcQFZ.sno/:18053:0:99999:7::: || 42. |
notch:$6$RdxVAN/.$DFugS5p/G9hTNY9htDW/nYYL.w.DkjrUs0PlYNcYZWhh0:17349:0:99999:7::: || 43. |
noulis:$6$ApsLg5.I$Zd9blHPGRHAQOab94HKuQFtJ8m7ob8MFnX6WIIr0Aah6pW/aZ.yA3T1iU13lCSixrh6NG1.GHPl.QbjHSZmg7/:17247:0:99999:7::: || 44. |
Ori:$6$1zYgjEIM$8pbWnEXjqTmEdFnQRXKmTmXPXmt55/oyup40NiXD8J9GxmXF7DYiaHZDRshrs3f1:17237:0:99999:7::: || 45. |
oscp:$6$k8OEgwaFdUqpVETQ$sKlBojI3IYunw8wEDAyoFdHgUqP569BokTZ52mDroq/rmJY9zgfeQVmBFu/Sf.:18452:0:99999:7::: || 46. |
peter:$6$QpjS4/x7GhQQ/6R58SJddU2X/QTQKNJWzwiByeTELKeyp0:17721:0:99999:7::: || 47. |
pi:$6$SQPHFoql$gSE5qWbZRGHDin4LnFY56sMnQsm.3Kcq/Pws88e8yjKgJnaxN3zdq8f5ots1bJcY/:17148:0:99999:7::: || 48. |
postgres:$1$dwLrUikz$LRJRShCPfPyYb3r6pinyM.:17239:0:99999:7::: || 49. |
puck:$6$A/mZxJX0$Zmgb3T6SAq.FxO1gEmbIcBF9Oi7q2eAi0TMMqOhg0pjdgDjBr0p2NBpIRqs4OIEZB4op6ueK888lhO7gc.27g1:15768:0:99999:7::: || 50. |
reynard:$6$h54J.qxd$yL5md3J4dONwNl.36iA.mkcabQqRMmeZ0.m.mkQzz55U2H5kUh1:15768:0:99999:7::: || 51. |
robert:$1$rQRWeUha$ftBrg:15374:0:99999:7::: || 52. |
robot:$6$HmQCDKcM$mcINMrQFa0Qm7XaUaS5xLEBSeP3bUkr18iwgwTAL8AIfUDYBWG5L8J9.Ukb3g.I5qaHBnTddK/:16752:0:99999:7::: || 53. |
root:$1$5GMEyqw.:15375:0:99999:7::: || 54. |
root:$1$DdHlo6rh$usiPcDoTR37eL7DAyLjhk1:0:0::0:0:Charlie &:/root:/bin/csh || 55. |
root:$1$FTpMLT88$.:14529:0:99999:7::: || 56. |
root:$1$p/d3CP0:17239:0:99999:7::: || 57. |
root:$1$QAKvVJey$6rRkAMGKq1u62yfDaenUr1:15082:0:99999:7::: || 58. |
root:$1$XROmcfDX$tF93GqnLHOJeGRHpaNyIs0:14513:0:99999:7::: || 59. |
root:$6$.w/hDW8t$a/dHKimULfr5rJTDlS7uoUanuJB2YUUkh.LWSKF7kTNp4aL8UTlOk2wT8IkAgJ.:18452:0:99999:7::: || 60. |
root:$6$9xQC1KOf$5cmONytt0HkyJLjiSWcAS/.OF0iu.:16753:0:99999:7::: || 61. |
root:$6$aorWKpxj$yOgku4F1ZRbq/6K/UU5wLobTSz/Pw5/IL/NQbOr1Wzp2bTbpNQr1jNNlaGjXDu5Yj1:17721:0:99999:7::: || 62. |
root:$6$B$Q6rY5I9yQUhIz/o5UfDxZw7MMq8atR3UdJjhpkF.:17431:0:99999:7::: || 63. |
root:$6$CM3c1cdI$HbQWZlQdGEW/RFK4G7fafTUIUYLWk52zm9O8KRLhqZenF8KbqsUjHlZQk4:17111:0:99999:7::: || 64. |
root:$6$cQPCchYp$rWjOEHF47iuaGk/DQdkG6Dhhfm3.hTaNZPO4MoyBz2.bn44fERcQ23XCsp43LOt5NReEUjwDF8WDa5i1ML2jH.:16695:0:99999:7::: || 65. |
root:$6$GpmQGQUN$8kLewzMF4ItmxezcryWqSPrXNRTH5TOQFKKkHjK2NSmrTg95xiYi.l8L.RYUL.8pAsj8s4EG.:15585:0:99999:7::: || 66. |
root:$6$kdMFceEg$pk9h93tdD7IomhE7L0Y396HO6fxSM.XDh9dgeBhKpdZlM/WYxCZe7yPRNHfZ5F/IN0:18012:0:99999:7::: || 67. |
root:$6$L2m6DJwN$p/xas4tCNp19sda4q2ZzGC82Ix7GiEb7x/eR82G4/YOnni/.L69tpCkOGo5lm0AU7zh9lP5fL6A0:17247:0:99999:7::: || 68. |
root:$6$m20VT7lw$172.XYFP3mb9Fbp/IgxPQJJKDgdOhg34jZD5sx.DBw4C5D:15768:0:99999:7::: || 69. |
root:$6$mqjgcFoM$X/qNpZR6gXPAxdgDjFpaD1yPIqUF5l5ZDANRTKyP6Uq7cPaYfzPSmgATM9cwD1:18050:0:99999:7::: || 70. |
root:$6$n.BA4A59$WeIF0ZbaB3.GhL9obYhxUjanXf/NJXiCHB.:17412:0:99999:7::: || 71. |
root:$6$O4bZf1Ju$0xcLPNyQk7XuFstUDWwYHKm4XJjSUgiwjPmEp0:17399:0:99999:7::: || 72. |
root:$6$P7ElNgGp$fNzyy4OgqSR1ANJXTgbpzp4U42JXG1qJ55iNcTOj0lqObyWhFu2y3udH.:17238:0:99999:7::: || 73. |
root:$6$PnbVvEMS$OcseJT8lZRrgrW1JBpHJ252SPRxS6Rkh3oaqaon7waFKwSqbg5fIjFgzUVFMS1:18048:0:99999:7::: || 74. |
root:$6$qAoeosiW$fsOy8H/VKux.9K0T3Ww2D3FPNlO5LAaFytx/6t69Q7LPDSS/nNiP4xzq0Qab.Iz3uy5fYdH3Aw/K5:16756:0:99999:7::: || 75. |
root:$6$sZyJlUny$OcHP9bd8dO9rAKAlryxUjnUbH0dxgZc2uCePZMUUKSeIdALUulXLQ1iDjoEQp.m39Xrt3mm91:17097:0:99999:7::: || 76. |
sarah:$6$DoSO7Ycr$2GtM5.8Lfx9Sw8X1fDMF.7zWDoOtxmej/8D7X8PQAGKYGl.gUb6/cG210:18010:0:99999:7::: || 77. |
scriptmanager:$6$WahhM57B$rOHkWDRQpds96uWXkRCzA6b5L3wOorpe4uwn5U32yKRsMWDwKAm.RF6T81Ki/MOyo.dJ0B8Xm5/wOrLk35Nqd0:17504:0:99999:7::: || 78. |
service:$1$cwdqim5m$bw71JTFHNWLjDTmYTNN9j/:17239:0:99999:7::: || 79. |
setup:$6$PR5zOqWk$3MKXMgf6.4bLlznh0R87RB4qaOAcGhbE0Cs8xtUq/6aMZnfsZOWKXL0DOqUc:17086:0:99999:7::: || 80. |
shelly:$6$aYLAoDIC$CJ8f8WSCT6GYmbx7x8z5RfrbTG5mpDkkJkLW097hoiEw3tqei2cE7EcUTYdJT0:17431:0:99999:7::: || 81. |
smeagol:$6$$6ldY35ytL8yRd.Gp947FnW3t/WrMZXIL7sqTQS4wuSKeAiYeoYCy7yfS2rBpAP.:16695:0:99999:7::: || 82. |
SUPPORT_388945a0:1001:aad3b435b51404eeaad3b435b51404ee:8ed3993efb4e6476e4f75caebeca93e6::: || 83. |
susan:$6$5oSmml7K$0joeac/3q2lBp5yZ7X/SR/:17721:0:99999:7::: || 84. |
sys:$1$NsRwcGHl$euHto/.:17239:0:99999:7::: || 85. |
togie:$6$d$jpt1Mle8ou.8Pf1:17392:0:99999:7::: || 86. |
tom:$6$ptD/.gN.$n.B/5dODEQFteBwg75Ip9leeaaXSMesGbfZzoK1JLZ6817ckZhAJF776Dg/ZJ0:17407:0:99999:7::: || 87. |
user1:$6$9iyn/lCu$UxlOZYhhFSAwJ8DPjlrjrl2WuHToNIIjTqMLGSh0R2Ch4Ij5gkmP0eEH2RJhZ0:18050:0:99999:7::: || 88. |
user2:$6$7g$ud1EgcfKqa24i/p3QeCMHj8ULl.:18050:0:99999:7::: || 89. |
user3:$6$PaKeECW4$5yMn9UU4YByCj0LP4QWaGt/S1aG0Zs73EOJXh.Rl0ebjpmsBmuGUwTgBamqCCx7qZ0sWJOuzIqn.GM69aaWJO0:18051:0:99999:7::: || 90. |
user4:$6$0pxj6KPl$NA5S/2yN3TTJbPypEnsqYe1PrgbfccHntMggLdU2eM5/23dnosIpmD8sRJwI1PyDFgQXH52kYk.bzc6sAVSWm.:18051:0:99999:7::: || 91. |
user5:$6$wndyaxl9$cOEaymjMiRiljzzaSaF.GszLm77k0d5GpQZzJpcw9n/:18051:0:99999:7::: || 92. |
user6:$6$Y9wYnrUW$ihpBL4g3GswEay/AqgrKzWtDZcUbh/5w/tQELa3LtiyTFwsLsWXubsSCfzRcao1u/:18051:0:99999:7::: || 93. |
user7:$6$5RBuOGFi$eJrQ4/xf2z/3pG43UkkoE35Jb0BIl7AW/umj1Xa7eykmal.89dXtGQXdH.Rdy0:18052:0:99999:7::: || 94. |
user8:$6$fdtulQ7i$G9THW4j6kUy4bXlf7C/0XQtntw123LRyz7wXsEhMc2XC4CqiTxATfb20xWaXP.:18052:0:99999:7::: || 95. |
user:$6$gL$CGHDuEBpkC90/7WJFpADj0zboPTKTqPbOHafZGUd/exj4OZ1Frc/:15585:0:99999:7::: || 96. |
:$6$ud4650Og$j9dN4Xh6nHTDUQ5LpnrUzl6FdRiapcG/Wx.G5Q.PFtb1nxGFiy56zS/:17033:0:99999:7::: || 97. |
:$6$tMOyhDF2$gExhASD.A8XLJb.DZ4yDTGMrhdi3lQ0:15585:0:99999:7::: || 98. |
wpadmin:$6$FtTN/YPC$iidNFmR/7G10aze2CA2W3ik/sHHyEPaNNY57tMvRDU0/Rs62FEimiKXD2:17096:0:99999:7::: || 99. |
www-data:$6$SYixzIan$P3cONYwMwplB62RWu1RklKqIGCX1zleXuZhms.:17264:0:99999:7::: |项目信息
开发语言:HTML
Star 数:182
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Writeups for vulnerable machines.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | writeups - Writeups for vulnerable machines. |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:47:40 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 282 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |