 CTF思路
点击放大
Arsenal - Offline-first, searchable arsenal for pentesting &
项目说明
<h1 align="center">ARS3NAL</h1>
<p align="center"><b>English</b> · <a href="README.ru.md">Русский</a></p>
<p align="center">
<b>A local, offline-first arsenal for pentesting & bug bounty.</b><br>
Clickable attack chains, payloads, a click-to-build command generator, GTFOBins, ready-to-run
scripts, wordlists, an embedded CyberChef, reverse shells, a Burp reference, operational
checklists and an engagement tracker. One fast, searchable, editable app that runs on your machine.
</p>
<p align="center">
<img alt="license" src="
<img alt="stack" src="
<img alt="offline" src="
<img alt="ui" src="
<img alt="docker" src="
</p>
<p align="center"><b>▶ <a href=" demo</a></b> — runs entirely in your browser, nothing to install (your data stays in your browser).</p>
!ARS3NAL command builder — click flags, the command assembles itself
> No telemetry. No cloud. No account. Your data lives in a local SQLite file and never
> leaves the box. Stop juggling 30 browser tabs and a folder of .md cheatsheets.
> ⚠️ For authorized security testing and education only. See Disclaimer.
> 🌐 Bilingual (Russian / English) — a one-click toggle switches the interface and most
> reference content (payloads, GTFOBins, commands, Burp docs, wordlists) between RU and EN.
> Payloads, commands and code themselves stay technical.
---
✨ Highlights
🔗 Attack Chains: from a finding to impact, step by step *(new)*
92 curated, clickable kill-chains across 11 categories (IDOR / access control, recon, injection,
OAuth / SSO, SSRF, client-side XSS / CSRF, auth / 2FA / logic, file upload / LFI, API / GraphQL,
modern web, AI / LLM). Each chain is tagged by level (Newbie / Intermediate / Ad) so a
newcomer can start easy and climb. Every step is a goal plus a concrete payload or command, with a
one-click jump straight into the matching Payloads / Scripts / Commands entry, and they are grounded
in real CVEs and disclosed reports. Paste your two accounts, client_id or redirect_uri into the
context tokens and the steps fill themselves in.
🛰️ Recon Tools: Wayback CDX, IDN homograph email-ATO, dorks *(new)*
Three offline recon crafters that only assemble what *you* run. A Wayback CDX query builder
(match types, extension filters, presets) with copy-paste post-processing recipes (gau/waybackurls
harvest,
uro dedup, gf classification, id_ deleted-file recovery, PDF secret scan). An **IDNhomograph generator** for 0-click account takeover email: it crafts the domain-part and
username-part look-alikes plus their on-the-wire form and the full attack workflow, with a defensive
analyzer that decodes
xn-- and flags confusables. And a dork builder with 20 Google categoriesplus GitHub code-search and Shodan pivots.
<p>
<img src="screenshots/recon.png" width="49%" alt="Wayback CDX query builder">
<img src="screenshots/recon-homograph.png" width="49%" alt="IDN homograph email-ATO generator">
</p>
🧰 Offline attack labs: OAuth/SSO + JWT *(new)*
Interacti that assemble, never fire. The OAuth / SSO Lab builds a malicious
/authorizeURL (redirect_uri bypass, PKCE downgrade, state/CSRF, token leak, nOAuth) you paste into Burp. The
JWT Workshop decodes a token and forges it in the browser: alg:none, RS256 to HS256 key confusion,
kid path-tra / SQLi, re-sign with a weak secret.
📝 Report Templates *(new)*
Per-class report skeletons (IDOR, OAuth ATO, SSRF, XSS, SQLi, RCE, auth, LLM and more) with a CWE
and a pre-filled CVSS:3.1 . The acti target and your context tokens substitute
into the text; copy the whole report or export it to
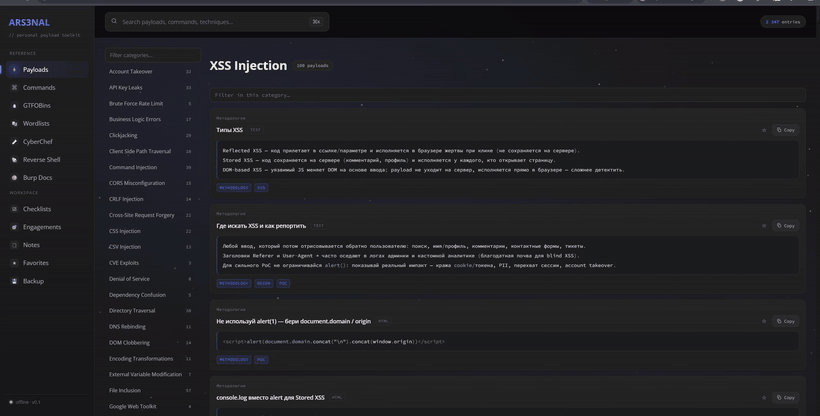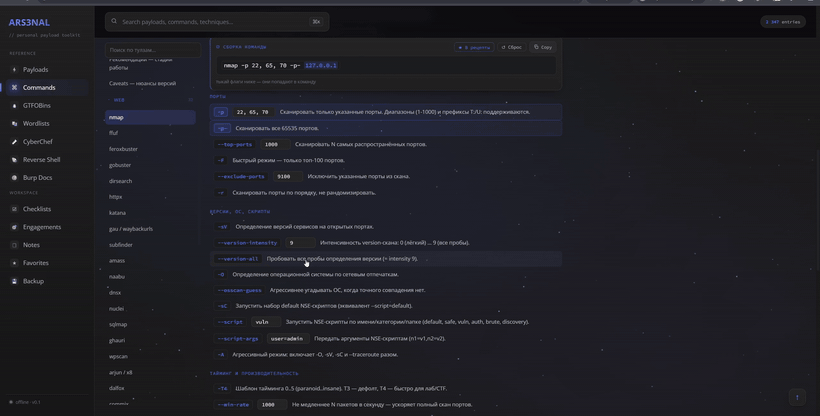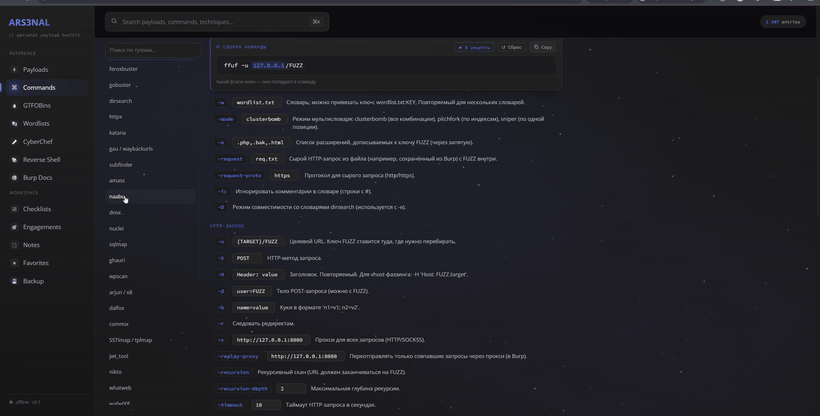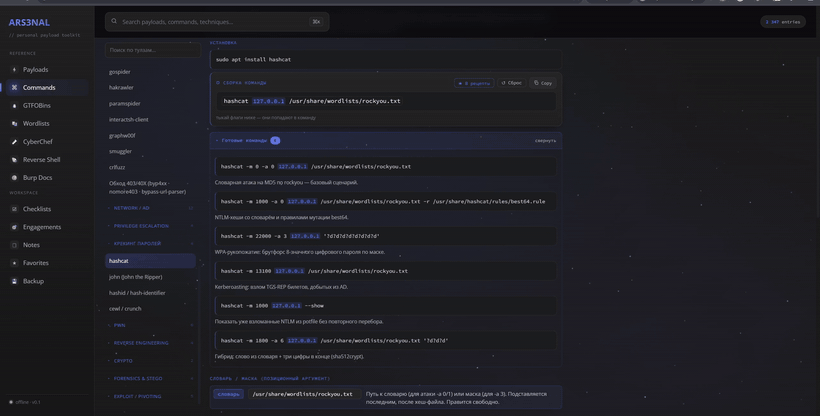
.md.🛠️ Command builder — assemble commands by clicking flags
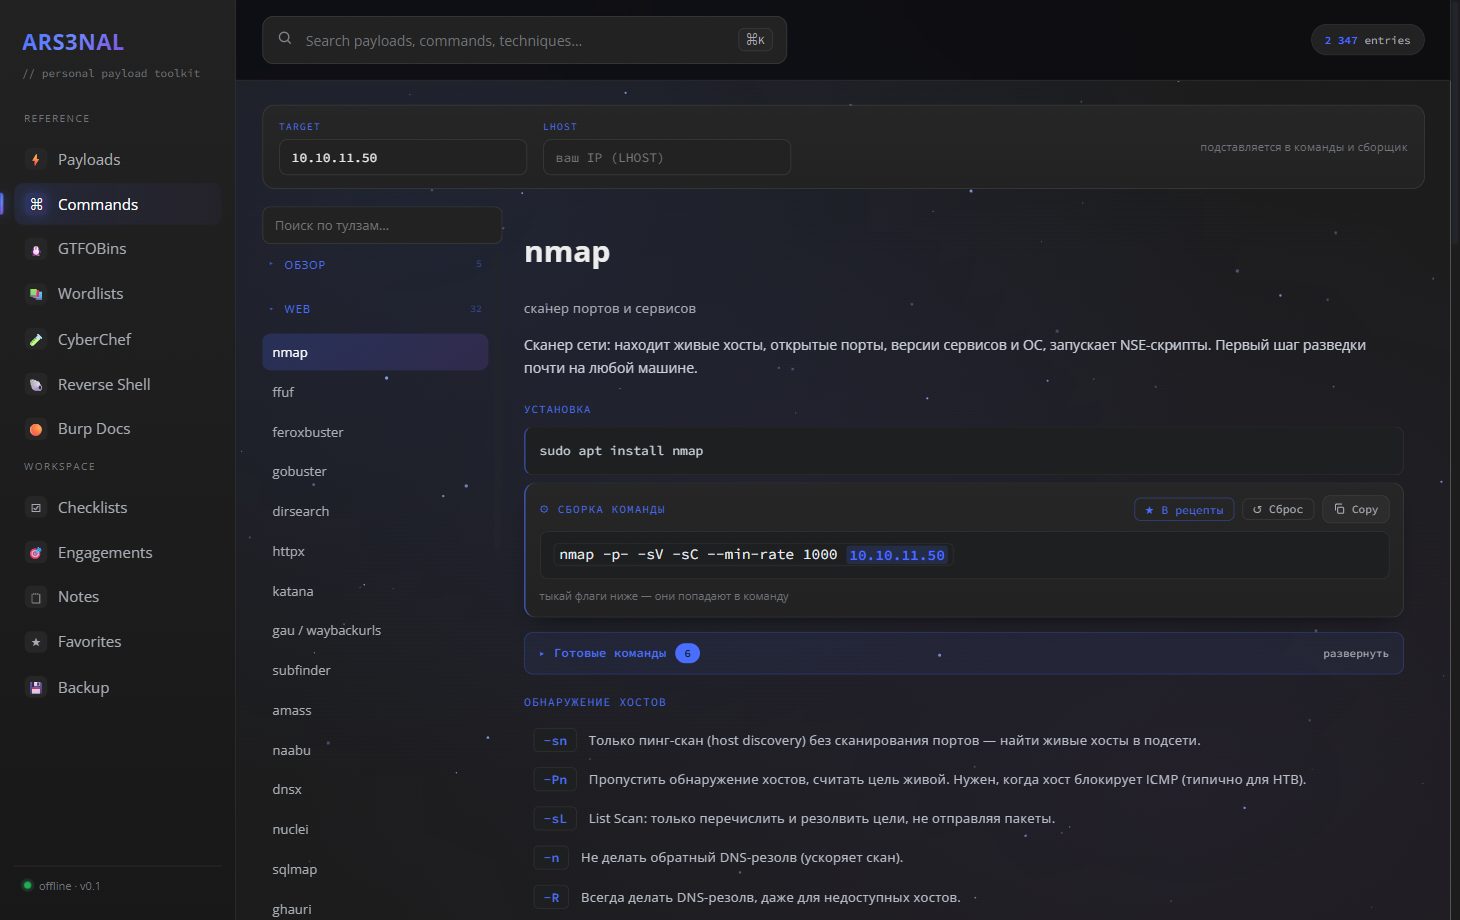
The headline feature. Pick a tool, toggle the flags you want, and the command assembles
itself with , documented flags (each flag is explained, RU/EN). Set your
Target / LHOST once in the top bar and it's substituted into *every* tool's examples
live — no more find-and-replace on
10.10.x.x. Sa commands to your own“Готовые команды” library (persists in the DB, drag-to-reorder). 59 tools have the
builder (nmap, ffuf, sqlmap, gobuster, hashcat, …); the rest are rich Markdown references.
!Command builder with nmap
⌨️ One search across e
A ⌘K palette that searches every payload, command, GTFOBin, wordlist and doc at once
(SQLite FTS5), so you find the thing without remembering which module it lives in.
!Global search — type once, jump straight to the result
⚡ Curated payloads — 63 categories
Hand-curated from PayloadsAllTheThings (~1500 entries): detection-first ordering, real
copy-ready payloads, diagrams and tables, with tips (RU/EN). Not a noisy auto-dump.
!Payloads
📜 Scripts — 110 ready-to-run scripts *(new in 1.0)*
Full copy-paste-and-run scripts (Python / Bash / JS / HTML PoC) across 27 categories, not
one-liners: boolean / time / error / UNION blind SQLi extractors, JWT forging, SSRF & XXE
out-of-band listeners, IDOR matrices, recon pipelines, cloud / k8s probes, CVE PoCs and more.
Filter by group and language; each script lists its dependencies, parameters and safety
badges (destructive / paid / root). All original code, RU / EN.
🧪 CyberChef — embedded & offline
The full official CyberChef build, embedded right in the app, re-themed to match and with
its UI localized to Russian. Encode, decode and crypto right inside ARS3NAL, offline.
!Embedded CyberChef
🐧 GTFOBins — all 458, RU / EN
Every GTFOBins binary with function/context filter chips (shell, file-read, sudo, SUID…)
and technique notes in Russian and English.
!GTFOBins
🐚 Re generator
re.com-grade: reverse / bind / msfvenom / listeners, with shell and encoding
selectors (base64 / URL / PowerShell). Your LHOST is shared with the rest of the app.
!Reverse shell generator
☑️ Operational checklists
70 per- checklists (web + AD / cloud / priv-esc / pi) you tick off —
progress persists — with a research panel and inline ⚡ payload cross-links per item.
!Checklists
🎯 Engagements & findings
A per-target workspace: host / LHOST / scope / notes + a findings tracker (se,
status, repro) + Markdown report export. The acti feeds
{TARGET} / {LHOST}into the command builder and re generator.
!Engagements
📚 Wordlists reference & 🟠 Burp reference
A curated guide to the top wordlists (canonical paths + GitHub links + “what each is for”),
and a reference for the Burp Suite desktop workflow (RU/EN).
<p>
<img src="screenshots/wordlists.png" width="49%" alt="Wordlists">
<img src="screenshots/burp.png" width="49%" alt="Burp reference">
</p>
Plus Notes (personal Markdown), Fa (★ across every module) and Backup
(export/import your personal layer as one JSON; restoring ne the bundled reference content).
---
🚀 Run
Two ways: the live demo runs client-only in your
browser (reference content is bundled; your notes/targets/progress live in the browser's
IndexedDB). For the full local app with your own SQLite database and editable content, run it
yourself:
Double-click start.bat (first run installs deps, seeds the DB and builds the UI),
then open <
Or manually (Node.js 18+):
Or with Docker (only Docker itself required):
The image seeds the content DB on first run; your custom entries, notes and fa persist in the arsenal-data across restarts. To use a different port, edit docker-compose.yml and add the new host:port to ALLOWED_HOSTS so the built-in local-only guard allows it.
Dev mode: npm run dev (Vite + Fastify with li). Tests: npm test.
🗂️ Layout
server/ — Fastify API + SQLite (better-sqlite3, FTS5)seed/ — parsers that build the DB (curated payloads, checklists, commands, Burp docs, GTFOBins, wordlist refs)web/ — Vite + SPA (no framework)data/arsenal.db — your data; custom entries, notes, engagements and checklist progress are ne by re-seeding, and the DB is git-ignored so nothing personal is e.🔒 Privacy
E is local. Notes, targets, findings and sa live only indata/arsenal.db (git-ignored). The seed pipeline rebuilds all *reference* content from
source, so ignoring the DB loses nothing.
⚖️ Disclaimer
ARS3NAL is a reference and productivity tool for authorized security testing,
CTF/learning, and defensi. Use it only against systems you own or have
explicit written permission to test. You are solely responsible for your actions and for
complying with all applicable laws. The authors accept no liability for misuse or damage.
Full text: DISCLAIMER.md.
🙏 Acknowledgements
ARS3NAL is mostly a fast, offline, searchable front-end o people's excellent work.
Huge thanks to:
Full per-source license details: THIRD_PARTY.md.
📄 License
GPL-3.0 (see LICENSE) — required because ARS3NAL bundles GPL-3.0 GTFOBins data.
项目信息
开发语言:CSS
Star 数:180
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Offline-first, searchable arsenal for pentesting & bug bounty: payloads, a click-to-build command generator, GTFOBins, wordlists, embedded CyberChef, reverse shells, checklists & an engagement tracker.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Arsenal - Offline-first, searchable arsenal for pentesting & |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:47:48 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 222 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |