 CTF思路
点击放大
CTFPacker - CTF和pentest/red team e的Shellcode打包机
项目说明
<p align="center">
<img src="assets/Full-Logo-red-black.svg" width="500" alt="CTFPacker">
</p>
</div>
<di="center">
!GitHub License
!X (formerly Twitter) URL
</div>
> [!TIP]
> Did CTFPacker help you with a penetration test engagement or in passing a certification exam? If so, please consider giving it a star ⭐! Your support would greatly help the project and motivate me to add more features or e it entirely into a much more capable packer!
Table-Of-Contents
* Goal
* General Information
* E Features
* Installation
* Usage
+ GUI
+ Format option
+ Staged
+ Stageless
* To-Do
* Detections
* Credits - References
Goal
This repository has been created to facilitate A during CTFs and/or pentest & red team exams. The goal is to focus more on pwning rather than struggeling with e !
Check out my blog post for more infos: Evade Modern AVs in 2025
General Information
>[!CAUTION]
>This tool is designed for authorized operations only. I AM NOT RESPONSIBLE FOR YOUR ACTIONS. DON'T DO BAD STUFF.
>[!NOTE]
>- The techniques used in the loader are nothing new. The loader generated from this packer will probably NOT evade modern AVs / EDRs. Do not expect that or anything ground breaking.
>- Most of the e techniques used here are NOT from me. I just added a bunch of known stuff together and it is enough for CTFs !
>- Depending on the interest shown to this project, I might add some techniques from my own research and maybe expand/rewrite the packer entirely.
E Features
-s argument-er)Injection Methods
| Flag | Name | Type | Target | How it works |
|------|------|------|--------|--------------|
| apc | EarlyBird APC | Remote — spawned process | RuntimeBroker.exe / s.exe | Spawns the target in a suspended state, queues an APC to the main thread pointing at injected shellcode, then resumes it |
| copyfile2 | CopyFile2 Callback | Self-injection (local) | Own process | Uses the CopyFile2 progress-callback mechanism to execute shellcode inside the current process — no remote handle required |
| tp_direct | PoolParty TP_DIRECT | Remote — existing process | RuntimeBroker.exe / s.exe | Hijacks the target's IoCompletion handle, writes shellcode into the target's memory, crafts a TP_DIRECT struct and queues it via ZwSetIoCompletion — the target's thread pool dispatches the callback |
| wf_o | PoolParty WF O | Remote — existing process | RuntimeBroker.exe / s.exe | Hijacks the target's TpWorkerFactory handle, o StartRoutine in the target's memory with the shellcode via WriteProcessMemory, then bumps the minimum thread count to force a new worker thread |
| timerqueue | Timer Queue Callback | Self-injection (local) | Own process | Allocates RWX memory, copies shellcode, and registers it as a one-shot CreateTimerQueueTimer callback — the thread pool fires it after 100 ms; main thread sleeps indefinitely |
> [!NOTE]
> apc spawns a new instance of the target process; tp_direct and wf_o require the target process to already be running; copyfile2 and timerqueue are self-injection and don't touch any other process.
Installation
Just run the install script:
That's it ! This will install the python package via pipx, set up a .desktop launcher and copy the logo to ~/.local/share/icons/. You can now use ctfpacker and ctfpacker-gui globally.
Usage
GUI
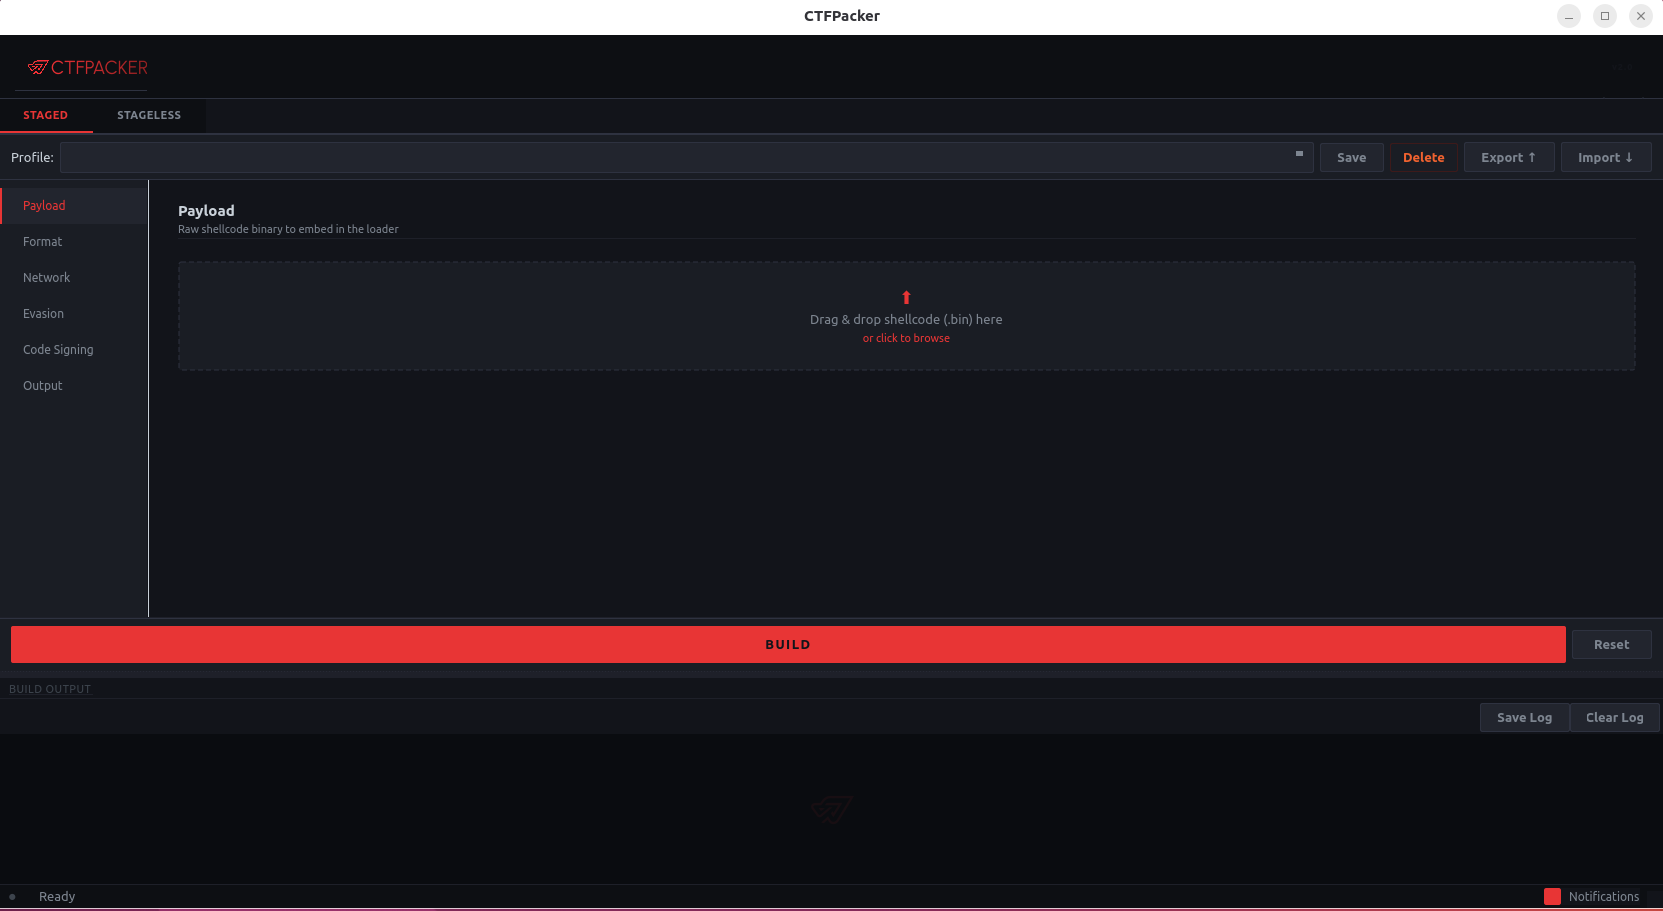
If you installed via pipx or install.sh, you can launch the GUI directly or through your desktop app launcher (which is the preferred way using CTFPacker):
<p align="center">
<img src="assets/GUI.png" width="800" alt="CTFPacker">
</p>
The GUI exposes all the same options as the CLI but with real-time build output, a log panel, and a profile system. You can save/load build configurations as named profiles, and export/import them as .ctfp files to share across machines.
General usage
Staged:
Stageless:
Format option
In both cases, staged or stageless, you can choose whether to compile your loader as an EXE or a DLL. To compile it as a DLL, simply append -f DLL. By default, it compiles as an EXE, though you can also explicitly specify this using -f EXE (but you don't need to).
The DLL exports a function called ctf. This is the function you need to call to start the exection.
Staged
When using the staged "mode", the packer will generate you a .bin file named accordingly to your -o arg. With the -pa argument, you are actually telling the loader *where* on the websever (basically the path) it should search for that .bin file. So TLDR those two should usually be the same.
Example:
With this command, your telling the loader to connect to the 192.168.2.121 IP, at port 8080 and download the shellcode.bin file. So you should serve this file via a webserver.
Stageless
This is fairly simple. The shellcode will be included into the loader. I recommend you to use the encryption arg -e. Otherwise the signature-based detection will likely catch it.
To-Do
Detections
Credits - References
Most of the code is not from me. Here are the original authors:
项目信息
开发语言:C
Star 数:149
技术要点
该项目属于CTF思路方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Shellcode packer for CTFs and pentest / red team exams aiming for AV evasion!展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | CTFPacker - CTF和pentest/red team e的Shellcode打包机 |
| 所属分类 | CTF思路 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:49:56 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 141 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |